
minimal
 rtvkiz/minimal
Minimal CVE Hardened container image collection
cloud-securityconfiguration-auditingcontainer-security+3
rtvkiz/minimalMinimal CVE Hardened container image collection
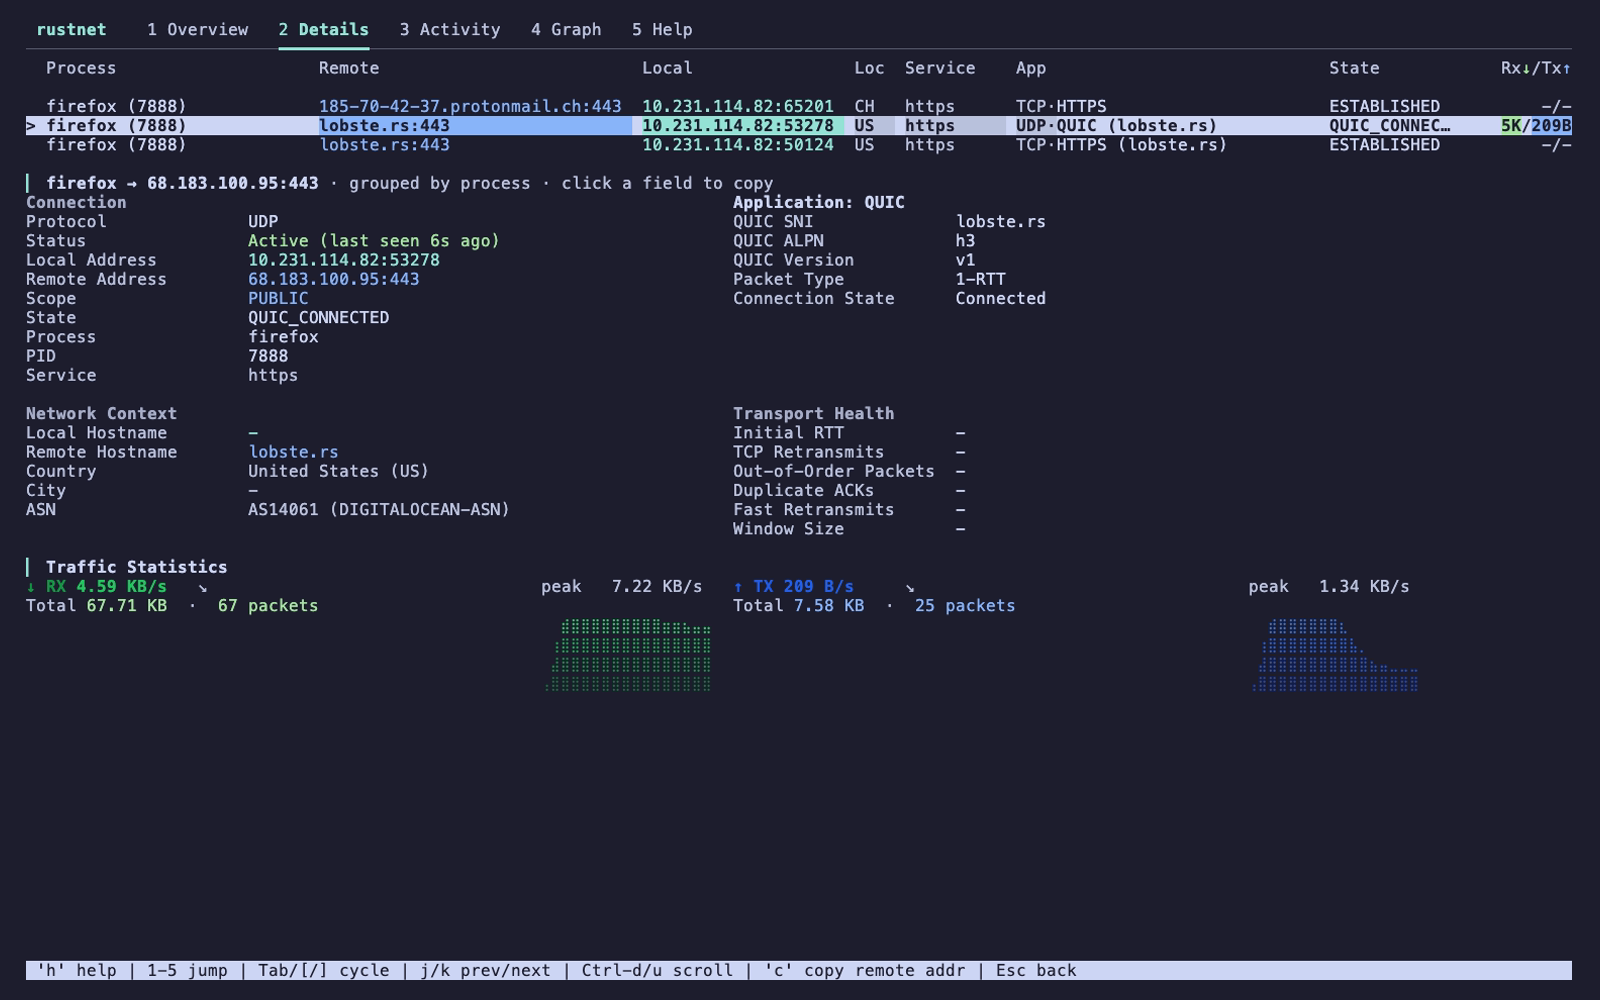 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 microsoft/litebox
A security-focused library OS supporting kernel- and user-mode execution
 paradigmxyz/iron-proxy
An egress firewall for untrusted workloads.
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 mondoohq/installer
Linux, macOS and Windows Install scripts for cnquery & cnspec
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 dockur/windows
Run Windows inside a Docker container with KVM acceleration, automatic installation, and customizable resources. Supports multiple Windows versions,…
 h3ck13r/cve-2026-35204
Proof-of-concept demonstrating a path traversal vulnerability (CVE-2026-35204) in Helm plugin installation, allowing arbitrary file write via crafted…
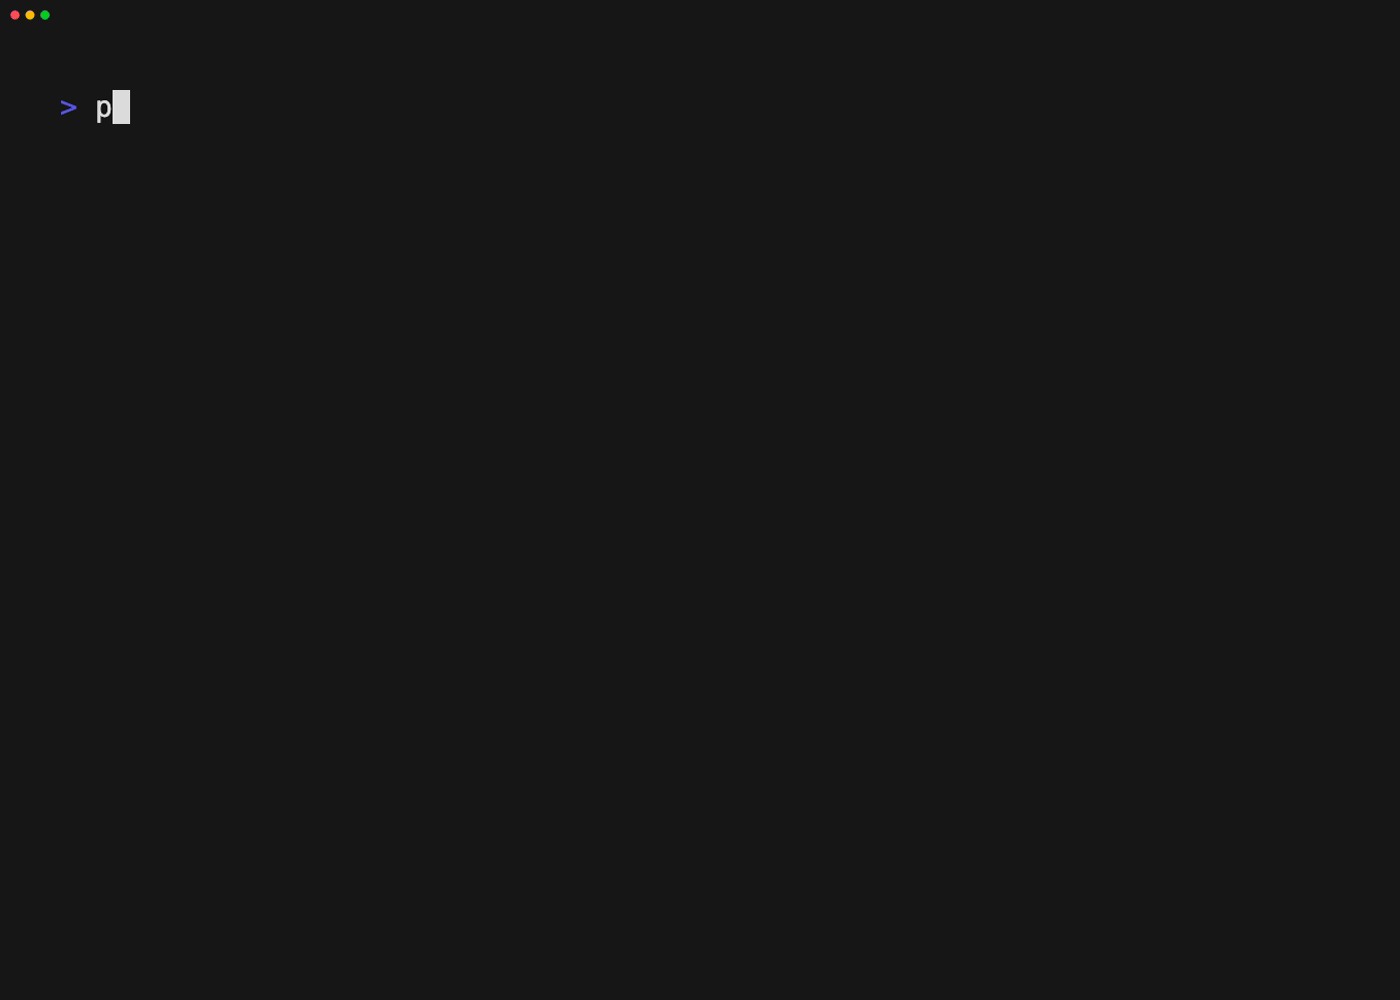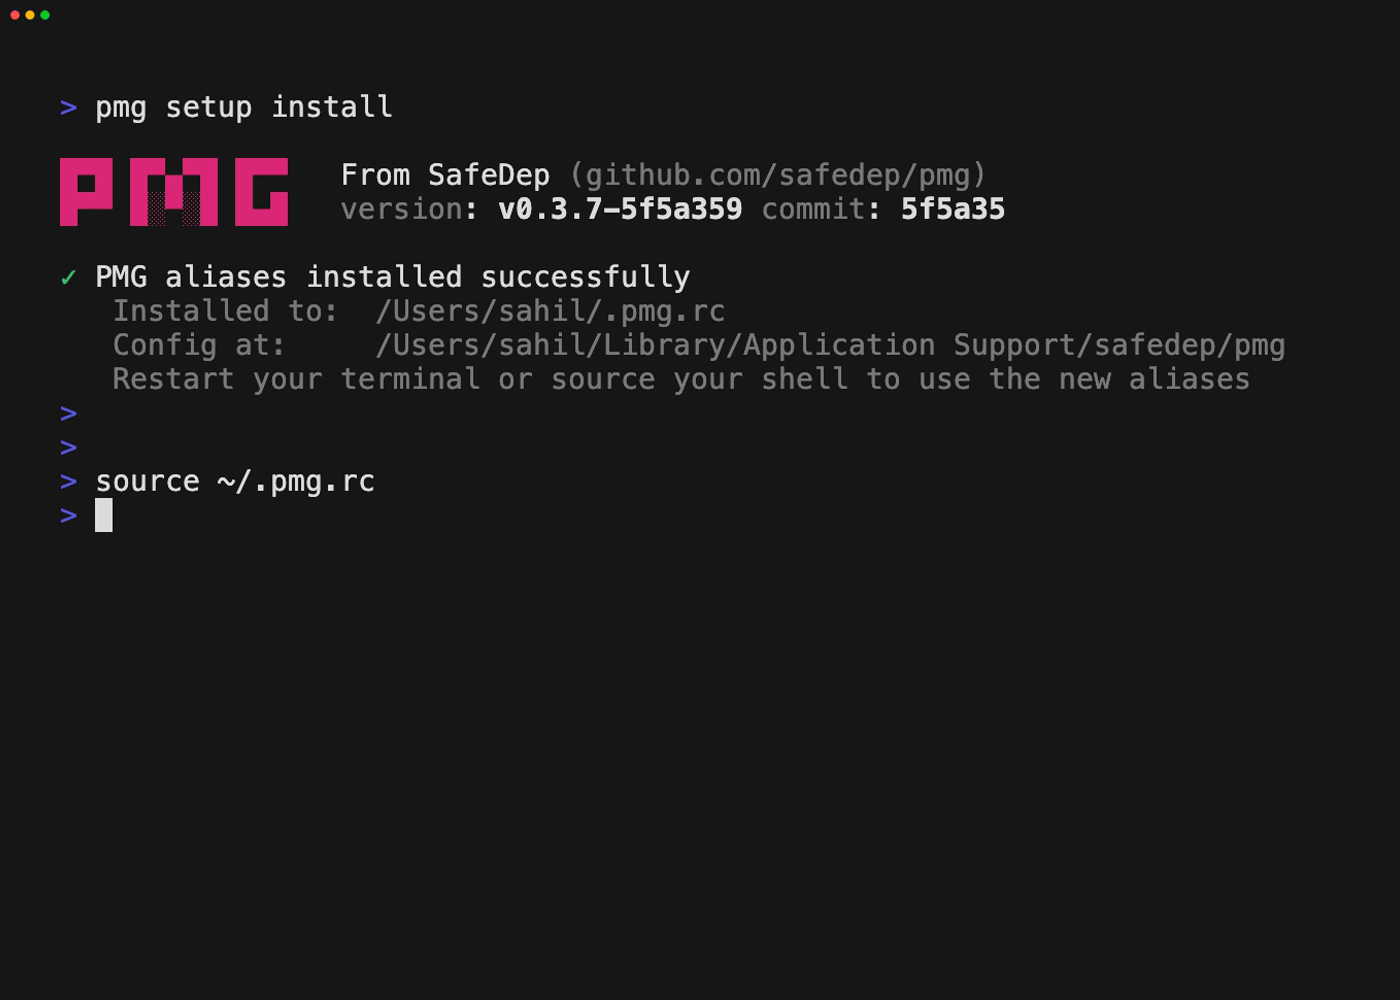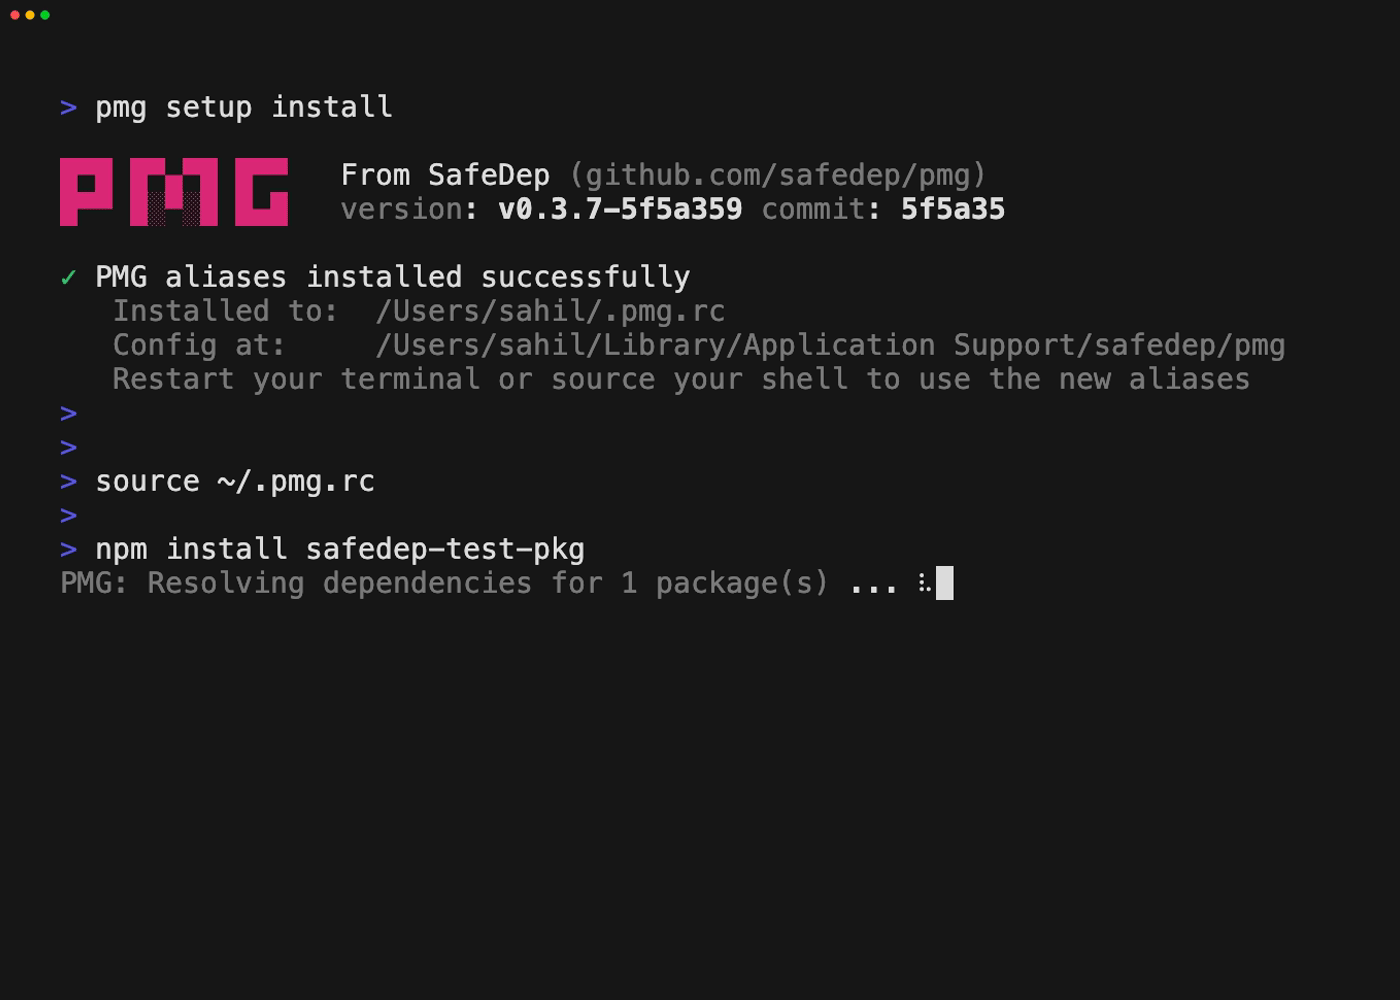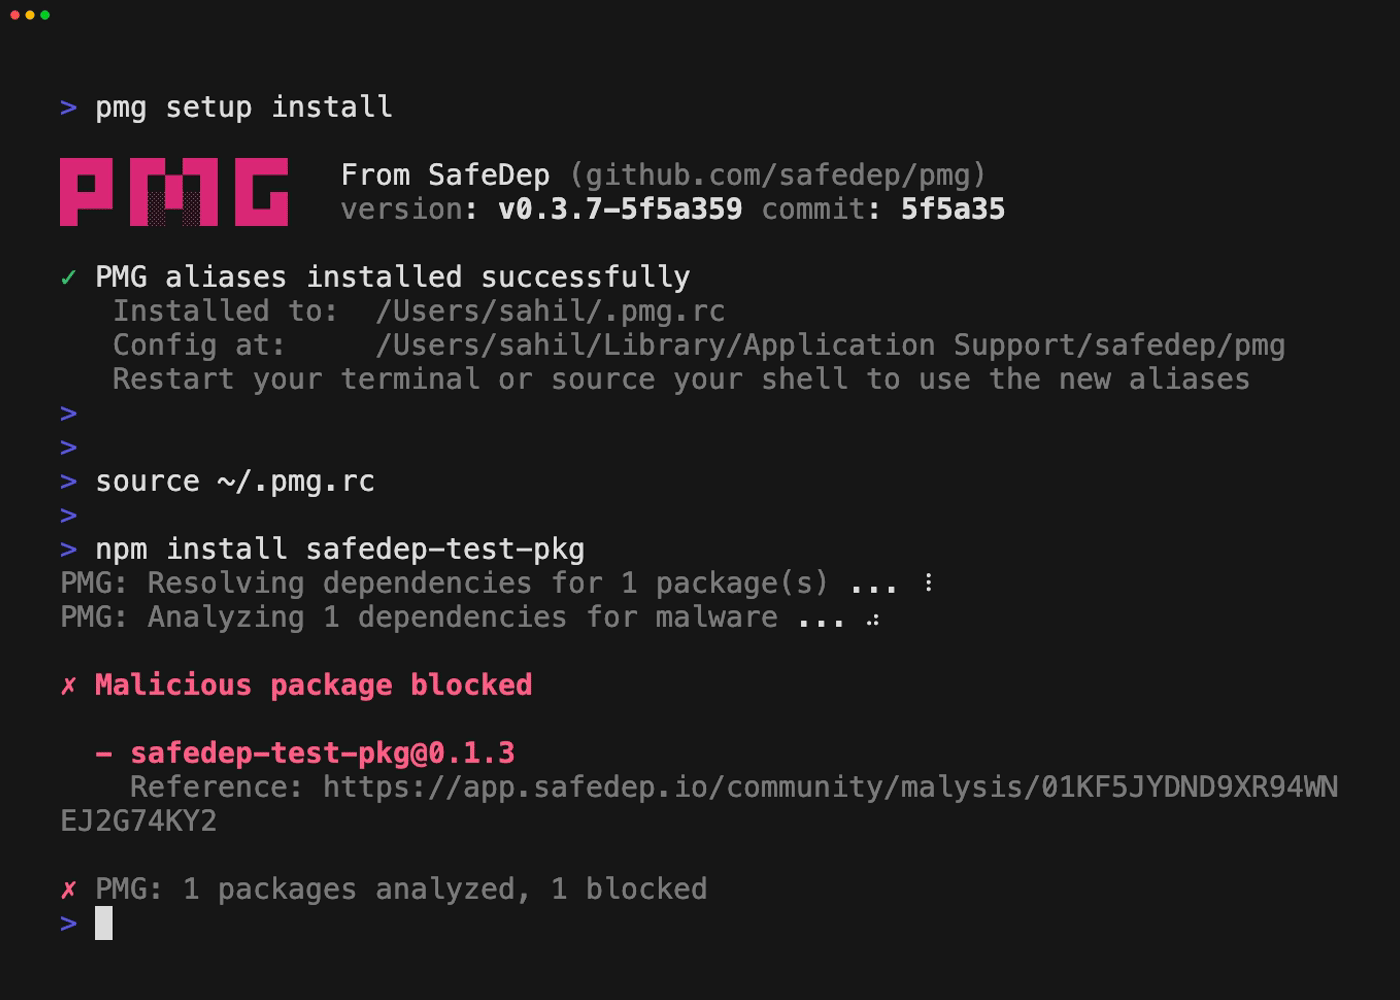 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
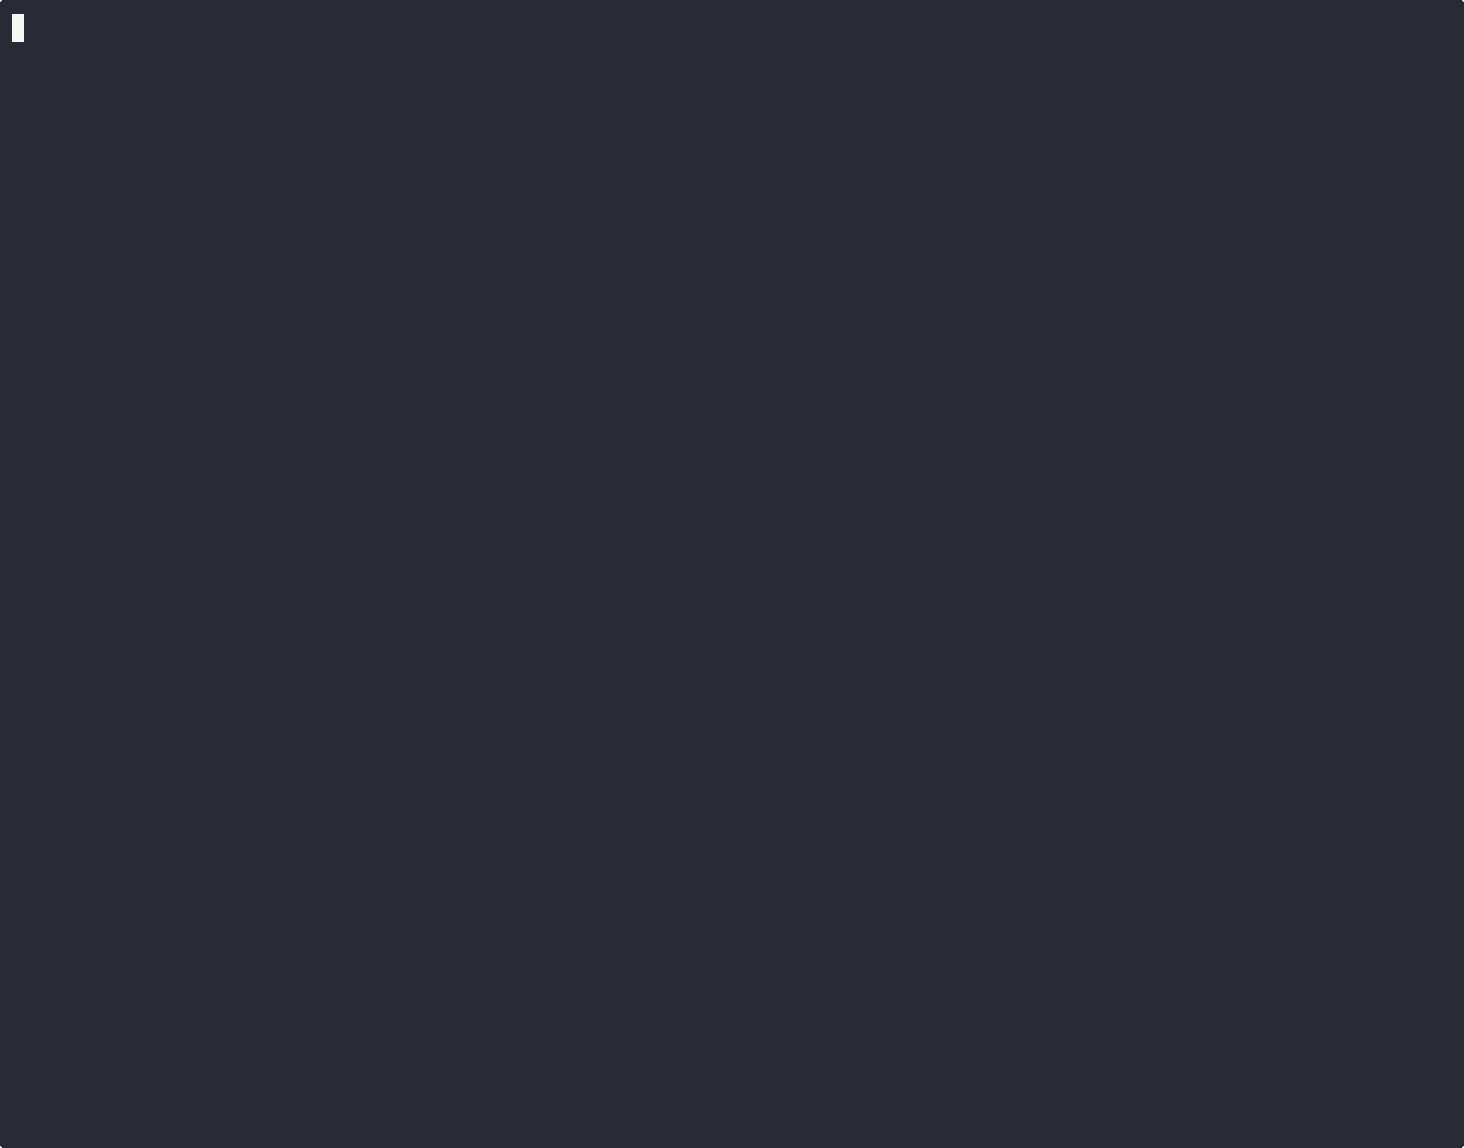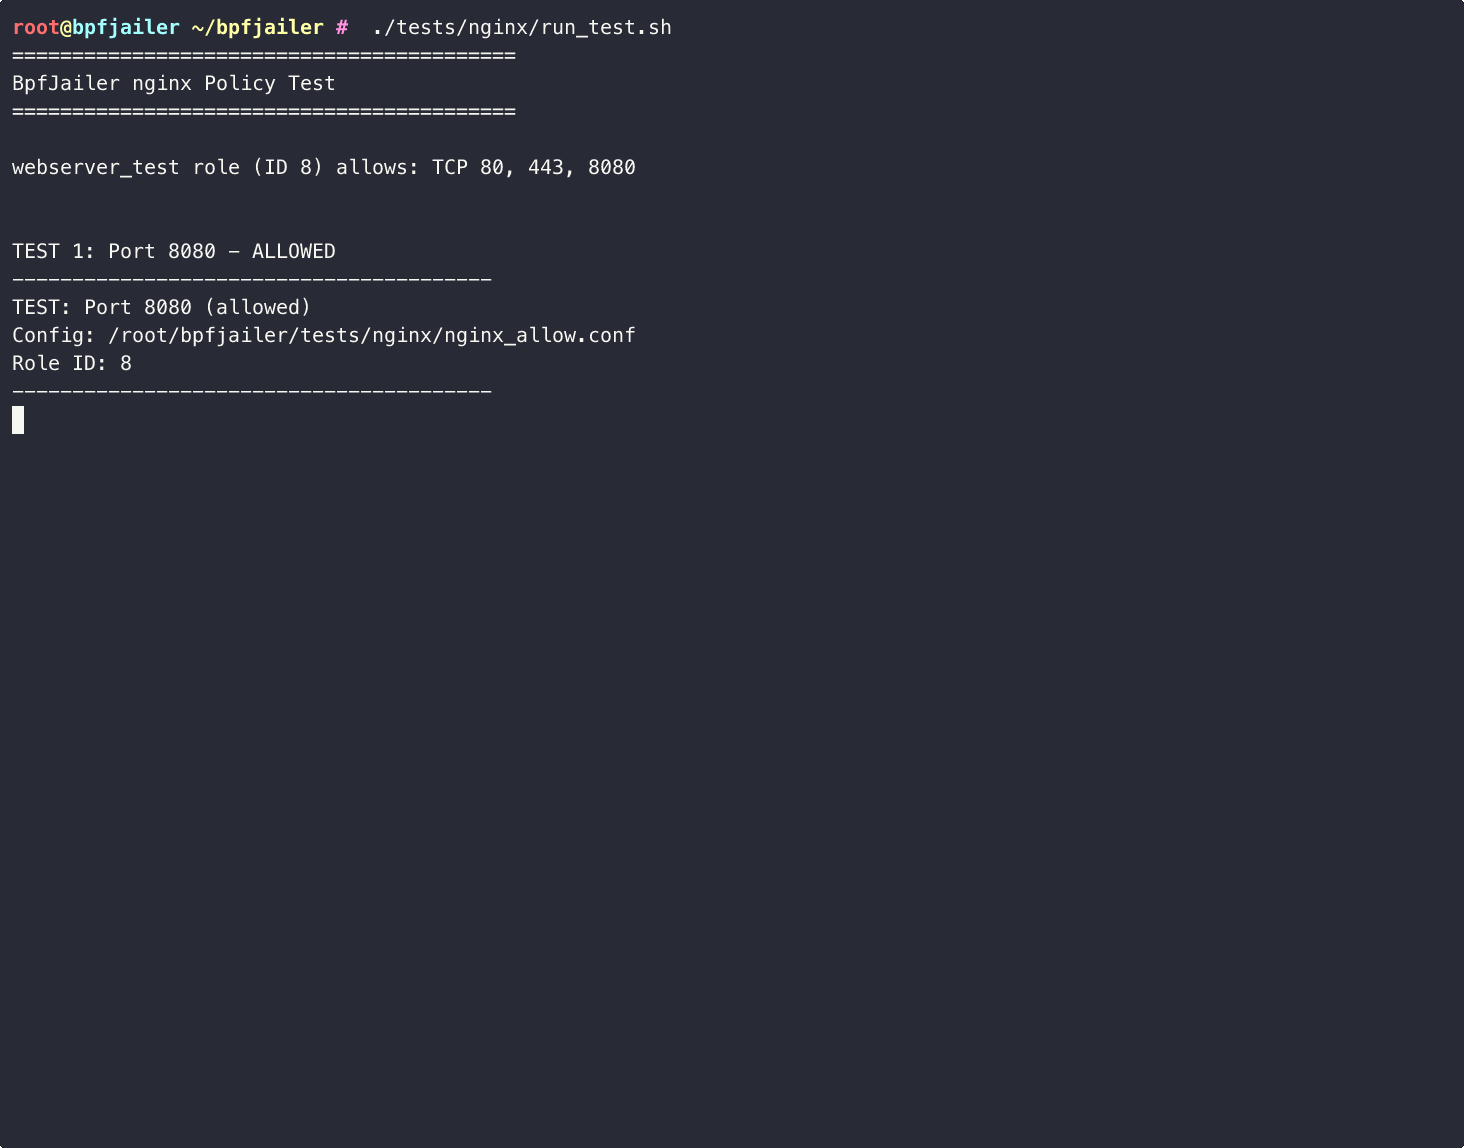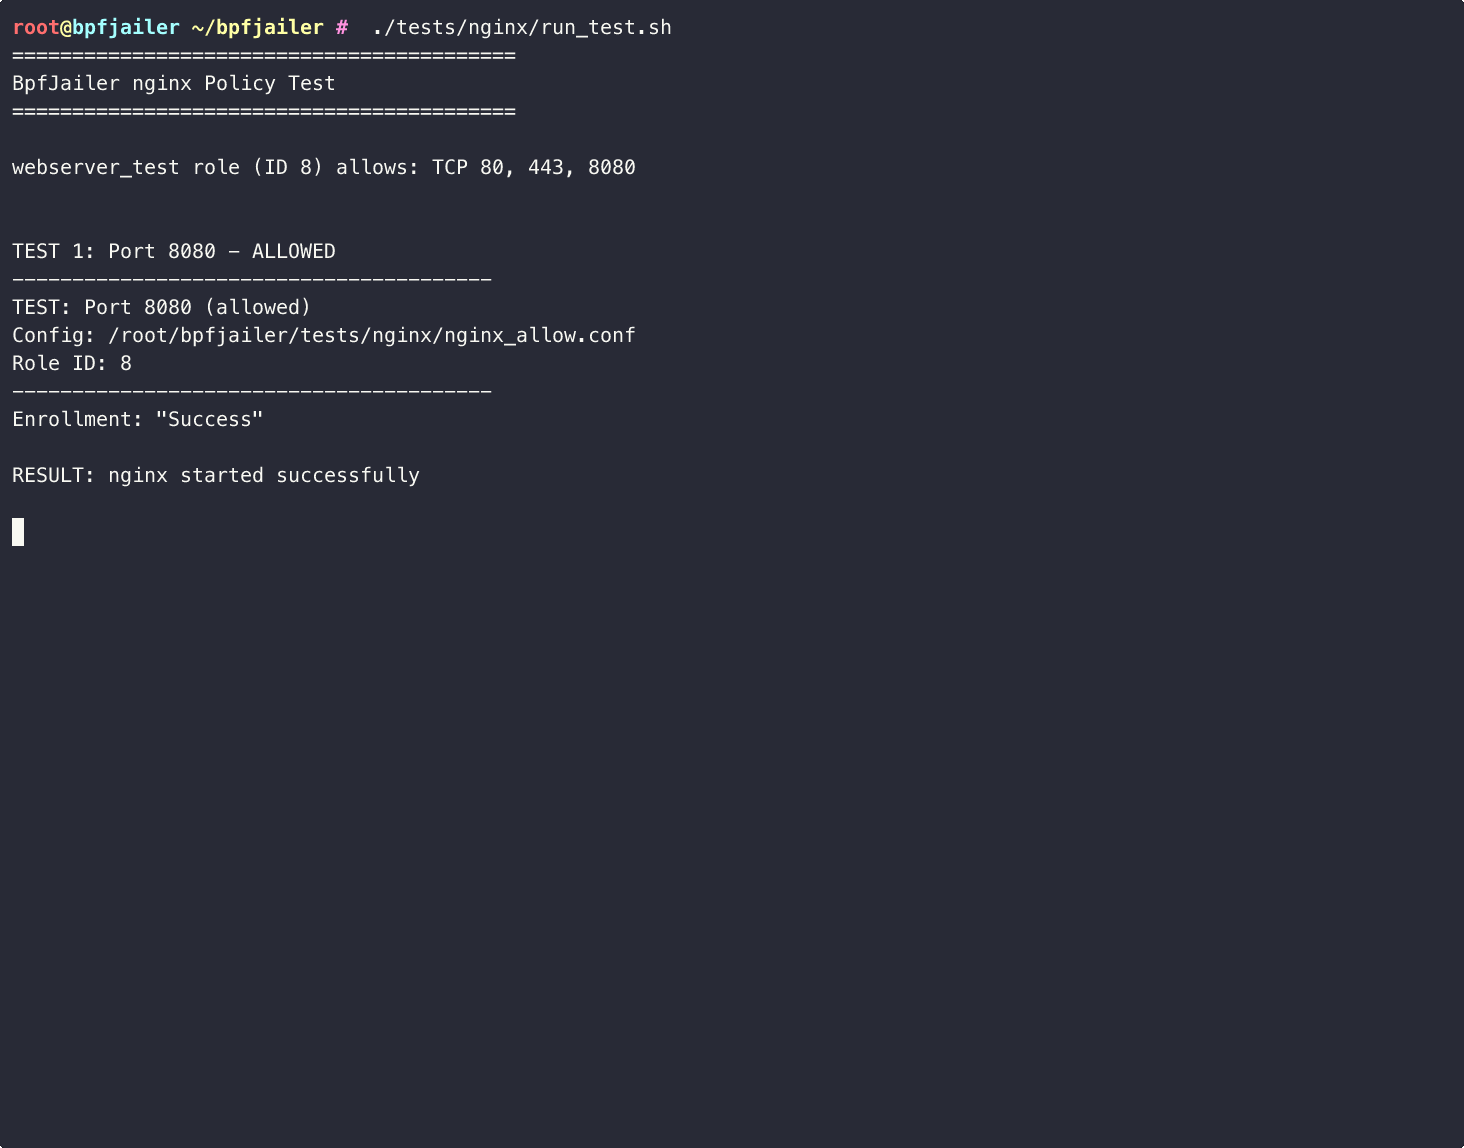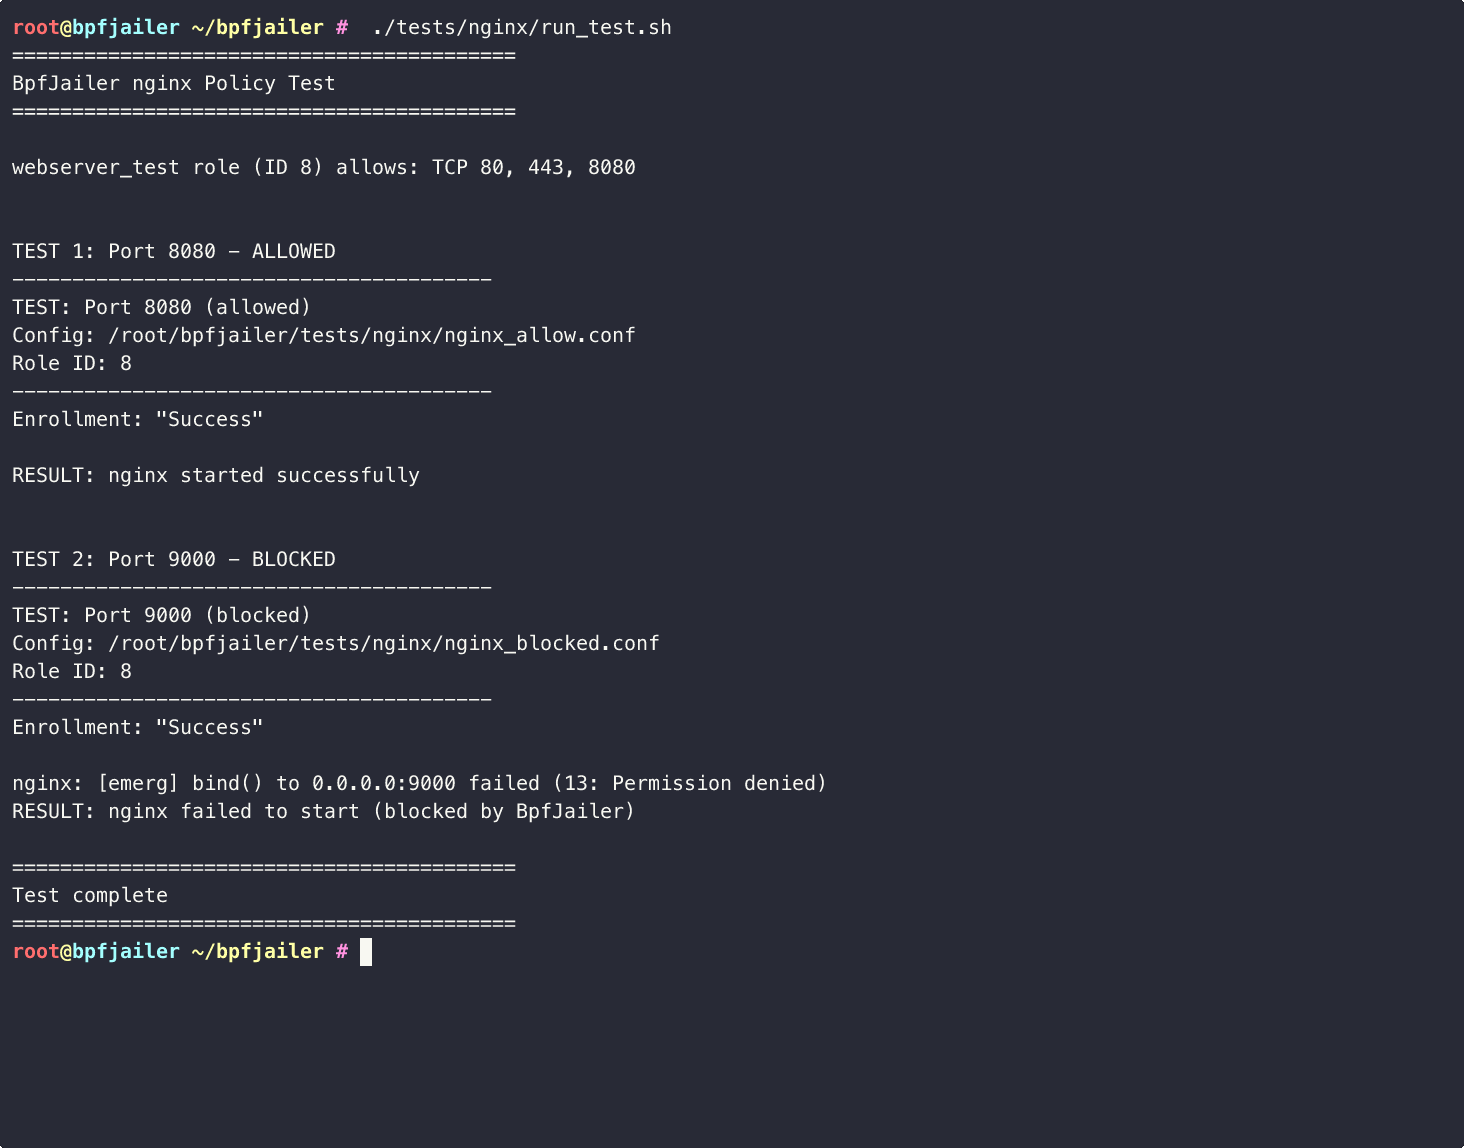 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
 aquasecurity/trivy-operator
Kubernetes-native security operator that automates vulnerability scanning, configuration auditing, secret detection, RBAC analysis, and compliance…
 joaovicdev/exploit-cve-2026-33634
Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…