terraform-aws-secure-baseline

Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…

Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…

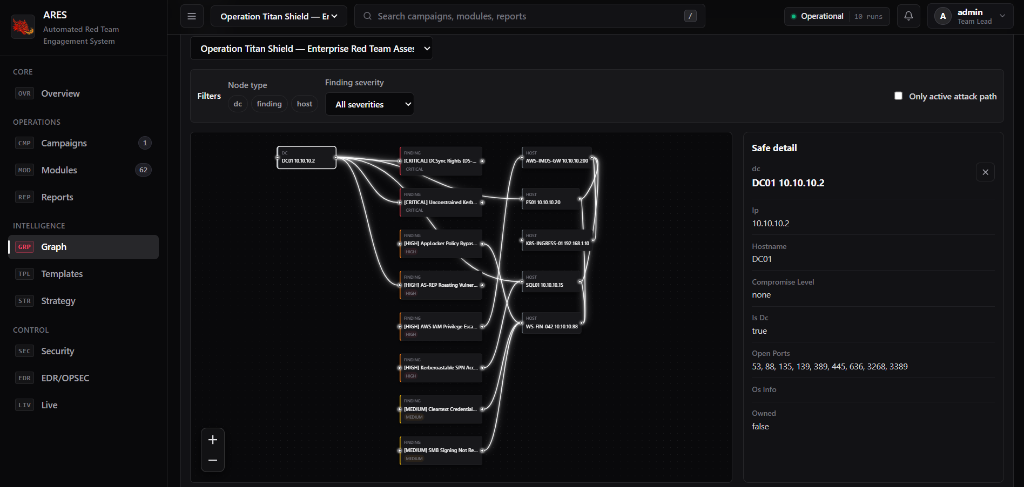
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…

SSH agent that creates and manages TPM-sealed keys for hardware-bound authentication, supporting key generation, import, wrapping, PIN protection,…

Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533

Identify privilege escalation paths within and across different clouds

Terraform module to manage AWS Security Groups. Currently, the ingress and egress rules support IPv4, IPv6, and Security Group ID inputs.

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.

CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具

Detection and mitigation tooling for CVE-2026-31431 (Copy Fail) on Linux kernels. Includes Phalanx-CCS and Silent4Labs scripts plus an Ansible…

Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…

Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…

PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…

PowerShell module for Office 365 and Azure log collection

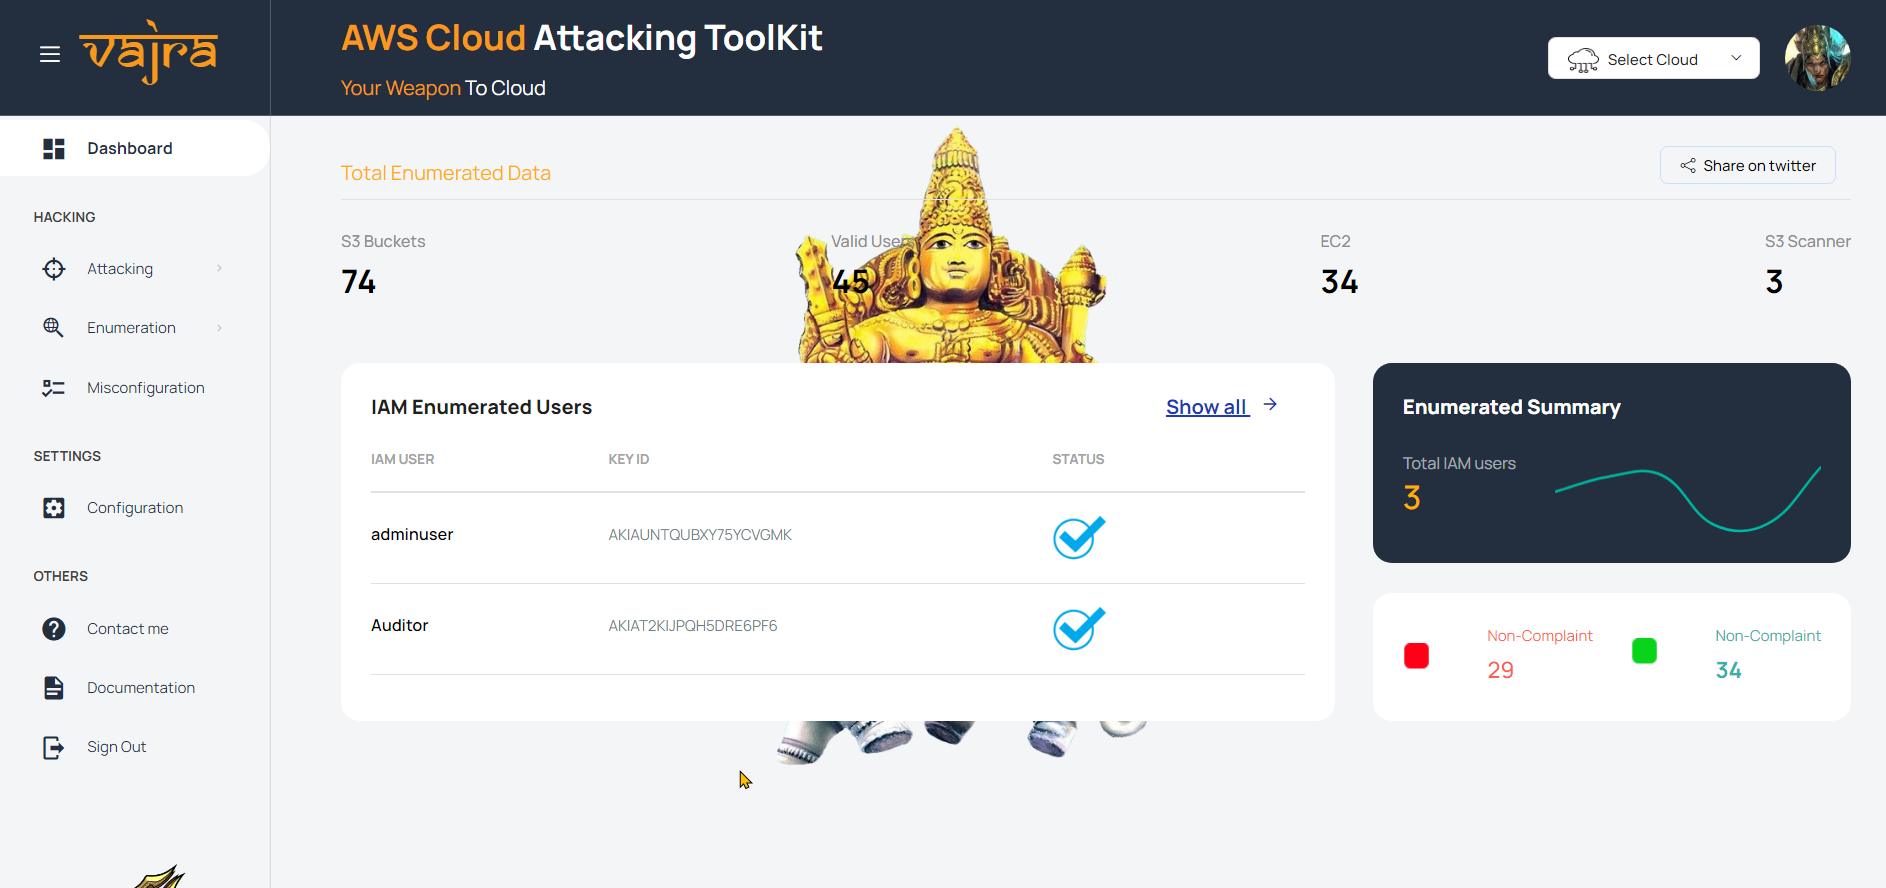
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…

OWASP Domain Protect - prevent subdomain takeover

Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…

Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…

The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…