

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17k22h 26m ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…

 scille/parsec-cloud
Open source Dropbox-like file sharing with full client encryption !
 microsoft/igvm
Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…
 pgbackrest/pgbackrest
Parallel backup and restore solution for PostgreSQL with encryption, delta restore, and multi-cloud object store support for enterprise disaster…
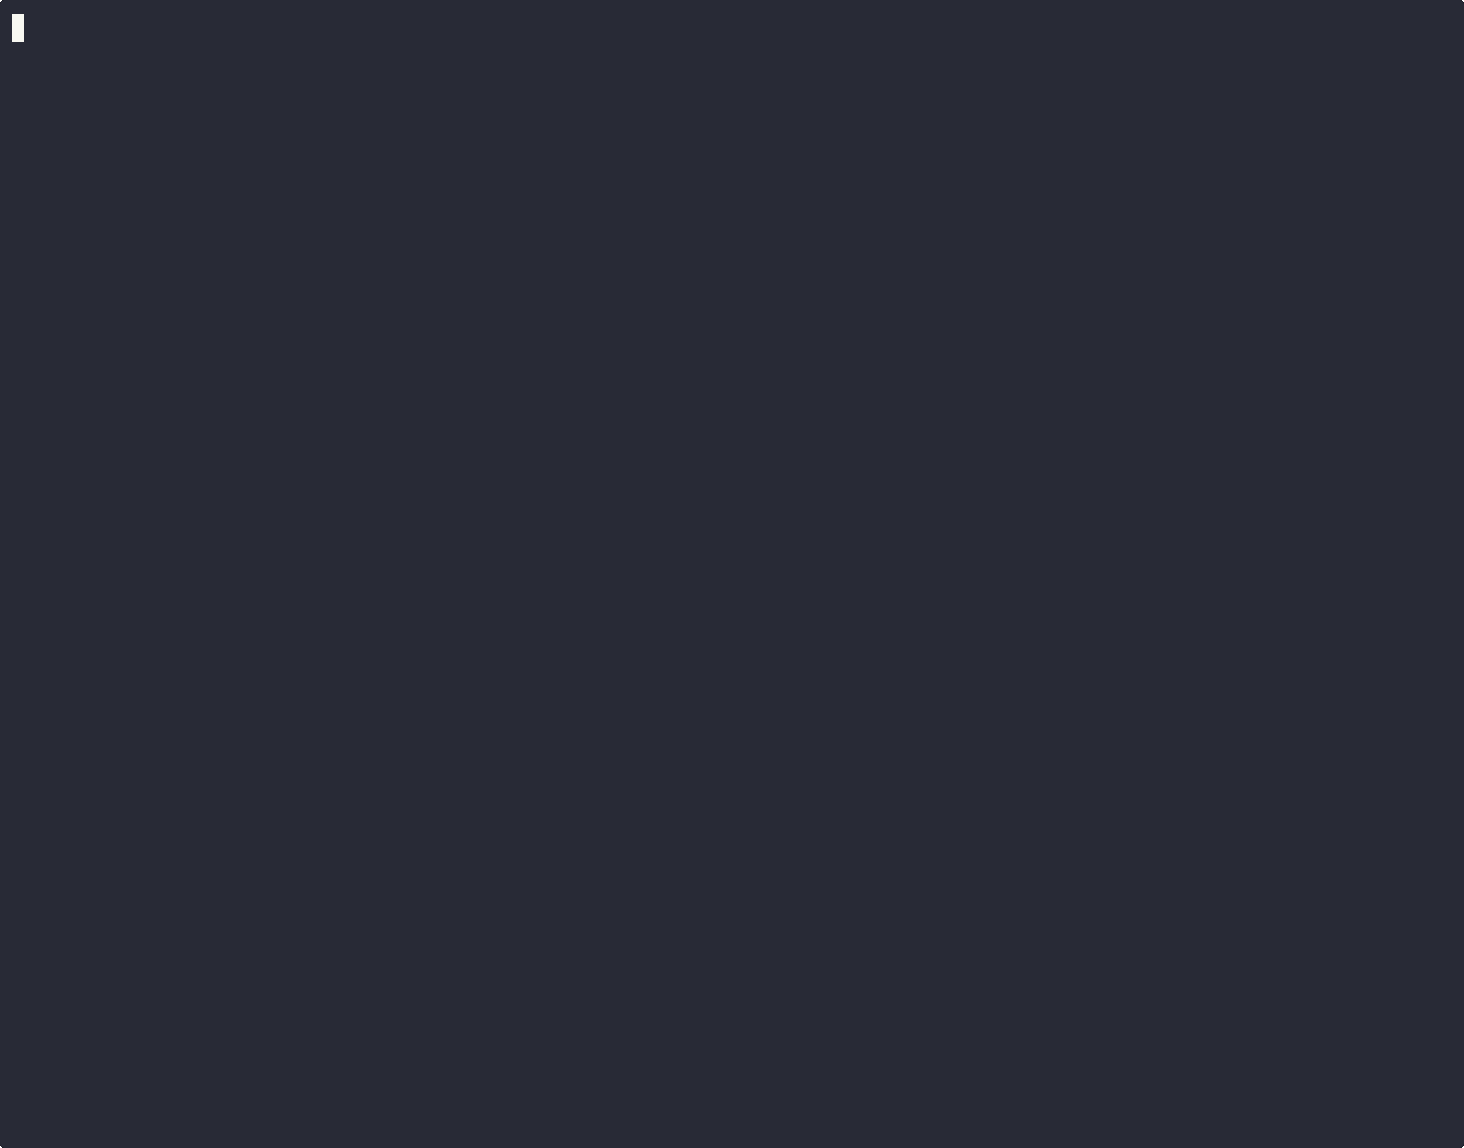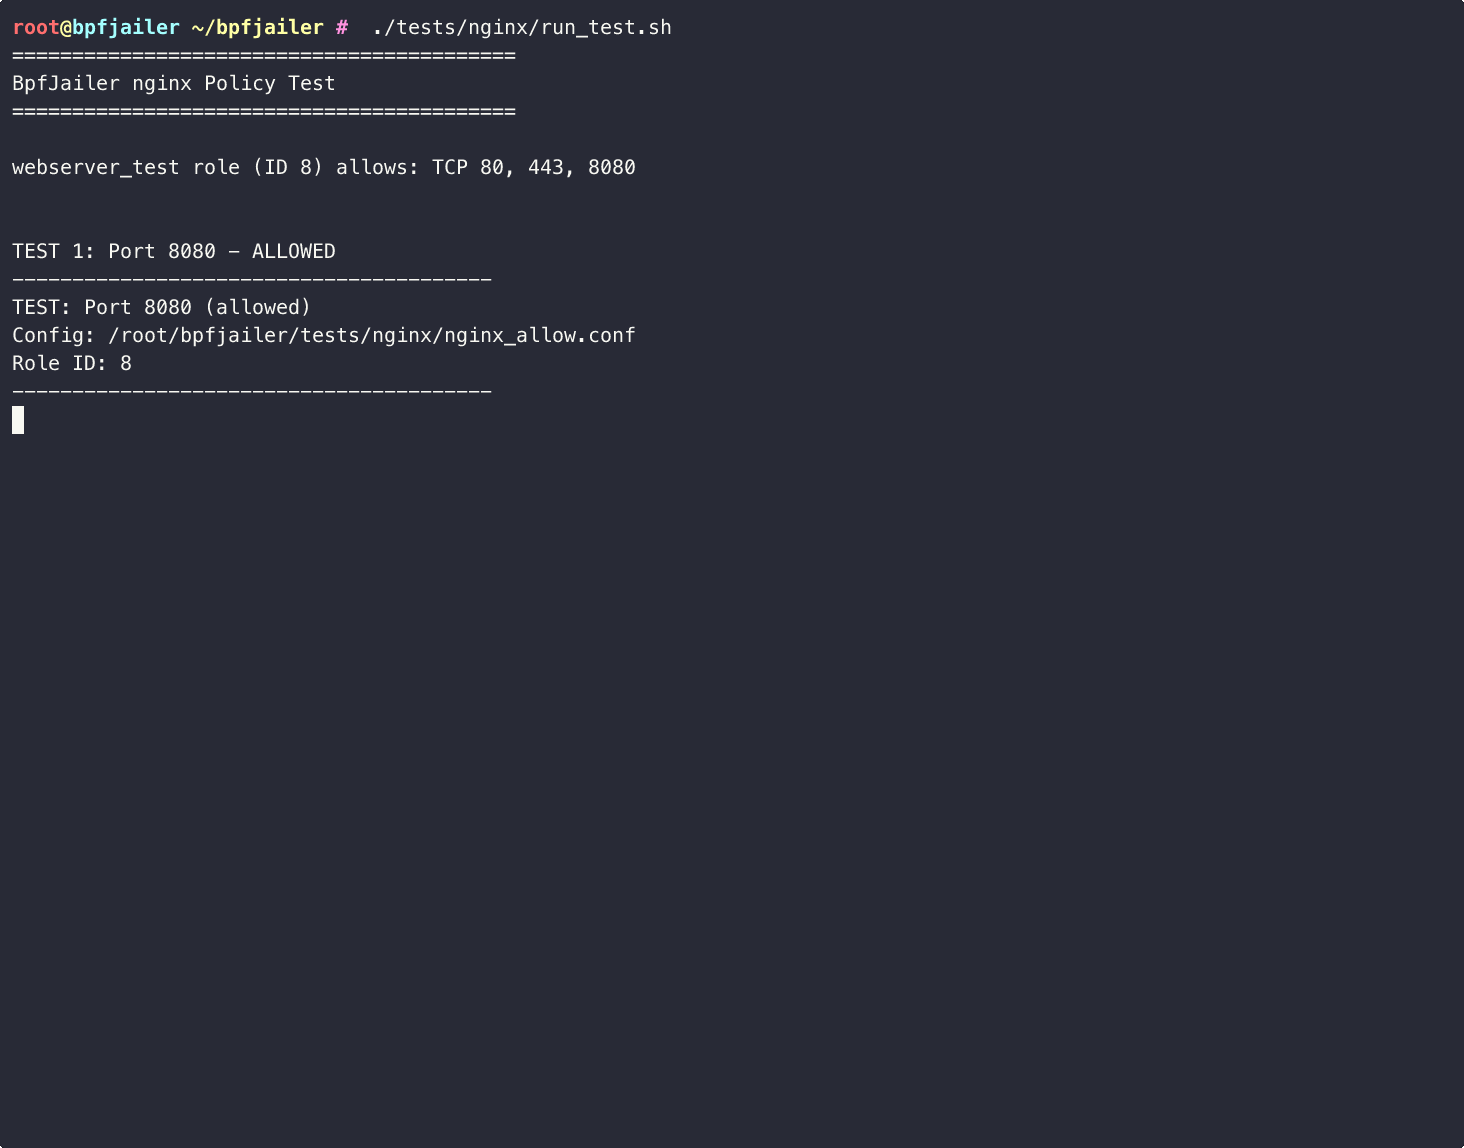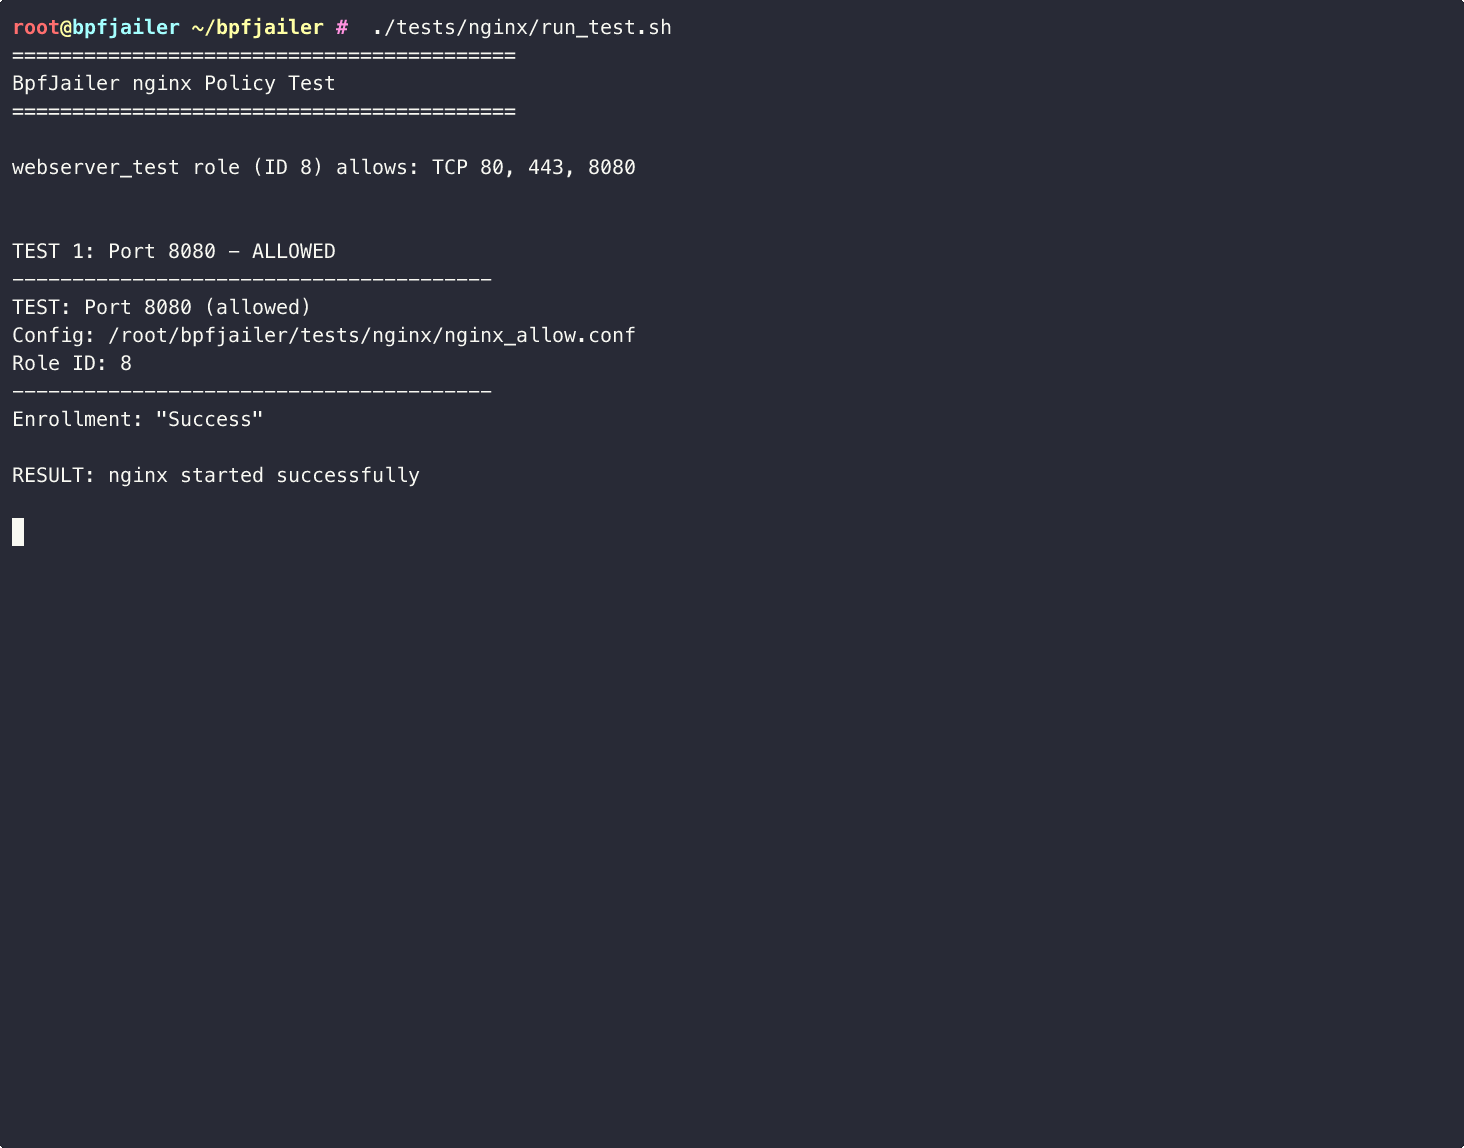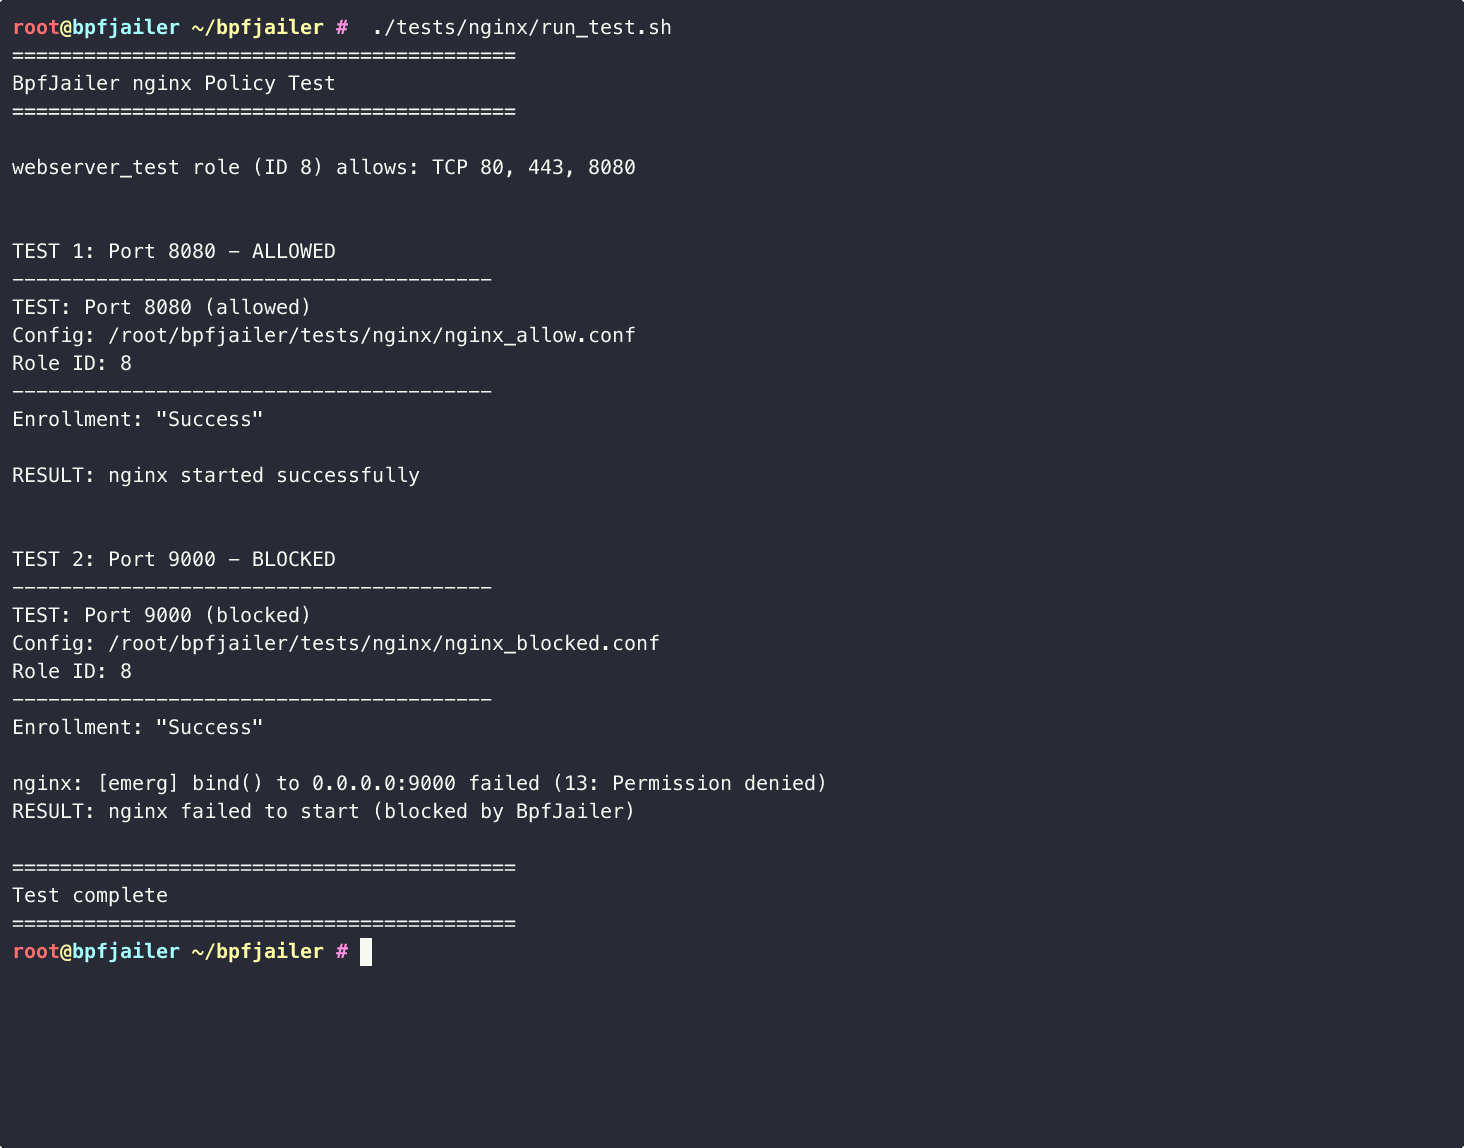 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 ustayready/thunderstorm
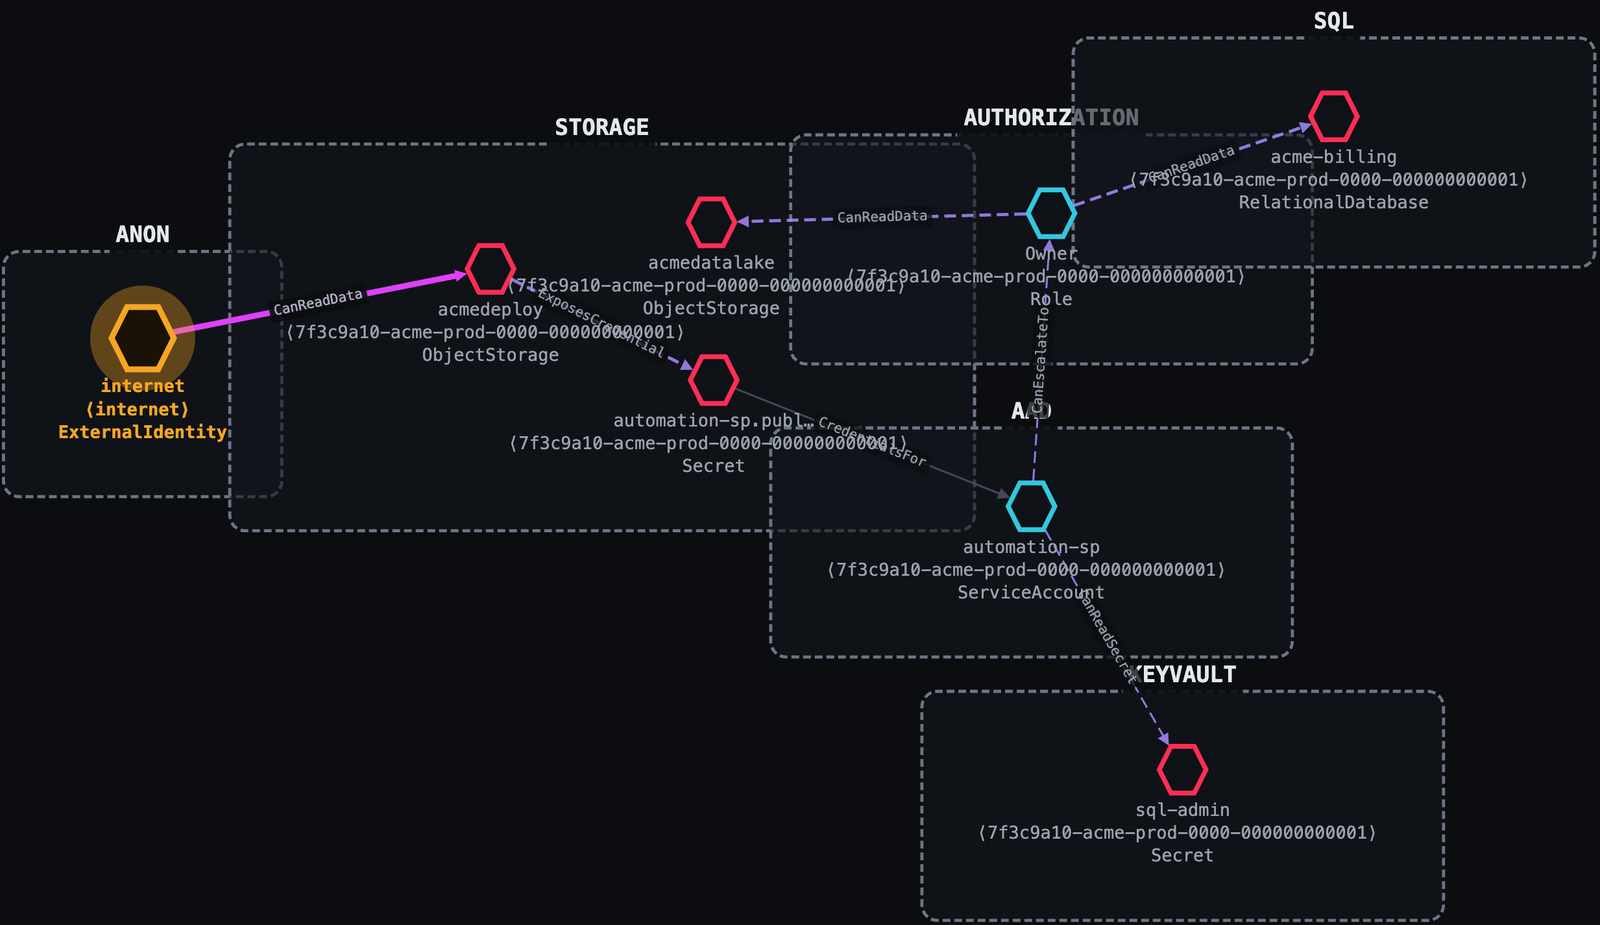
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 leitwacht/leitwacht-agent
eBPF + nftables + DNS proxy egress enforcement for GitLab Runner CI/CD job containers — community edition data plane https://leitwacht.eu/
 h3ck13r/cve-2026-35204
Proof-of-concept demonstrating a path traversal vulnerability (CVE-2026-35204) in Helm plugin installation, allowing arbitrary file write via crafted…
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
 dshamany/privatesphare
An at-rest encrypted filesharing application with multiple clients who seek to share privately, without tracking.
 fran314/secrets-manager-rs
A command-line tool for securely backing up, restoring, and verifying secrets using interoperable standards like age encryption and coreutils,…
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…