
Dark-Moon
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
ai-securitycloud-securitydevsecops+6
968
ascit31/dark-moonAutonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 mvelazc0/badzure
BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
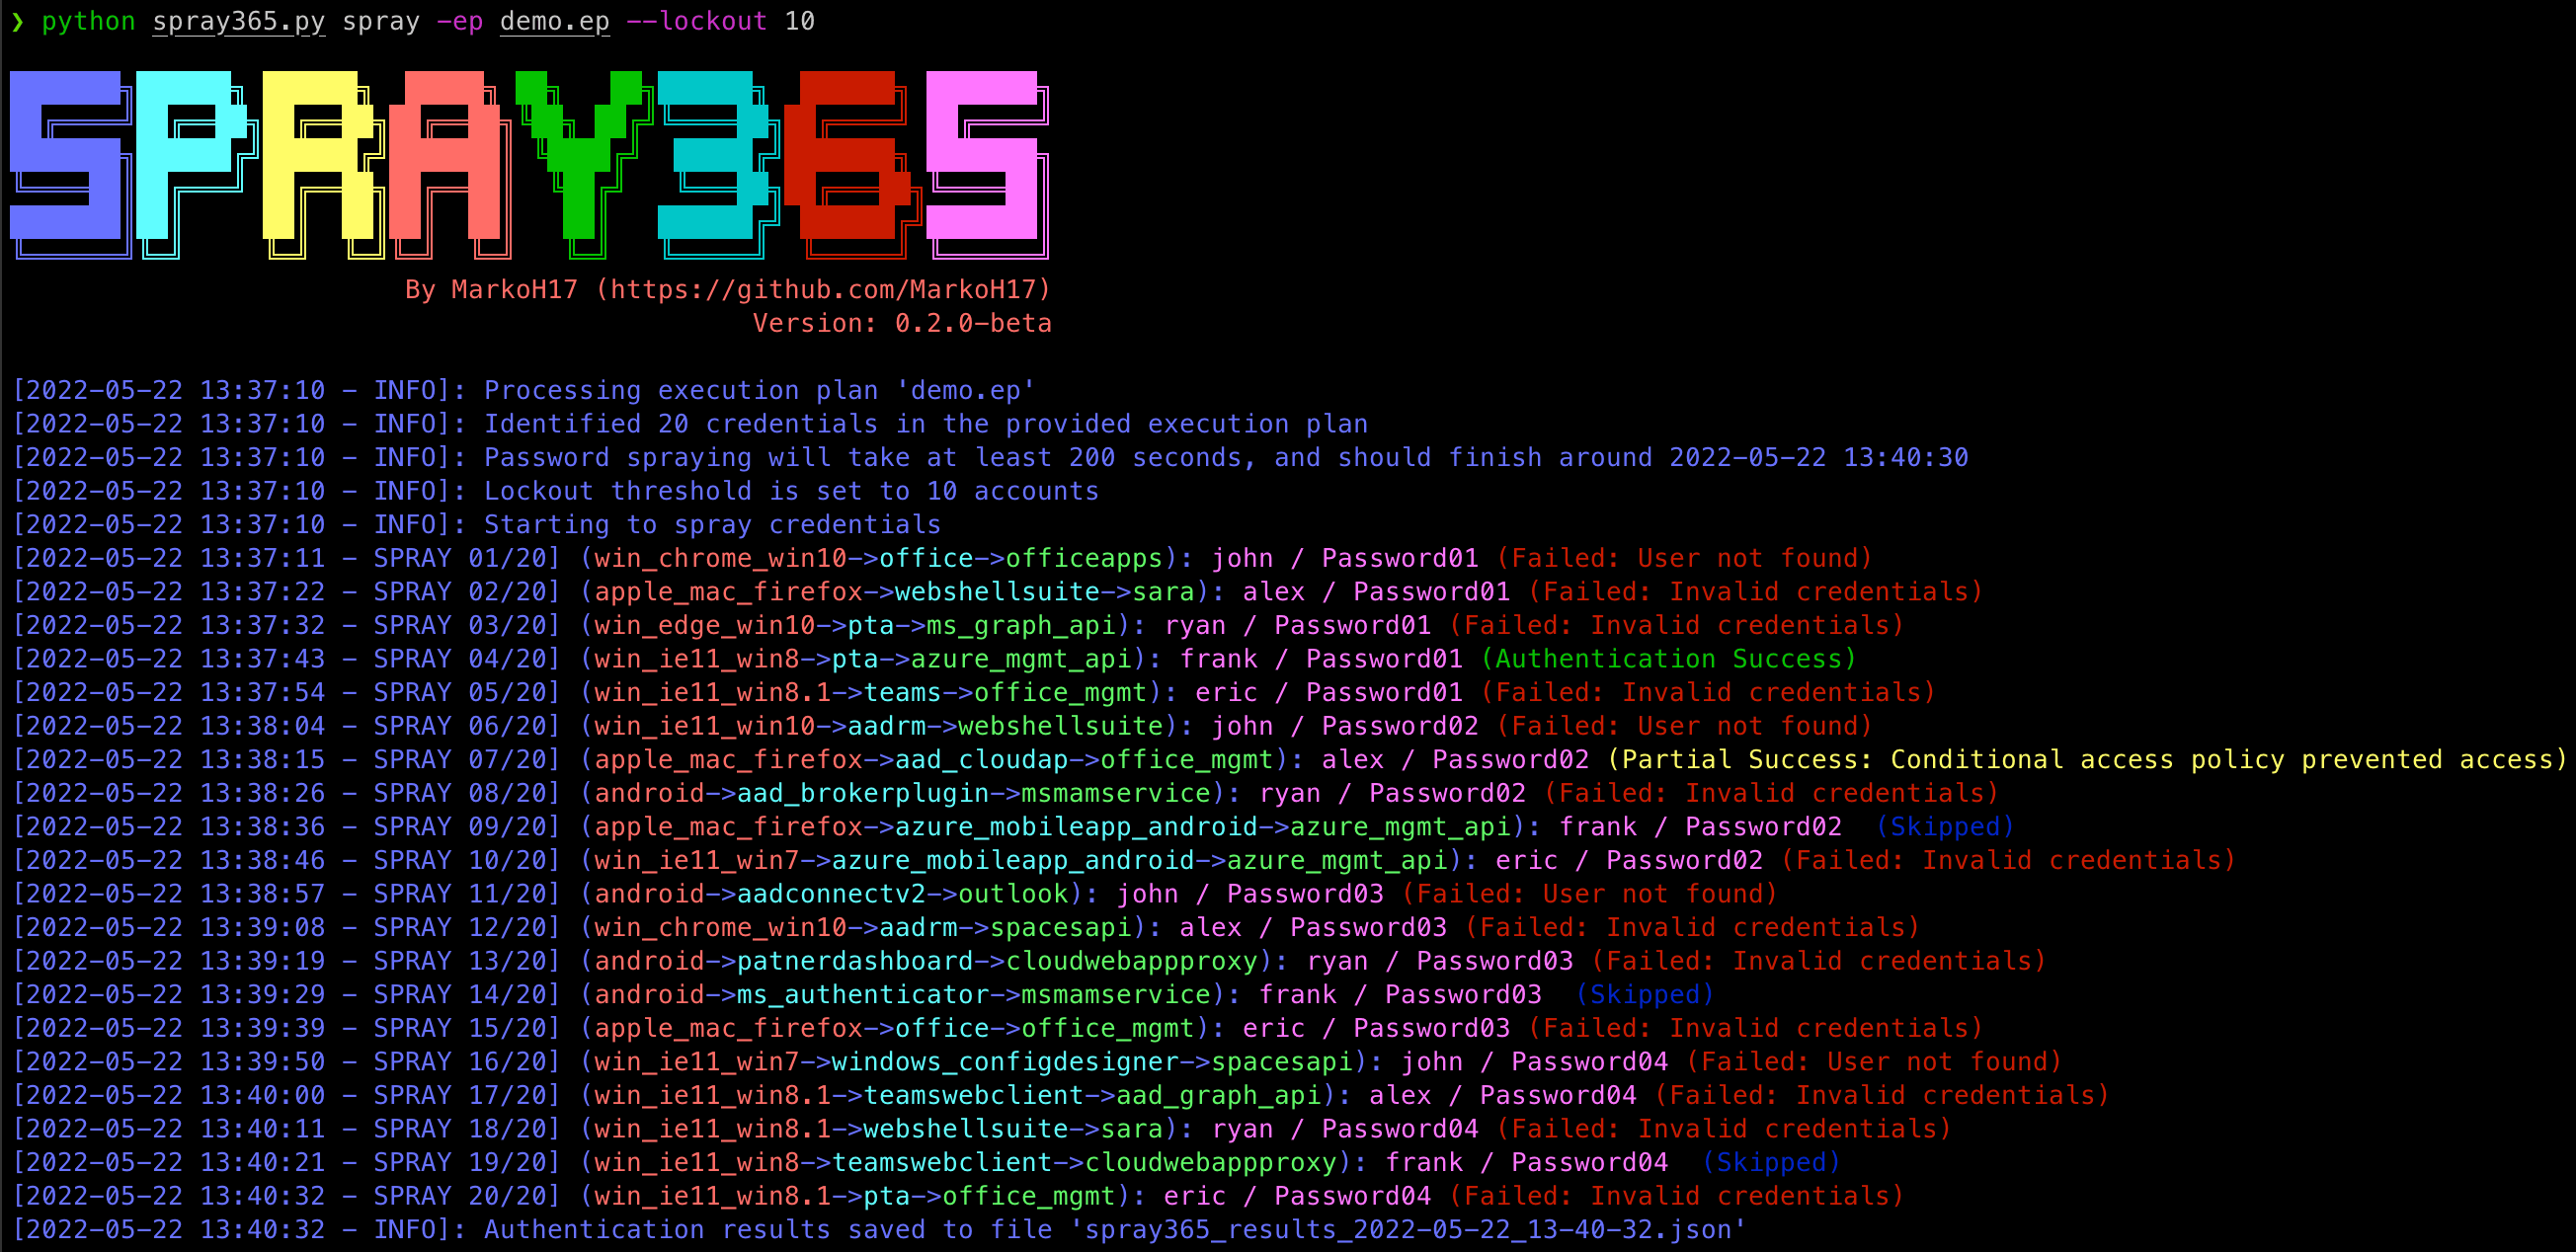 markoh17/spray365
Spray365 makes spraying Microsoft accounts (Office 365 / Azure AD) easy through its customizable two-step password spraying approach. The built-in…
 ajf8729/blacklotus
BlackLotus aka CVE-2023-24932 Detection/Remediation Scripts for Intune, ConfigMgr, and generic use
 spyata123/cve-2023-3128
Python script to detect CVE-2023-3128 authentication bypass in Grafana via Azure AD email claim validation. Checks Azure AD SSO configuration and…
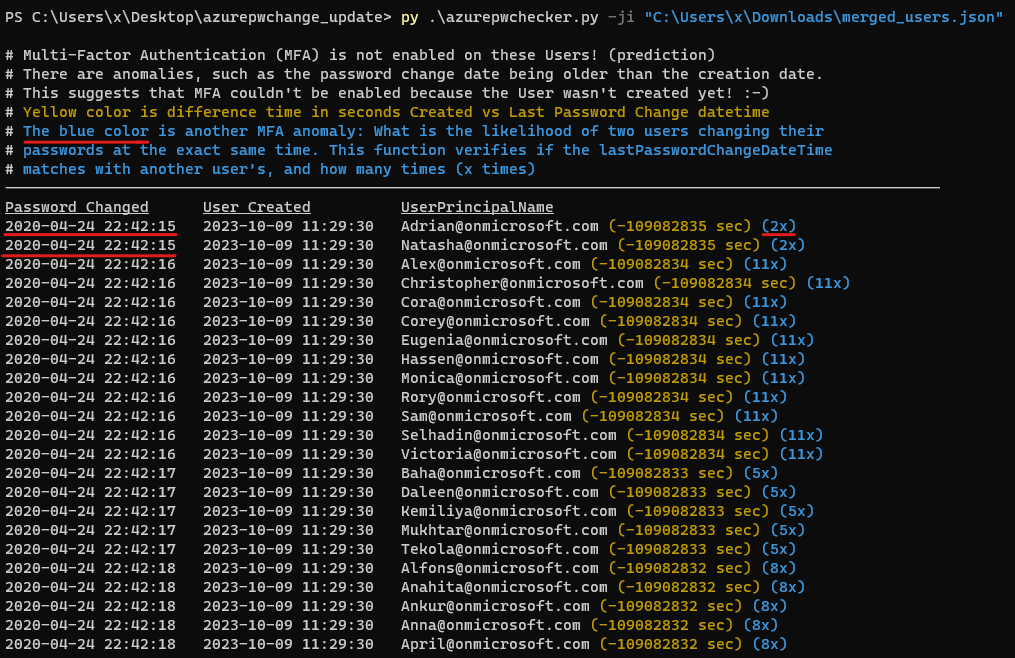 quahac/azure-ad-password-checker
Azure AD Password Checker
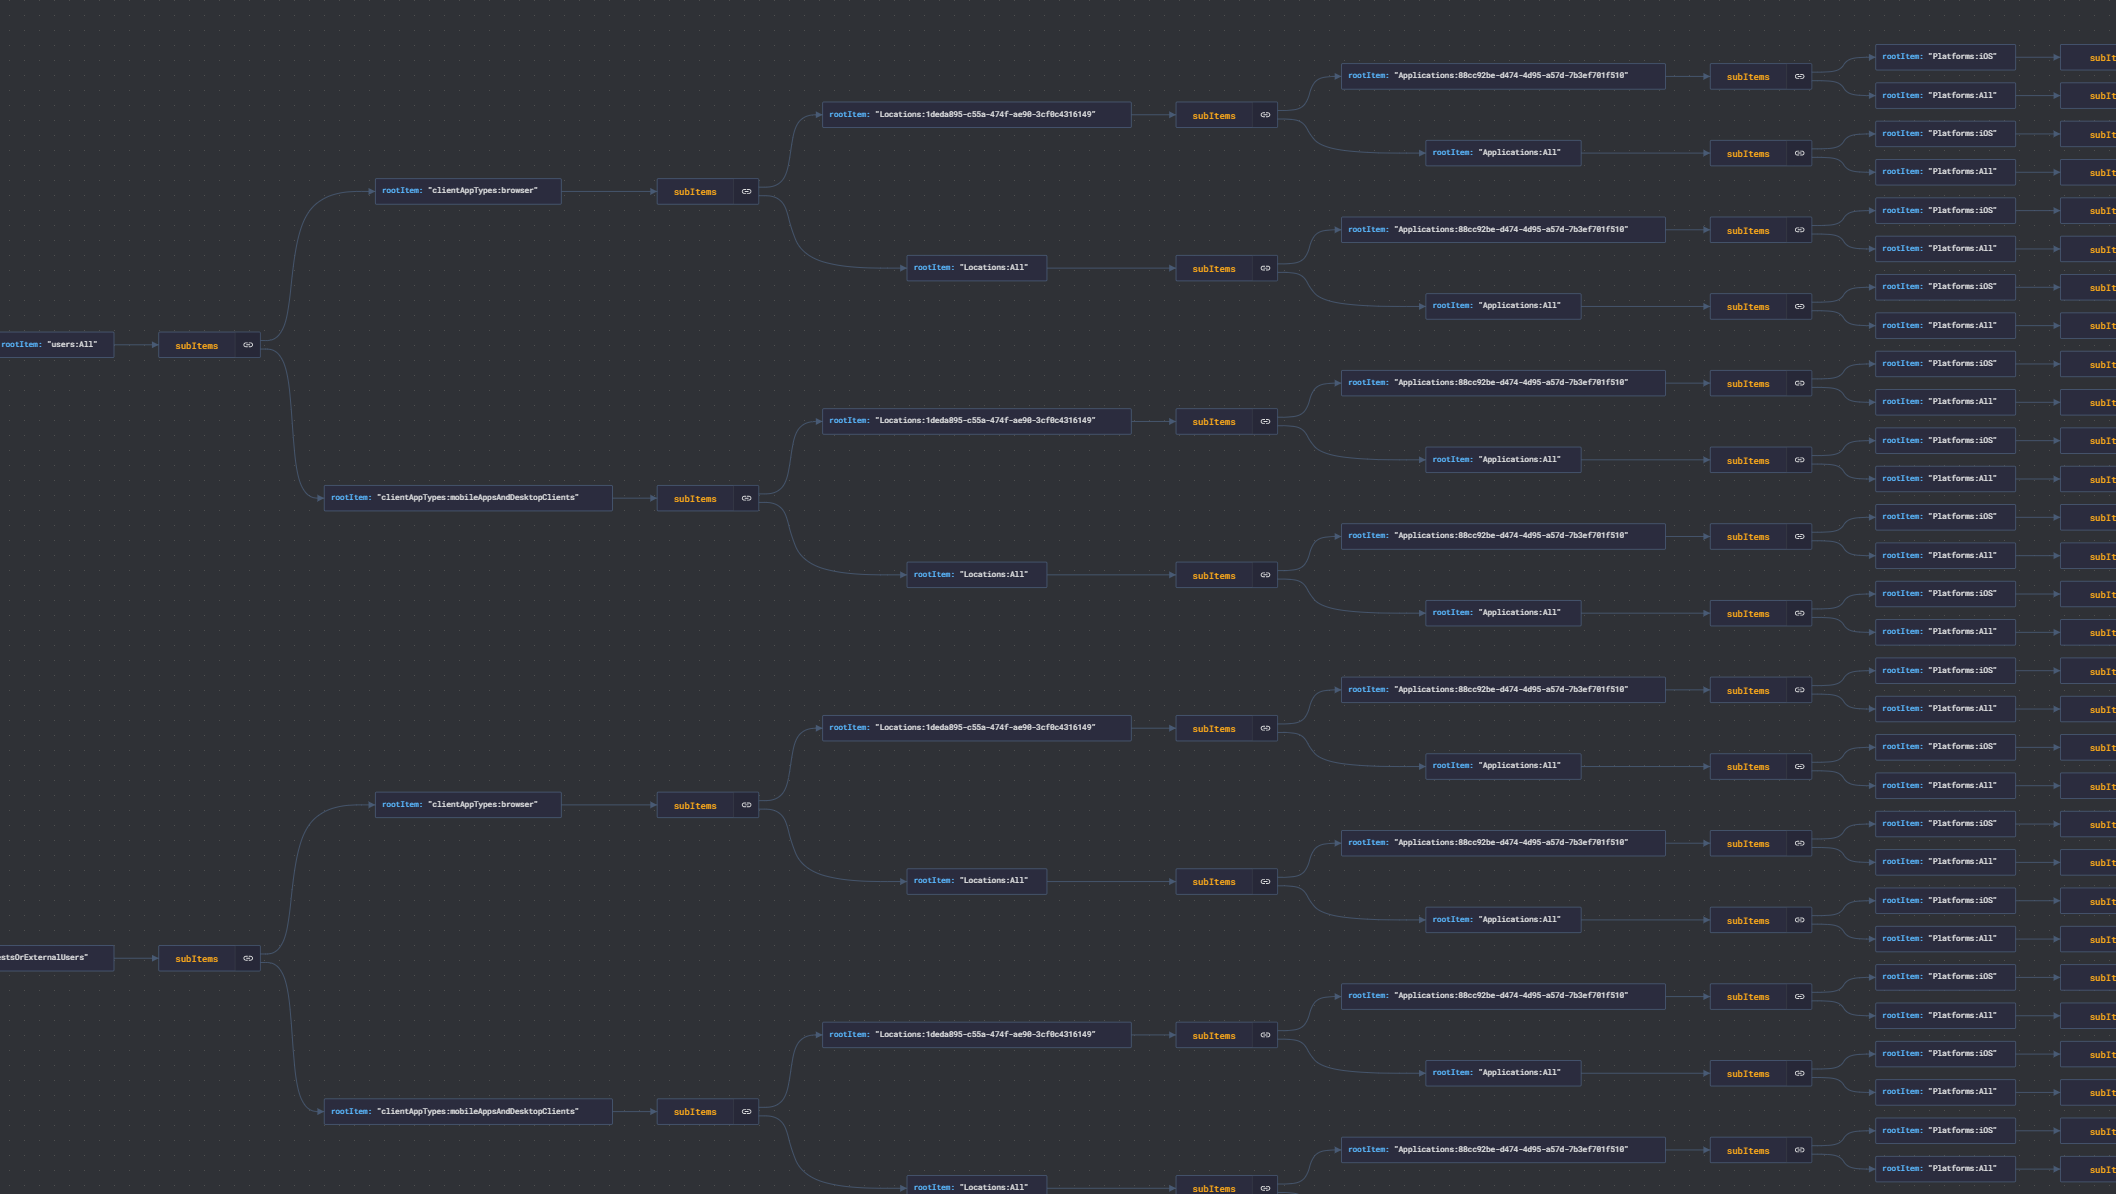 jsa2/caoptics
CA Optics - Azure AD Conditional Access Gap Analyzer
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
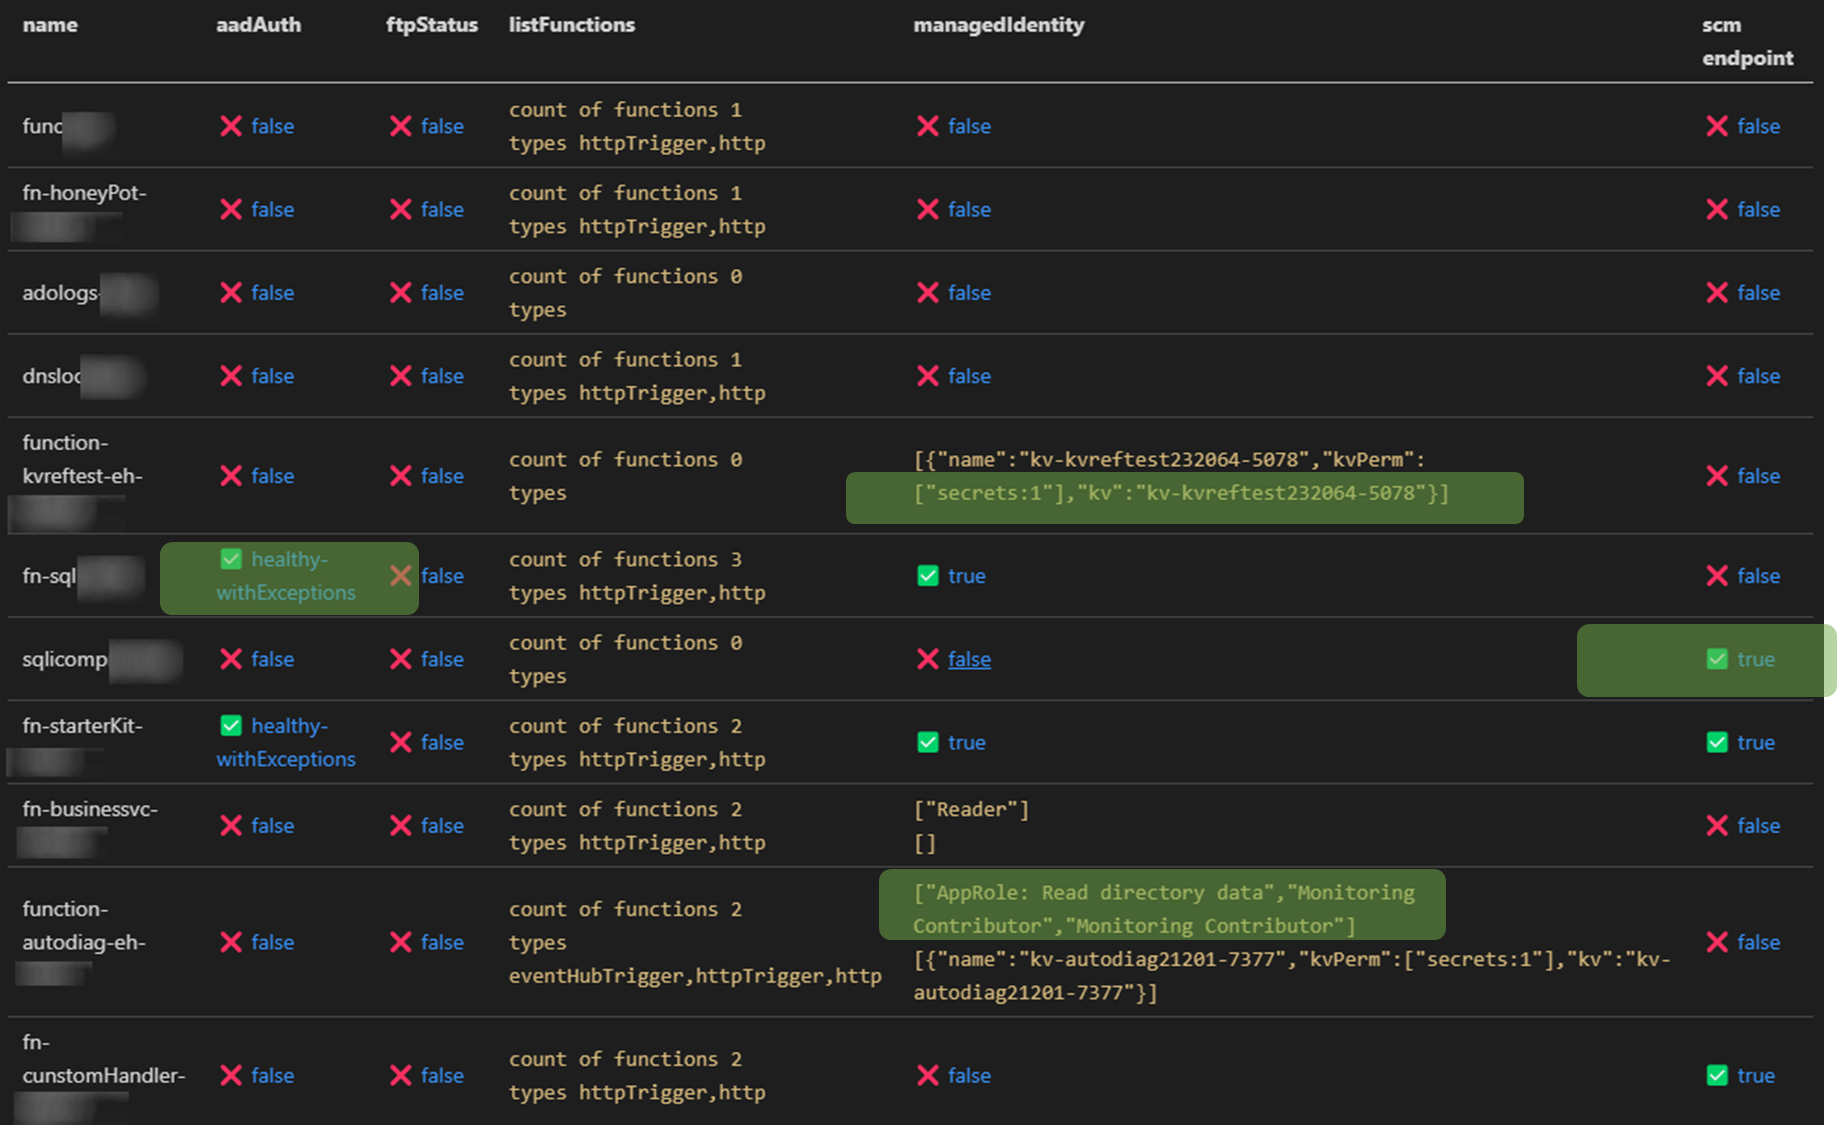 jsa2/east
Extensible Azure Security Tool - Documentation
 crowdstrike/crt
Audits Azure AD and Exchange Online configurations for hard-to-find permissions, federation trusts, mail forwarding rules, and delegated access to…
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…