
minimal
 rtvkiz/minimal
Minimal CVE Hardened container image collection
vulnerability-scannerscontainer-securityconfiguration-auditing+3
rtvkiz/minimalMinimal CVE Hardened container image collection
 kviklet/kviklet
Pull Request-like Review/Approval flow for database queries. For compliant but smooth Engineering access to production.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 nilsteampassnet/teampass
Collaborative Passwords Manager
 salesforce/cloudsplaining
Cloudsplaining is an AWS IAM Security Assessment tool that identifies violations of least privilege and generates a risk-prioritized report.
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 resiprocate/resiprocate
C++ implementation of SIP, ICE, TURN and related protocols.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 traccar/traccar
Traccar GPS Tracking System
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
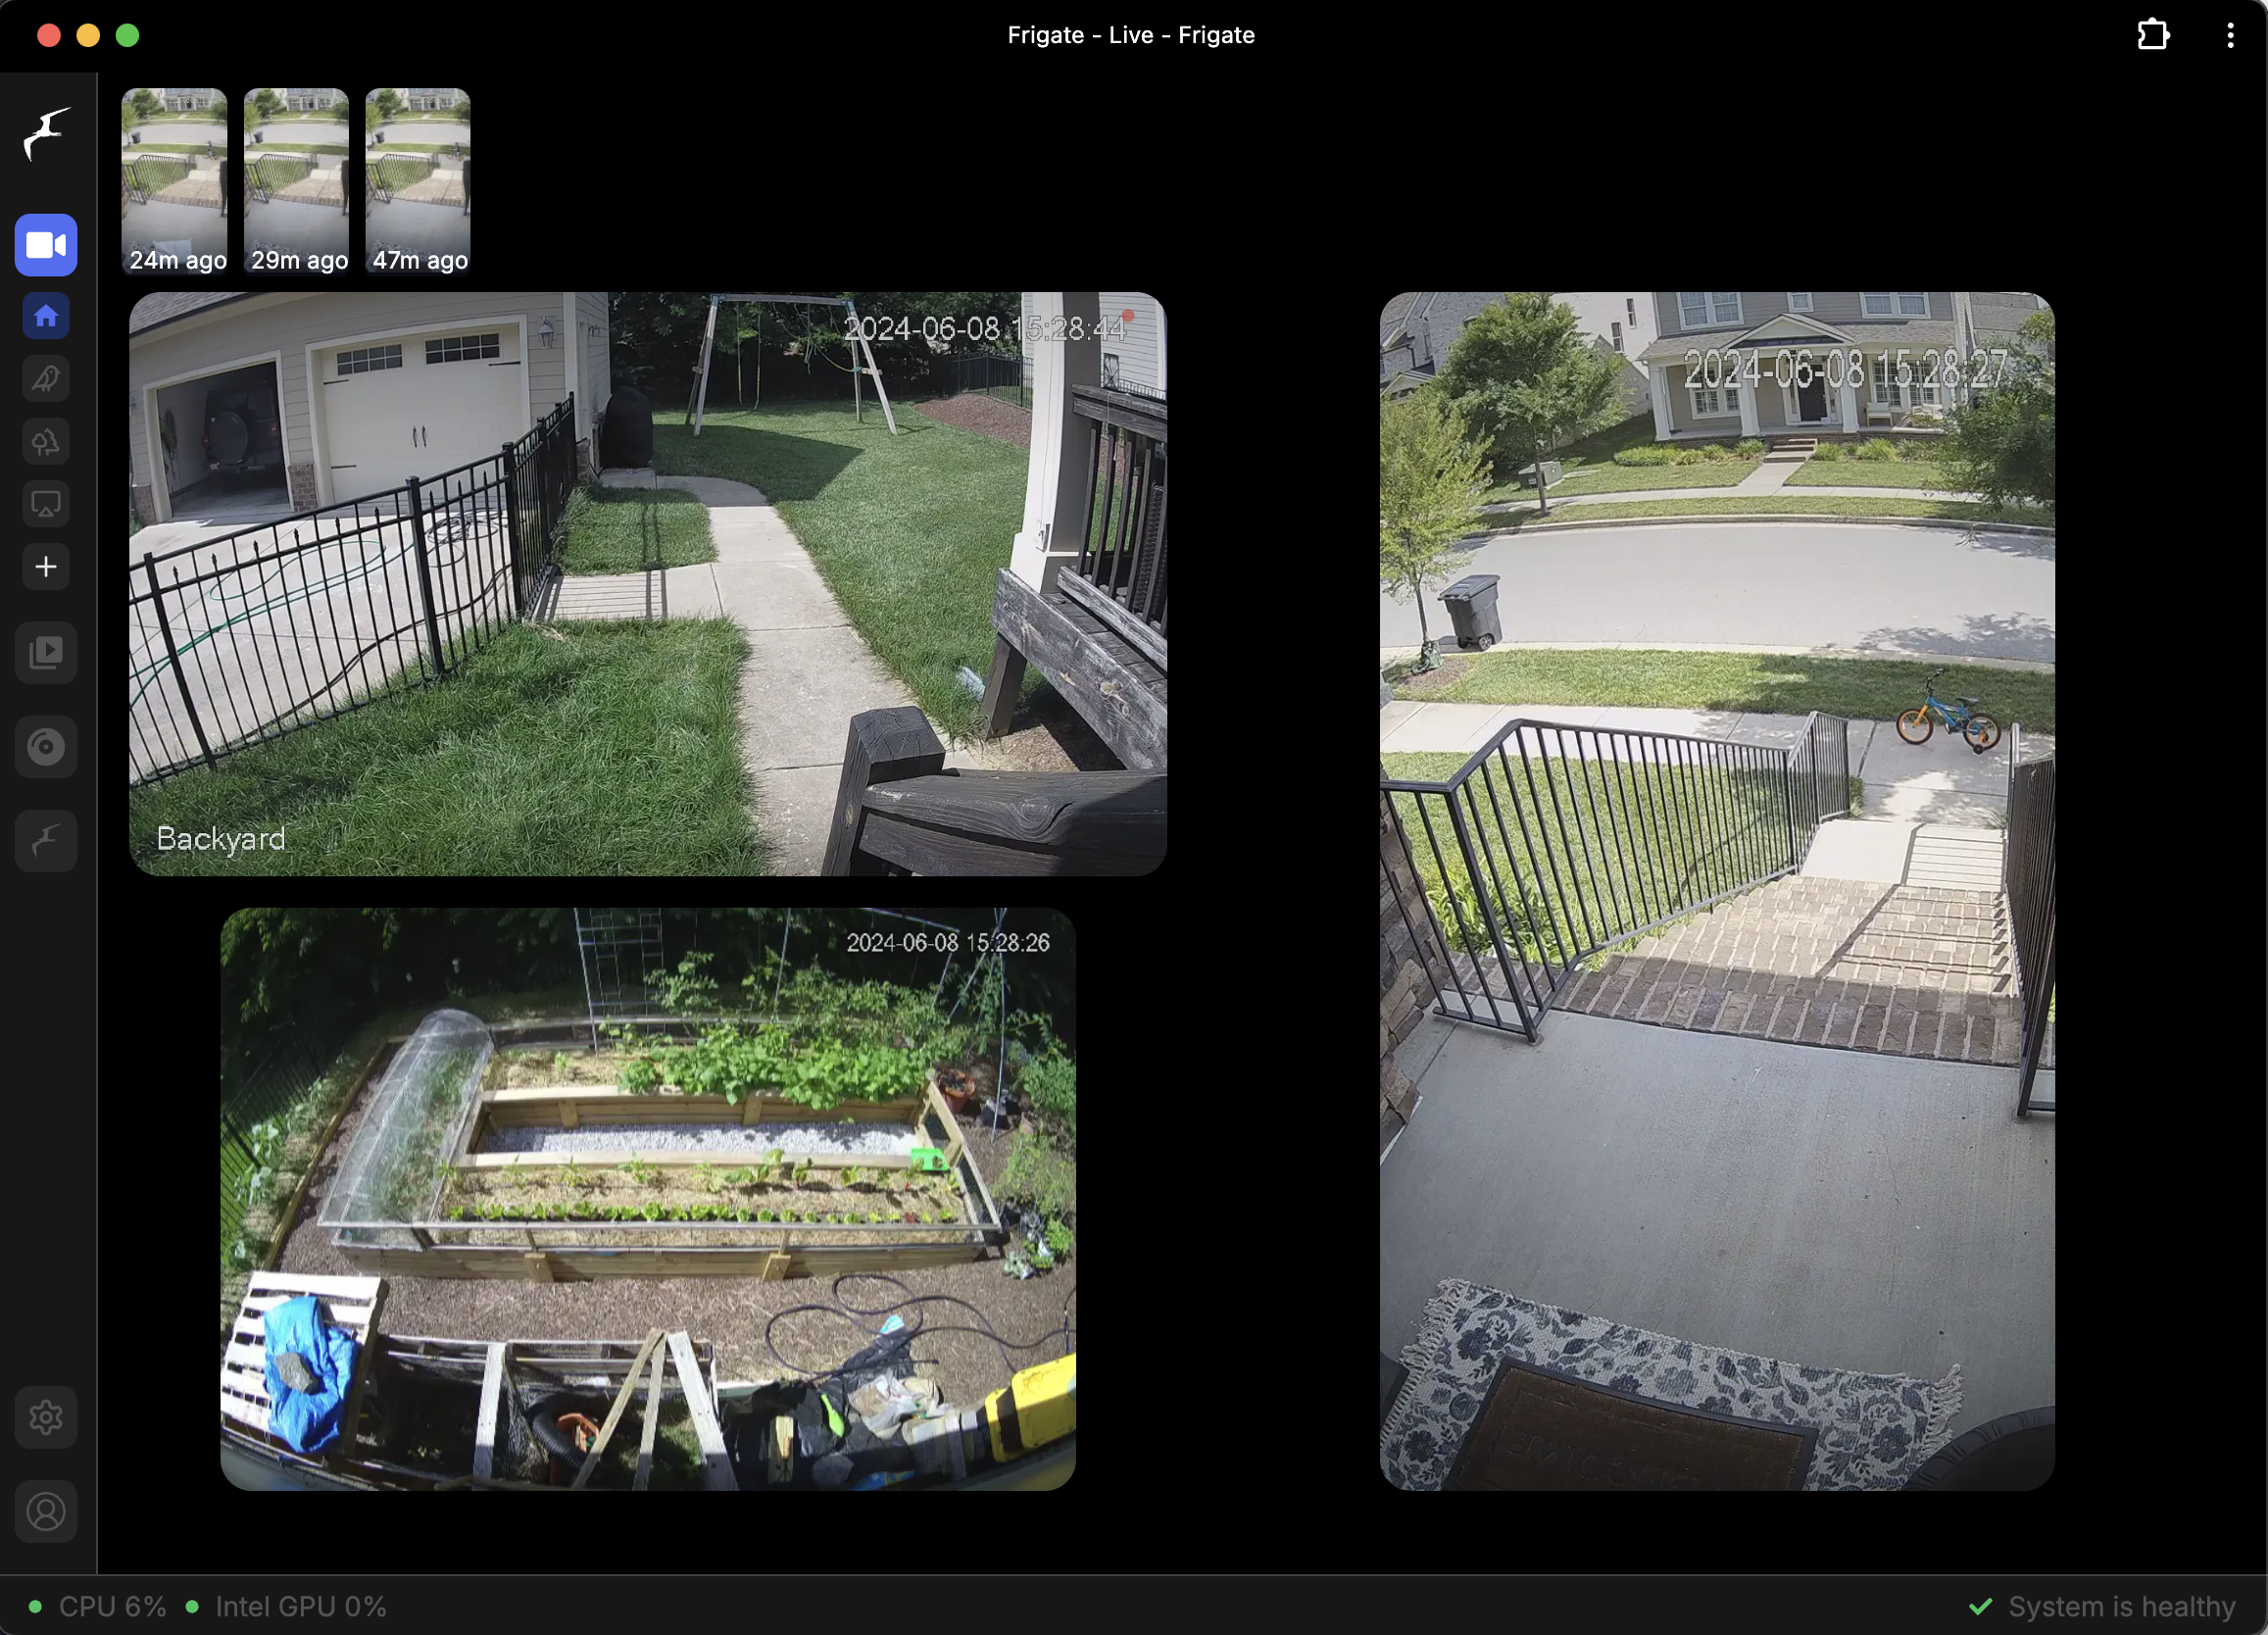 blakeblackshear/frigate
NVR with realtime local object detection for IP cameras
 wso2/carbon-identity-framework
Core framework for identity and access management, providing authentication, authorization, and identity governance capabilities for enterprise…