

ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
478
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 jackdpeterson/imagick_secure_puppet
Puppet module to harden ImageMagick policy.xml against CVE-2016-3714 by restricting dangerous image processing directives.
 istenrot/centos-dirty-cow-ansible
Ansible playbook automating CVE-2016-5195 (Dirty COW) mitigation on CentOS/Scientific Linux using SystemTap kernel module generation.
 alexzorin/cve-2017-2636-el
Ansible role for workaround for CVE-2017-2636 (Red Hat) - https://access.redhat.com/security/cve/CVE-2017-2636
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 yakovyakov/cve-2026-31431-mitigation
Detection and mitigation tooling for CVE-2026-31431 (Copy Fail) on Linux kernels. Includes Phalanx-CCS and Silent4Labs scripts plus an Ansible…
 foxboron/ssh-tpm-agent
SSH agent that creates and manages TPM-sealed keys for hardware-bound authentication, supporting key generation, import, wrapping, PIN protection,…
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 nozaq/terraform-aws-secure-baseline
Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
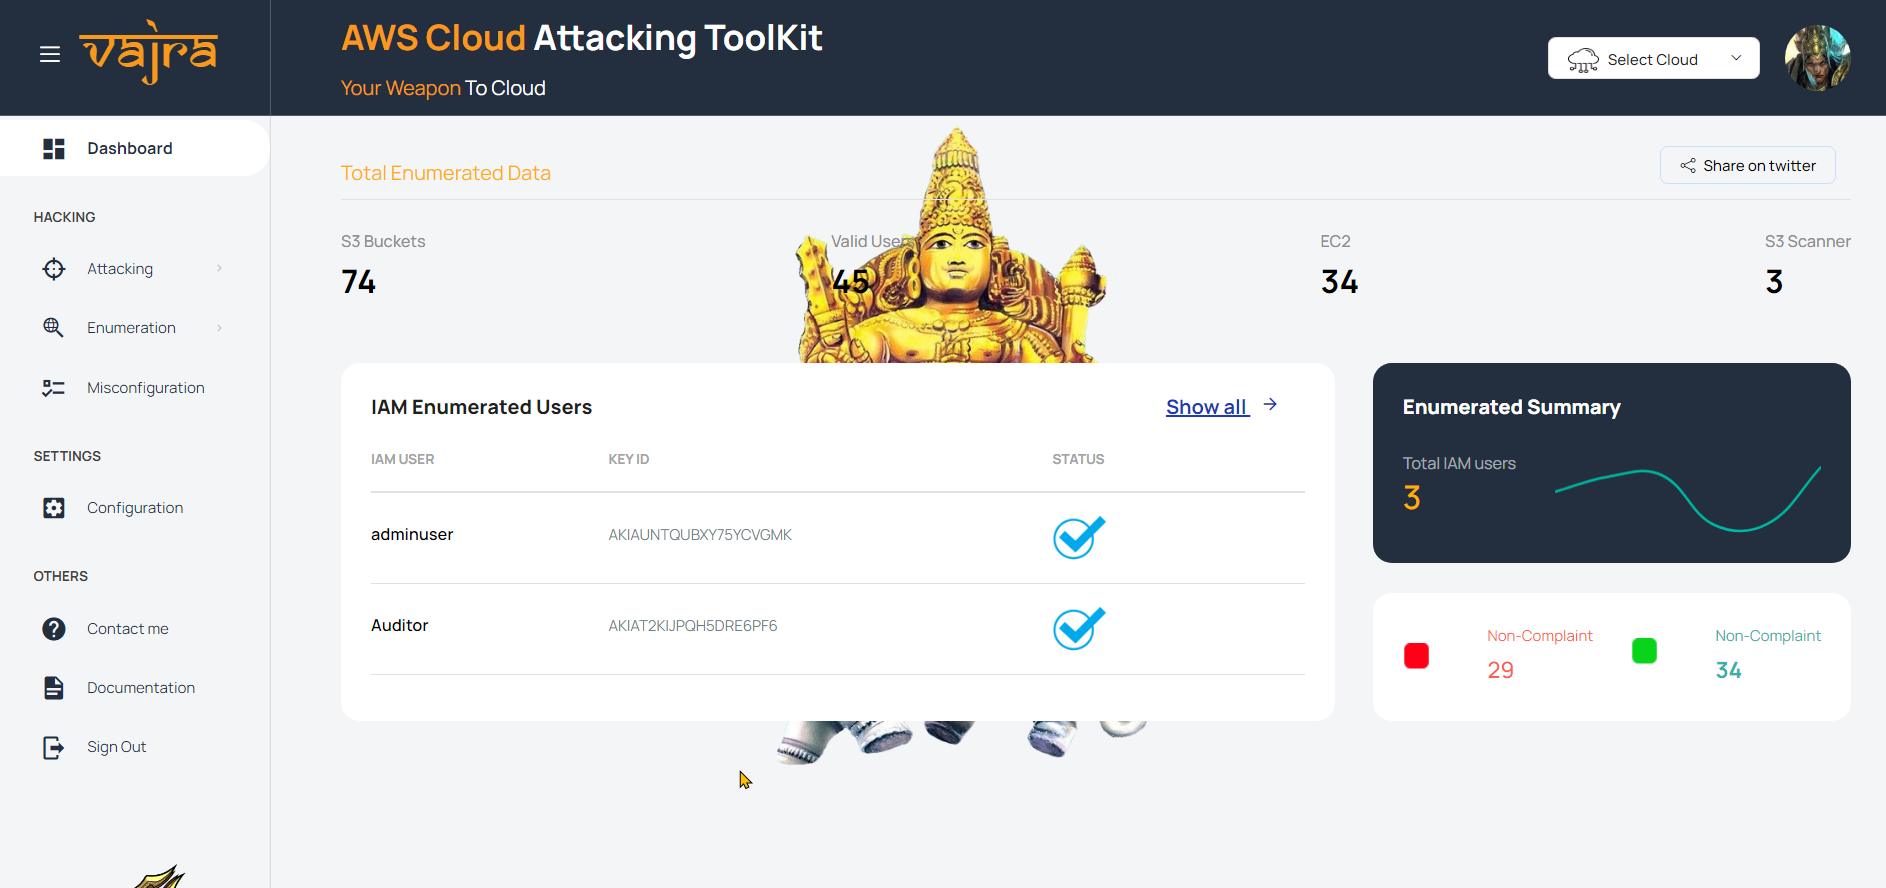 trouble-1/vajra
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…