Awesome-Asset-Discovery

Curated list of asset discovery and attack surface reconnaissance resources covering subdomain enumeration, IP discovery, port scanning, email…

Curated list of asset discovery and attack surface reconnaissance resources covering subdomain enumeration, IP discovery, port scanning, email…

C implementation of a cache-based jamming agreement that establishes a cross-VM cache covert channel between co-located virtual machines for research…

Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.

Enumerate the permissions associated with AWS credential set

Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…

Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…

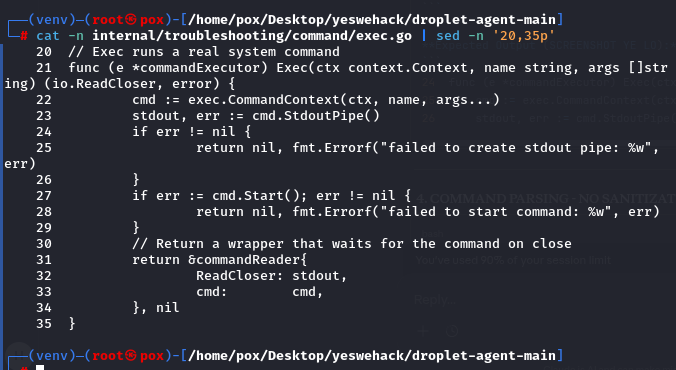
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).

Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…

Python3 rewrite of AsOutsider features of AADInternals

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Deep-dive analysis of CVE-2026-62201: OpenClaw sandbox exec-server network policy bypass (SSRF). Root cause, vulnerable vs patched code,…

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

Detection signatures for CVE-2026-41940 and shemas for cPanel logs

BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide

Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…

Docker-based proof-of-concept demonstrating CVE-2025-23320 in NVIDIA Triton inference server, exploiting shared memory key leakage to trigger an…

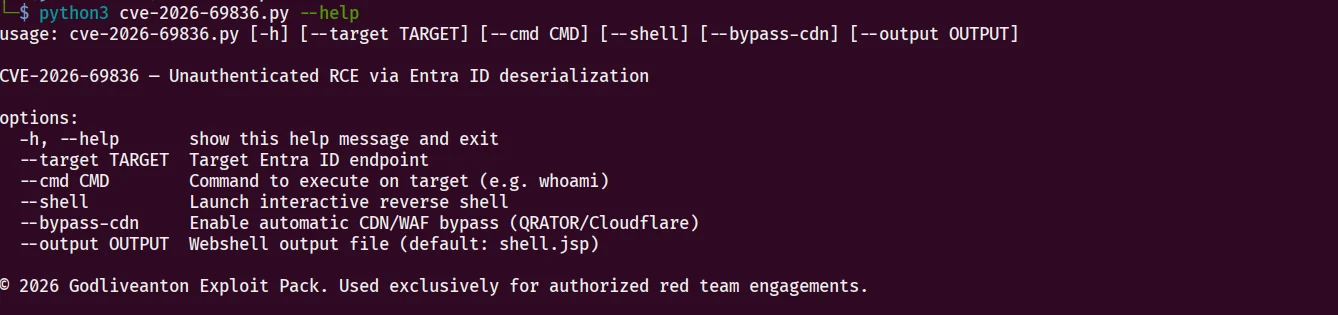
CVE-2026-69836 — Unauthenticated RCE via Entra ID deserialization

AI-powered bug bounty hunting toolkit that works with or without subscription.