
cve-2026-103956-loom-unauth
 abraxas/cve-2026-103956-loom-unauth
CVE-2026-103956 - Loom for AWS - Critical - Auth bypass - unauthenticated super-admin when no IdP is configured
authenticationcloud-securityexploitation+5
8
abraxas/cve-2026-103956-loom-unauthCVE-2026-103956 - Loom for AWS - Critical - Auth bypass - unauthenticated super-admin when no IdP is configured
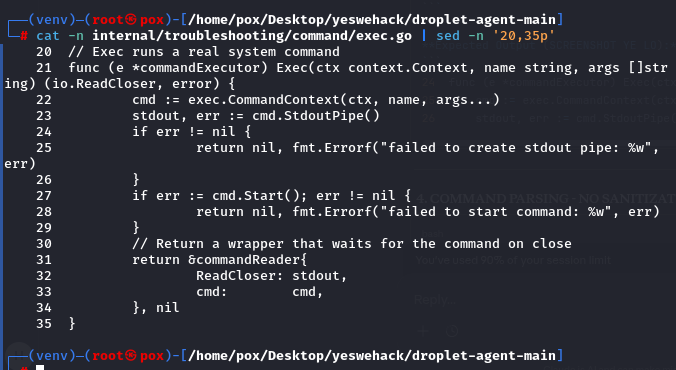 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).
 diedromeo/cve-2026-62201-openclaw-ssrf
Deep-dive analysis of CVE-2026-62201: OpenClaw sandbox exec-server network policy bypass (SSRF). Root cause, vulnerable vs patched code,…
 isaca0315/cve-2026-44578-next-js-ssrf
este laboratorio puede estar bien o mal esta el pruebas pero debe funcionar preguntale a la IA hahah
 gagaltotal/cve-2026-82329-poc
PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and…
 dinosn/cve-2026-82329-jfrog-artifactory
Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 grabesec/xcp_ng_cve-2026-31431_tester
Non-destructive detector for CVE-2026-31431 (Copy Fail) local privilege escalation in XCP-ng 8.3 Dom0, validating kernel vulnerability via page-cache…
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 b0b0haha/cve-2026-29954
Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…
 zeropathai/spinnaker-poc
POCs for CVE-2026-32604 and CVE-2026-32613 which allow post-auth RCE and credential theft in Spinnaker
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
 exploreunknowed/cve-2026-24306
Proof-of-concept exploit for Azure Front Door privilege escalation (CVE-2026-24306) enabling routing rule injection, backend pool modification, and…