enterprise-abac-gateway

Zero-trust reverse proxy and ABAC authorization gateway in Go with embedded OPA policy evaluation and distributed token revocation.

Zero-trust reverse proxy and ABAC authorization gateway in Go with embedded OPA policy evaluation and distributed token revocation.

Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…

Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.

Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…

AI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…

Apache Spark 4.2.0 - High - Remote - File write - Connect session SET copyFromLocalToFs.allowDestLocal

Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.

Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…

Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…

Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…

Enumerate the permissions associated with AWS credential set

Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…

Disabled TLS Certificate Verification for HashiCorp Vault KMS in confluent-kafka

Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…

Python PoC for CVE-2026-100835: audits Contrast manifests for AllowedChipIDs/AllowedPIIDs, detects versions, and probes Coordinator endpoints to…

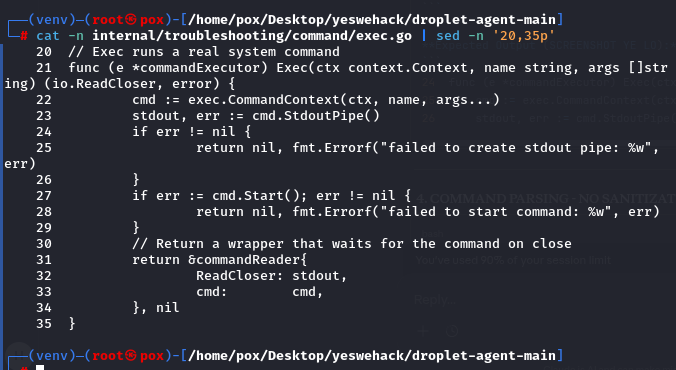
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).

OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…