EXPLOIT-CVE-2026-33634

Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…

Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…

PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter

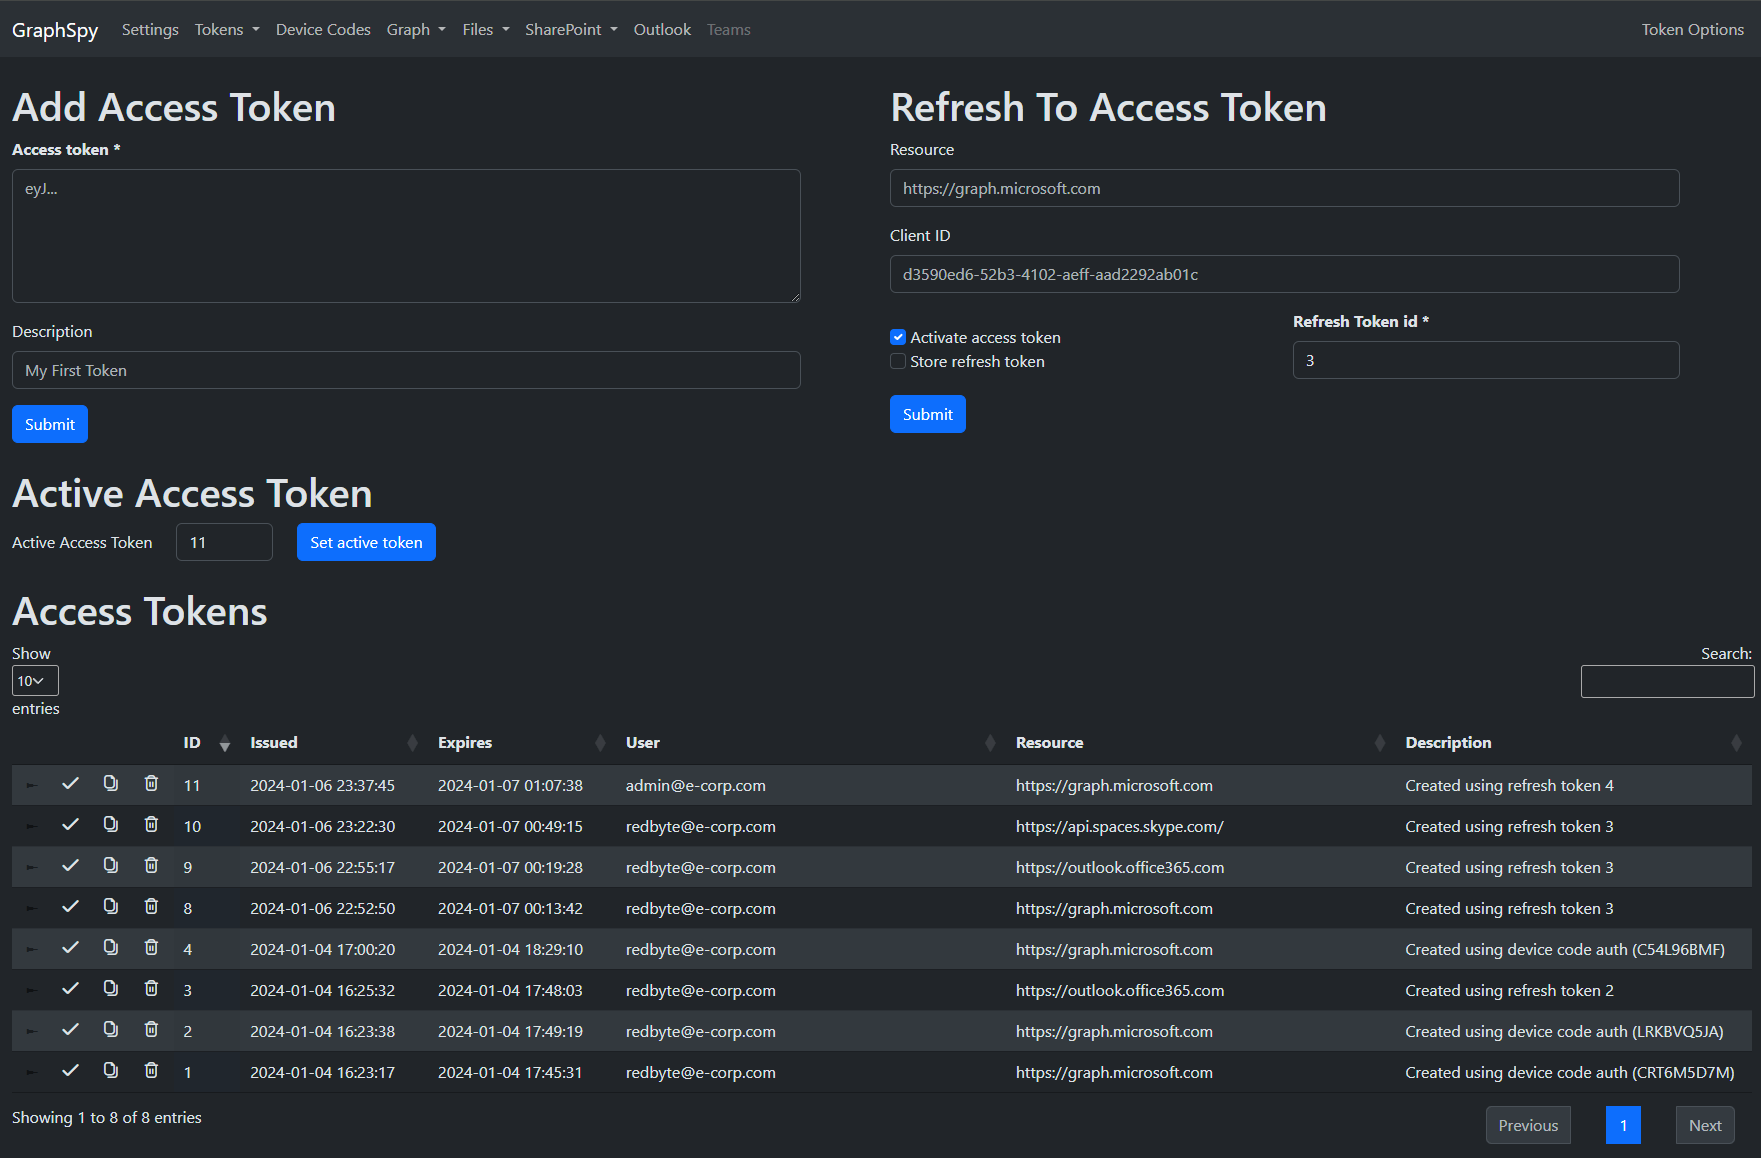
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI

Batch upgrade all your Next.js apps to patched versions - fight back against CVE-2025-55183/55184/67779

Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…

A lightweight caching proxy for package registries.

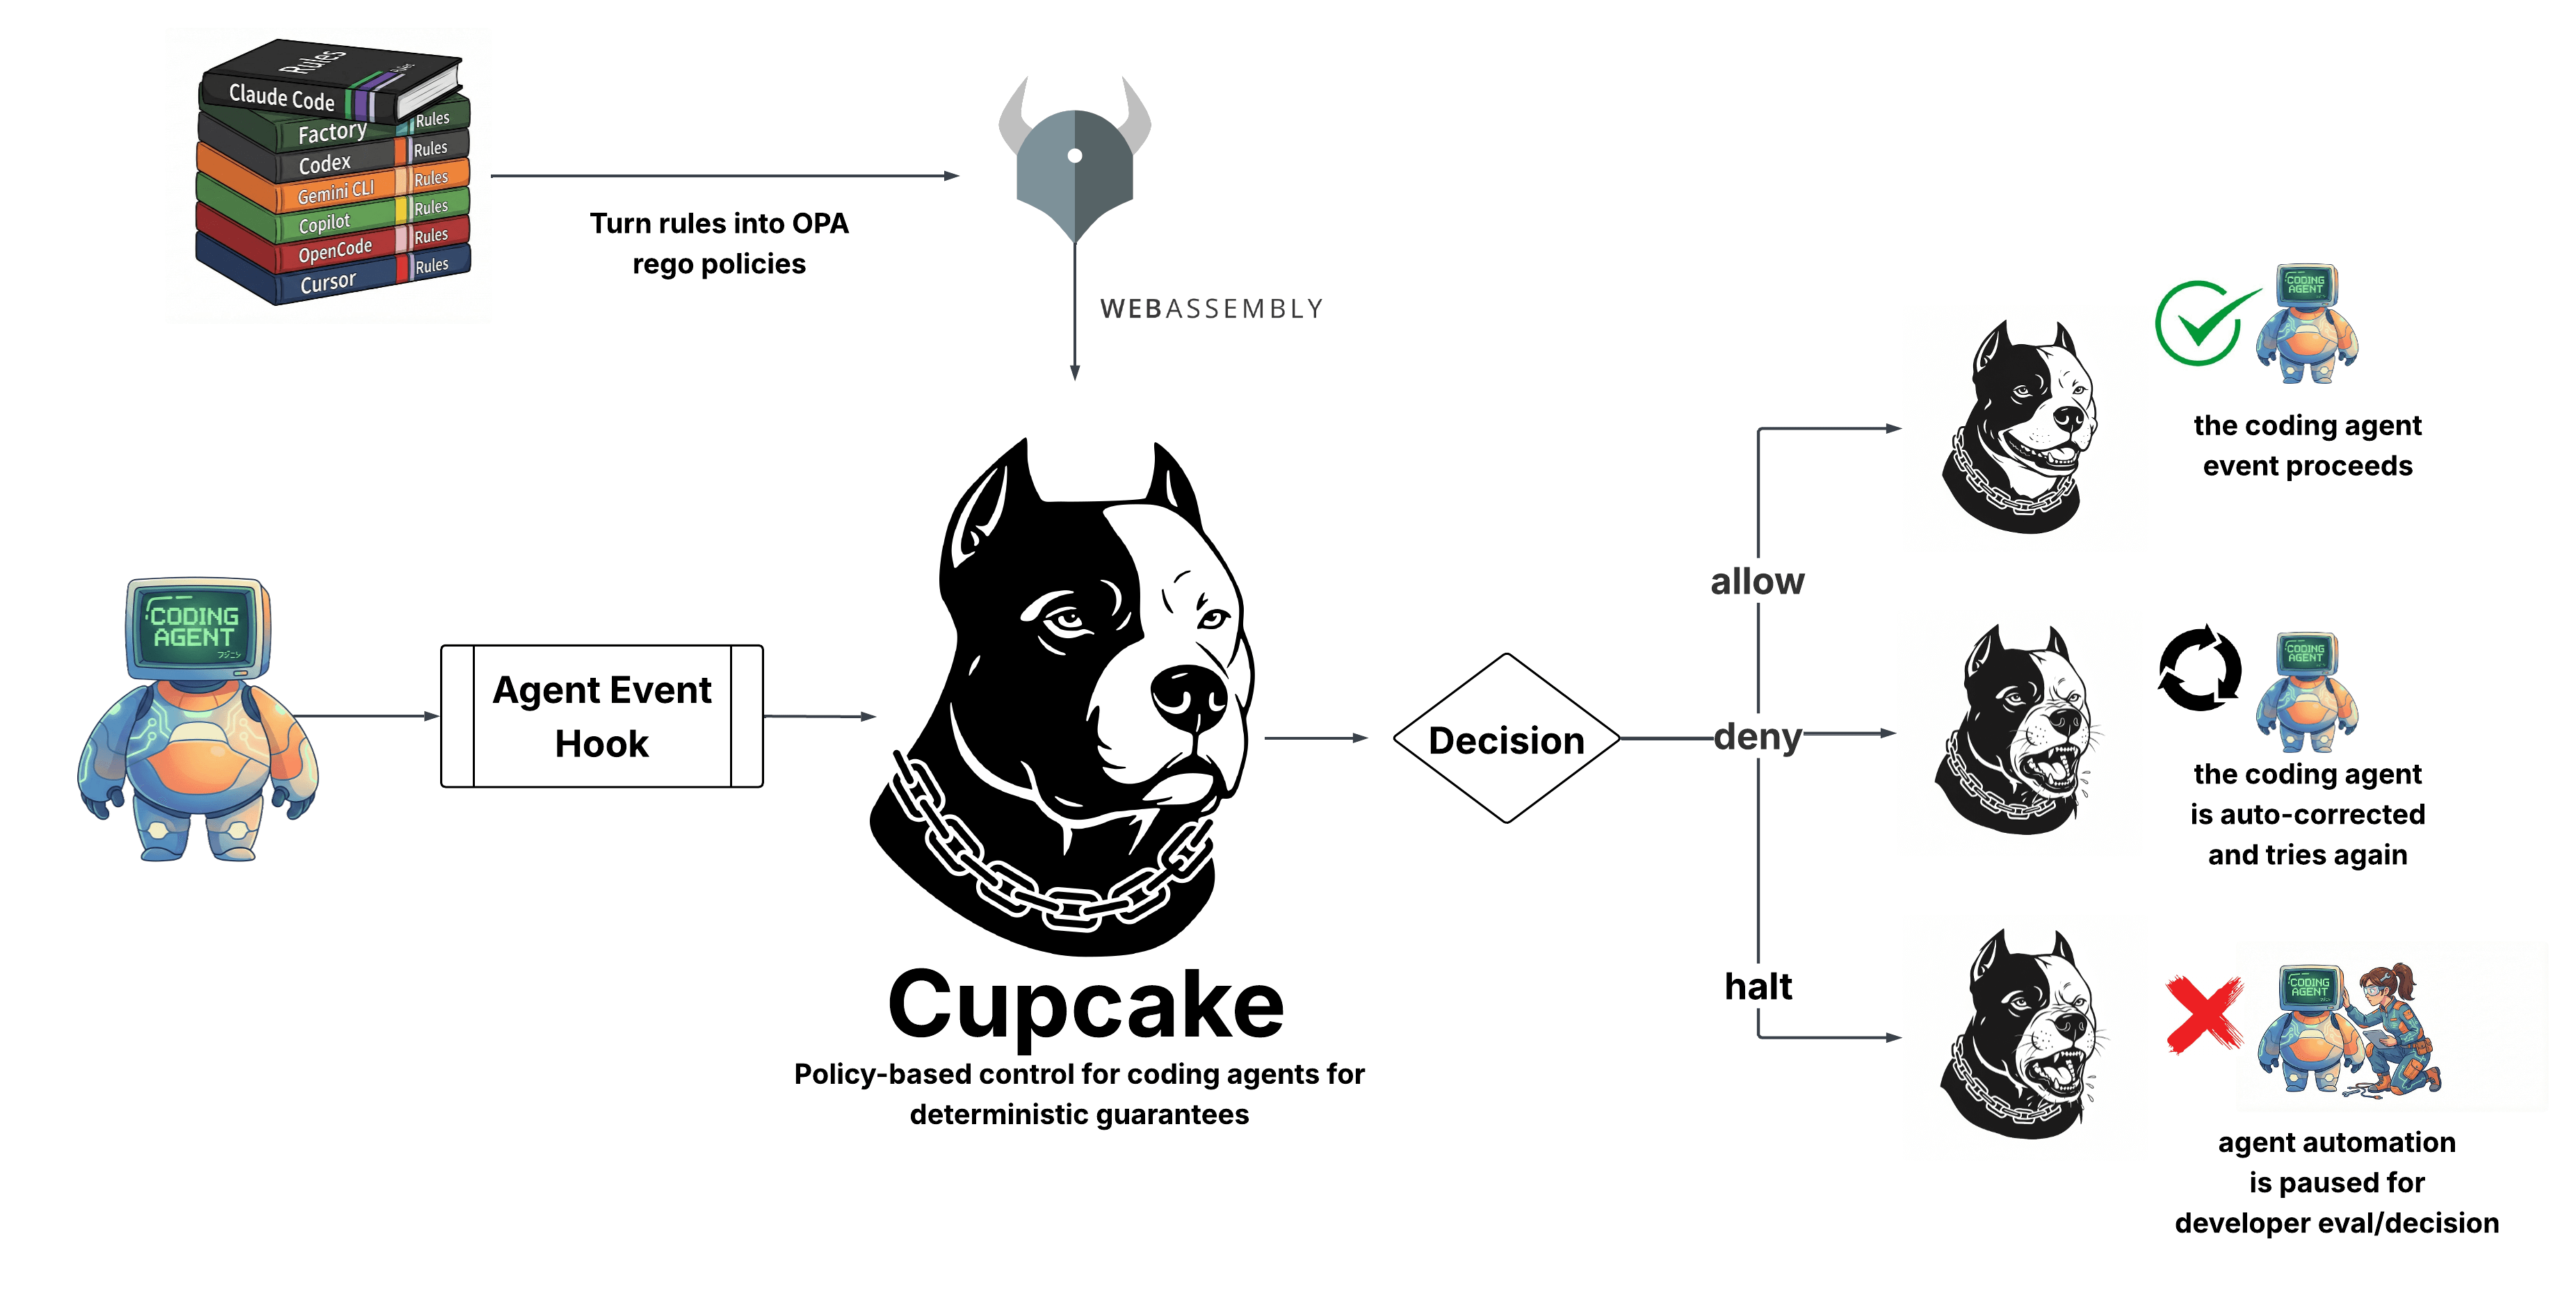
A native policy enforcement layer for AI coding agents. Built on OPA/Rego.

Inspect all of your Heroku apps for vulnerable versions of the JSON gem

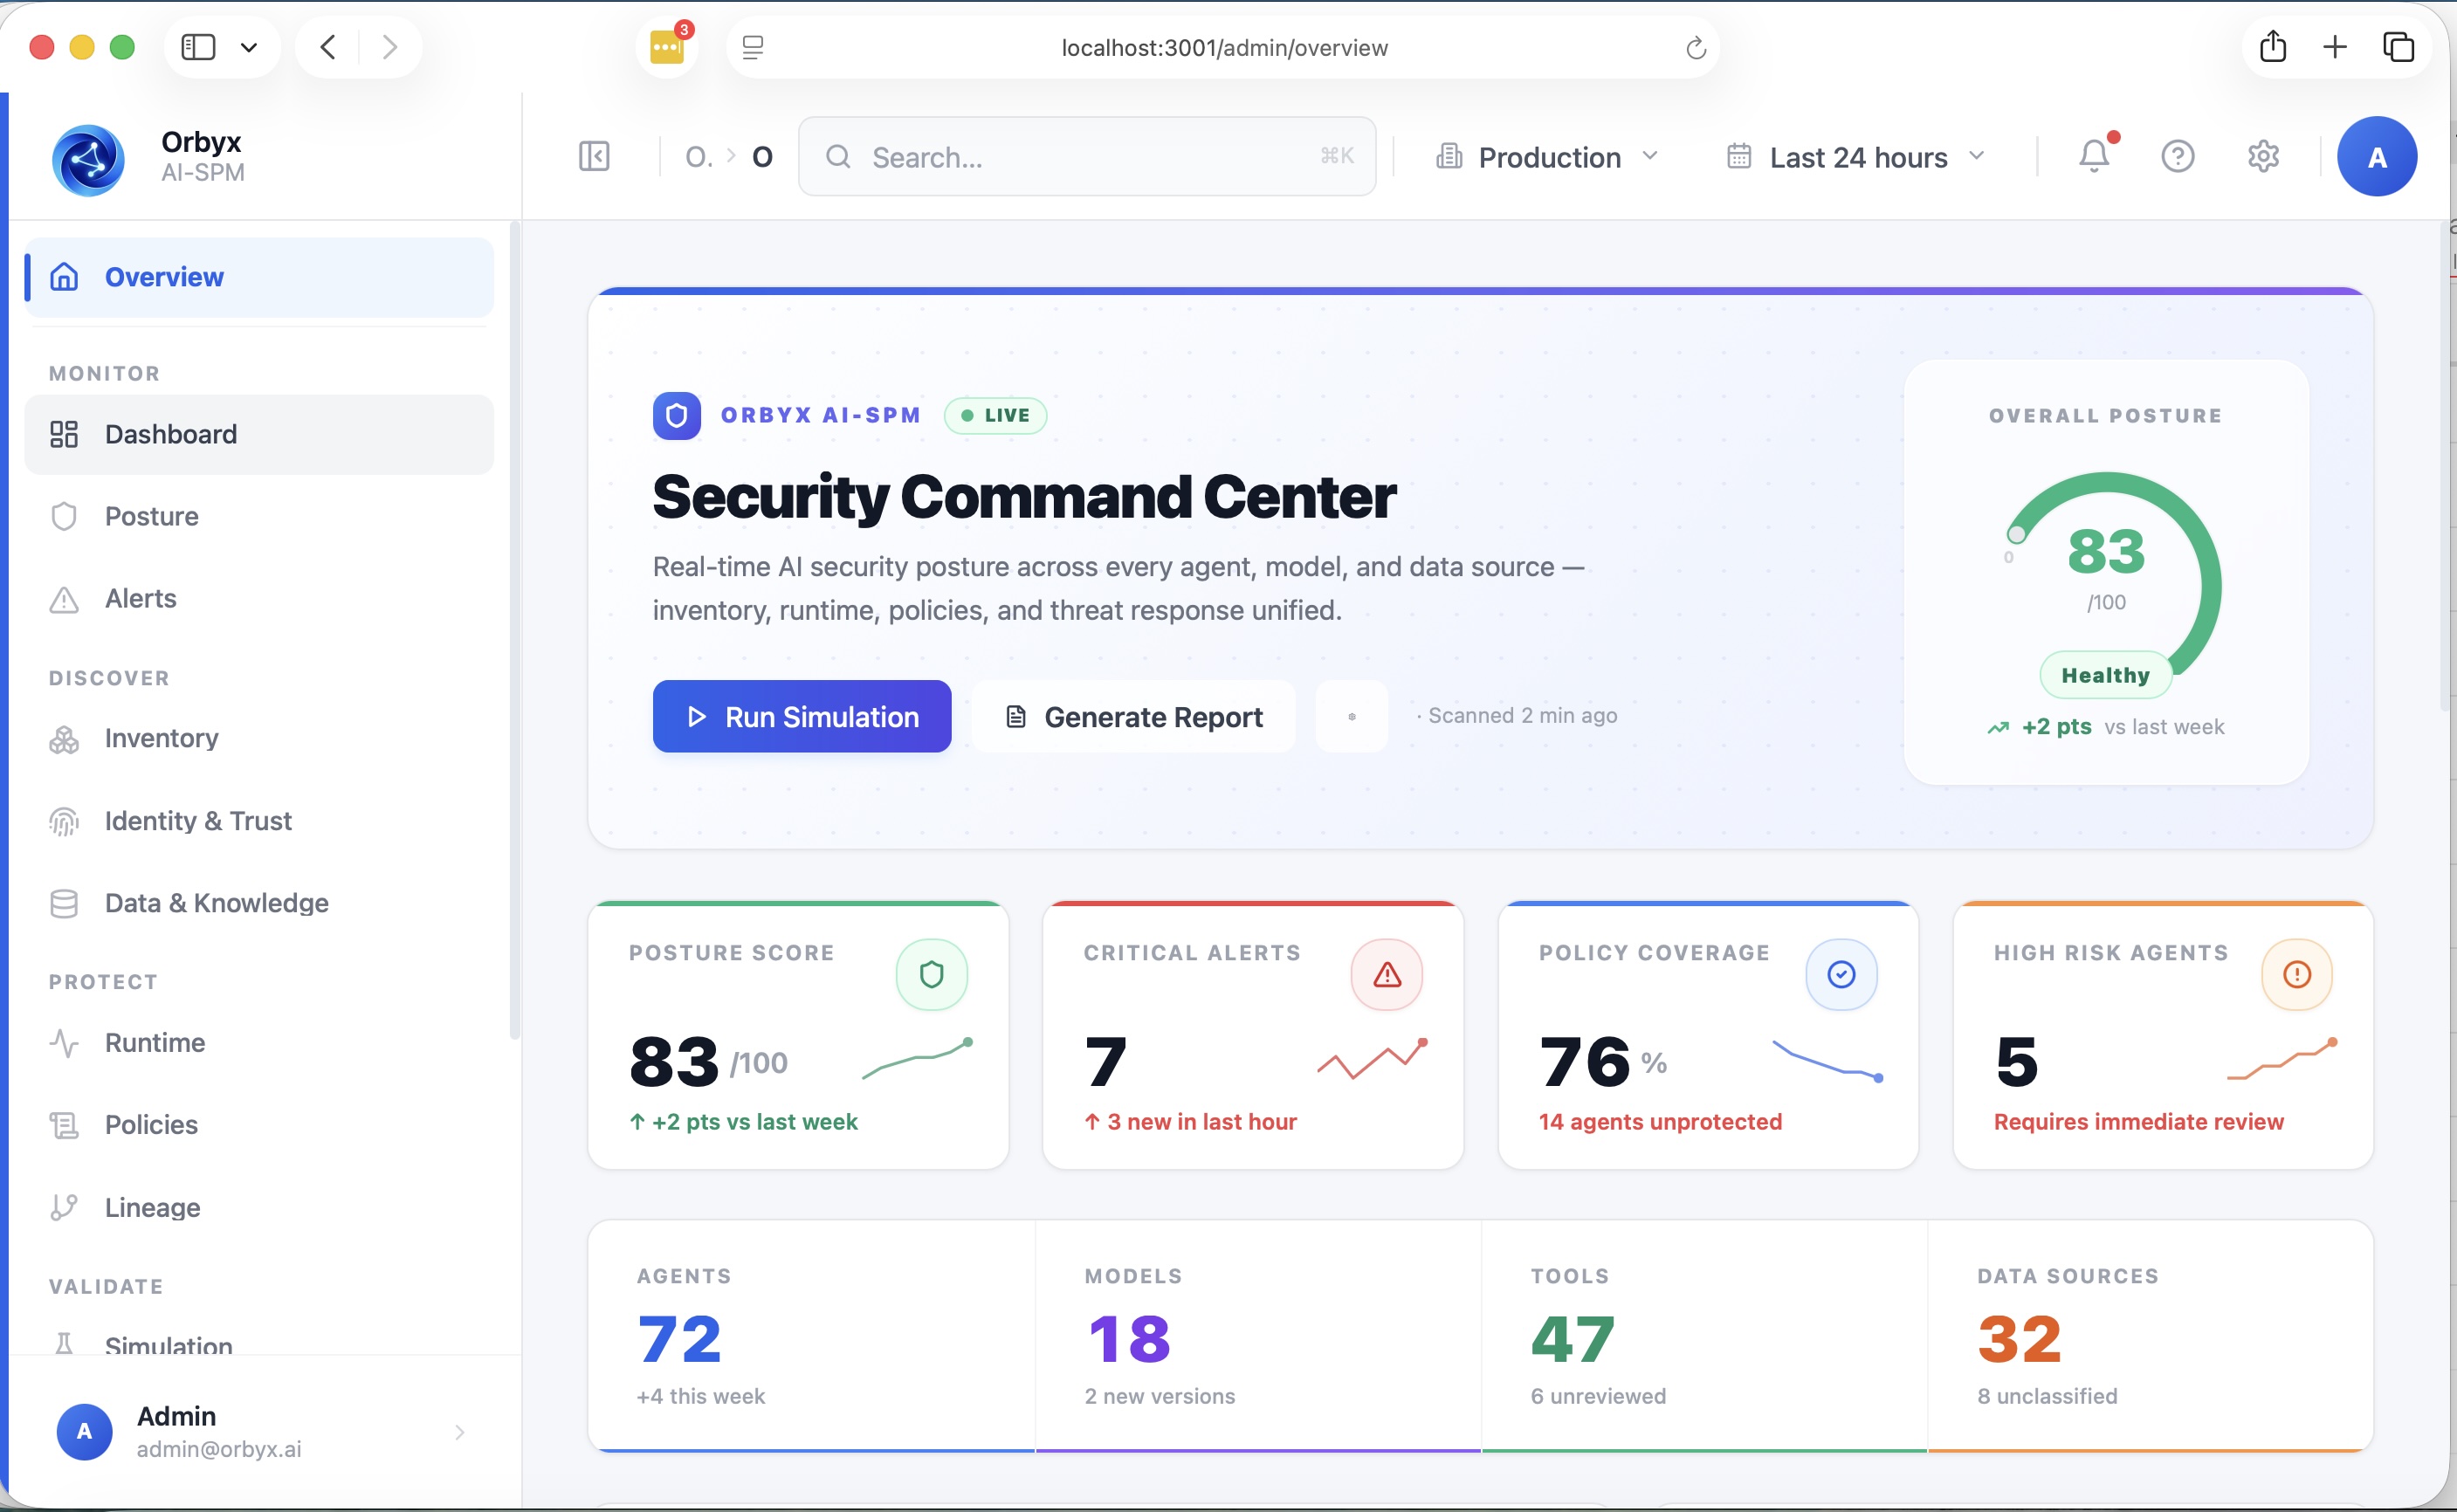
This opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…

📦 Make security testing of K8s, Docker, and Containerd easier.