
claude-bug-bounty
 shuvonsec/claude-bug-bounty
AI-powered bug bounty hunting toolkit that works with or without subscription.
ai-securitycloud-securityexploitation+8
5.4k
shuvonsec/claude-bug-bountyAI-powered bug bounty hunting toolkit that works with or without subscription.
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
 rolix44/kubestroyer
Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…
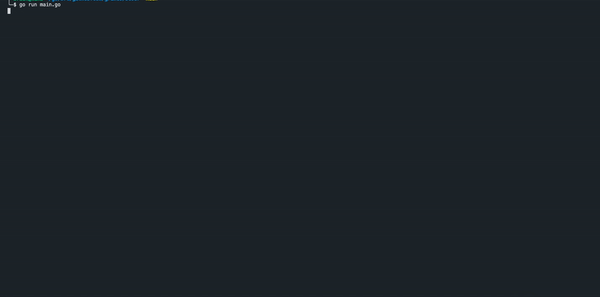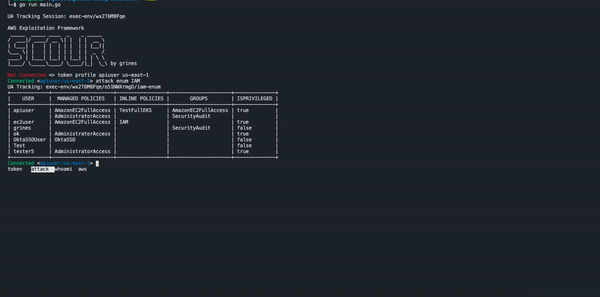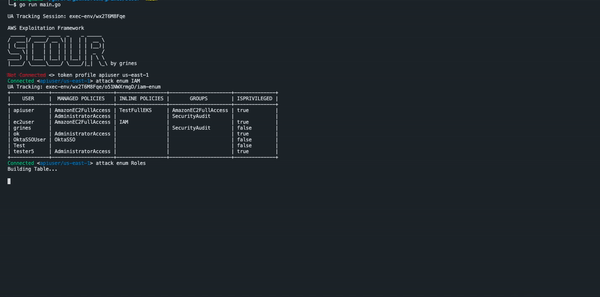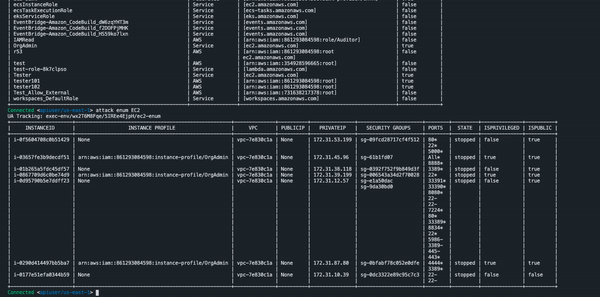 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
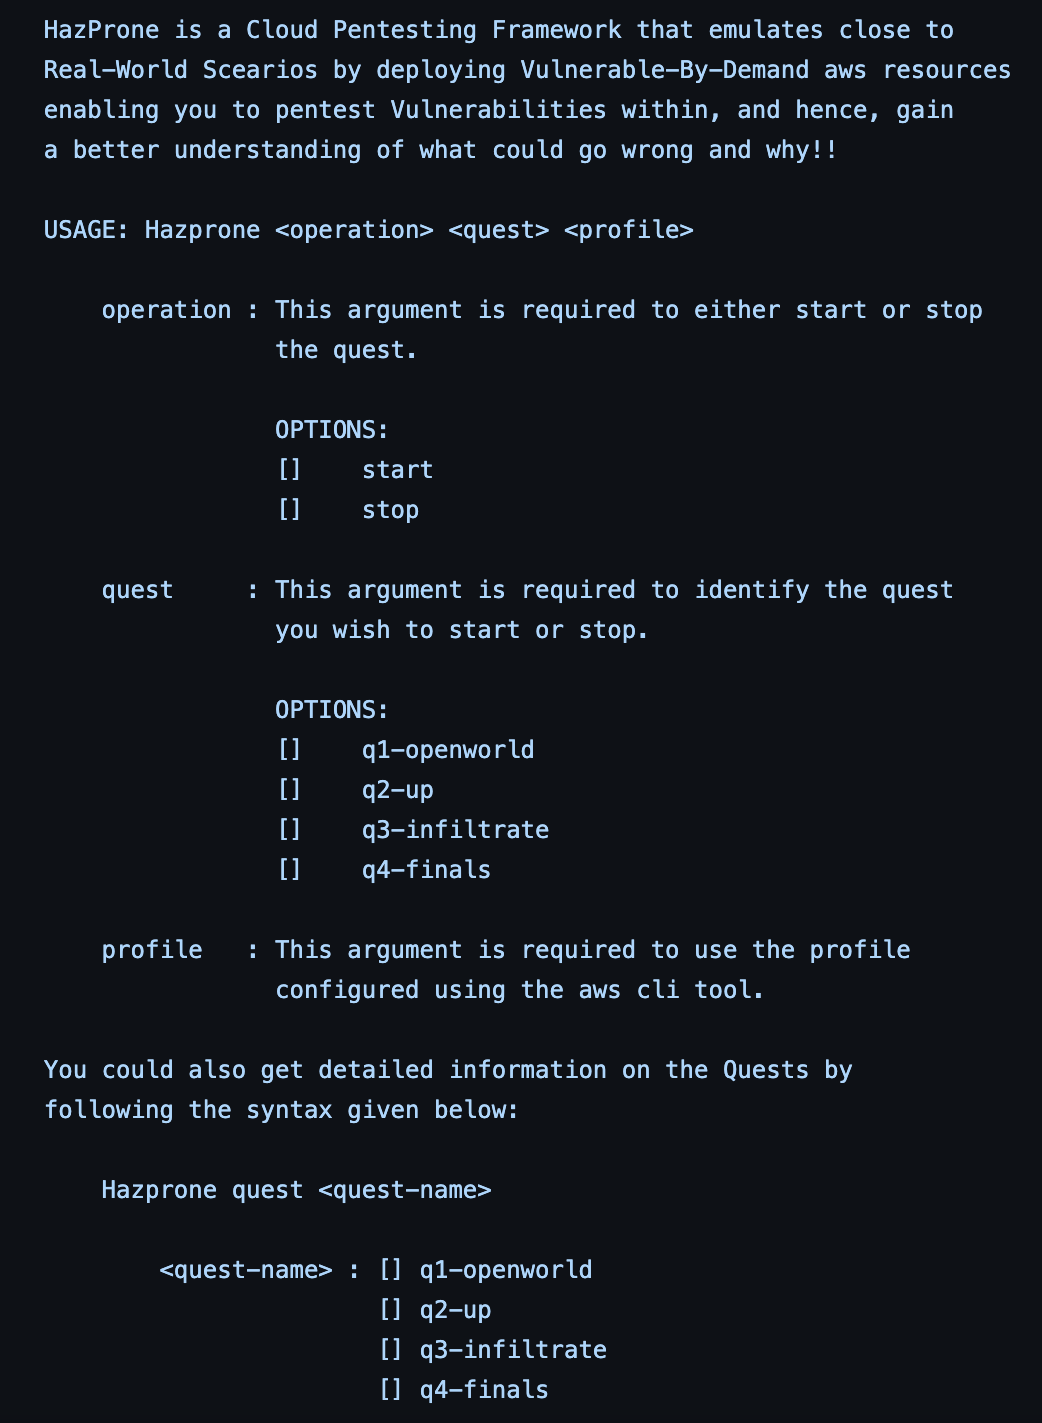 stafordtituss/hazprone
Cloud pentesting framework deploying vulnerable-by-demand AWS resources with quest-based scenarios to teach practical penetration testing and…
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
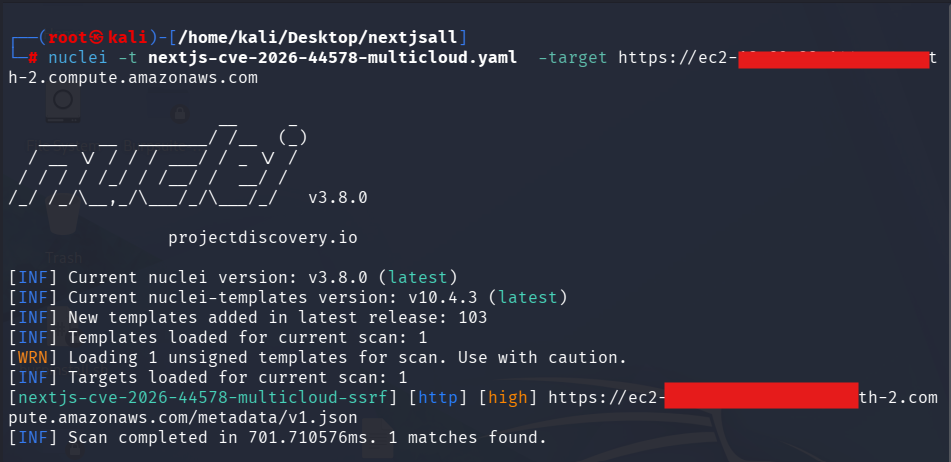 love07oj/nextjs-cve-2026-44578
Nuclei templates for detecting CVE-2026-44578 (Next.js WebSocket Upgrade SSRF) with multi-cloud metadata validation, Next.js fingerprinting, and…
 corelight/cve-2021-38647-noimages
Zeek package detecting CVE-2021-38647 (OMIGOD) exploit attempts by monitoring OMI/WMI traffic for missing Authorization headers and malicious SOAP…
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
 tocong282/cve-2026-44578-poc
Proof-of-concept exploit for CVE-2026-44578, a Server-Side Request Forgery in Next.js WebSocket upgrade handler. Includes detection mode and…
 oscerd/cve-2026-43867
Reproducer for CVE-2026-43867 — Apache Camel camel-pqc AwsSecretsManagerKeyLifecycleManager unsafe key-metadata deserialization (RCE)
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
 mgeeky/penetration-testing-tools
A collection of more than 170+ tools, scripts, cheatsheets and other loots that I've developed over years for Red Teaming/Pentesting/IT Security…
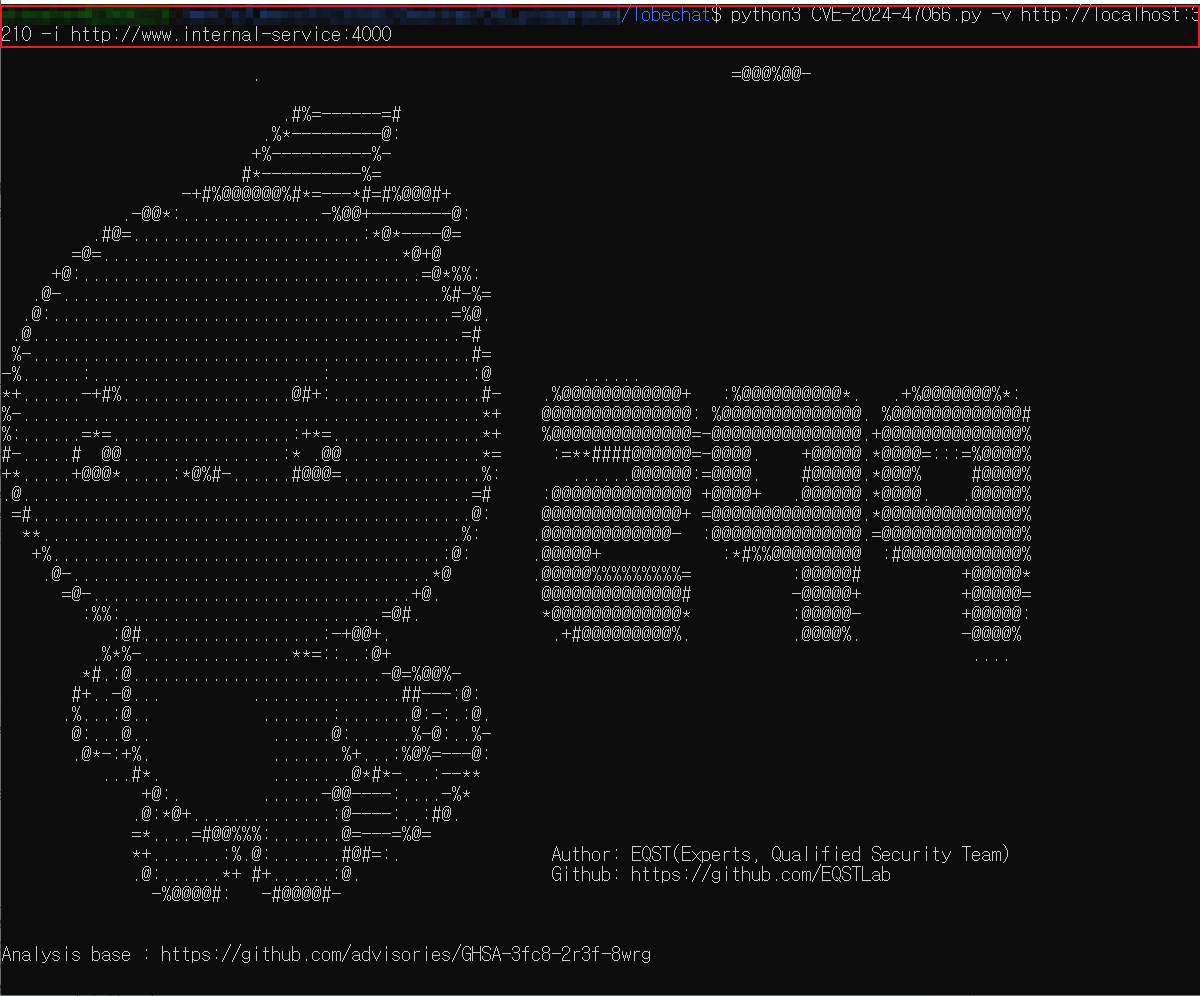 l8bl/cve-2024-47066
Proof-of-concept exploit for CVE-2024-47066, a server-side request forgery (SSRF) vulnerability in LobeChat that bypasses IP-based restrictions via…
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.