

kubernetes-goat
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
cloud-securitycontainer-escapecontainer-security+4
5.8k
madhuakula/kubernetes-goatIntentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 jacobideji/aiiroverlay
AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
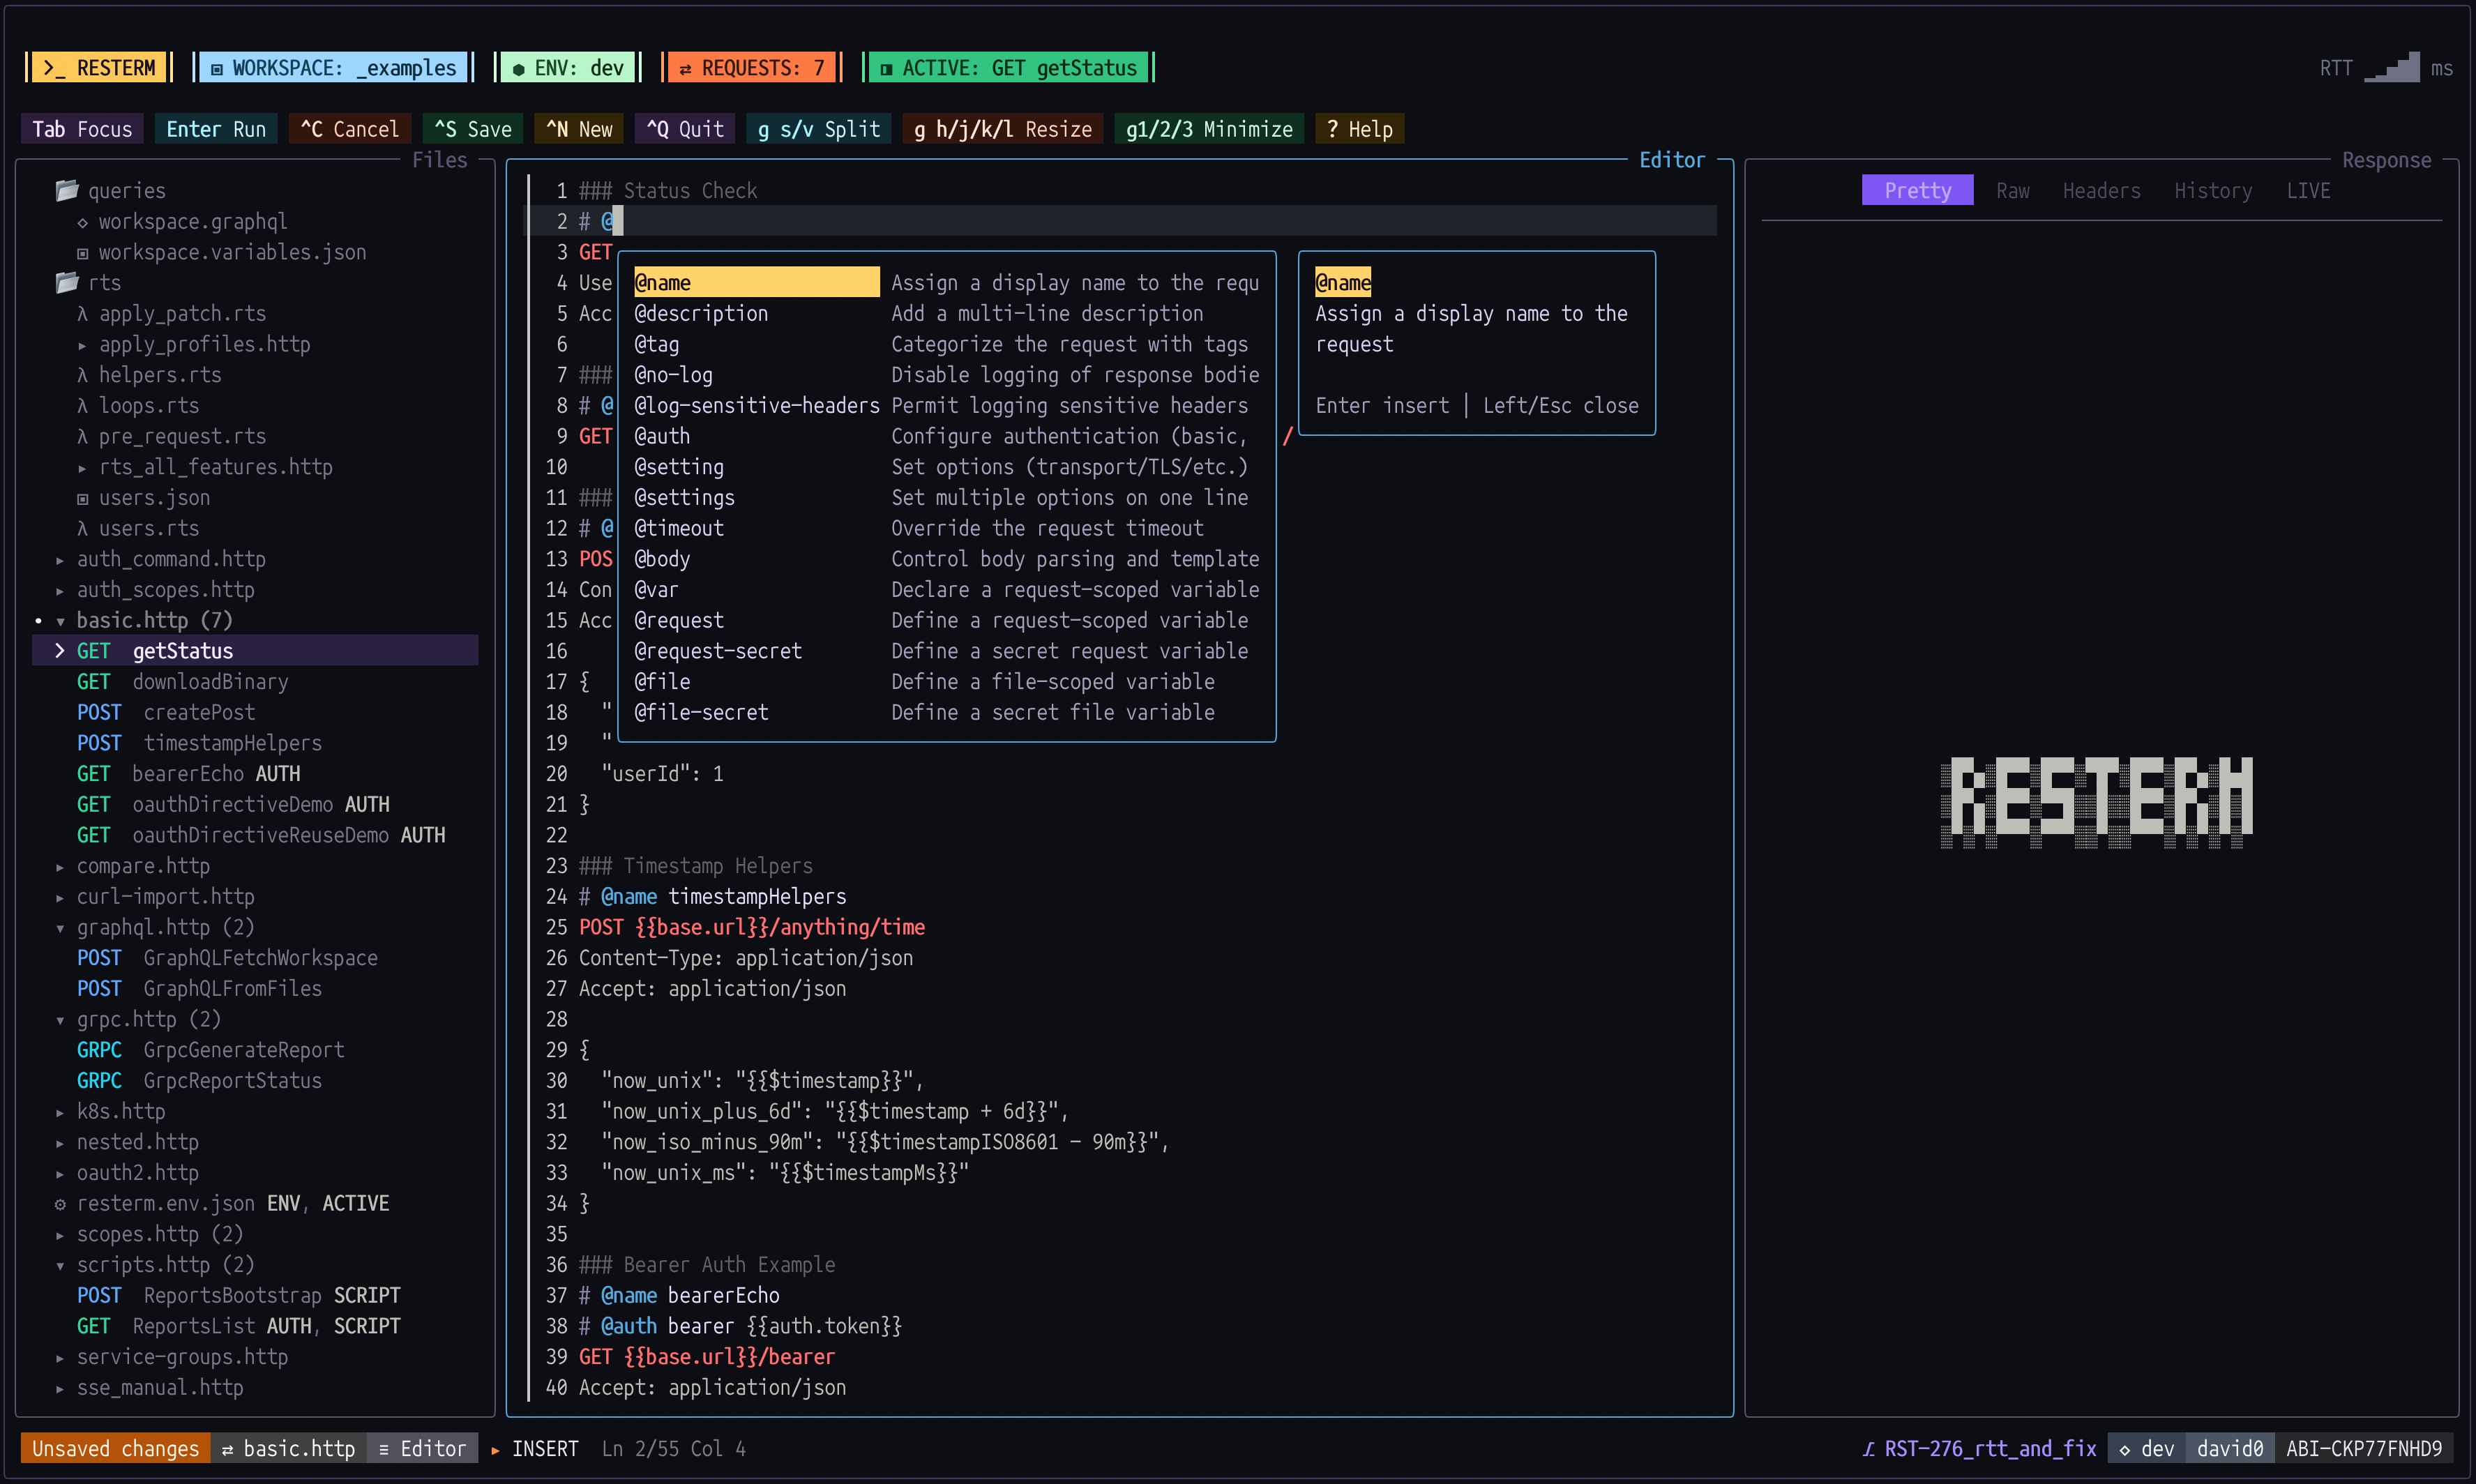 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 biitts/cve-2026-54917-seaweedfs-cross-bucket-traversal
PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…