

trufflehog
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
cloud-securitycode-analysisdevsecops+6
trufflesecurity/trufflehogFind, verify, and analyze leaked credentials
 d-xuan/cve-2024-52510
Proof-of-concept exploit for CVE-2024-52510 demonstrating signature bypass in Nextcloud's E2EEv2 protocol, enabling server-side decryption of…
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 jordanpotti/awsbucketdump
Security Tool to Look For Interesting Files in S3 Buckets
 nsonaniya2010/subdomainizer
A tool to find subdomains and interesting things hidden inside, external Javascript files of page, folder, and Github.
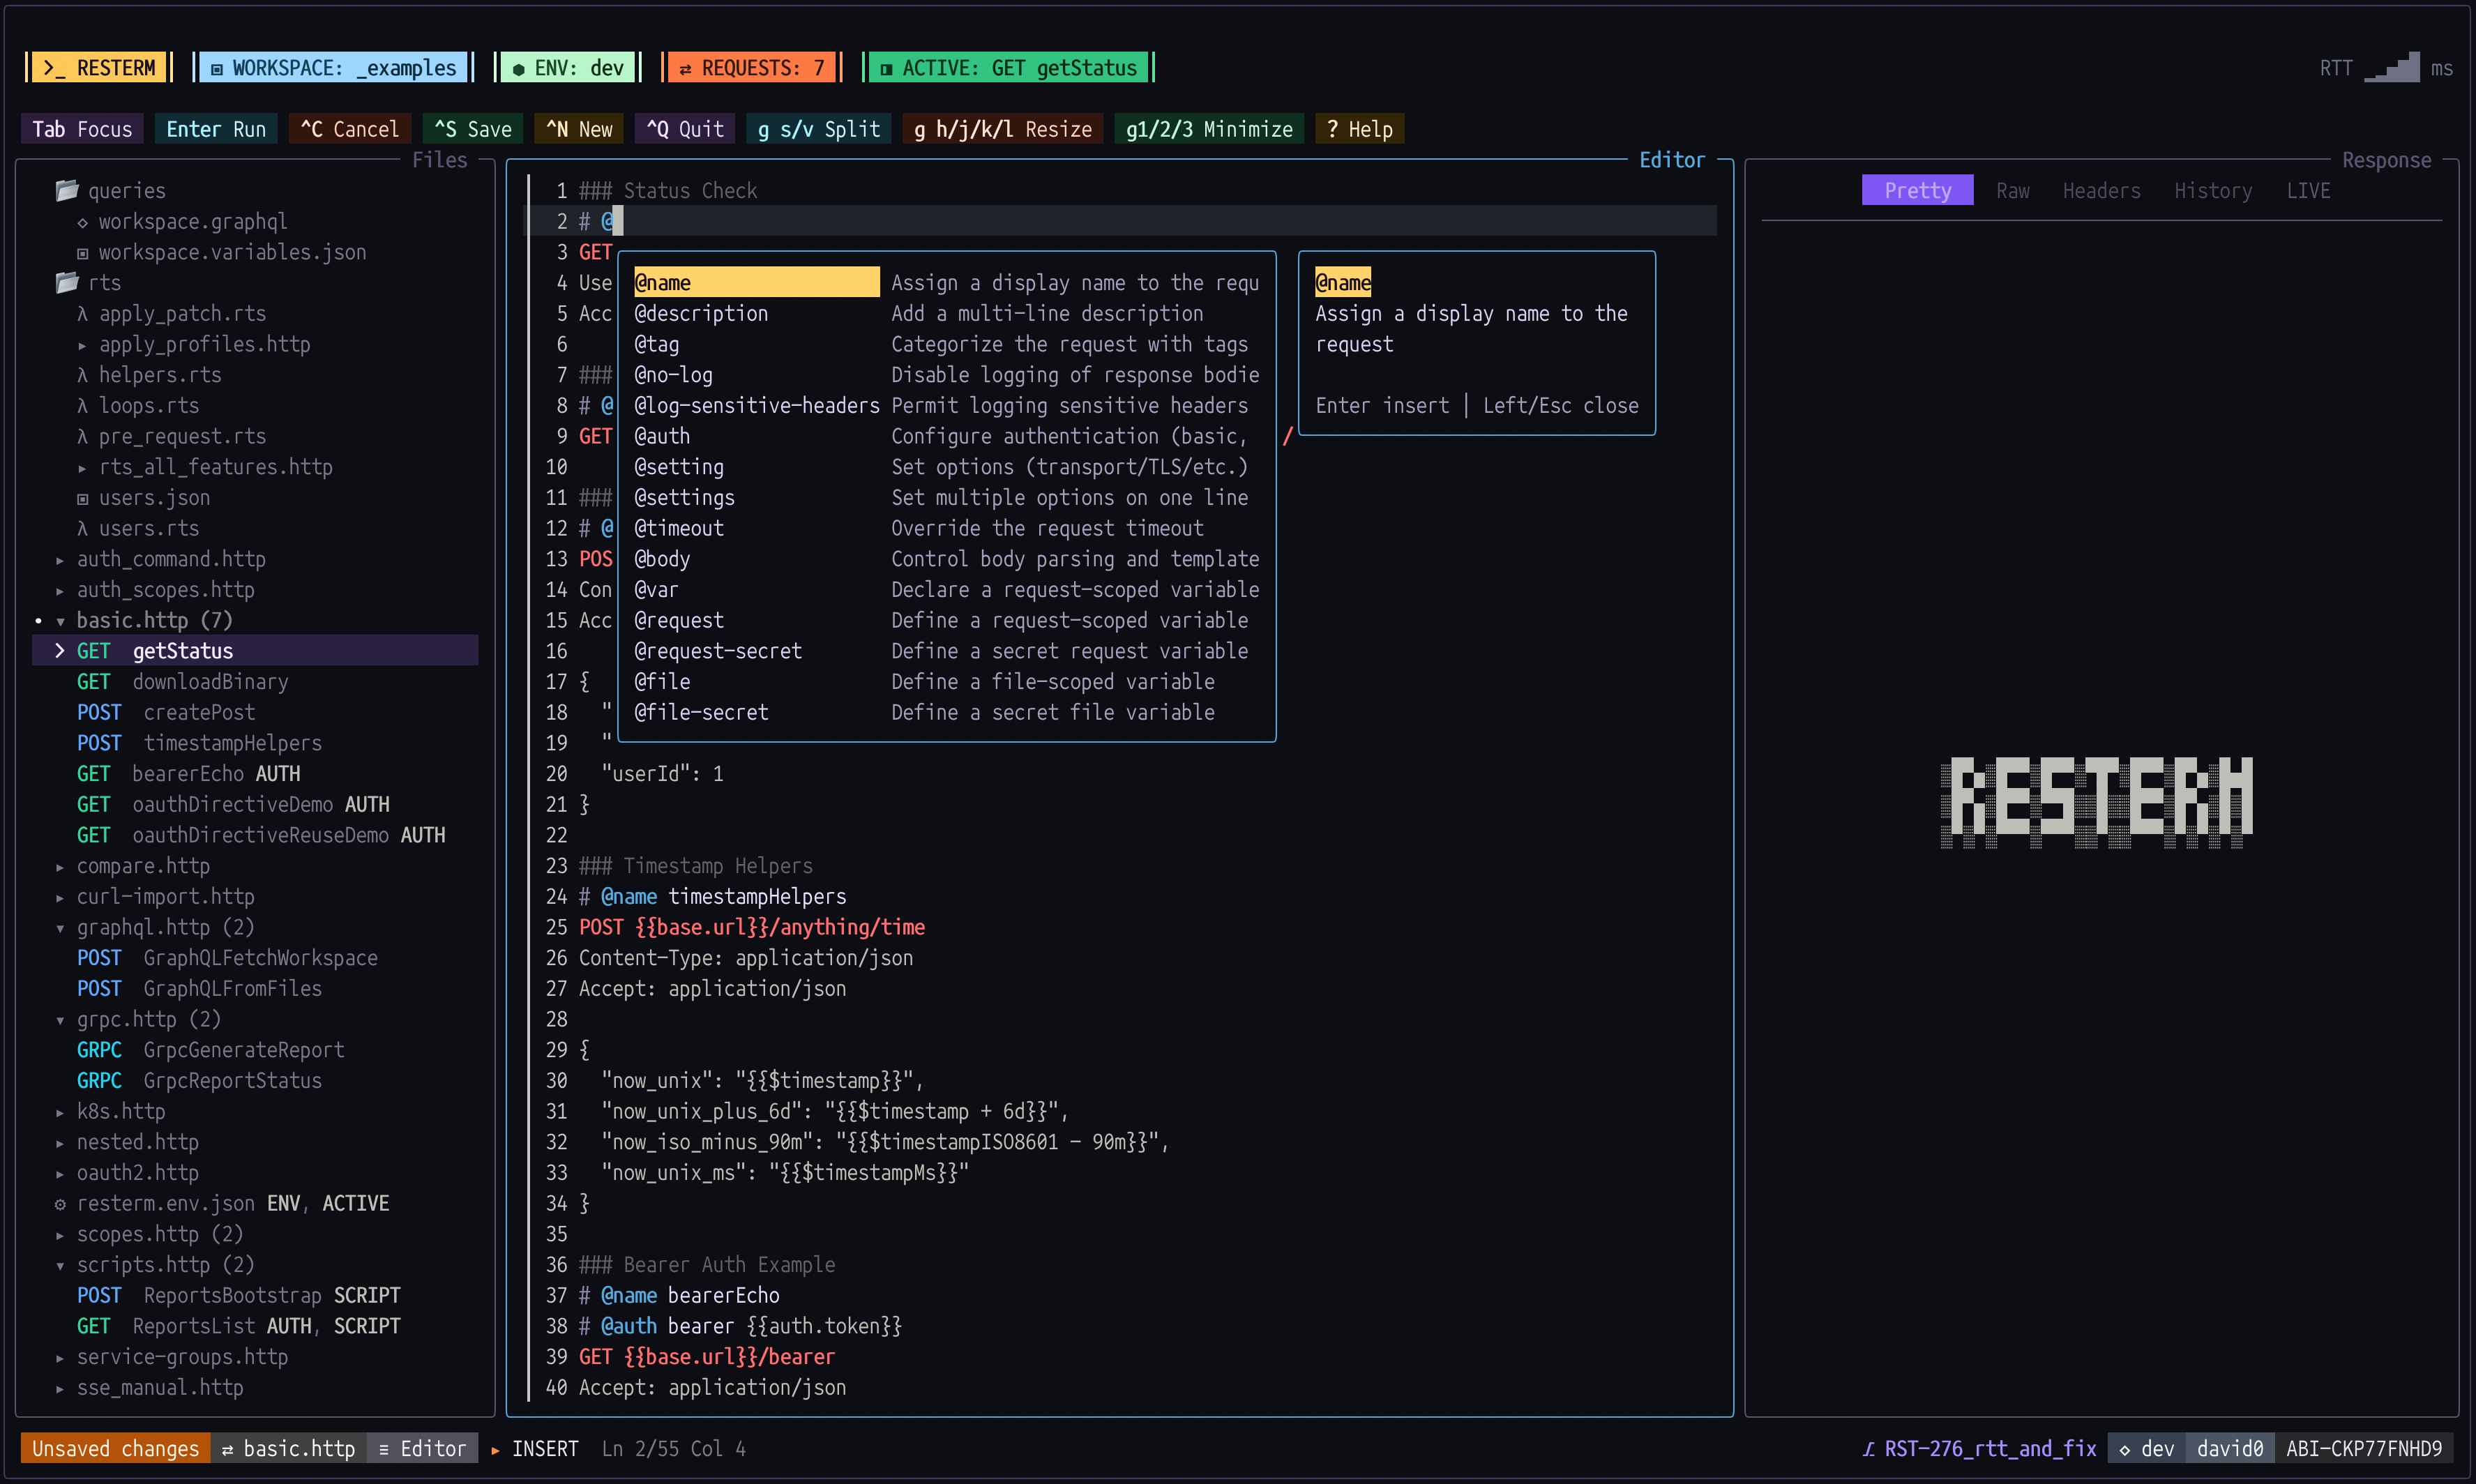 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 getsops/sops
Simple and flexible tool for managing secrets
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 microsoft/igvm
Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…
 gdatasoftwareag/vaas
Verdict-as-a-Service SDKs: Analyze files for malicious content
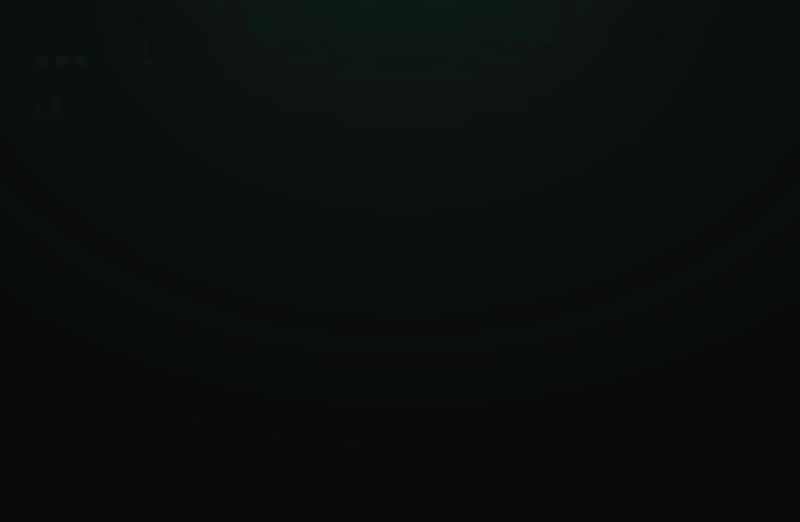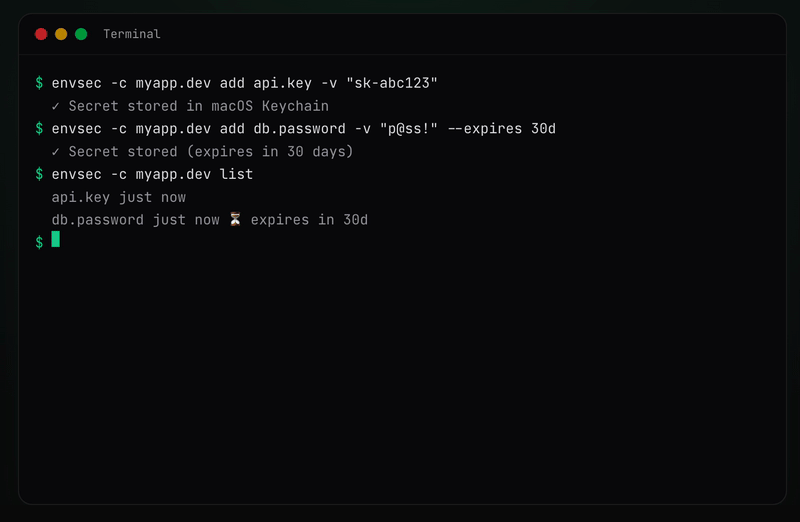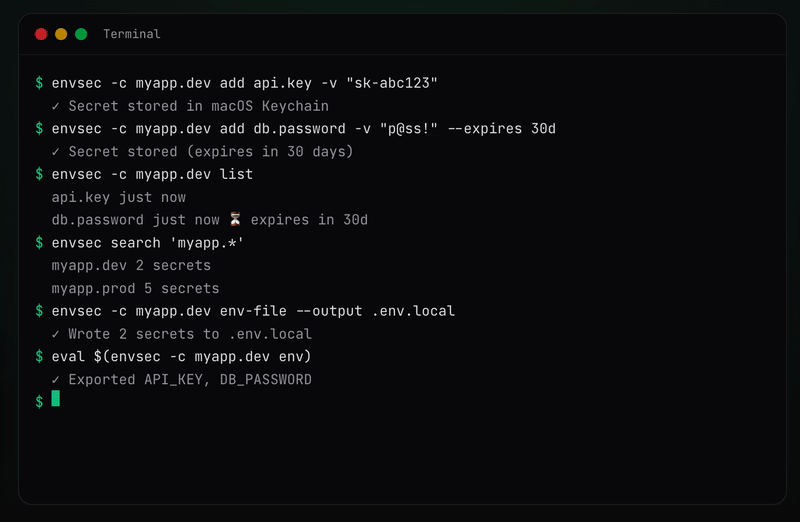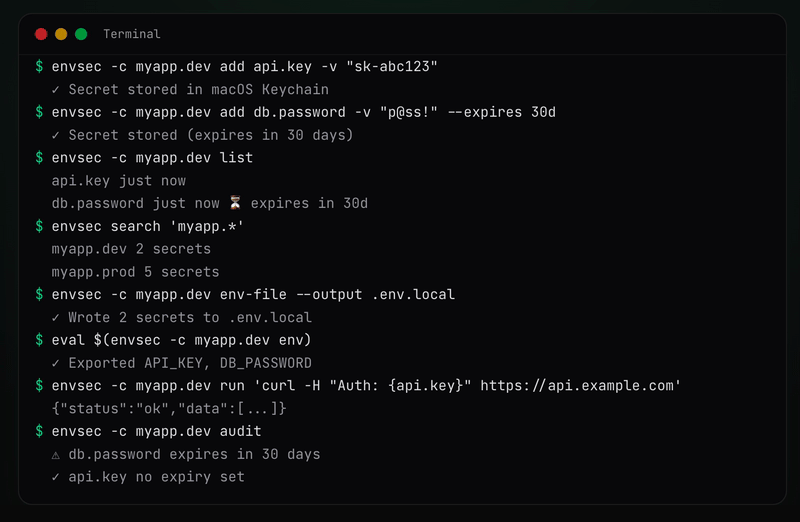 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
 coffinxp/gemini-api-key-hunter
Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…
 boringtools/git-alerts
Tool to detect and monitor GitHub org users' public repositories for secrets and sensitive files
 nccgroup/s3_objects_check
Whitebox evaluation of effective S3 object permissions, to identify publicly accessible files.
 fleralex/enseal
Secure, ephemeral secret sharing for developers.
 tcollins-hashicorp/vault-cve-2026-5006-audit
Audit and educational toolkit for CVE-2026-5006, a Vault templated-policy slash-injection vulnerability. Includes a read-only audit script generating…