prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

Cloudsplaining is an AWS IAM Security Assessment tool that identifies violations of least privilege and generates a risk-prioritized report.

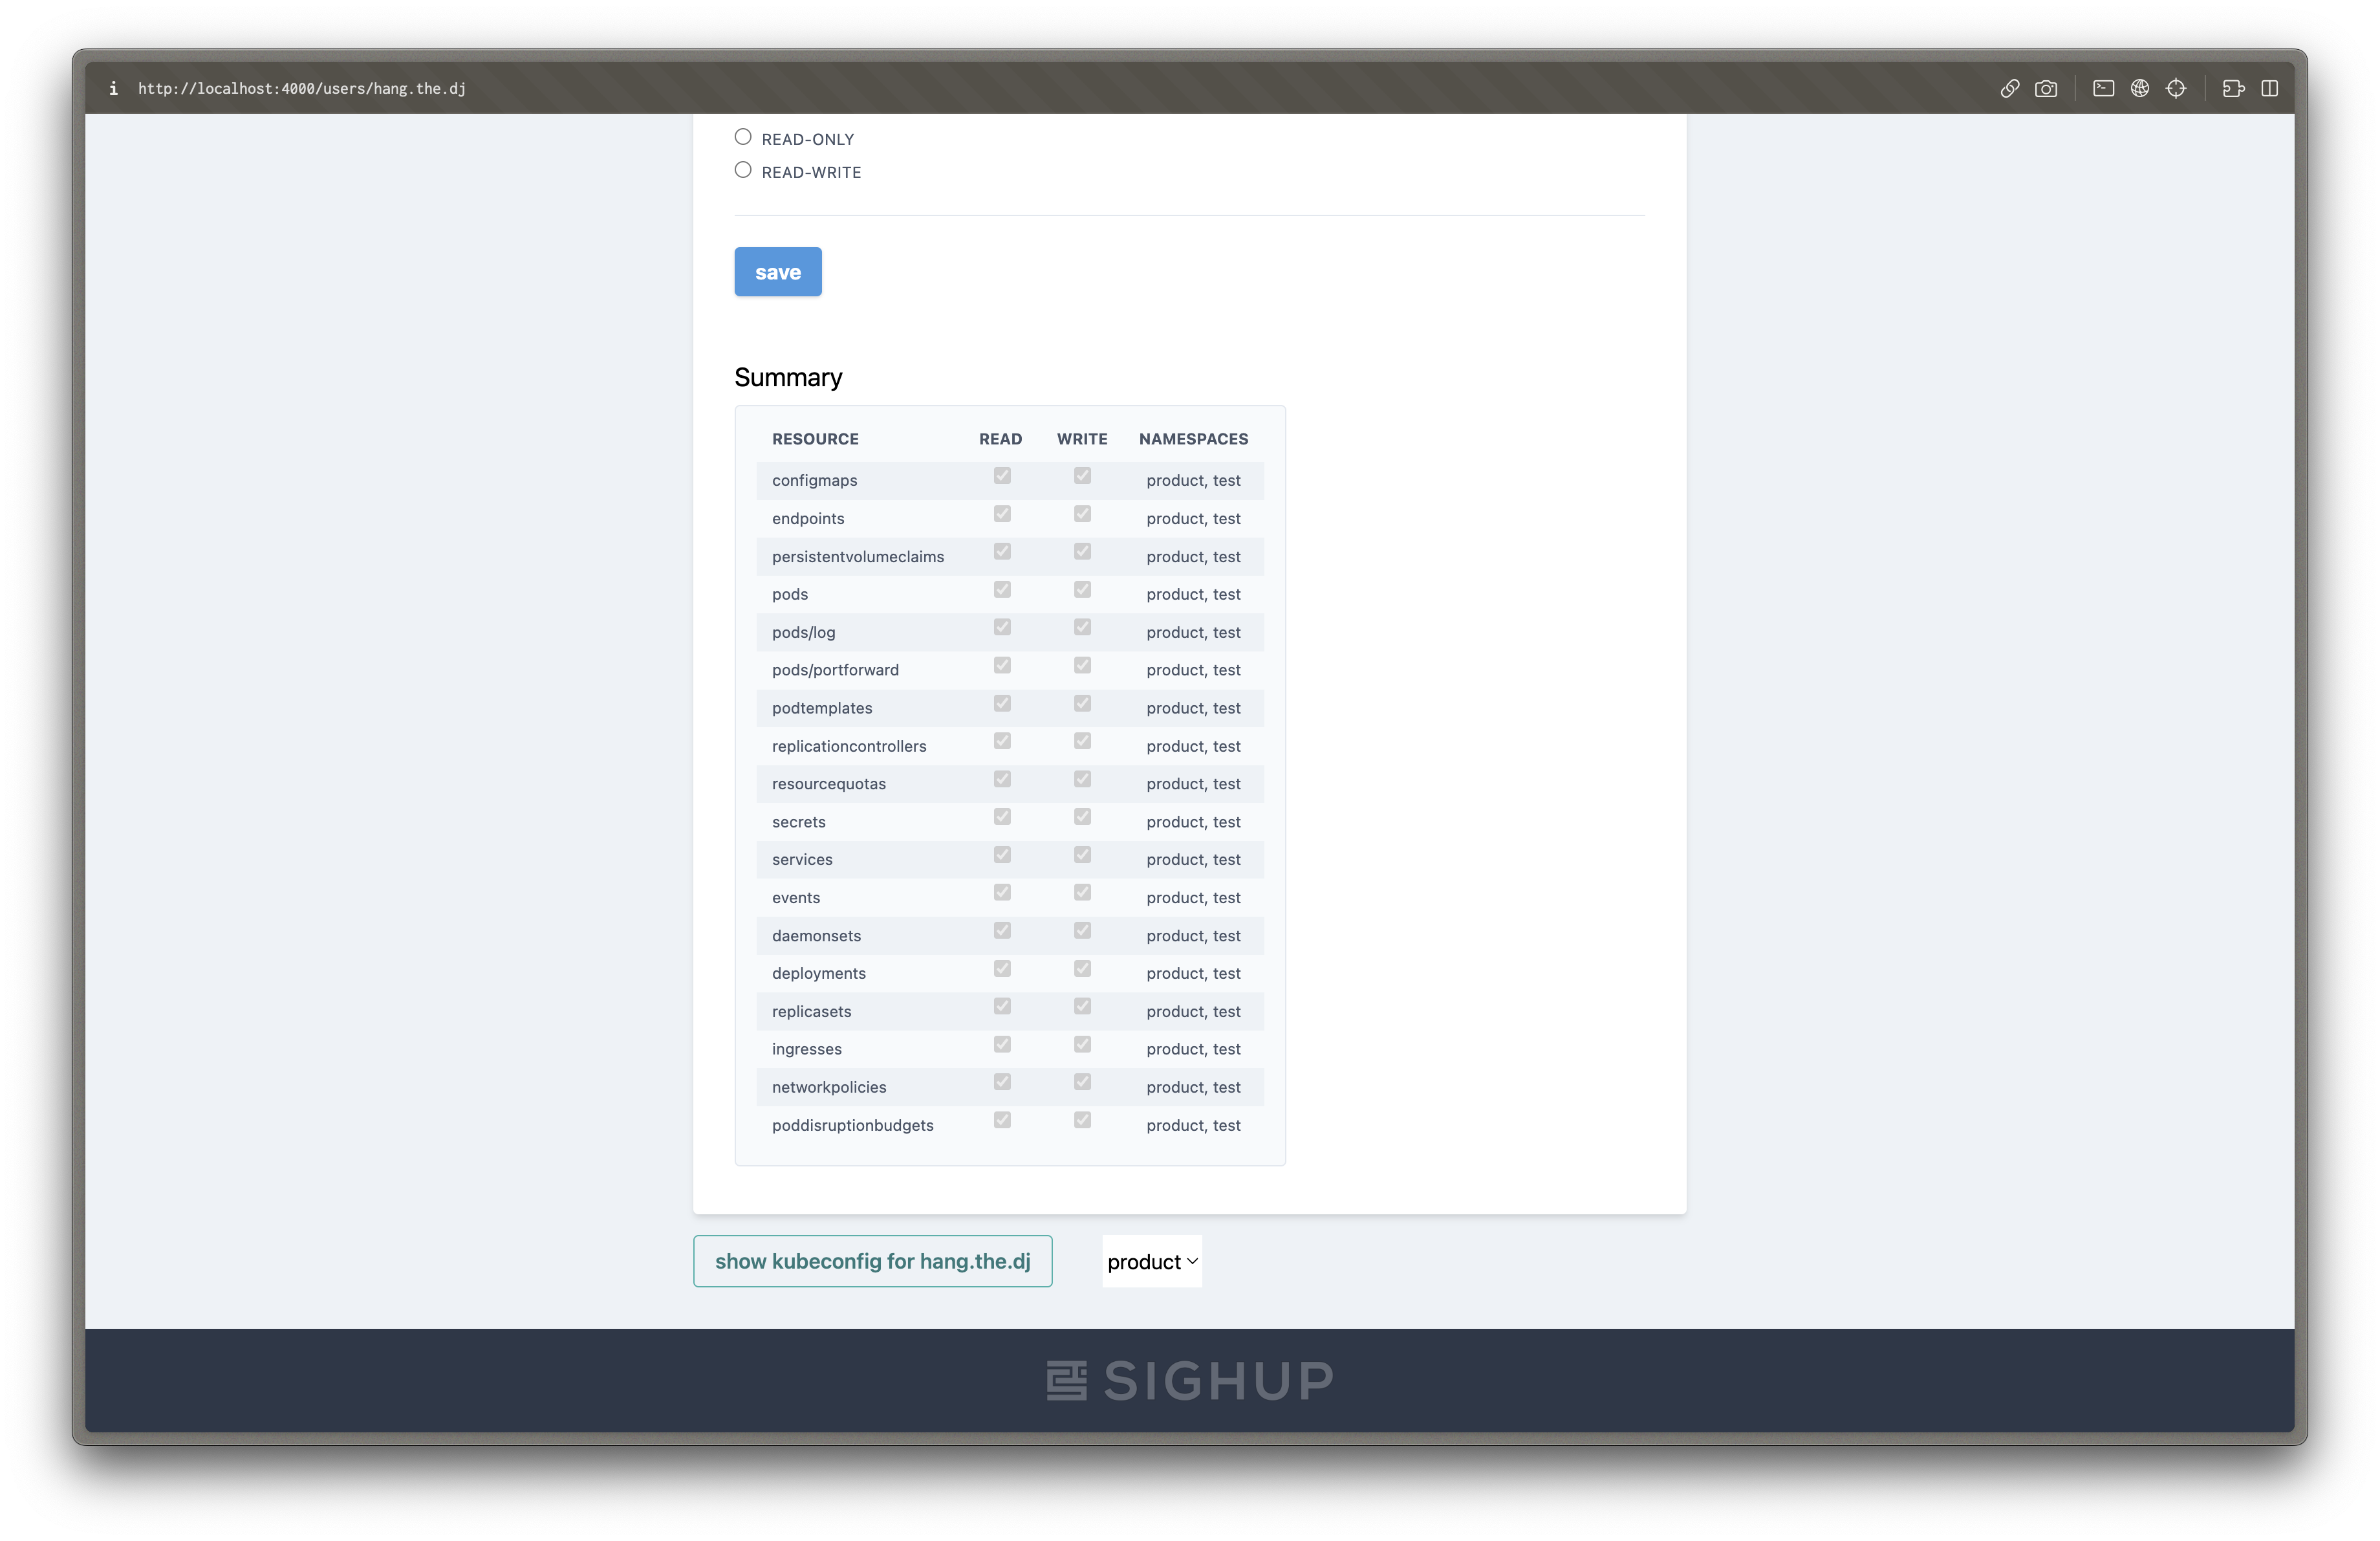
Permission Manager is a project that brings sanity to Kubernetes RBAC and Users management, Web UI FTW

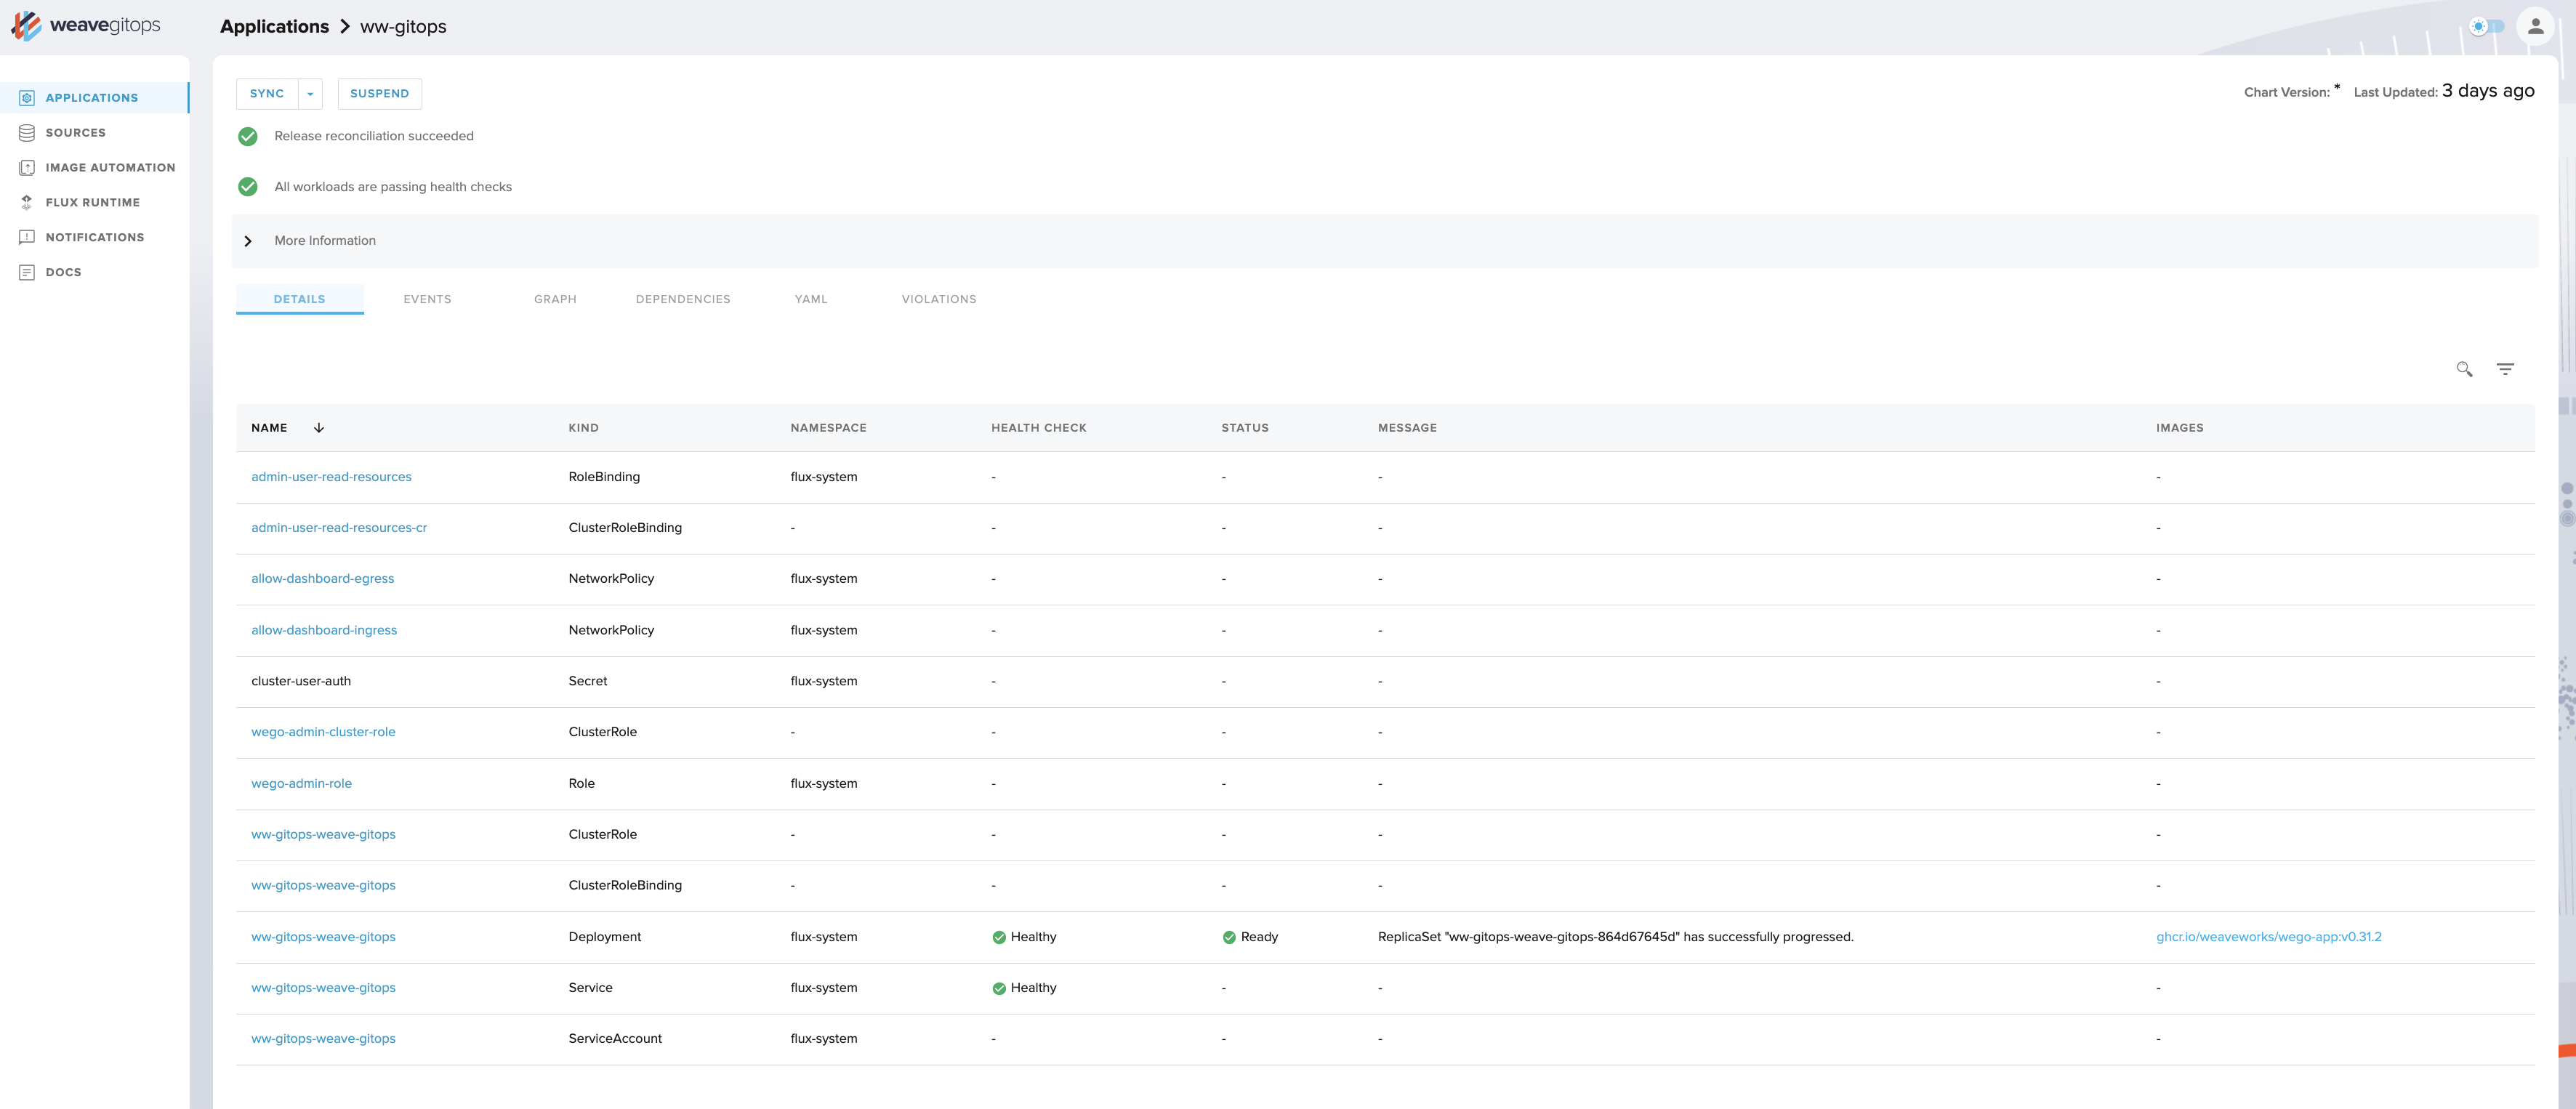
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…

🛡️ 🔒 This project's goal is to be simple to create and destroy your own VPN service using WireGuard.

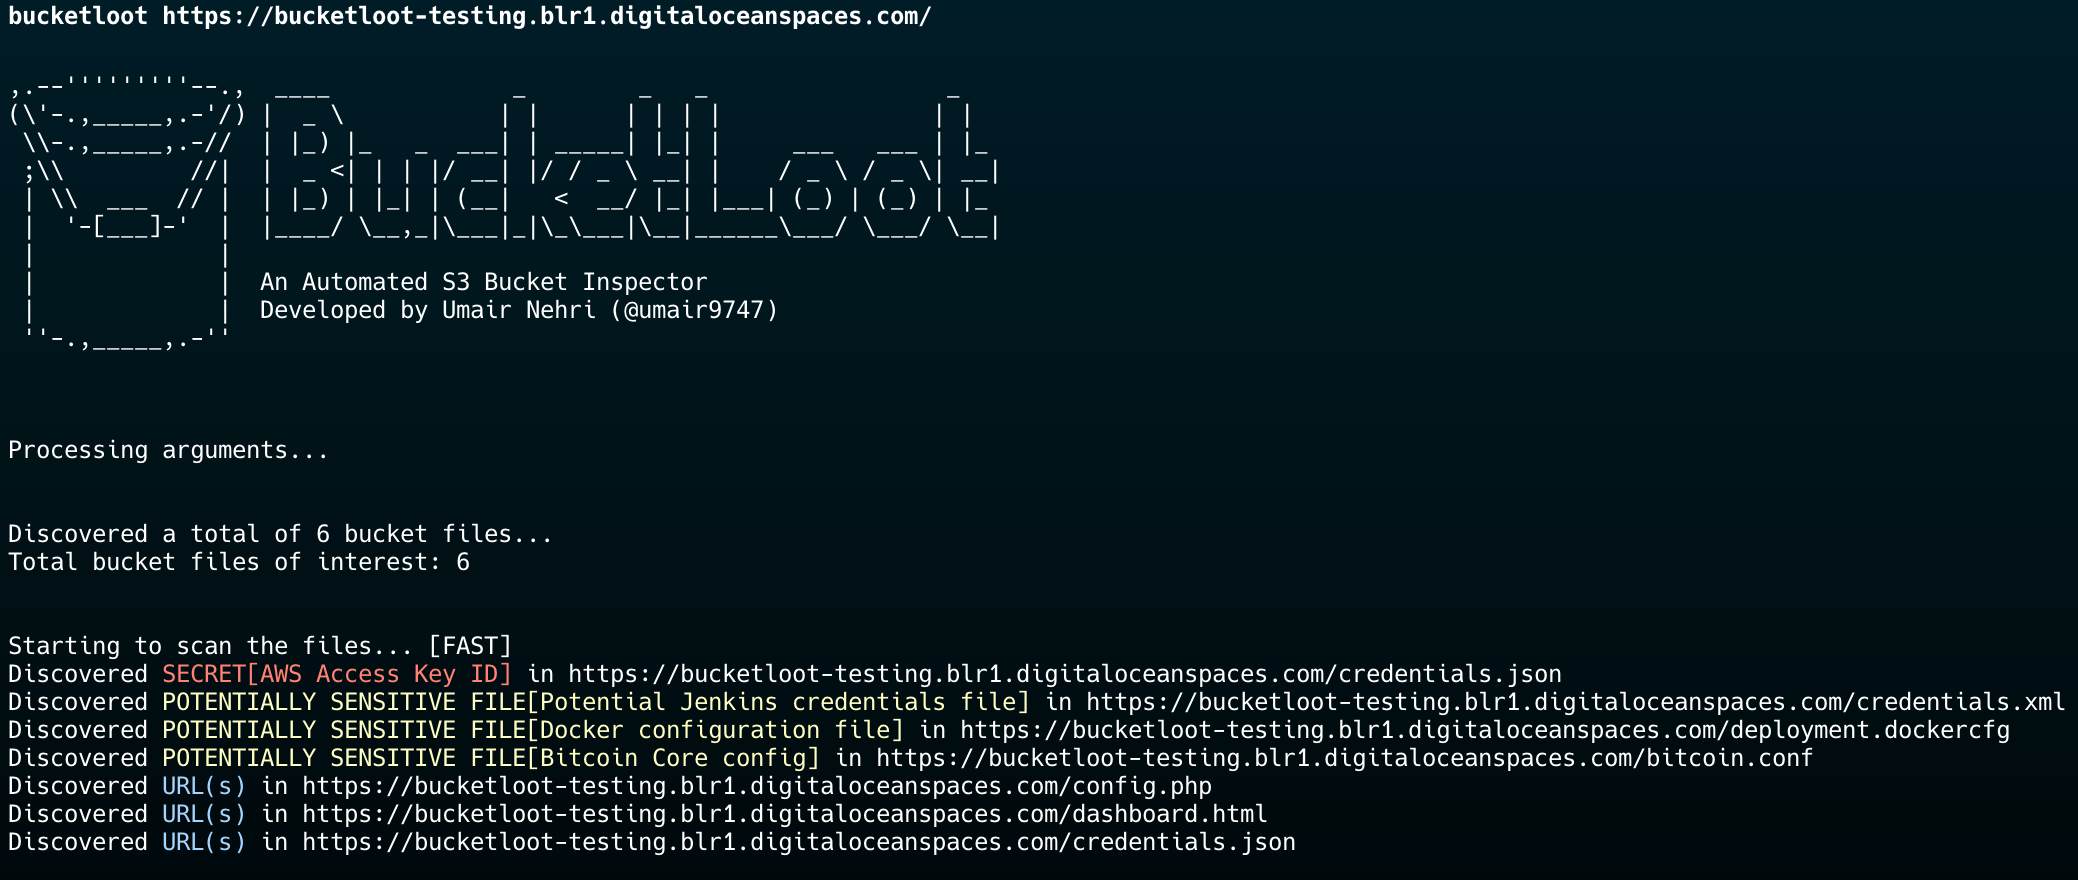
BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…

CNAPPgoat is an open source project designed to modularly provision vulnerable-by-design components in cloud environments.

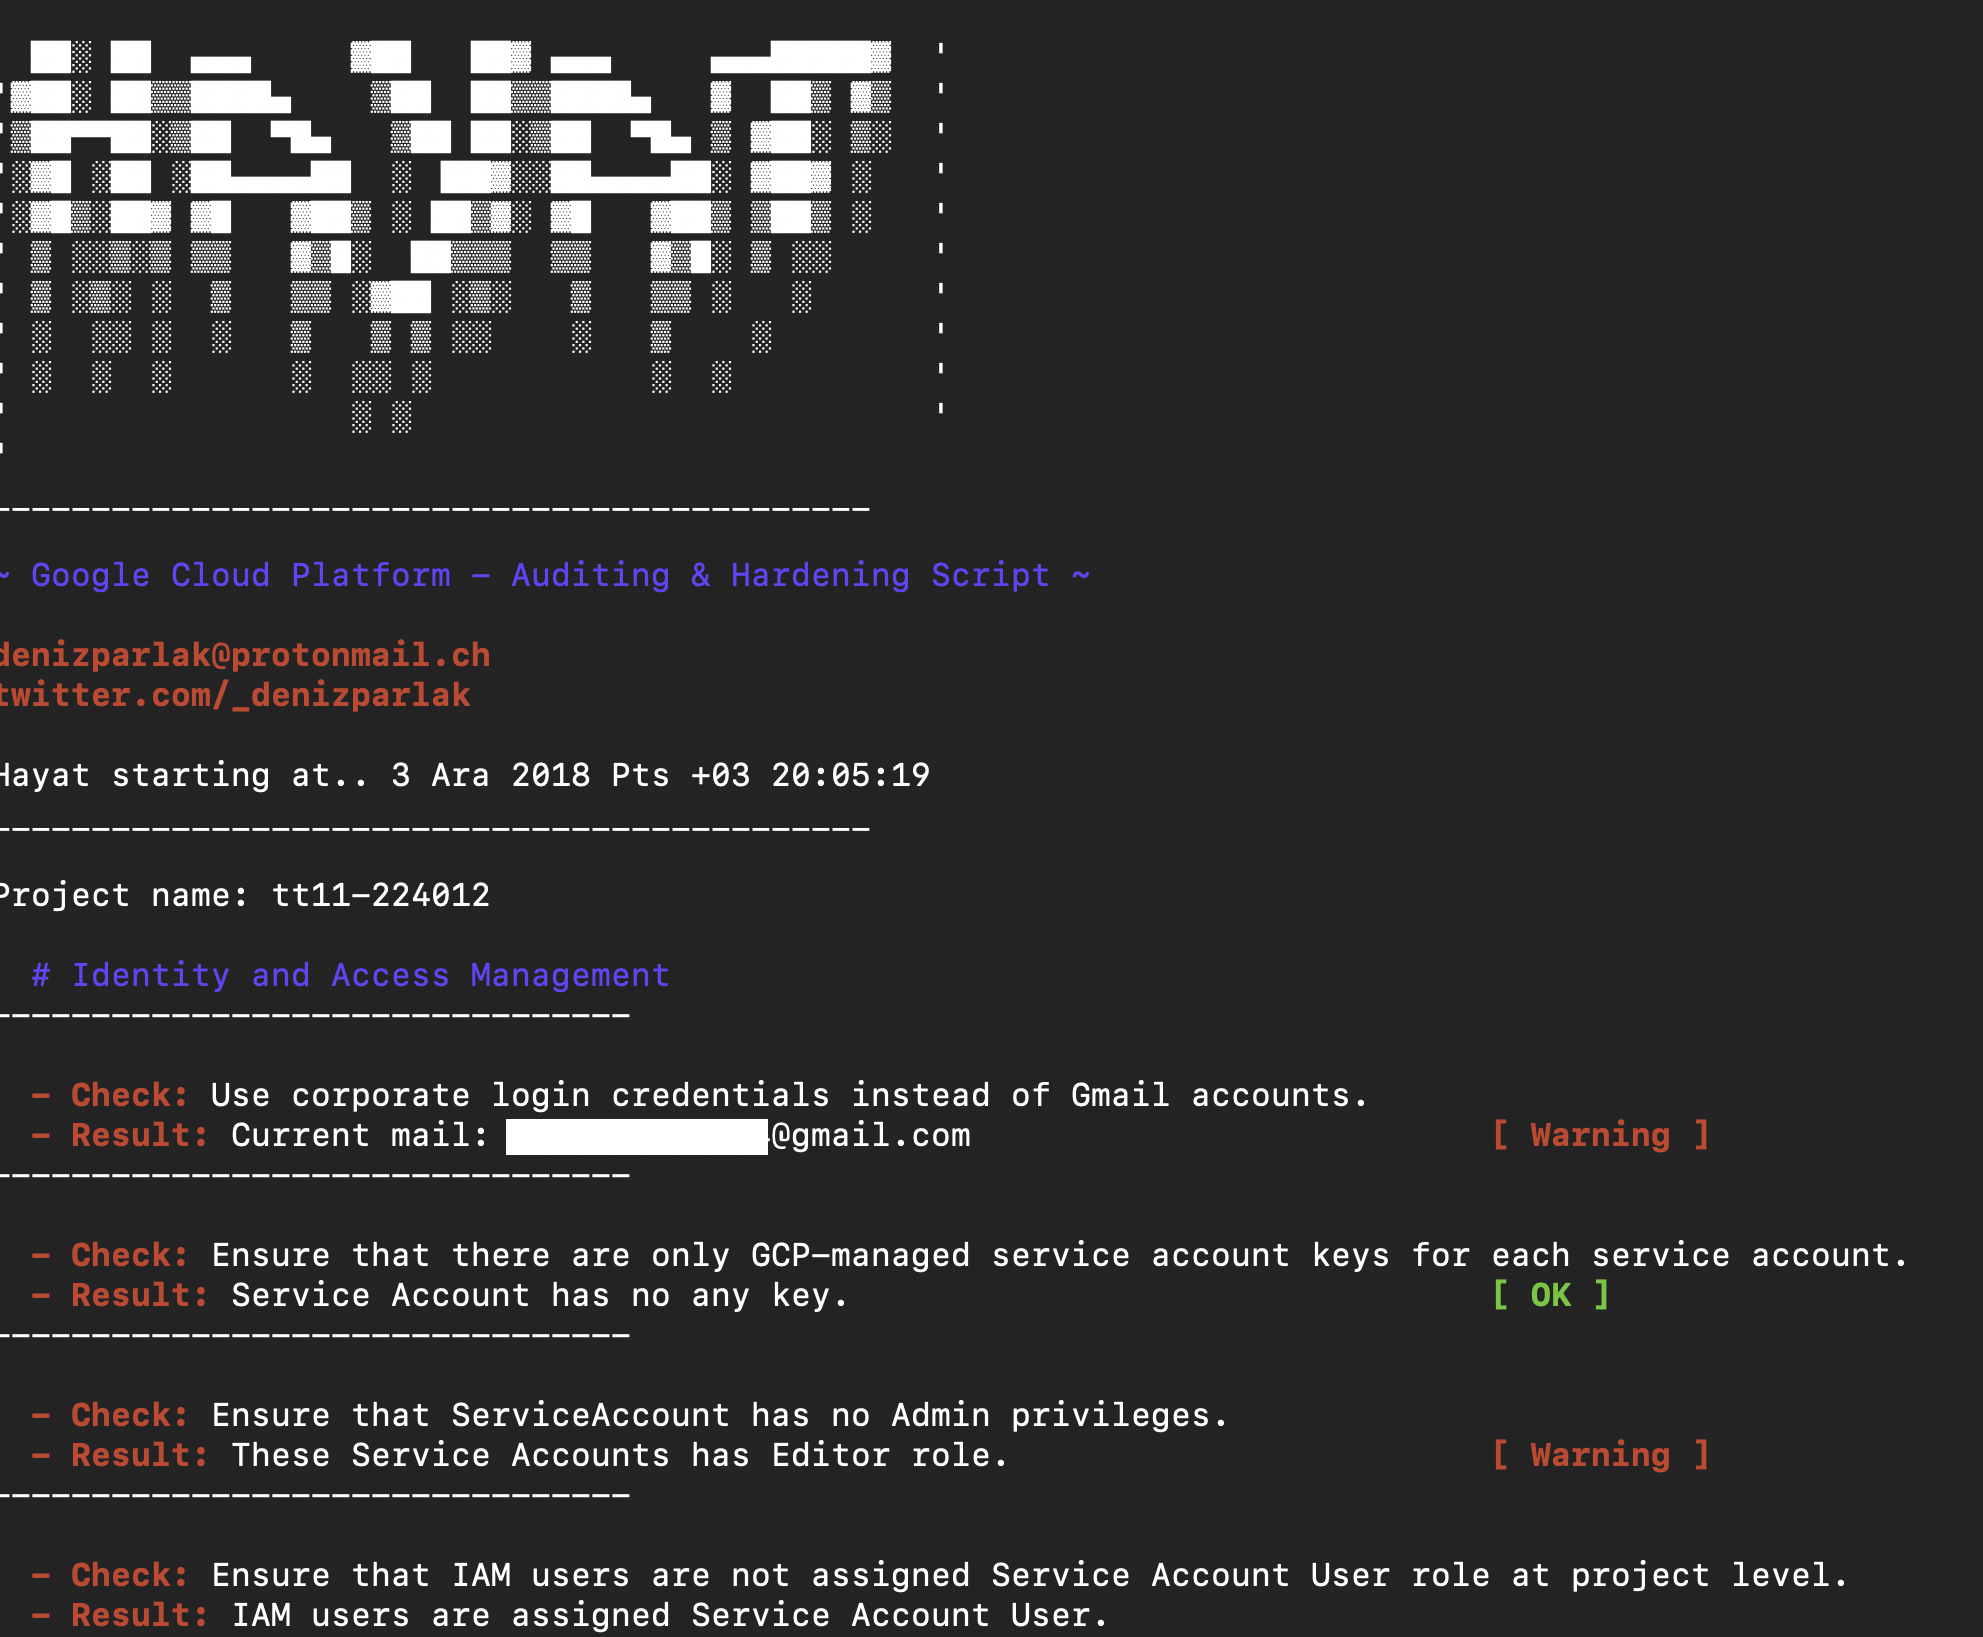
Hayat is a script for report and analyze Google Cloud Platform resources.

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…

CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…

GitHub Actions workflow to test if the runner is vulnerable to CVE-2026-31431, confirming root privileges in a controlled environment.

Mitigates CVE-2026-31431 (Copy Fail) by unloading and blacklisting algif_aead kernel module if it is loadable and has no active references.

This is a script designed for deployment on ubuntu instances patching the CVE-2026-3888 exploit

OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure