
s3crets_scanner
Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and…

Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and…

The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.

CNAPPgoat is an open source project designed to modularly provision vulnerable-by-design components in cloud environments.

🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files

CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…

This is a script designed for deployment on ubuntu instances patching the CVE-2026-3888 exploit

CVE-2020-9483 OR CVE-2020-13921

Ansible playbook for patching CVE-2024-3094

Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…

Cloud-native Kubernetes cluster inspection tool that detects application misconfigurations, unhealthy components, and node problems using custom OPA,…

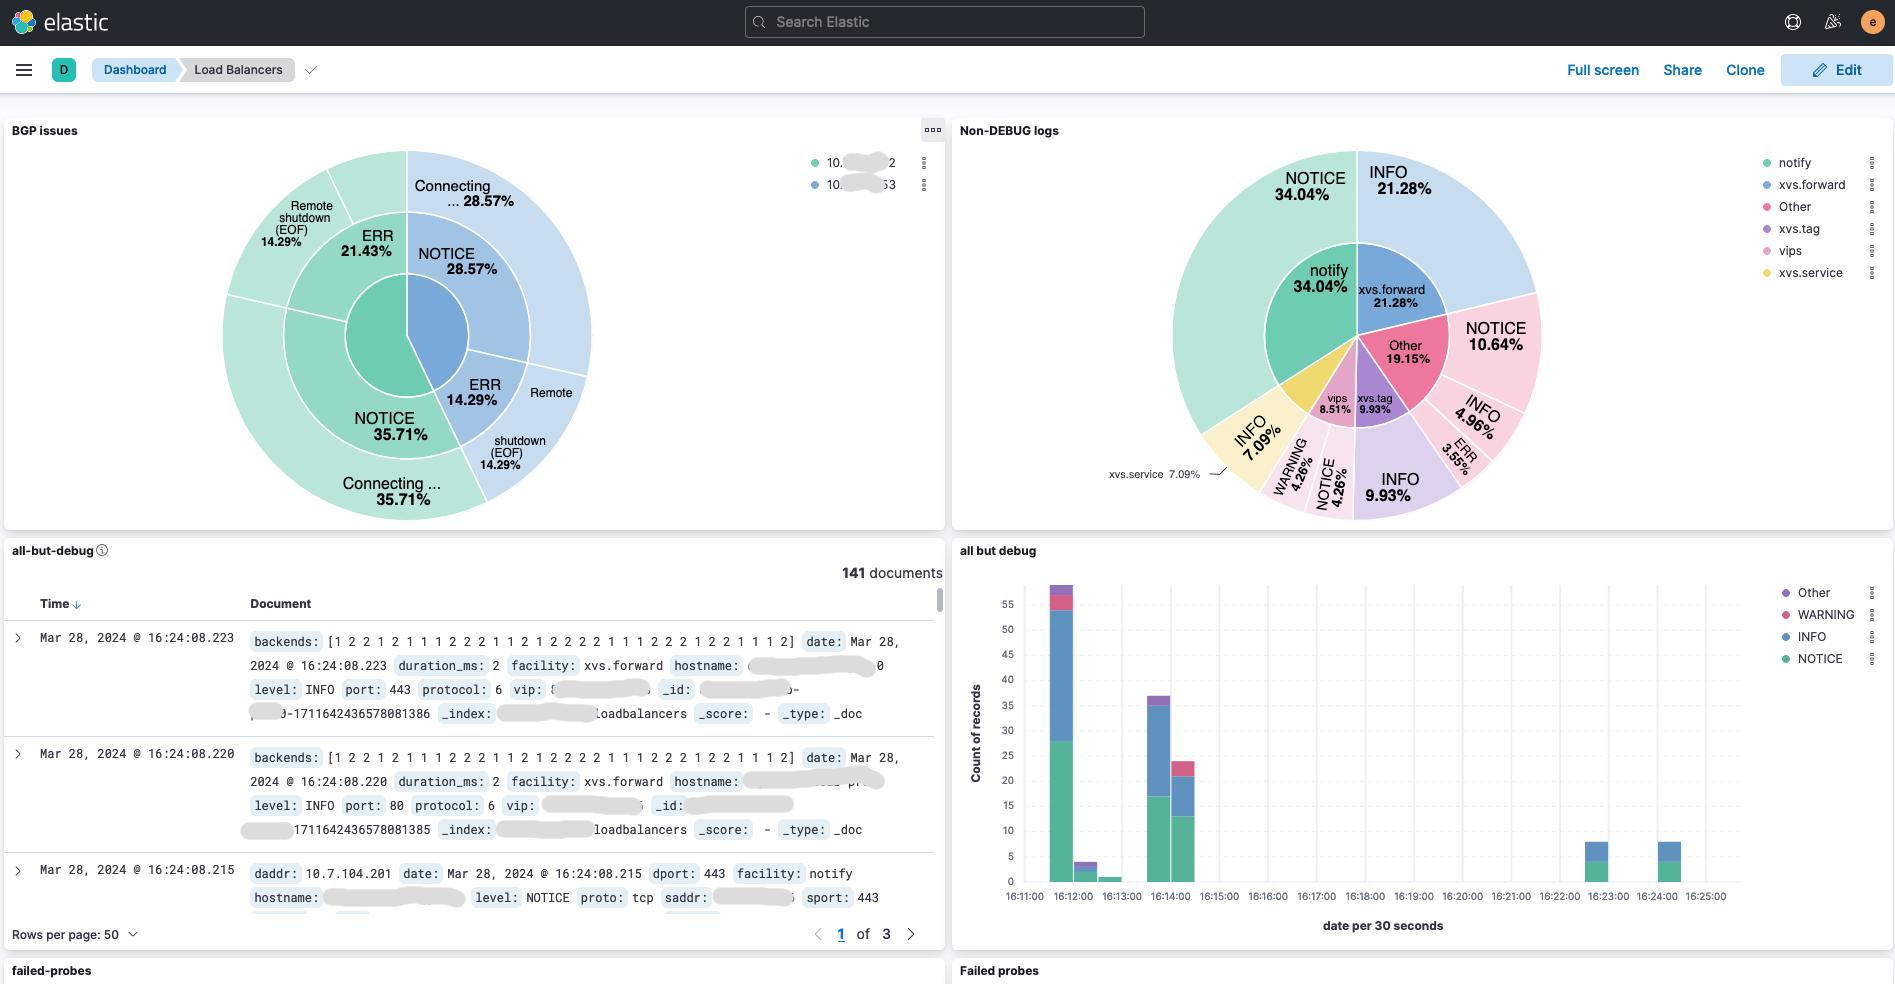
A horizontally scalable Direct Server Return layer 4 load balancer for Linux using XDP/eBPF

Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)

Passive, read-only vulnerability scanner for detecting CVE-2026-41940 in cPanel & WHM. Performs version-based fingerprinting, generates…

Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026