
vmsan
 angelorc/vmsan
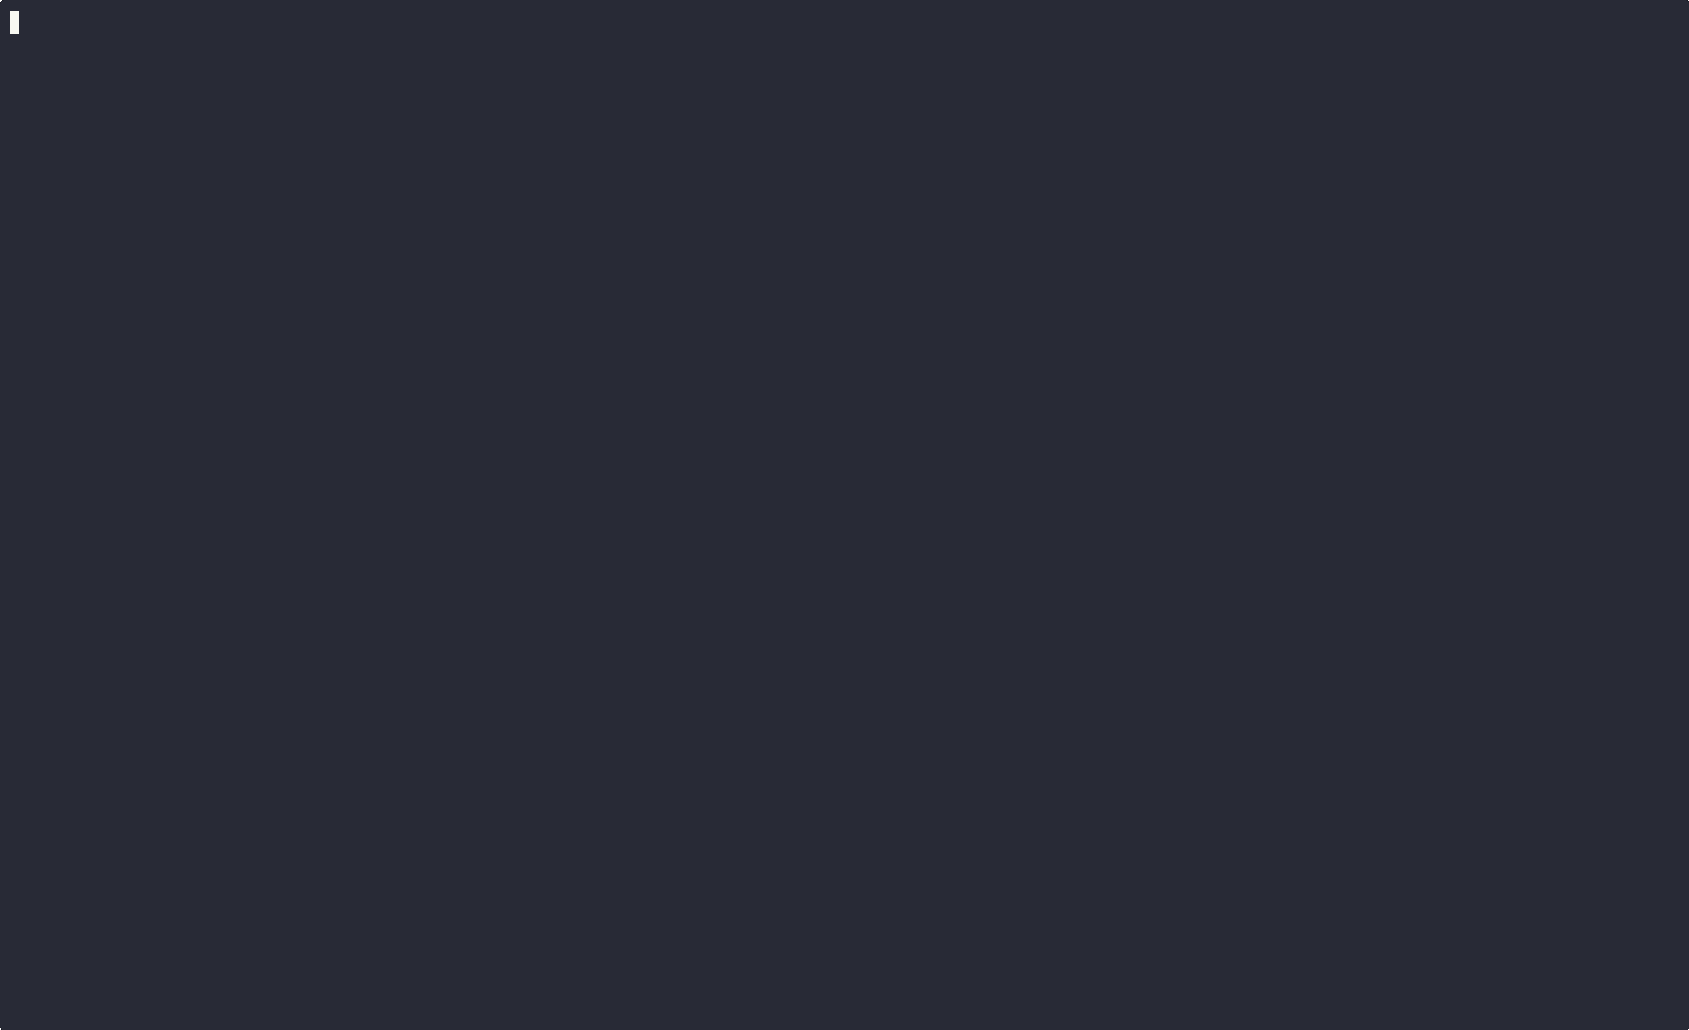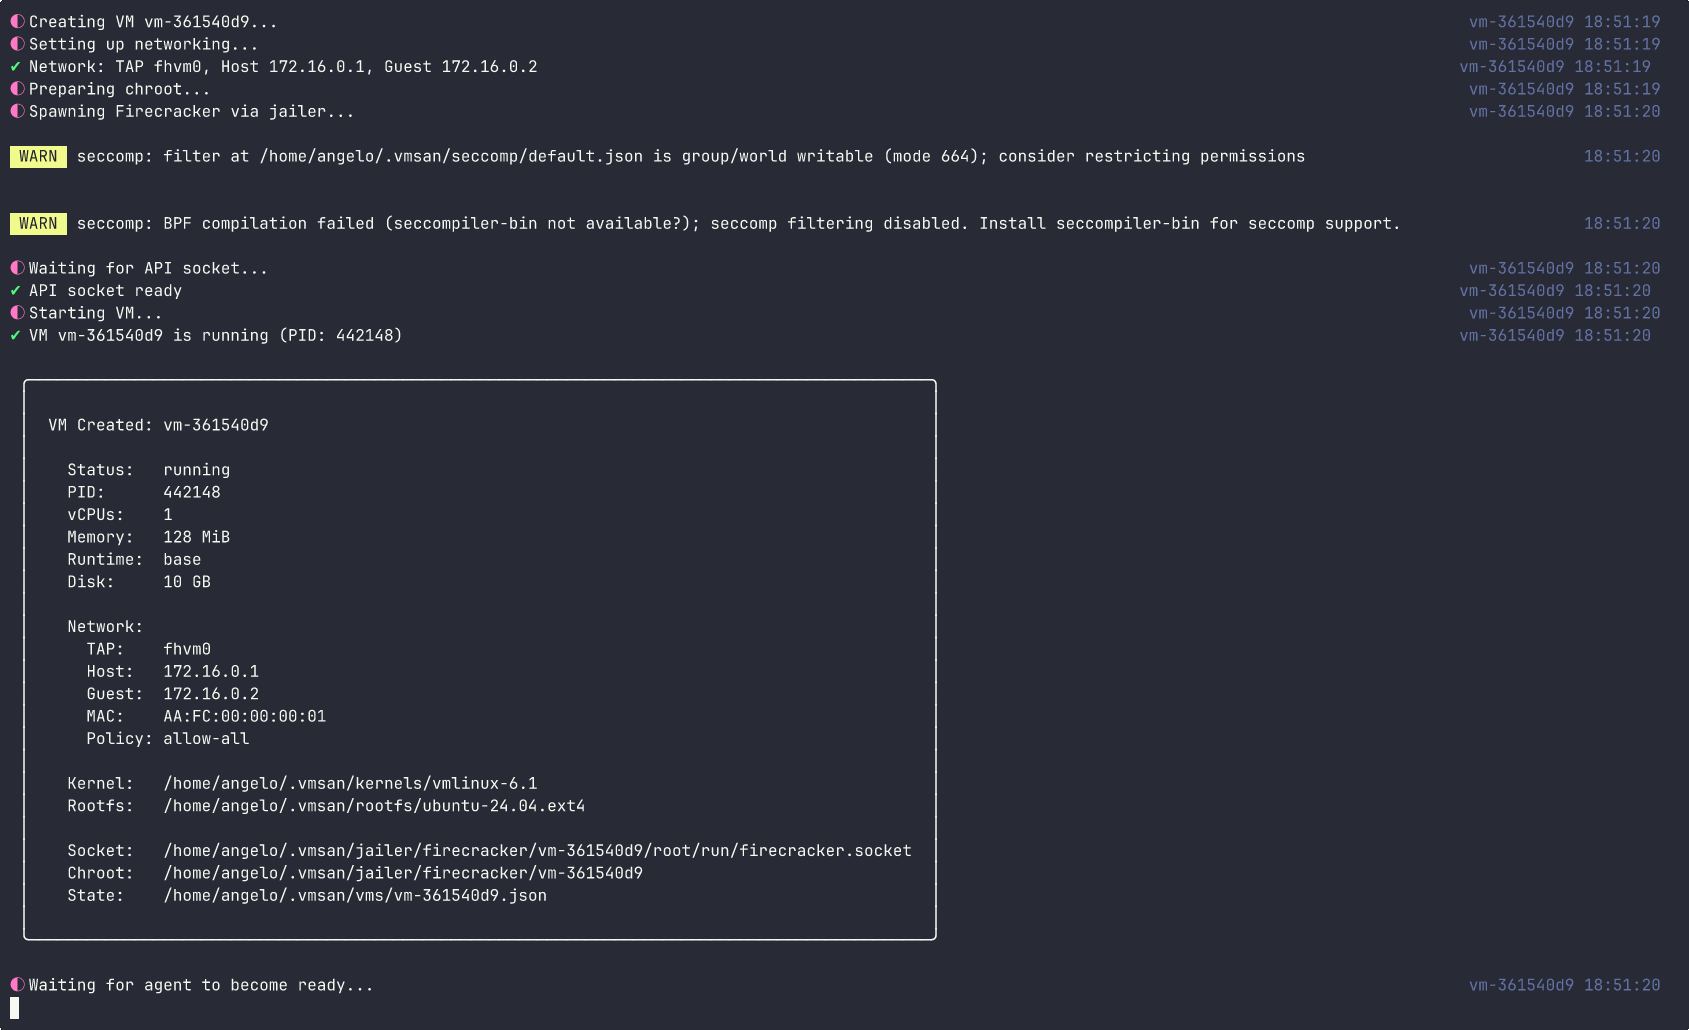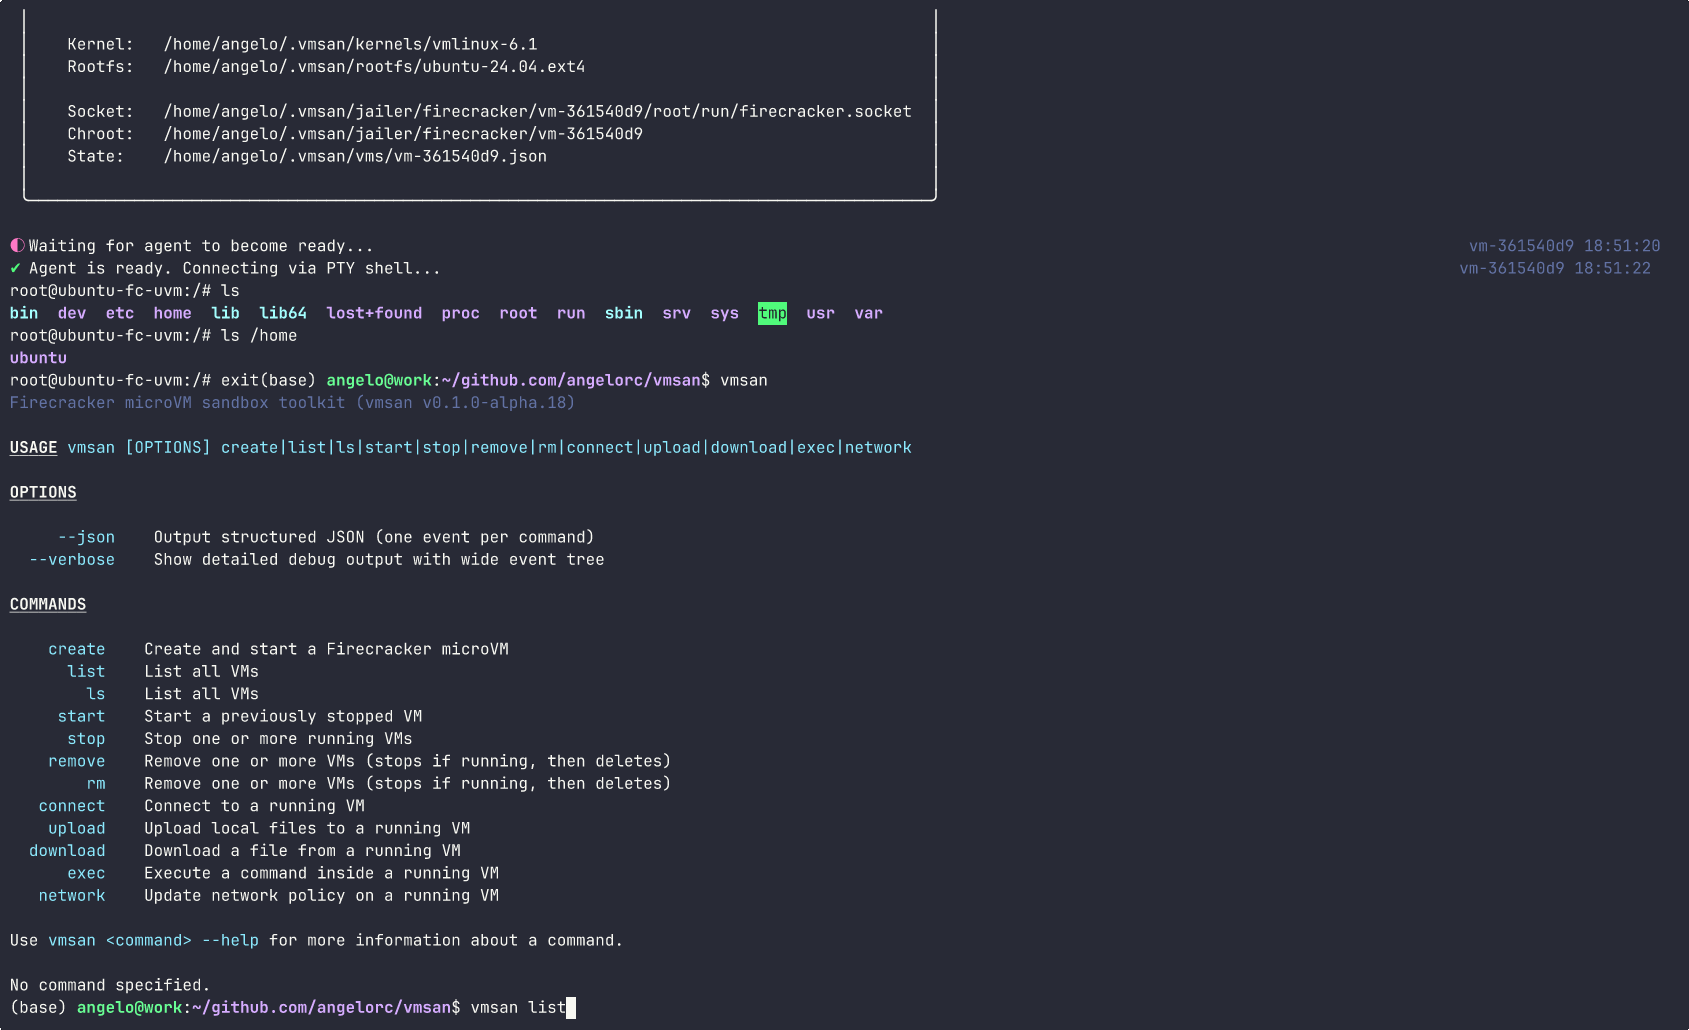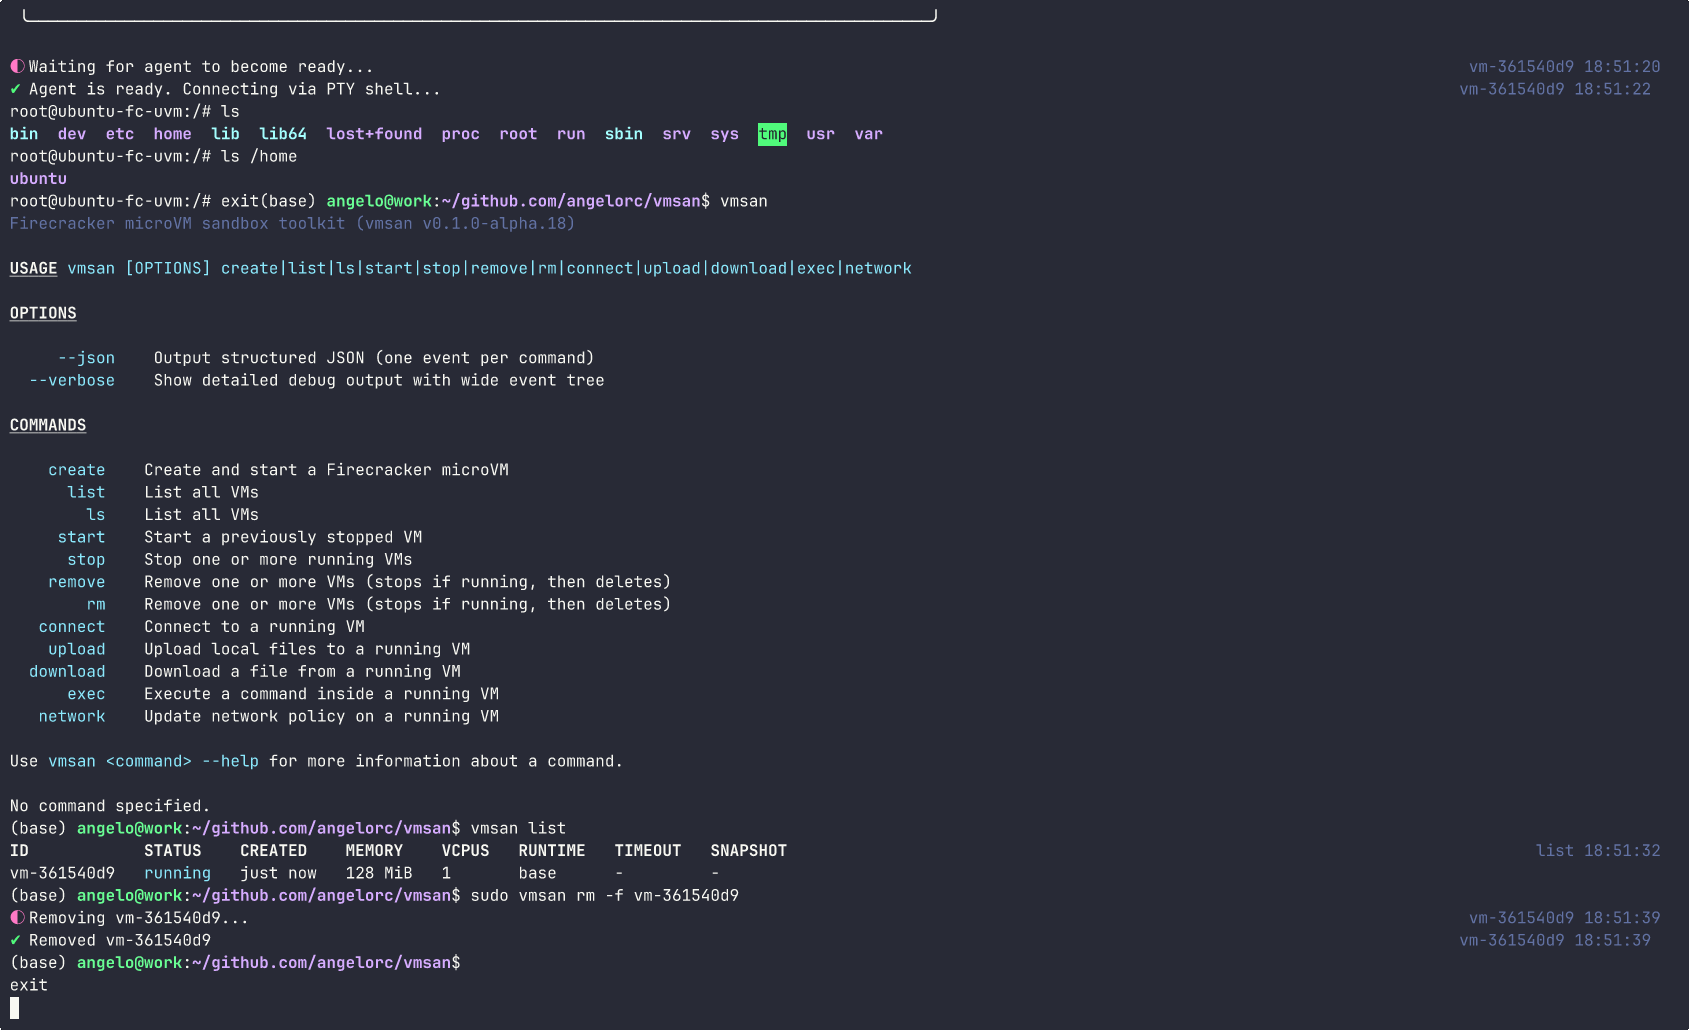
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
cloud-infrastructure-securitycontainer-securitydevsecops+3
87
angelorc/vmsanFirecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 tenable/kaimonkey
Deliberately vulnerable Terraform infrastructure for learning cloud security misconfigurations and validating IaC scanner detection across AWS and…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 crowdstrike/crt
Audits Azure AD and Exchange Online configurations for hard-to-find permissions, federation trusts, mail forwarding rules, and delegated access to…
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 salesforce/metabadger
Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).
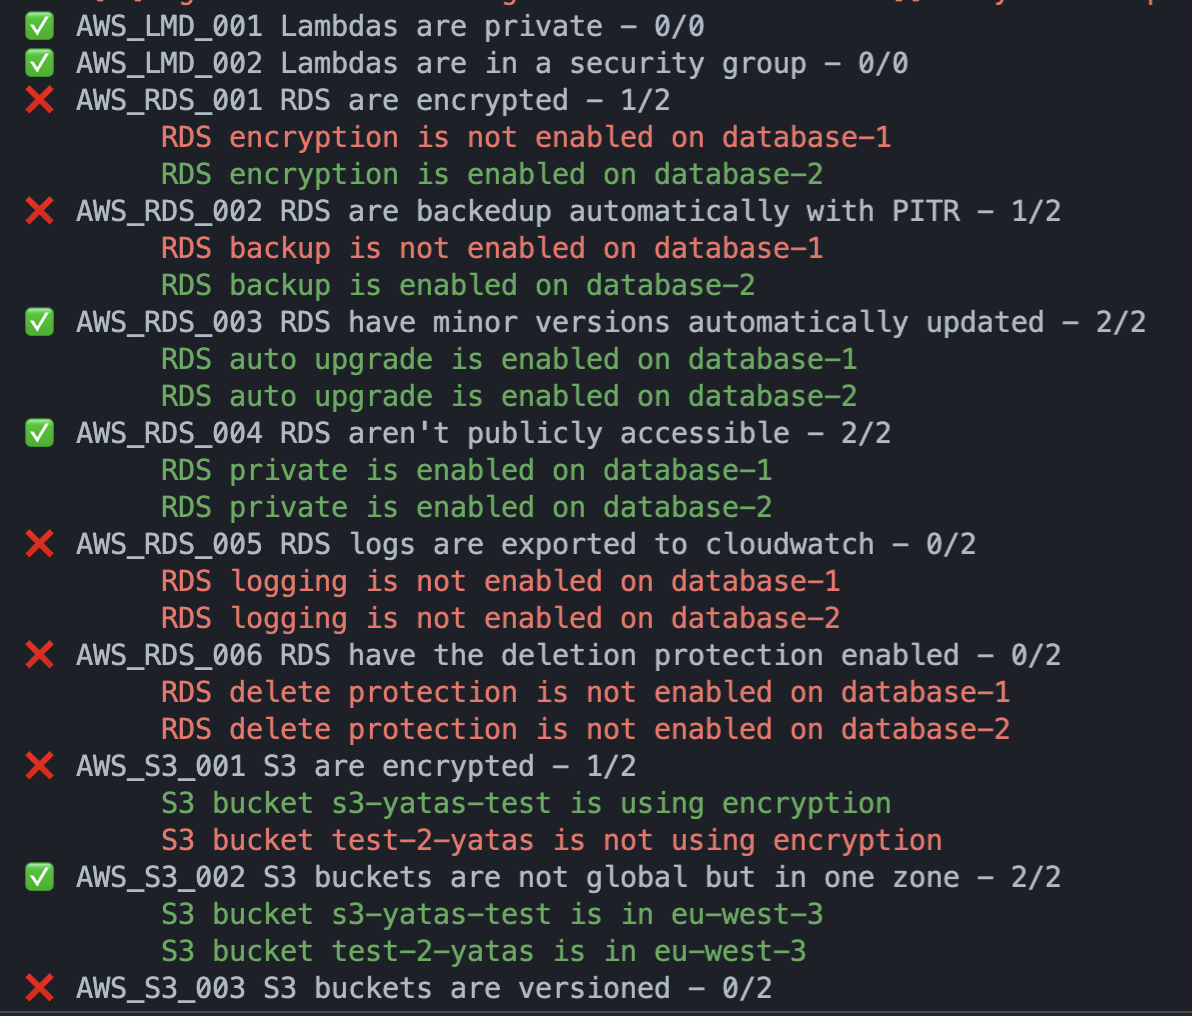 padok-team/yatas
:owl::mag_right: A simple tool to audit your AWS/GCP infrastructure for misconfiguration or potential security issues with plugins integration
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
 nozaq/terraform-aws-secure-baseline
Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
 mailcow/mailcow-dockerized
Dockerized mail server suite with Postfix, Dovecot, Rspamd, and ClamAV. Provides secure email hosting with integrated spam filtering, antivirus, and…
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
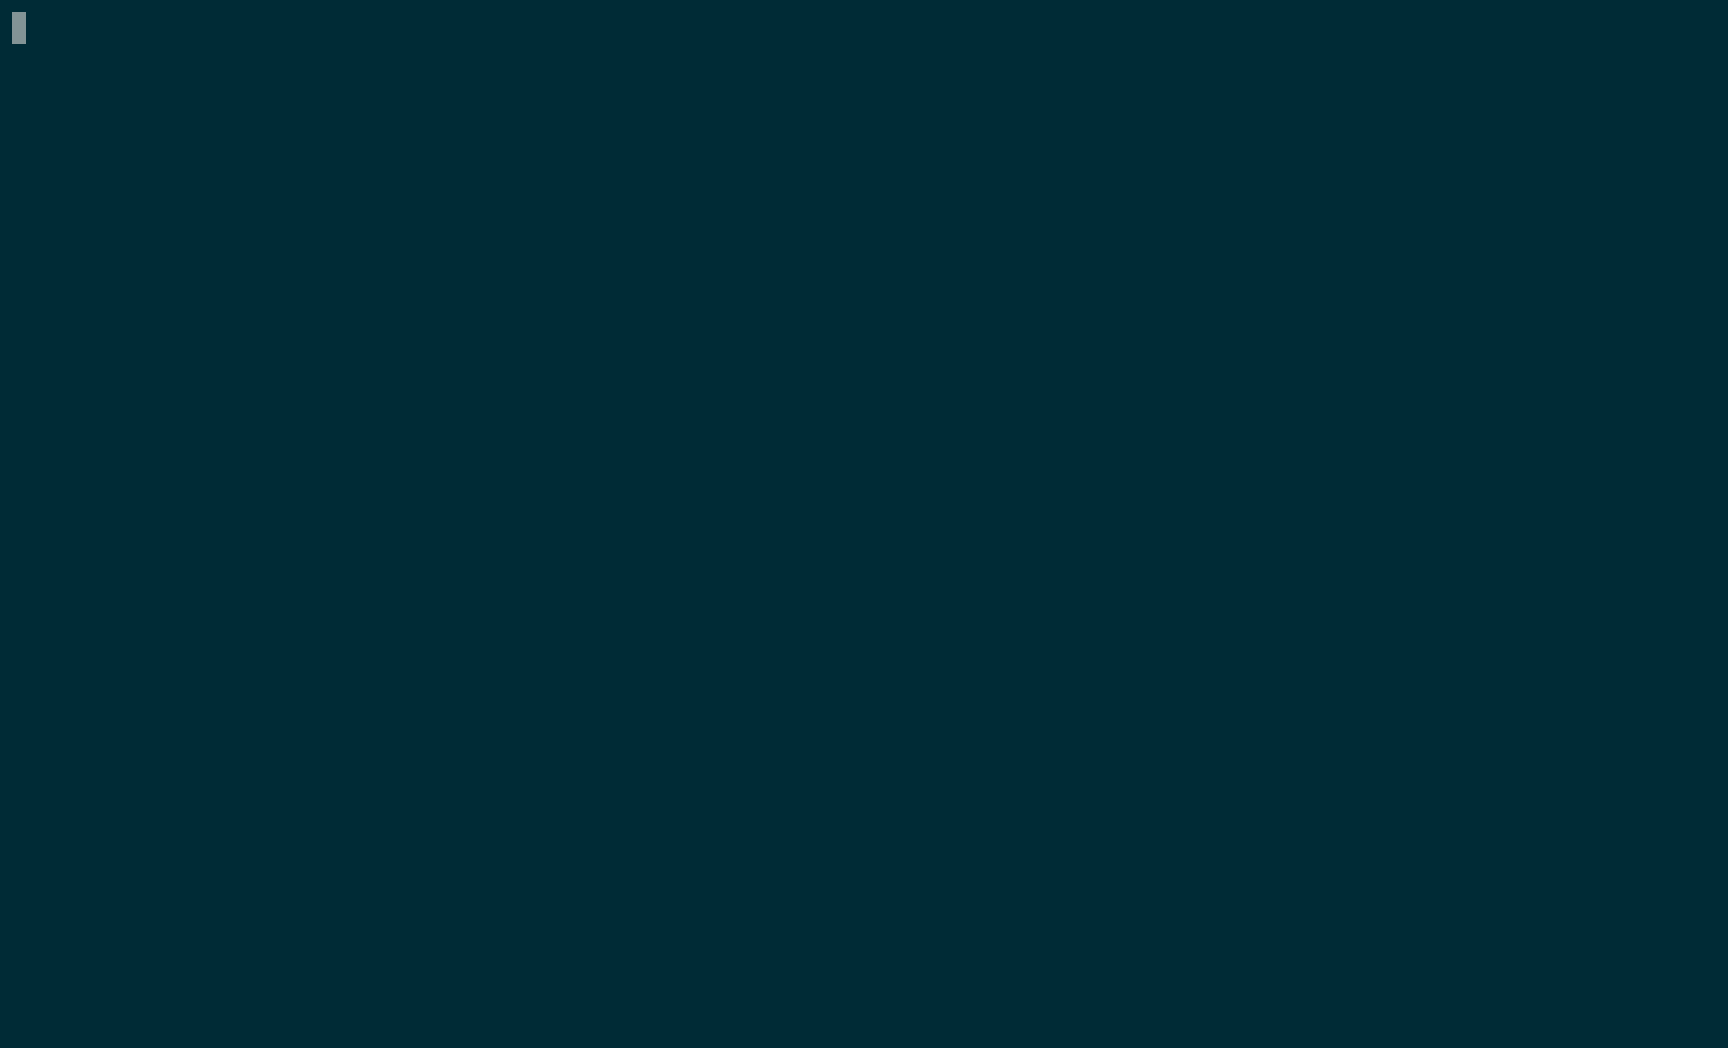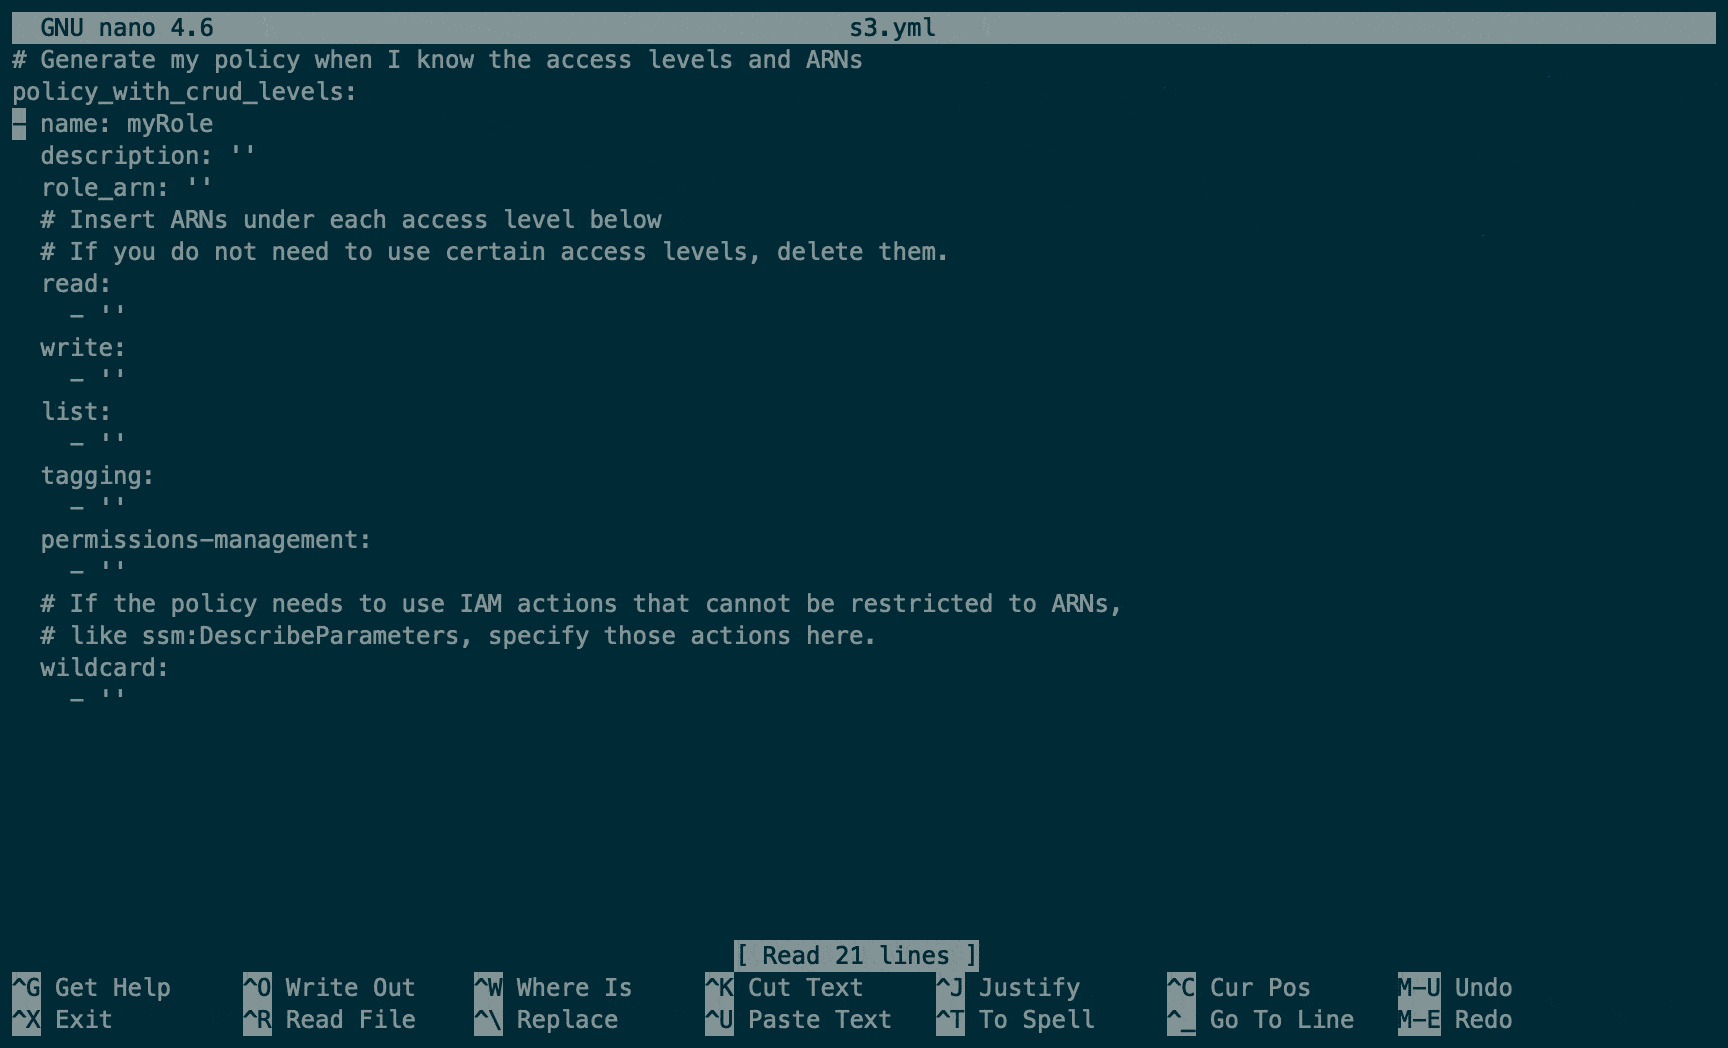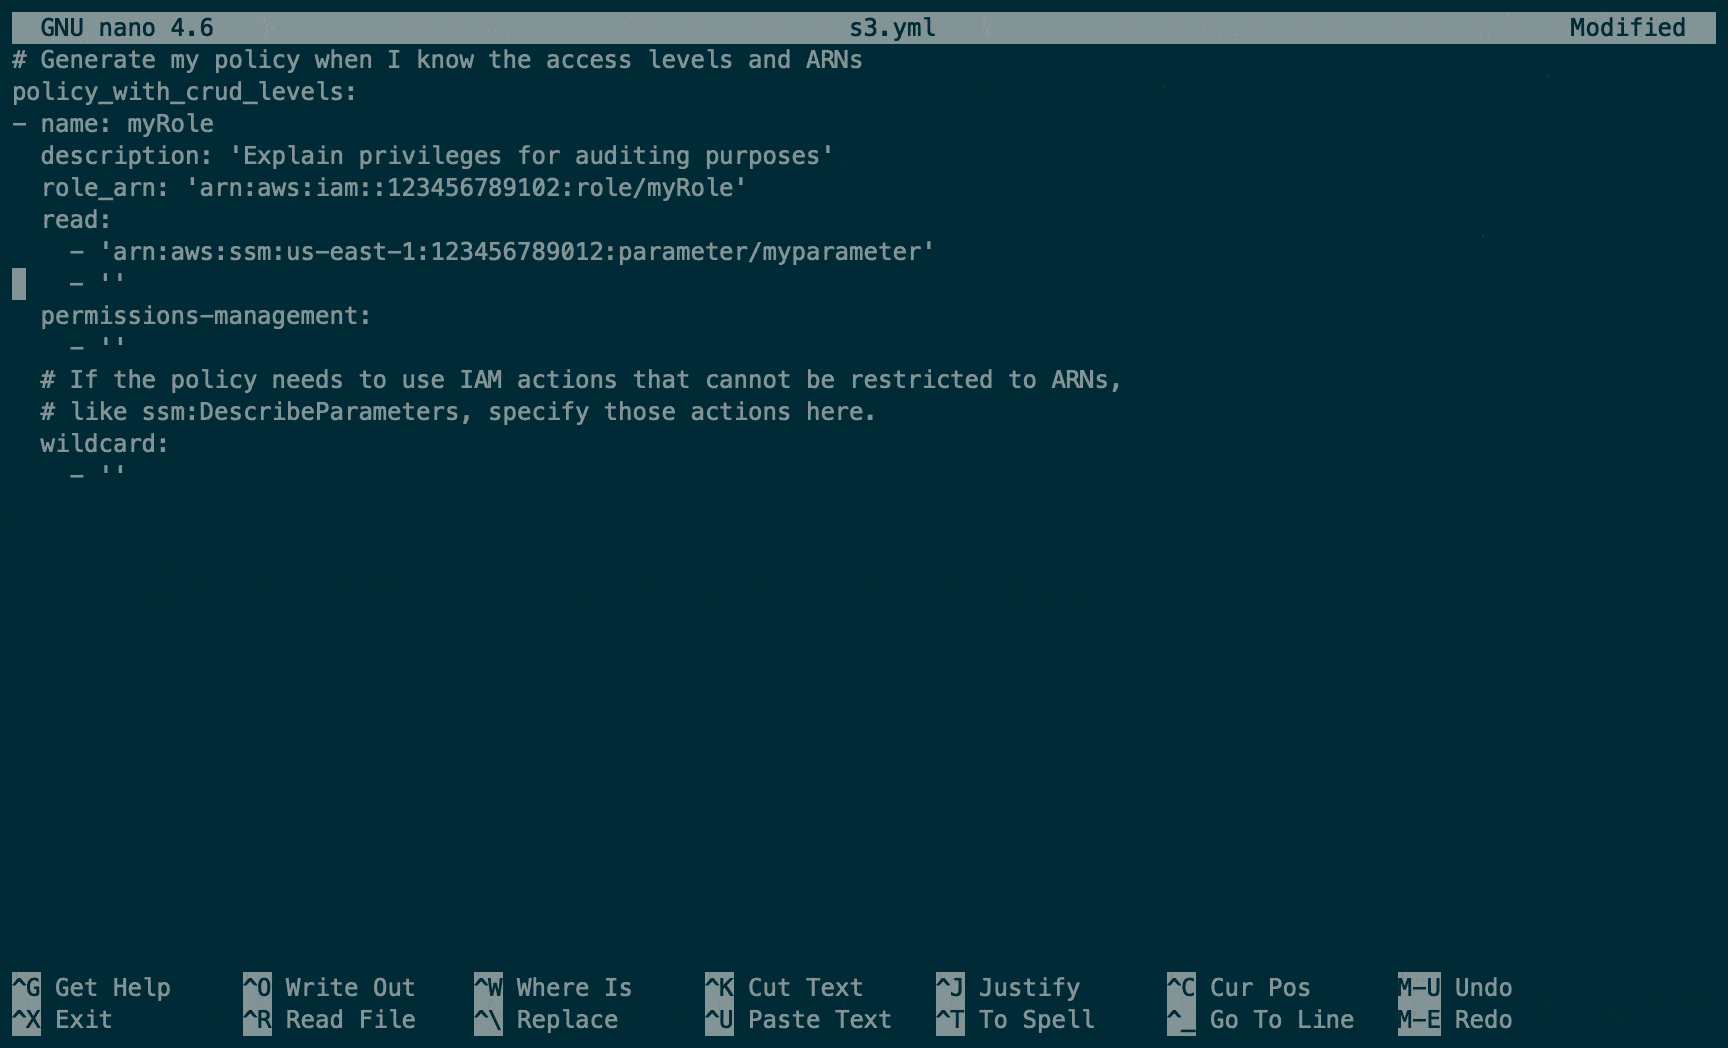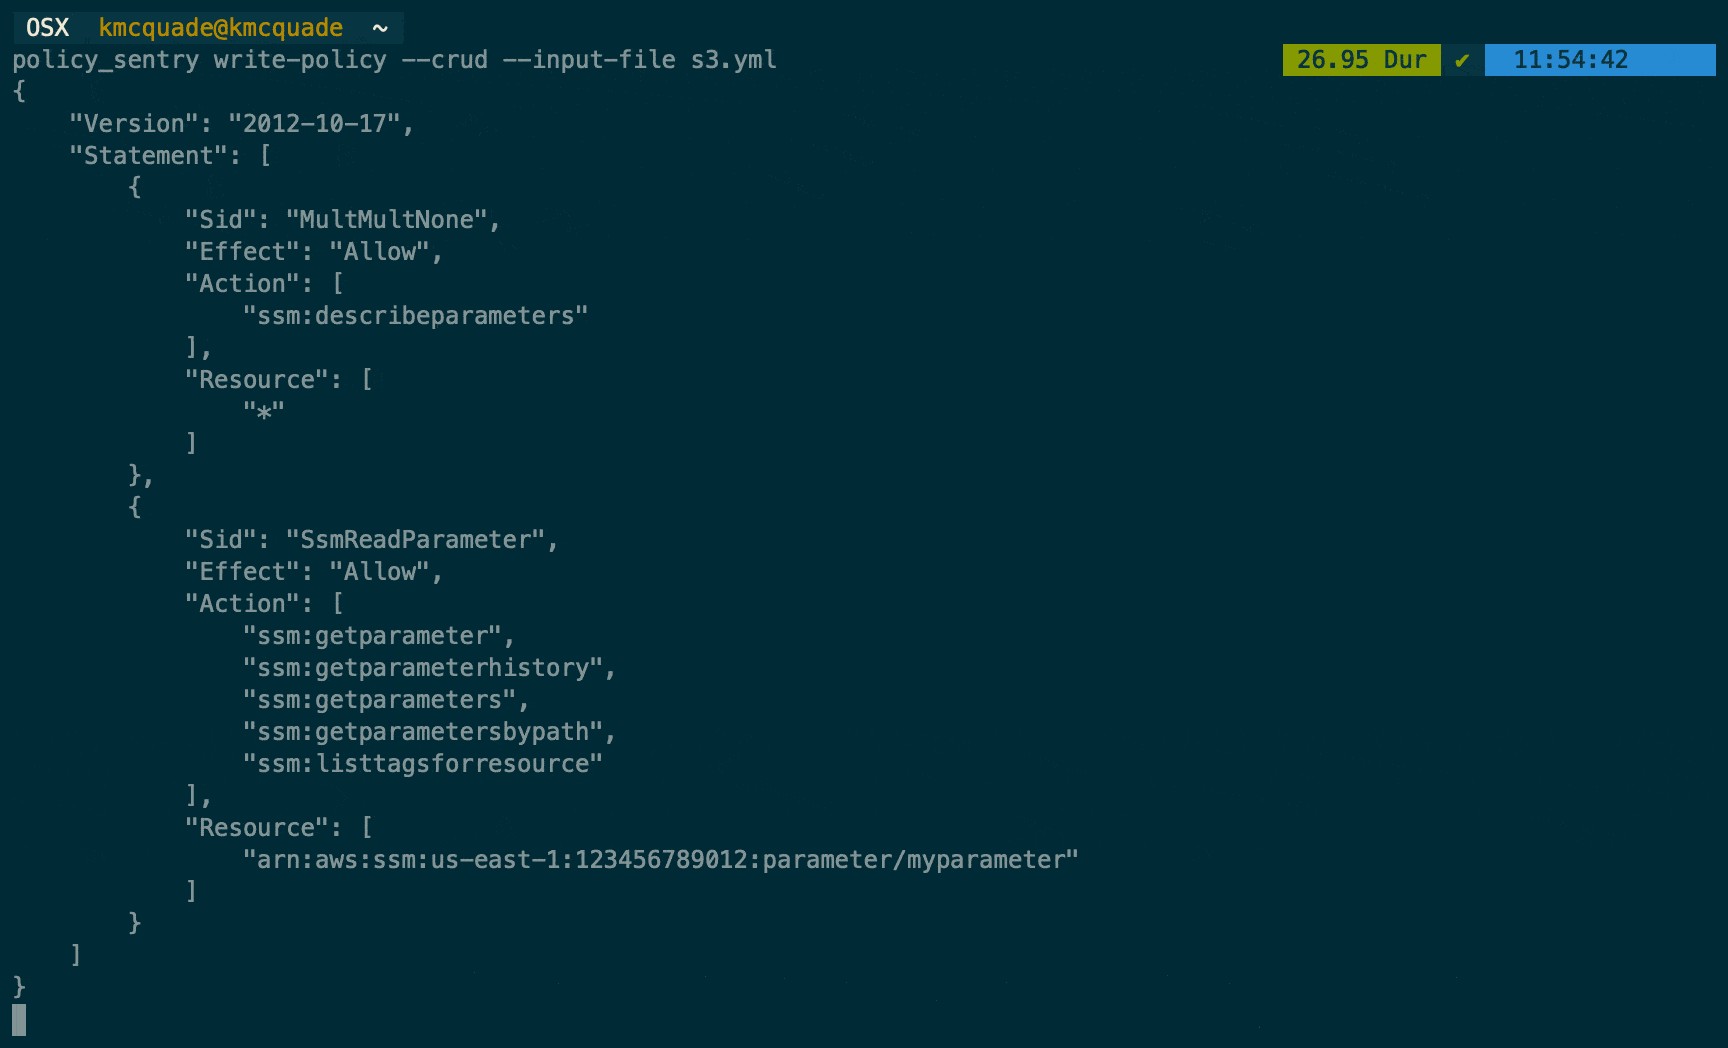 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 dev-sec/chef-ssh-hardening
This chef cookbook provides secure ssh-client and ssh-server configurations.
 dev-sec/puppet-ssh-hardening
This puppet module provides secure ssh-client and ssh-server configurations.
 omerati/almalinux-fix-cve-2026-31431
Automates kernel patching for CVE-2026-31431 and Dirty Frag, sets secure kernel as default in GRUB, and disables testing repo for production safety.