
cloudquery
Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…

Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…

Hardened, Azure-optimized Linux distribution built from Fedora sources with RPM packaging, supply chain security, and declarative configuration for…

Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

An open source, cloud-native security to protect everything from build to runtime

A tool to extract the IdP cert from vCenter backups and log in as Administrator

Python client for Batfish, a network configuration analysis tool that validates security, reliability, and compliance by modeling network behavior…

BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…

Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container

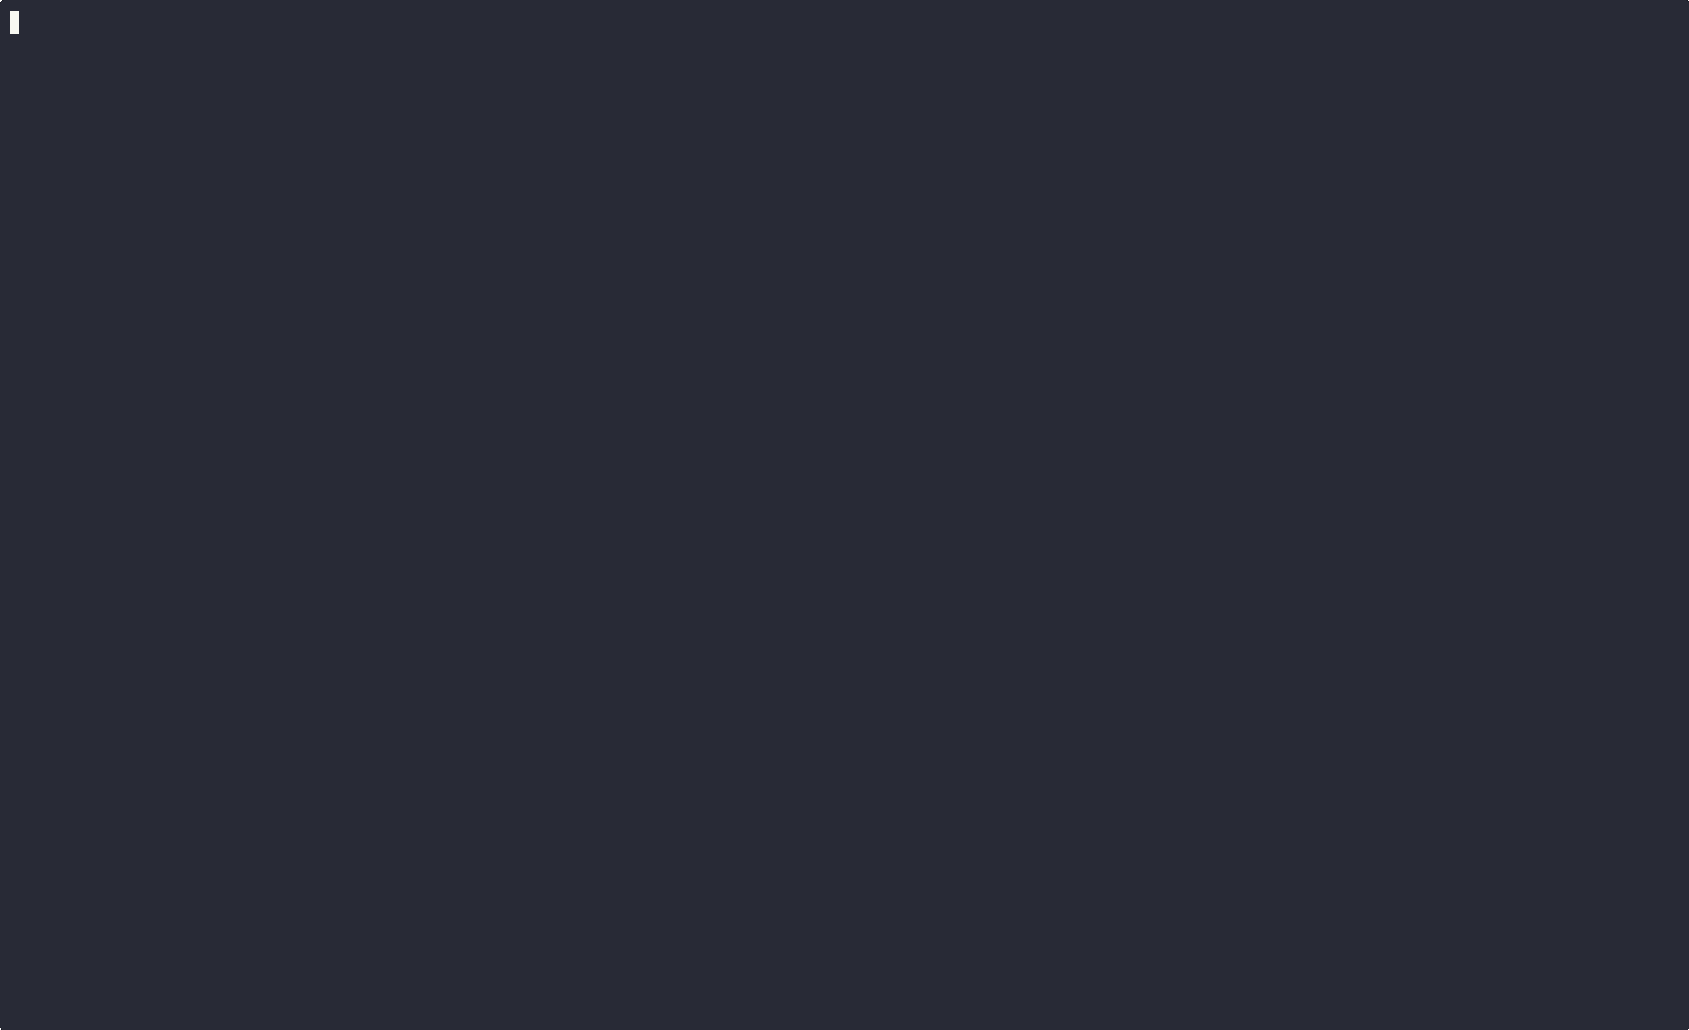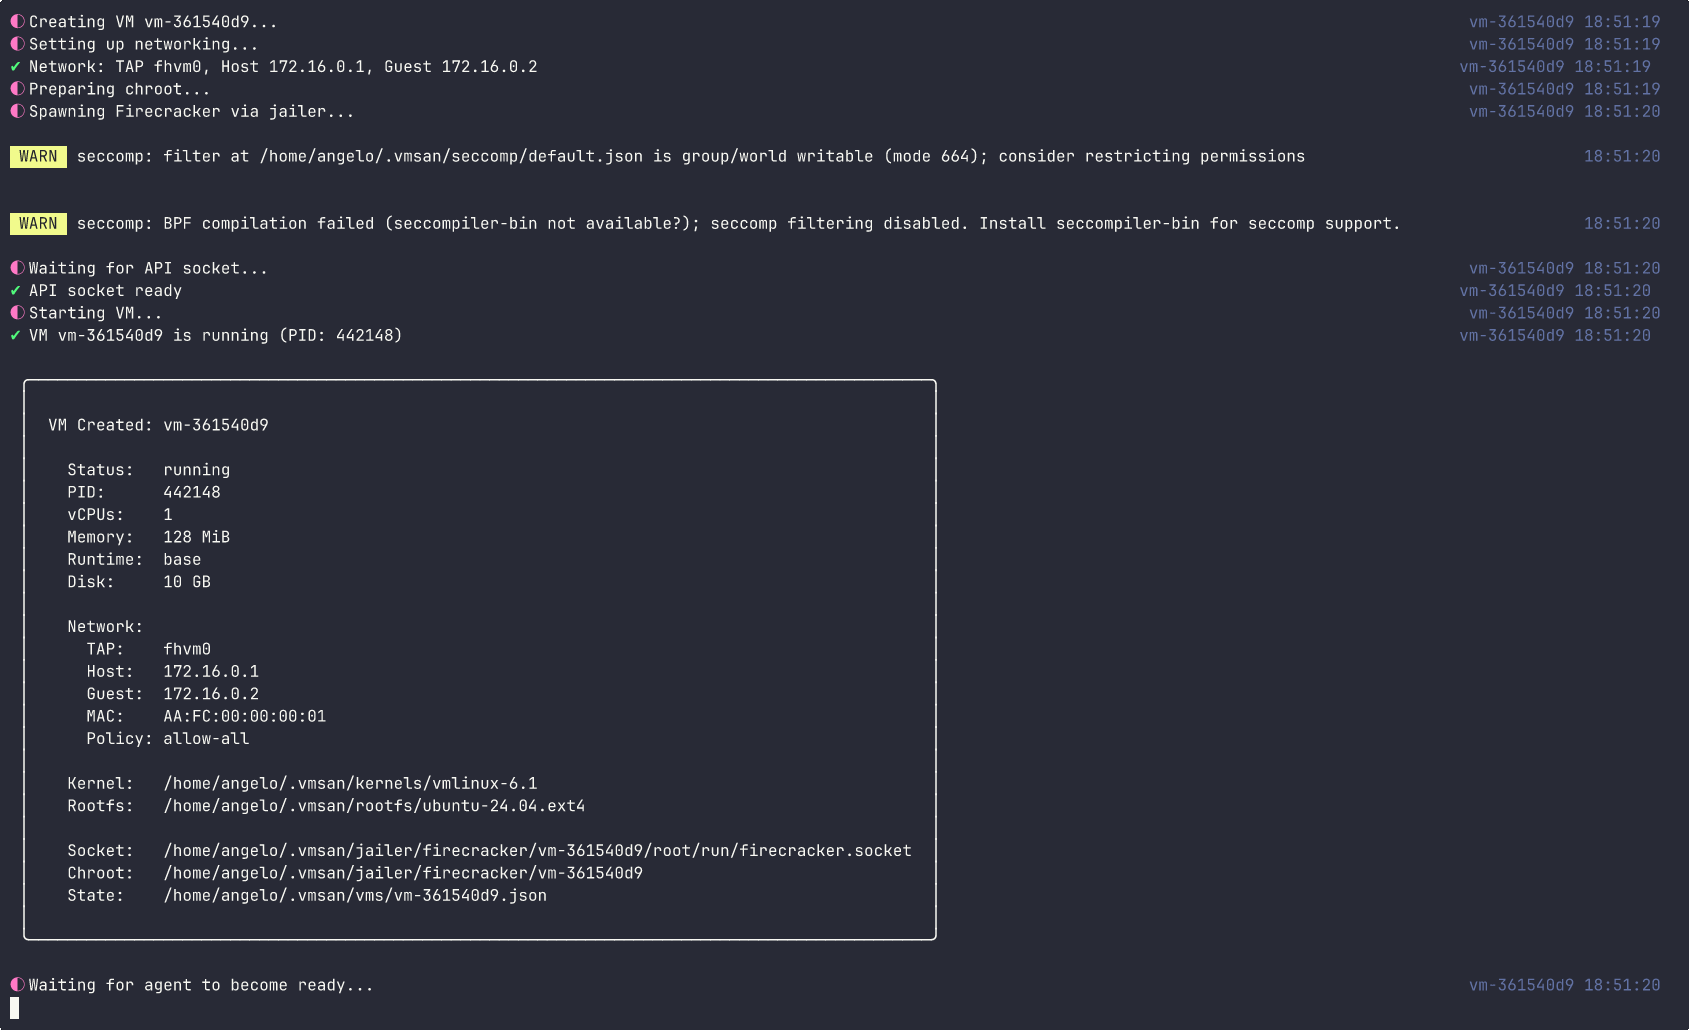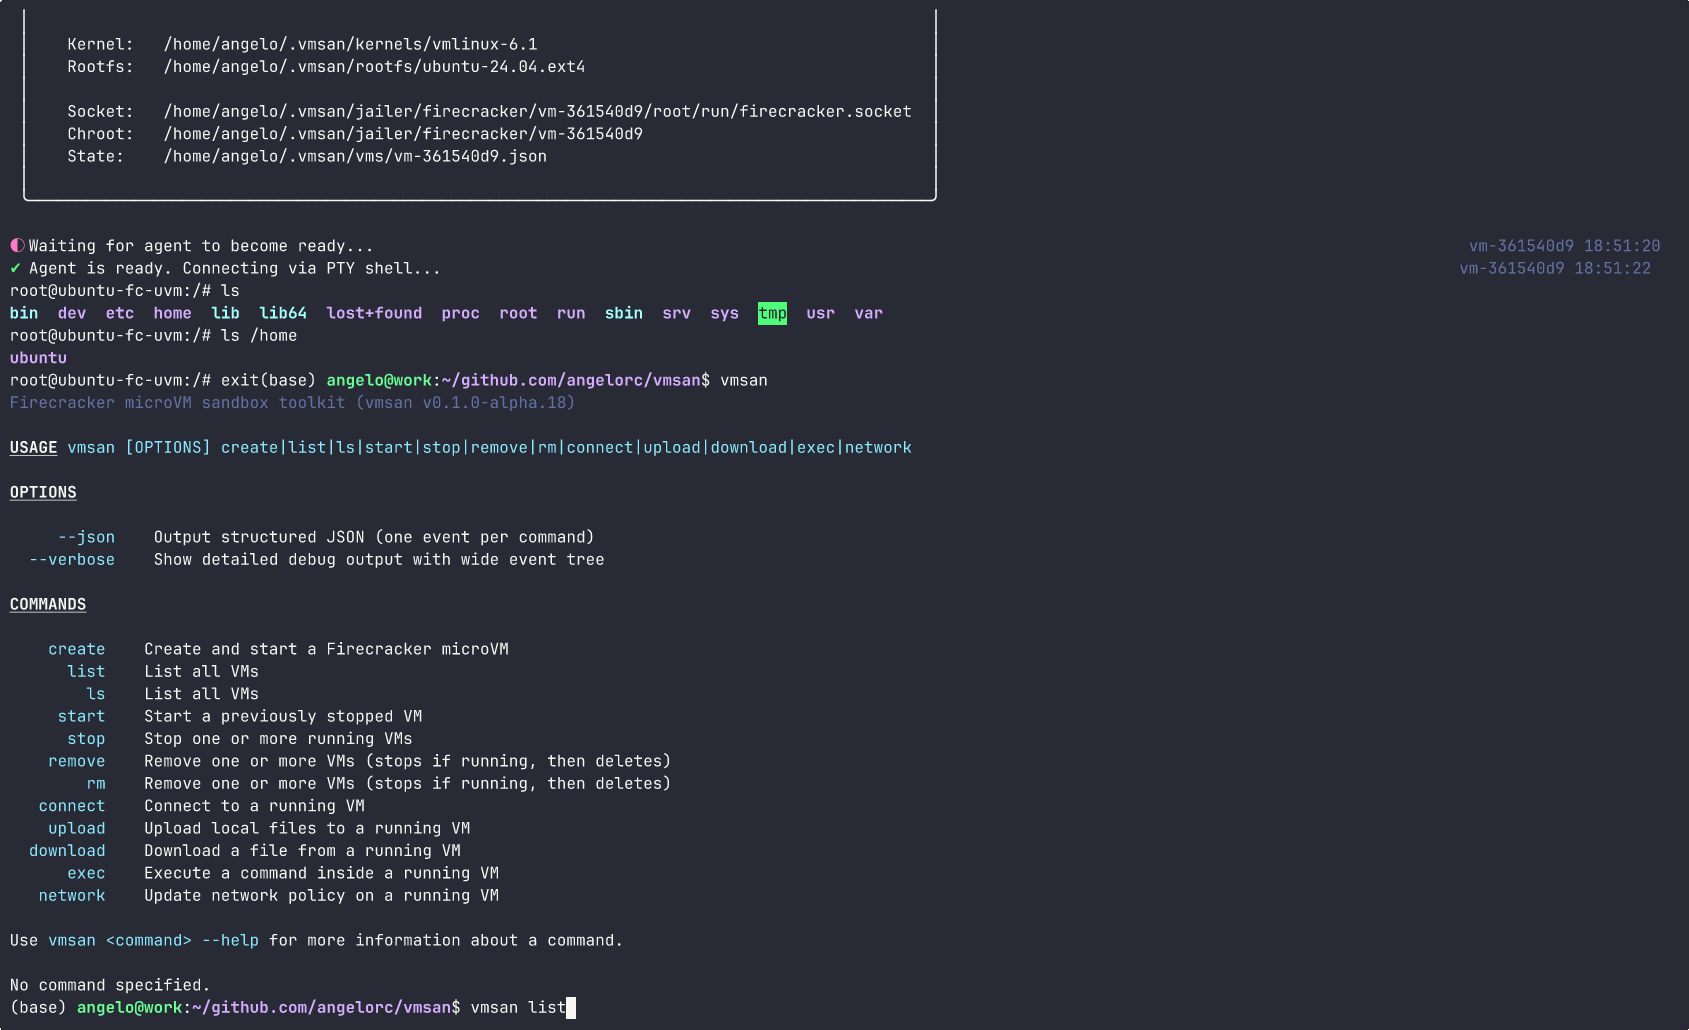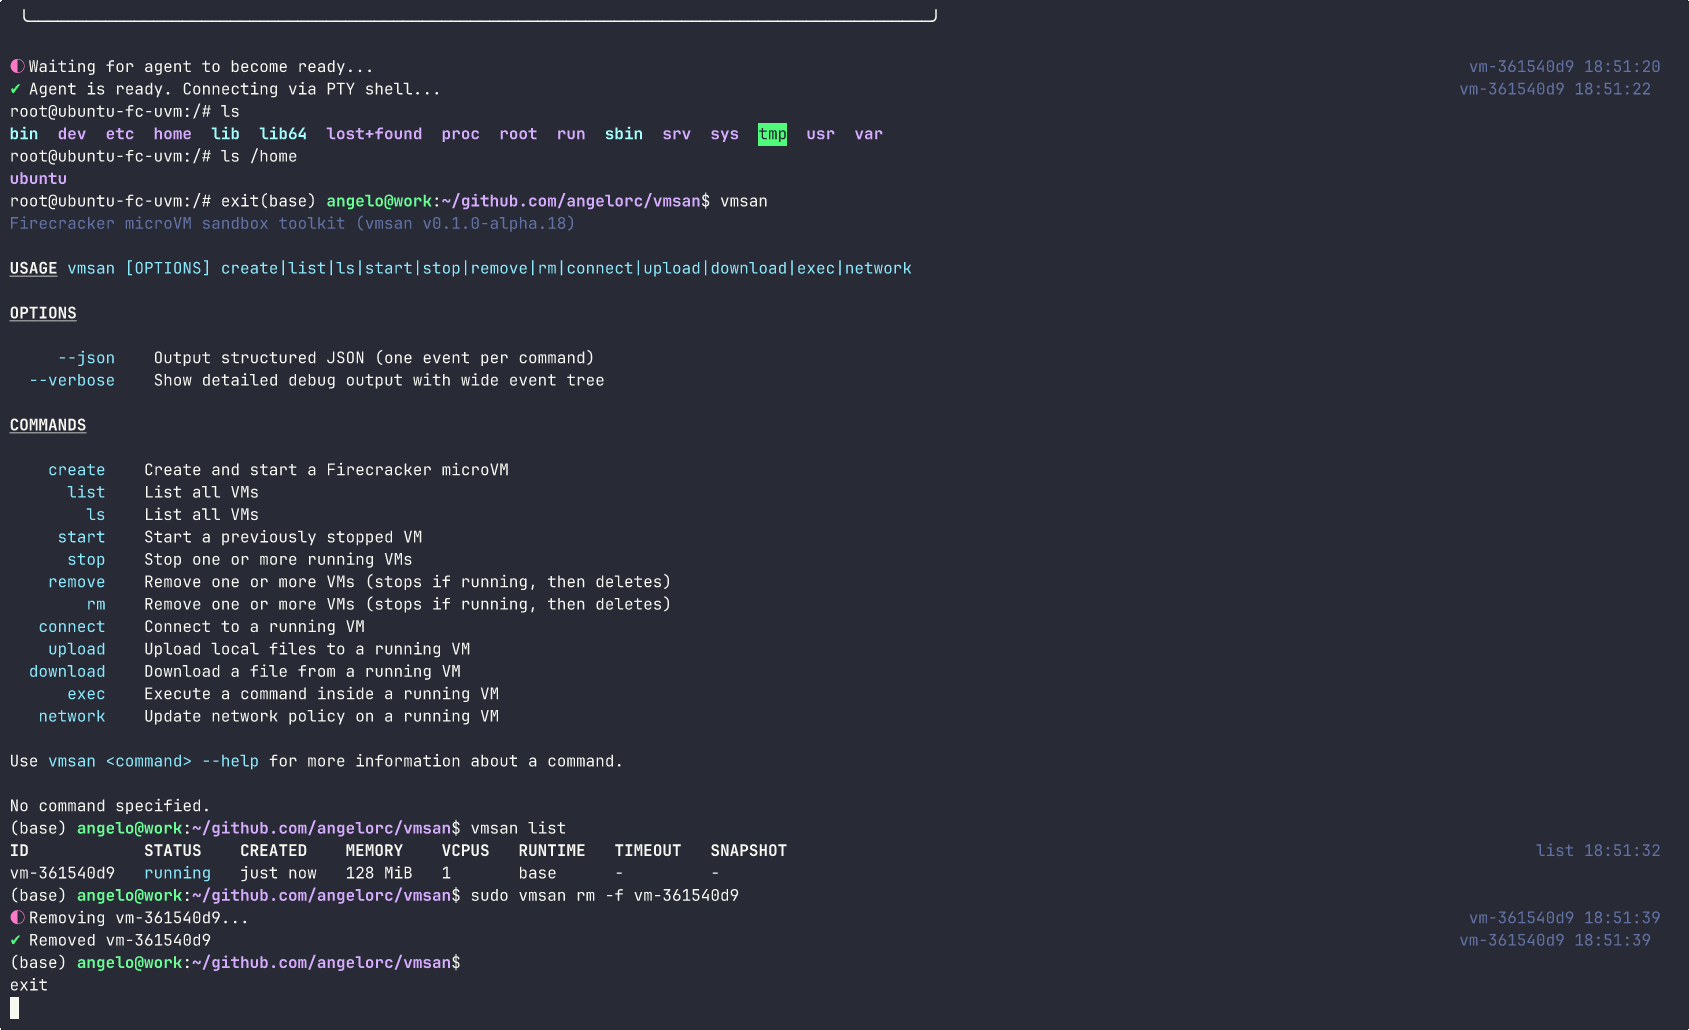
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.

Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…

🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files

A command-line interface tool for managing Azure Privileged Identity Management (PIM) role activations directly from your terminal.

Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…

OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

Extracts all S3 Buckets from CSP report headers and then tests for file upload vulns

OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.

Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…