

pacu
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
5.3k
rhinosecuritylabs/pacuThe AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 netspi/microburst
A collection of scripts for assessing Microsoft Azure security
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 dagrz/aws_pwn
A collection of AWS penetration testing junk
 nccgroup/pmapper
A tool for quickly evaluating IAM permissions in AWS.
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
 rams3sh/aaia
AWS Identity and Access Management Visualizer and Anomaly Finder
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
 devzero-security/redstackpro
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…
 tenable/escalategpt
An AI-powered tool for discovering privilege escalation opportunities in AWS IAM configurations.
 gen0cide/laforge
Competition Infrastructure Management
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 rhinosecuritylabs/iamactionhunter
An AWS IAM policy statement parser and query tool.
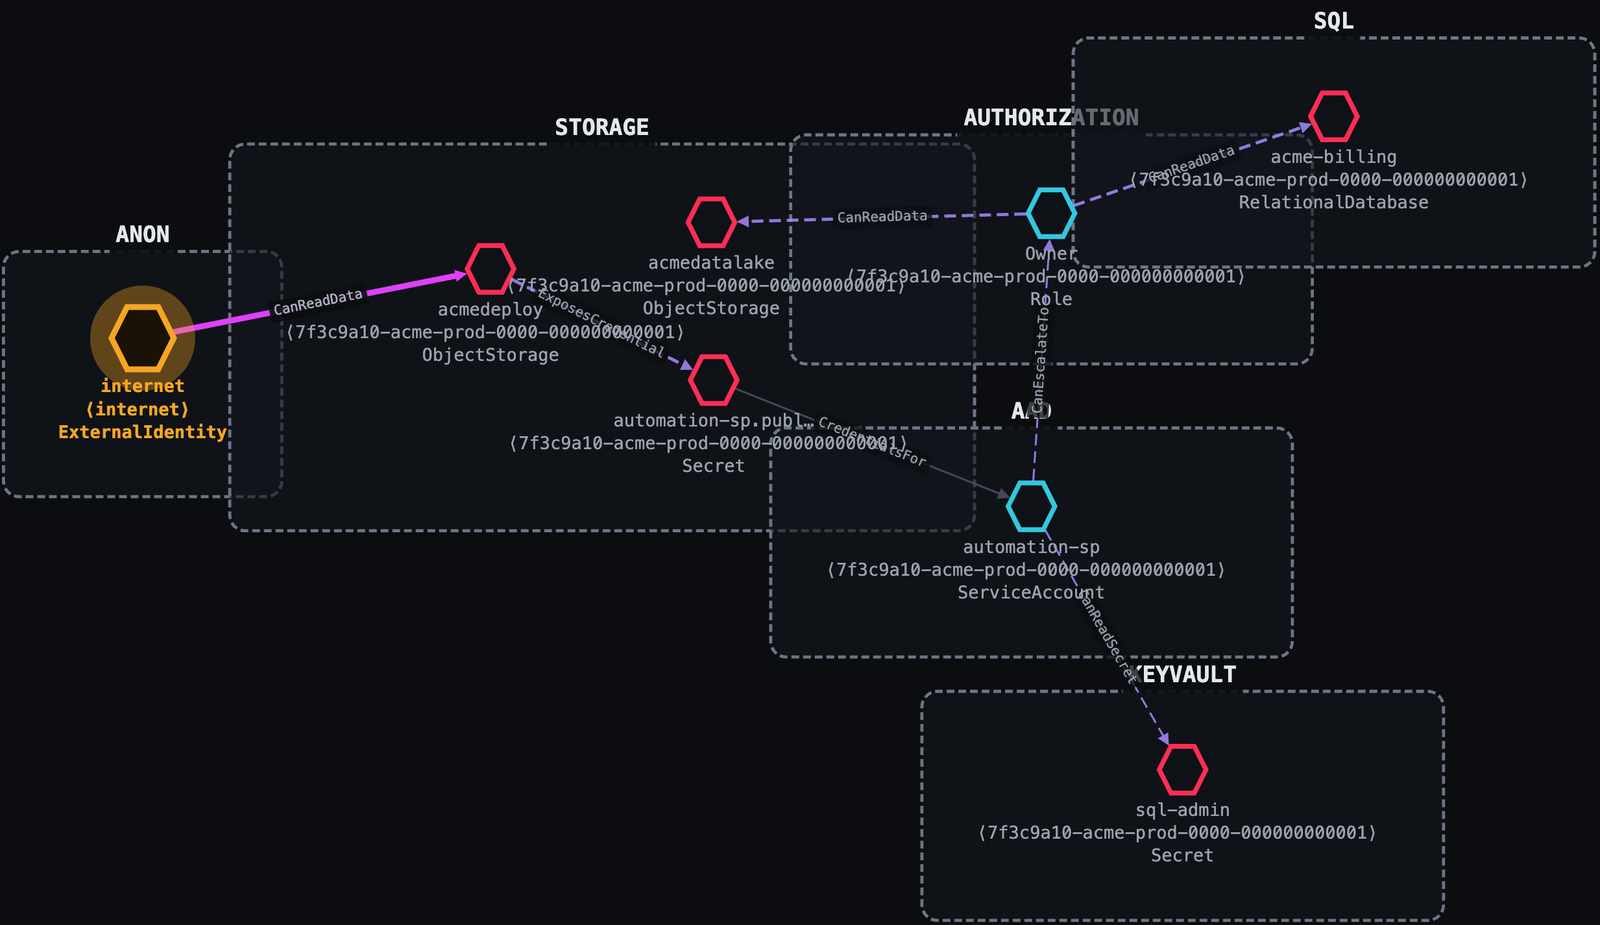 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
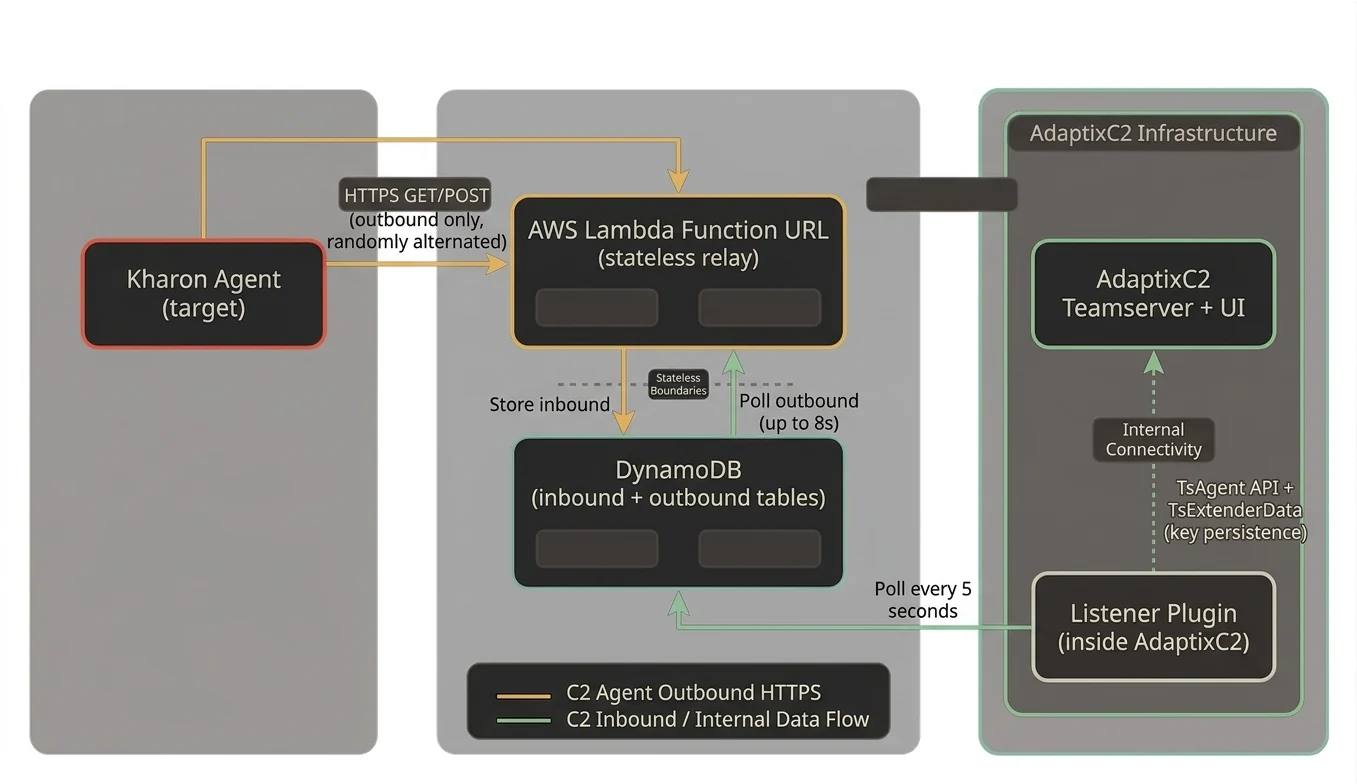 stillbigjosh/adaptix-serverless-c2
Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
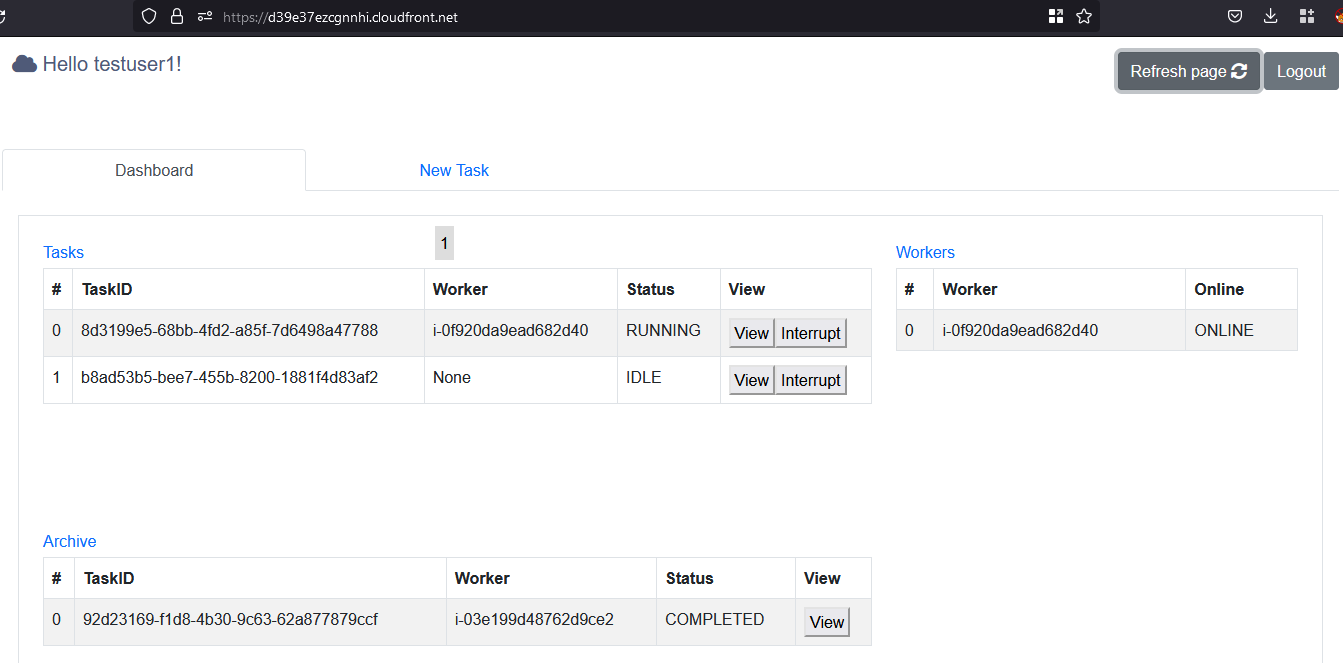 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…