Cowrie and Grafana Honeypot using Terraform on DigitalOcean

Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…

Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

Write tests against structured configuration data using the Open Policy Agent Rego query language

🛡️ 🔒 This project's goal is to be simple to create and destroy your own VPN service using WireGuard.

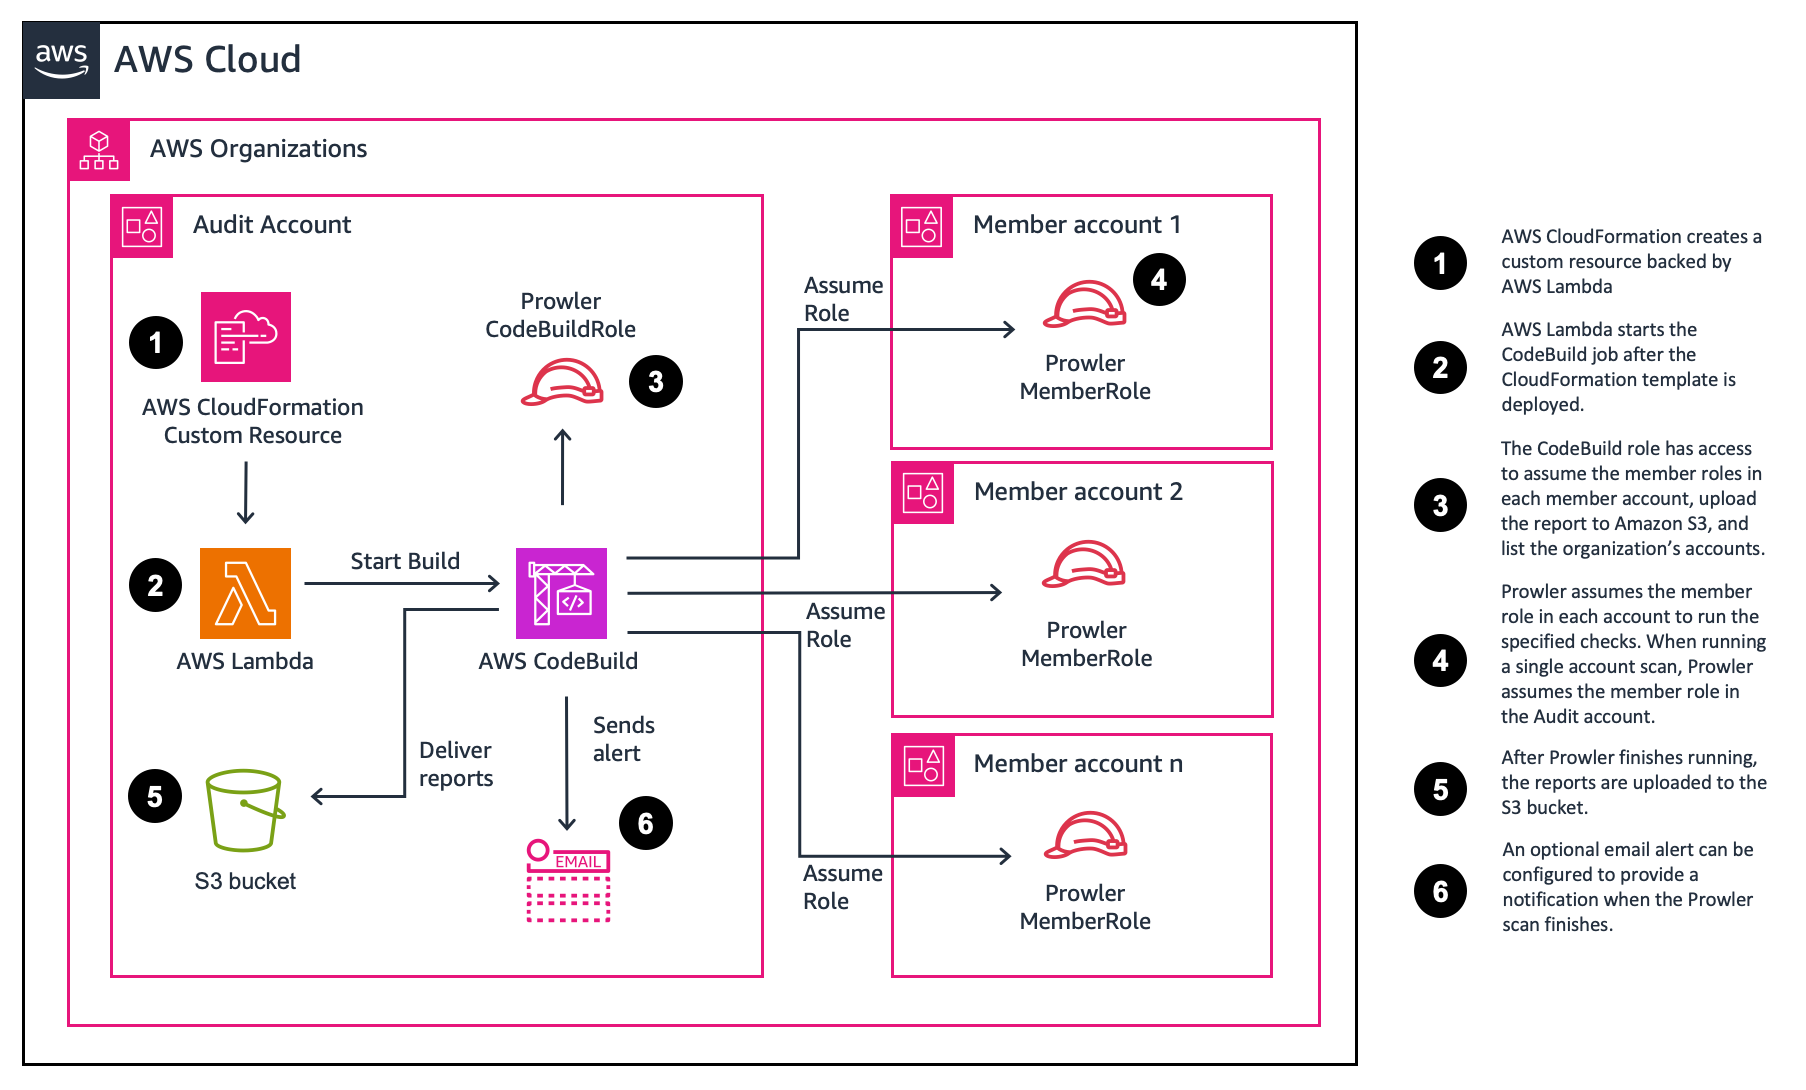
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.

Cloud-native Kubernetes cluster inspection tool that detects application misconfigurations, unhealthy components, and node problems using custom OPA,…

Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and…

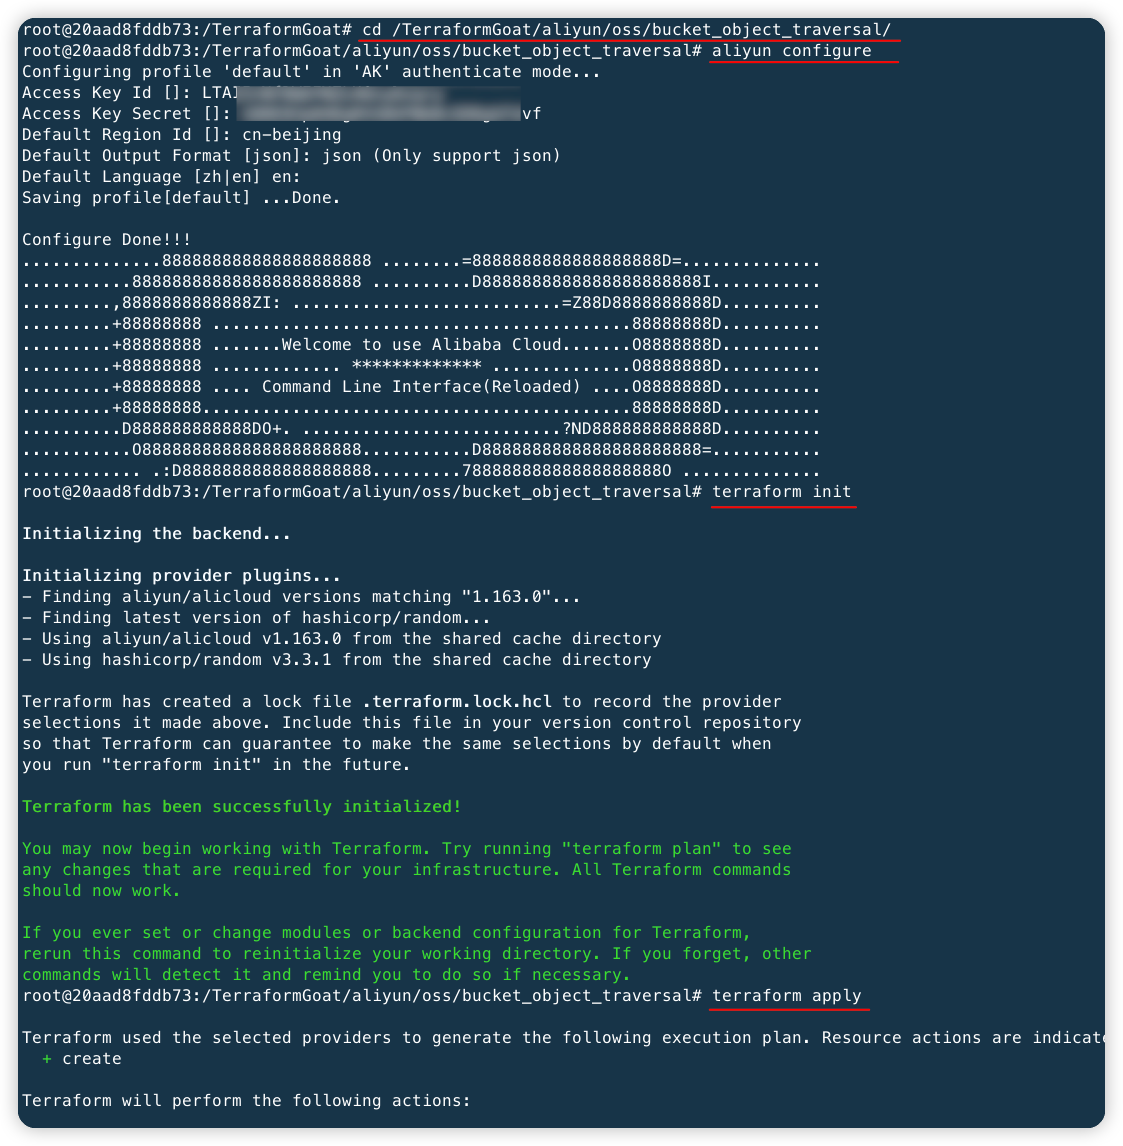
Multi-cloud vulnerable-by-design deployment tool using Terraform to provision intentionally insecure cloud infrastructure for security training and…

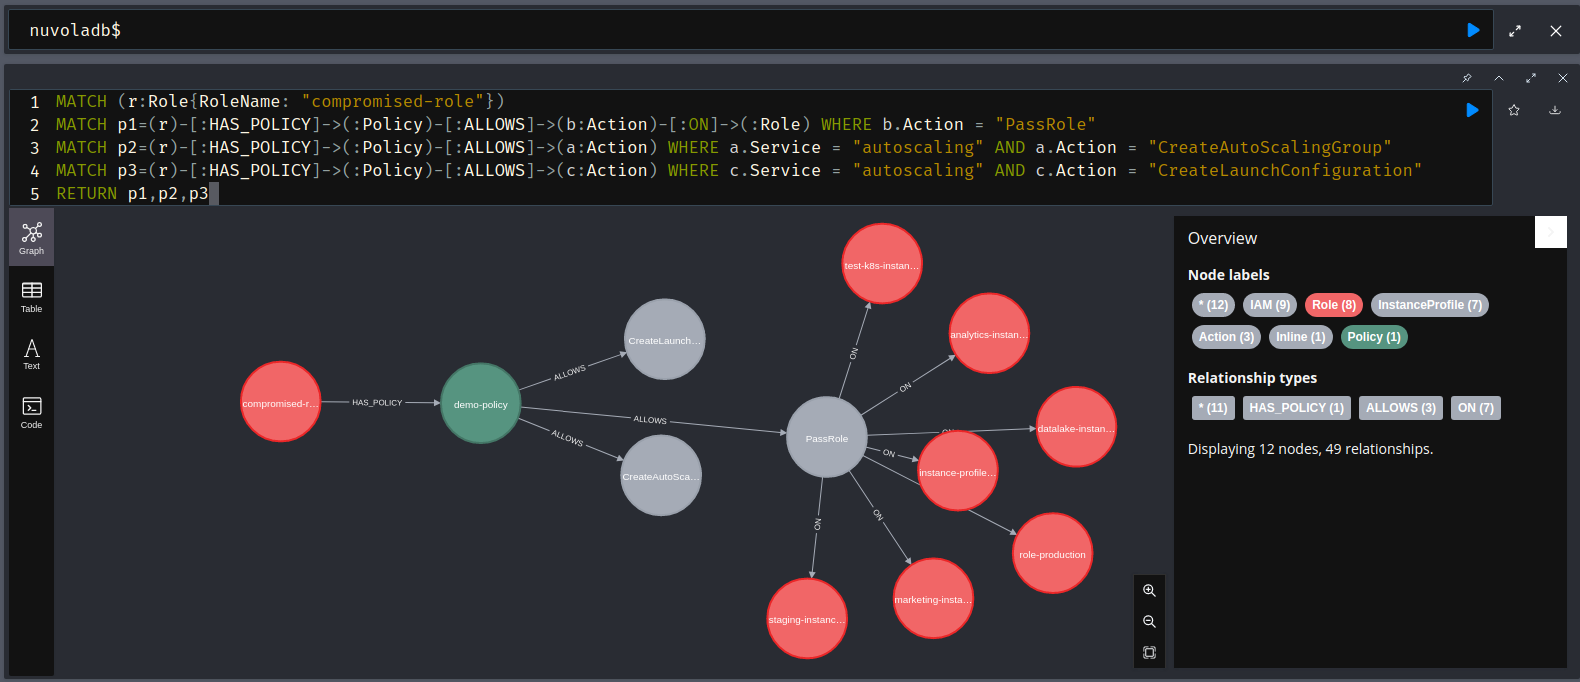
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…

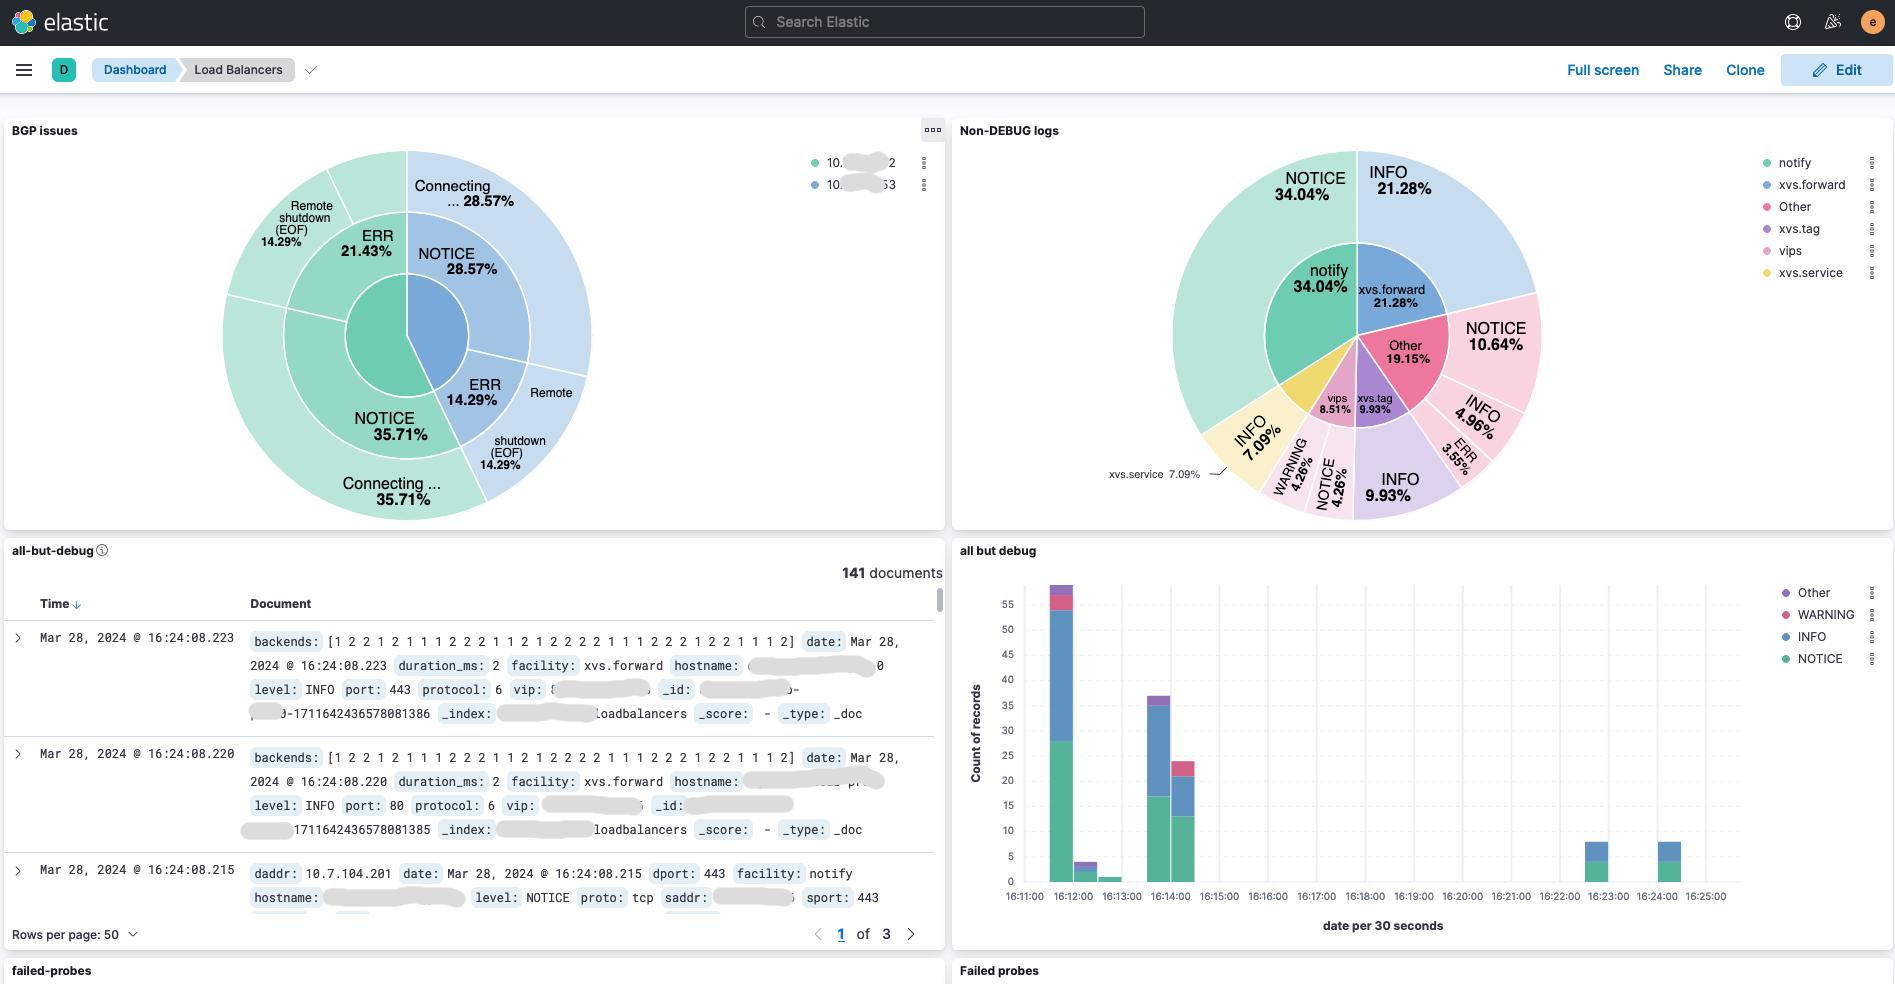
A horizontally scalable Direct Server Return layer 4 load balancer for Linux using XDP/eBPF

Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…

Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.

Automatically deploying Mythic C2 in Azure using Terraform

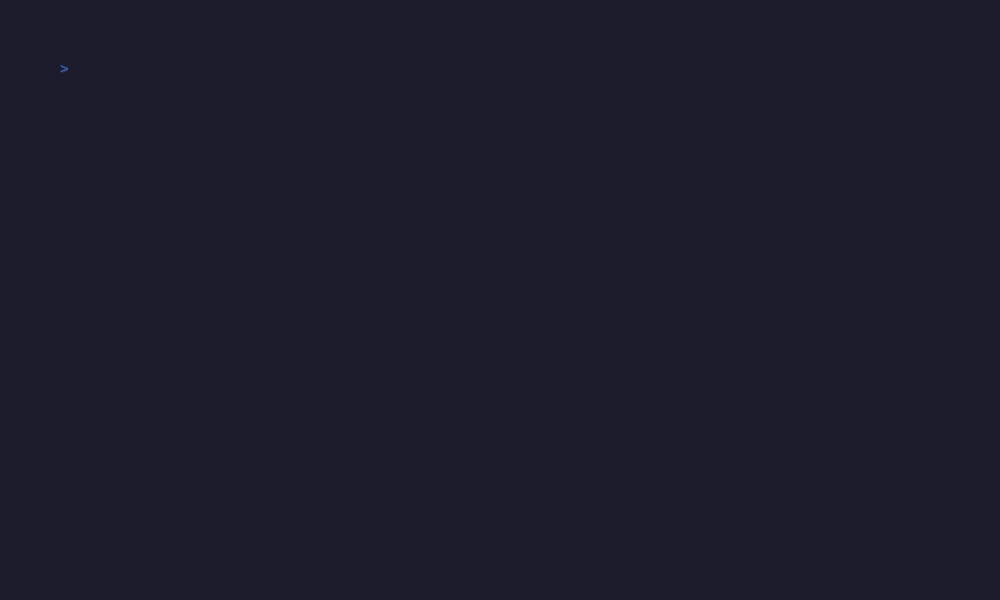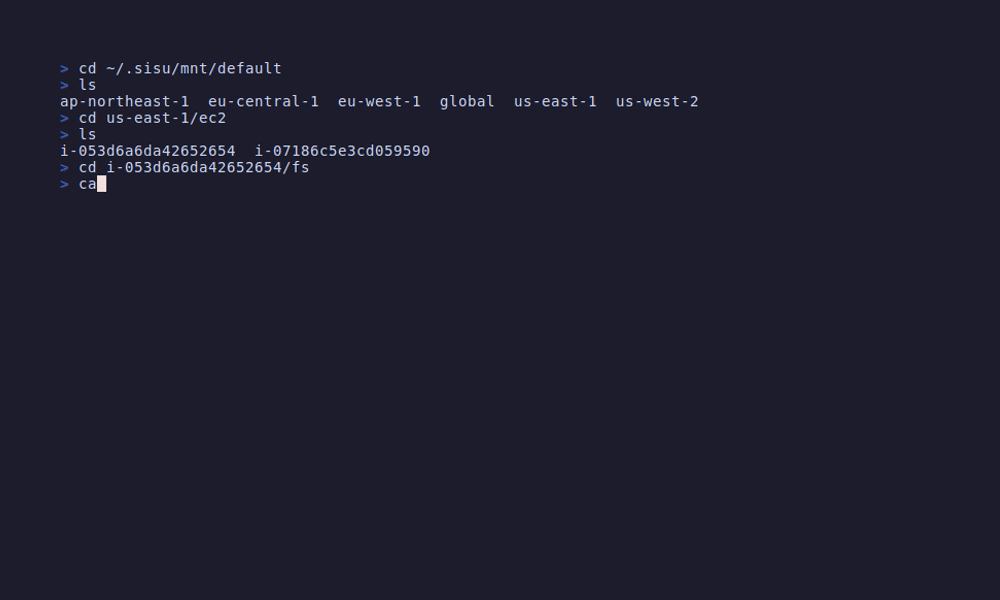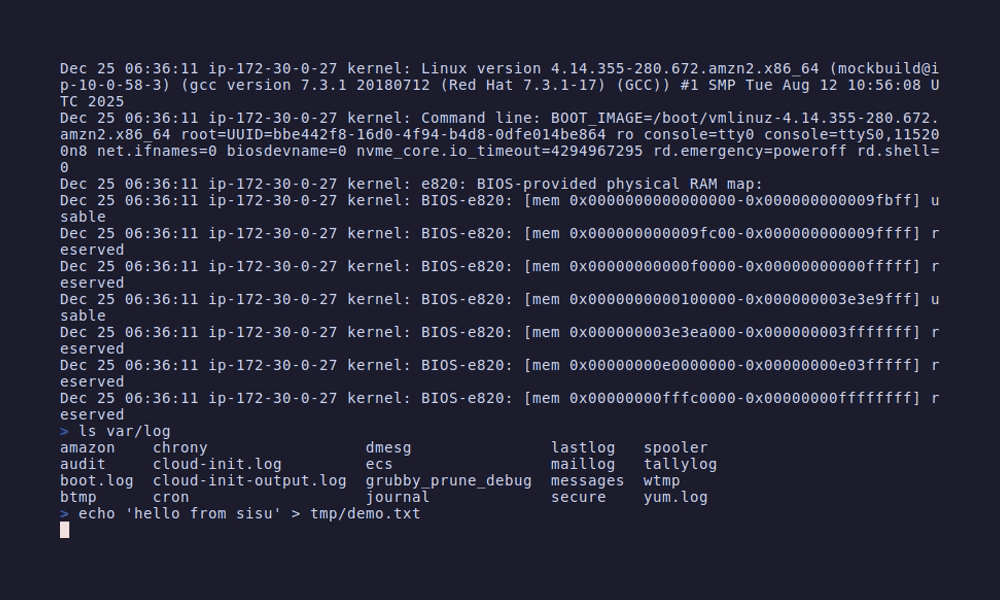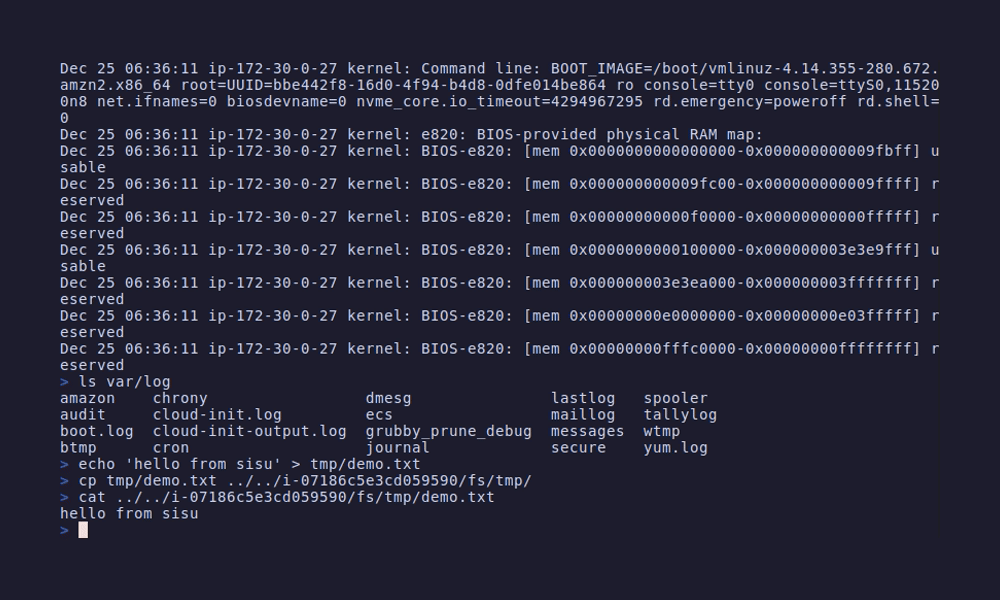
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…

Docker projects to retain beacon source IPs using C2 relaying infra

Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction

Vulnerability Exploitation using tools Penetration Testing, Grafana, Docker, Kali Linux.

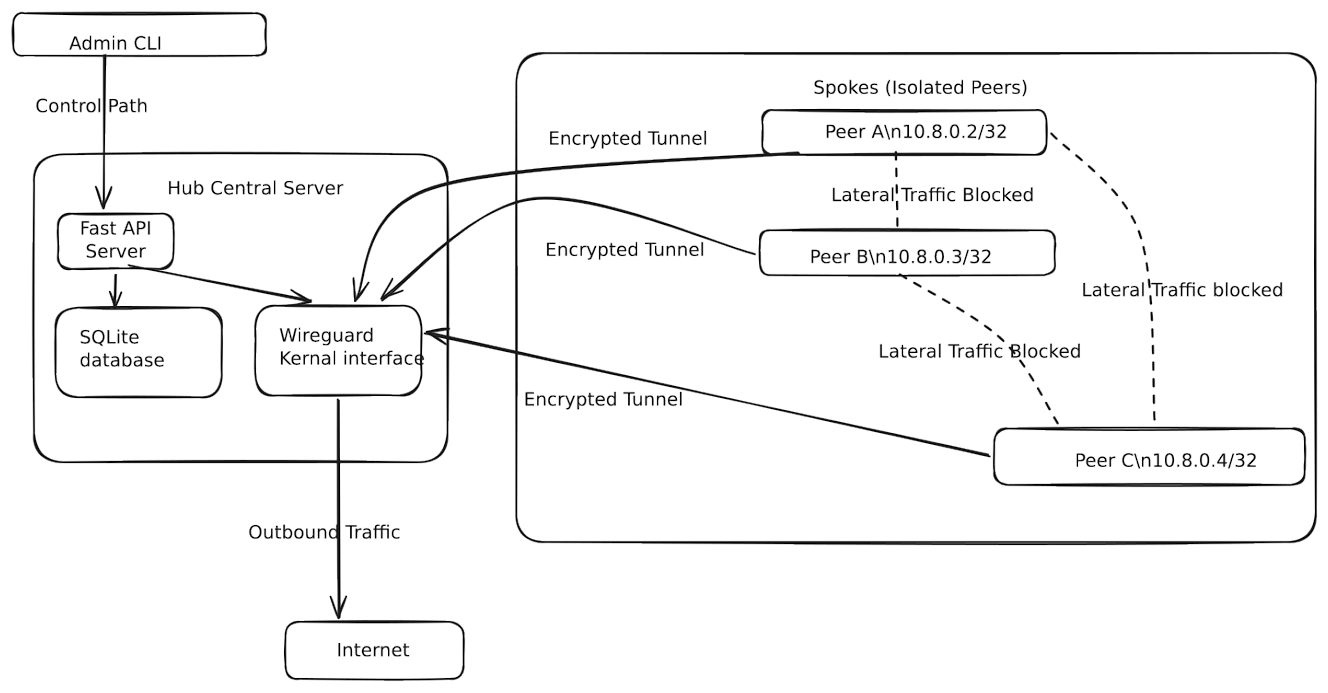
A lightweight, policy-driven framework that brings Zero-Trust micro-segmentation to SOHO networks using WireGuard.