

poro
 9rnt/poro
Scan publicly accessible assets on your AWS cloud environment
cloud-infrastructure-securitycloud-securitymisconfiguration+1
9rnt/poroScan publicly accessible assets on your AWS cloud environment
 wearecloudar/s3-account-search
S3 Account Search
 shanika04/cloudfoundry_uaa
CVE-2016-4468
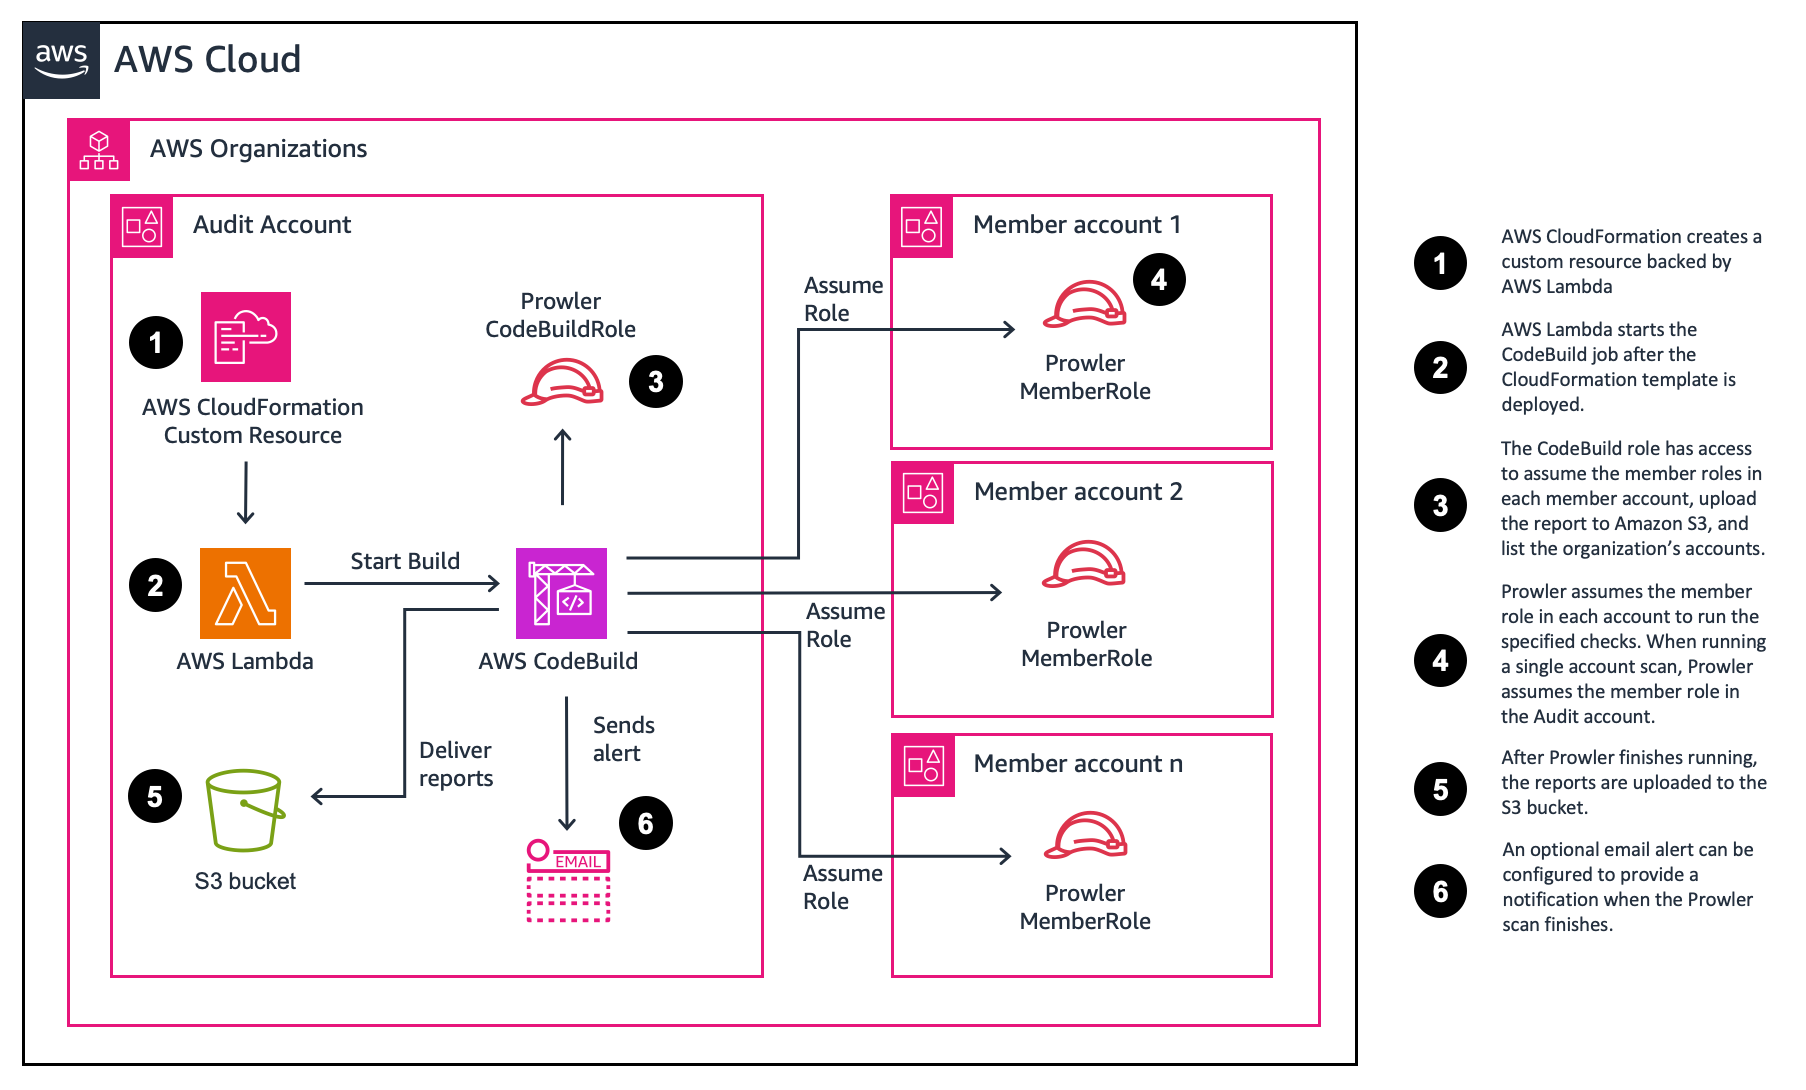 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
 tuladhar/ingress-nightmare
IngressNightmare (CVE-2025-1974)
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
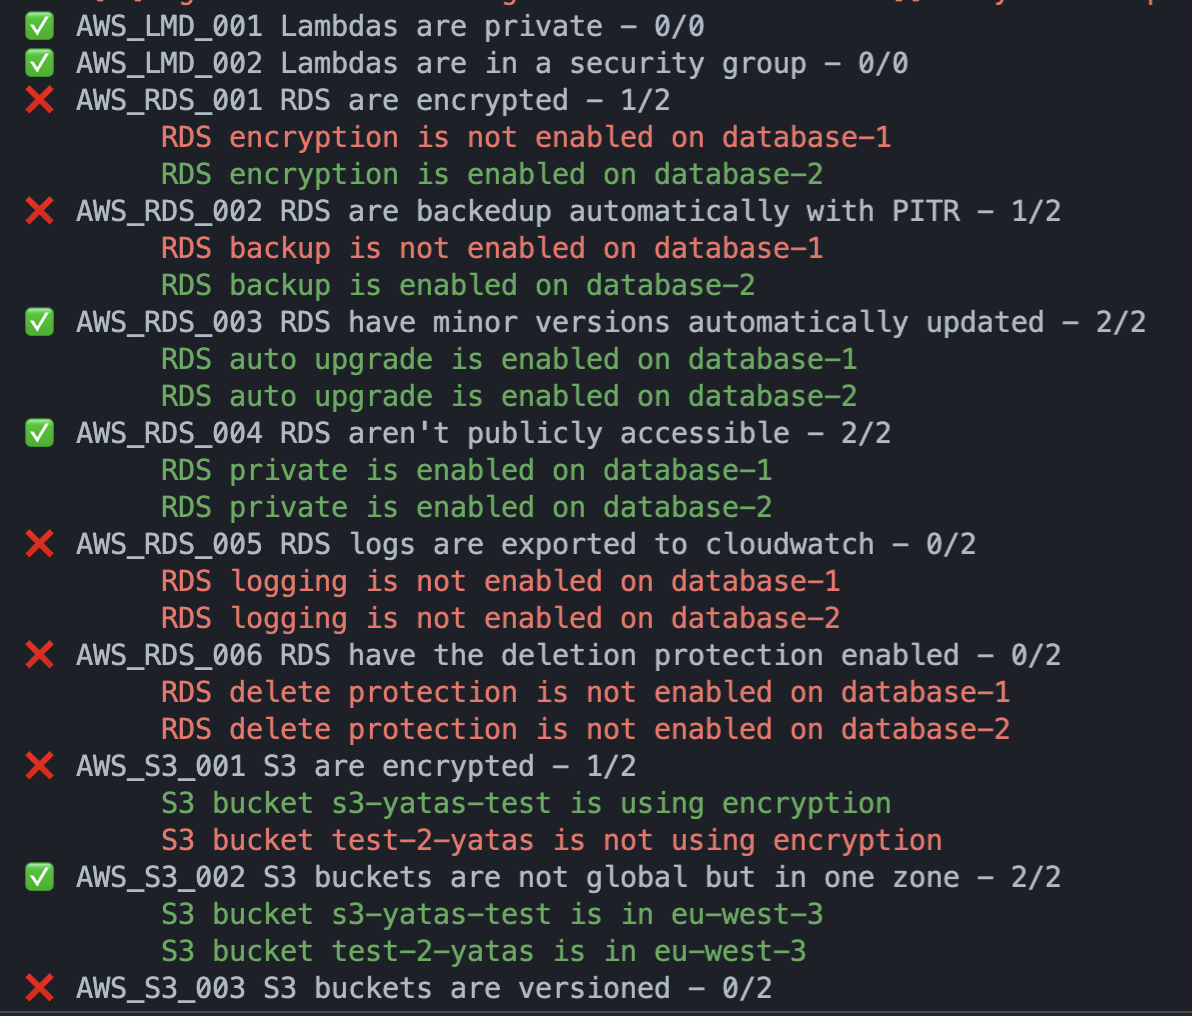 padok-team/yatas
:owl::mag_right: A simple tool to audit your AWS/GCP infrastructure for misconfiguration or potential security issues with plugins integration
 aker-gateway/aker
SSH bastion/jump host/jumpserver
 chaosblade-io/chaosblade
An easy to use and powerful chaos engineering experiment toolkit.(阿里巴巴开源的一款简单易用、功能强大的混沌实验注入工具)
 puppetlabs-toy-chest/puppetlabs-cve20113872
Puppet Module to help fix and migrate a Puppet deployment (CVE-2011-3872)
 andresriancho/nimbostratus-target
This repository holds a target infrastructure you can use for running the nimbostratus tools.
 chaostoolkit/chaostoolkit-kubernetes
Kubernetes driver extension of the Chaos Toolkit probes and actions API
 powerfulseal/powerfulseal
A powerful testing tool for Kubernetes clusters.
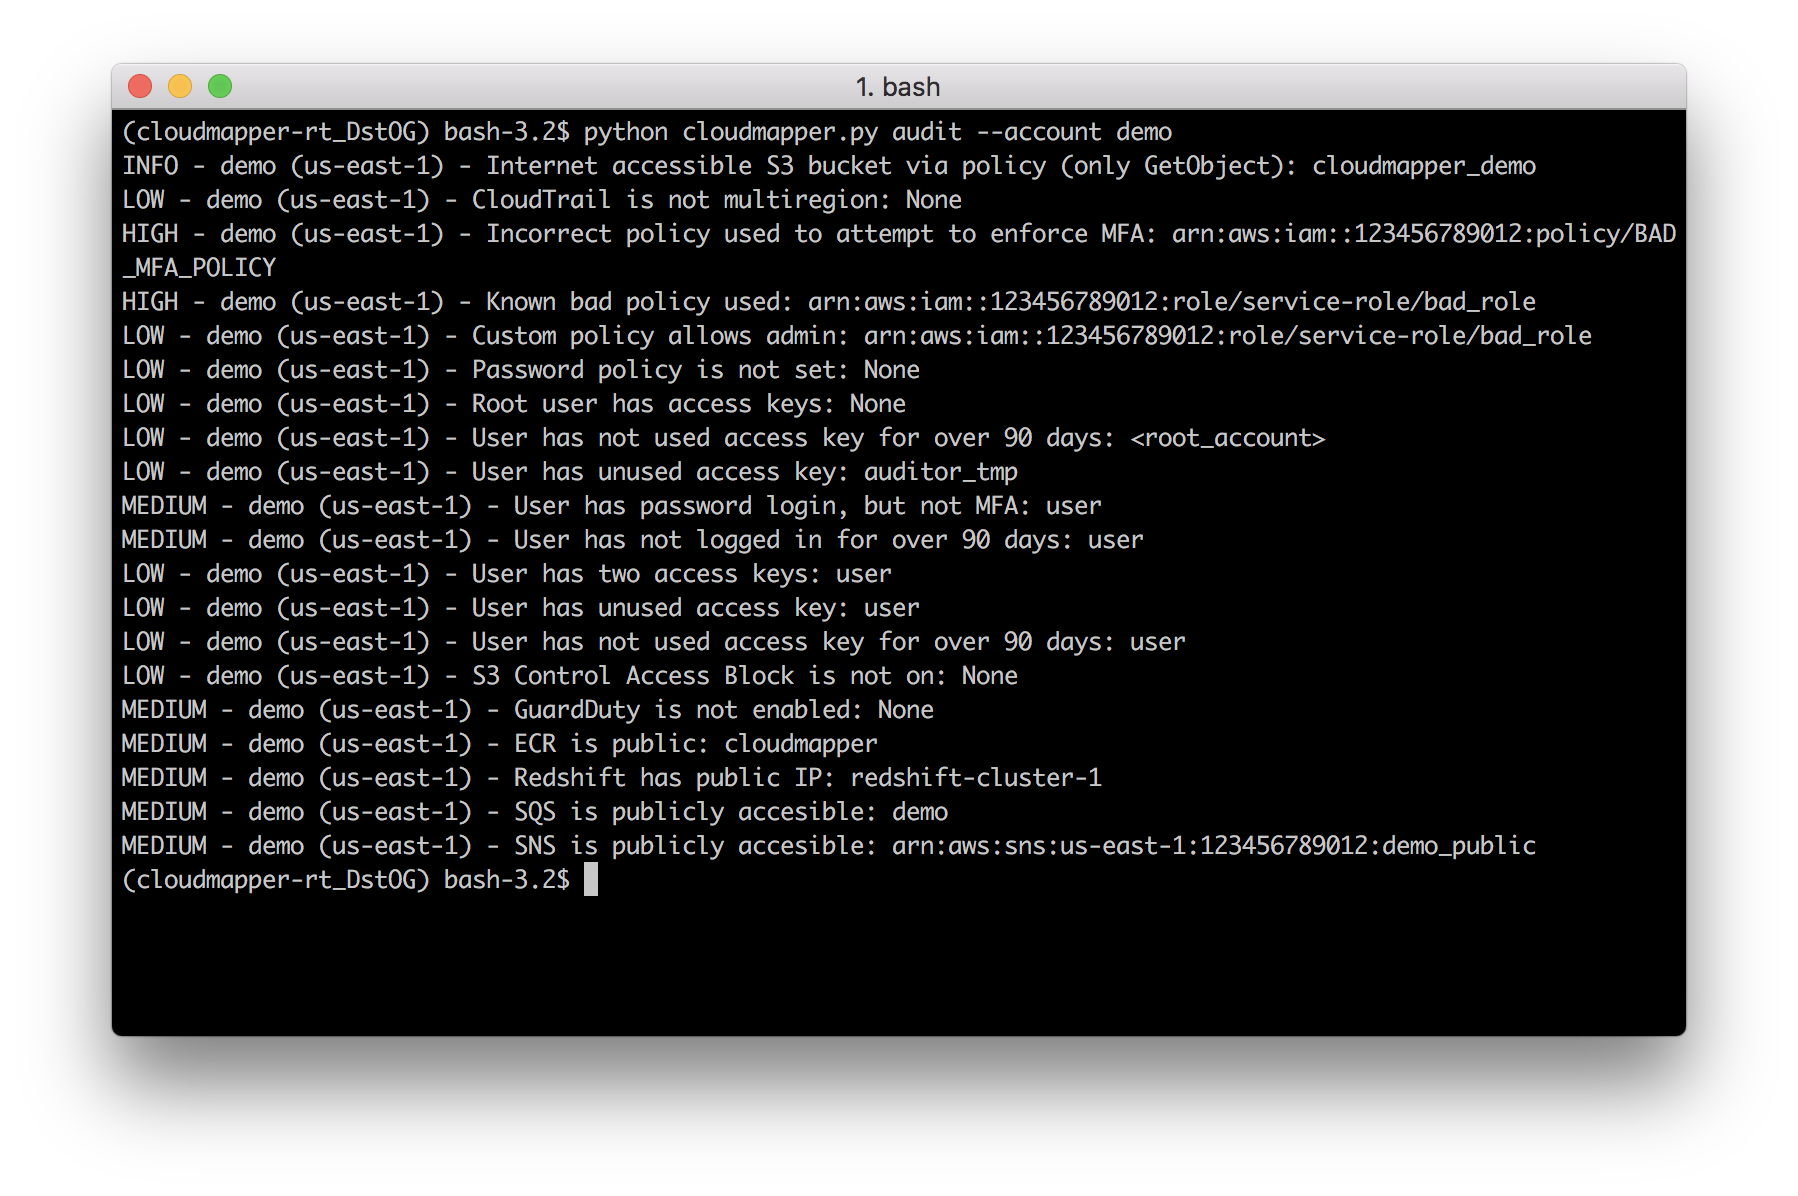 duo-labs/cloudmapper
CloudMapper helps you analyze your Amazon Web Services (AWS) environments.
 shopify/kubeaudit
kubeaudit helps you audit your Kubernetes clusters against common security controls
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
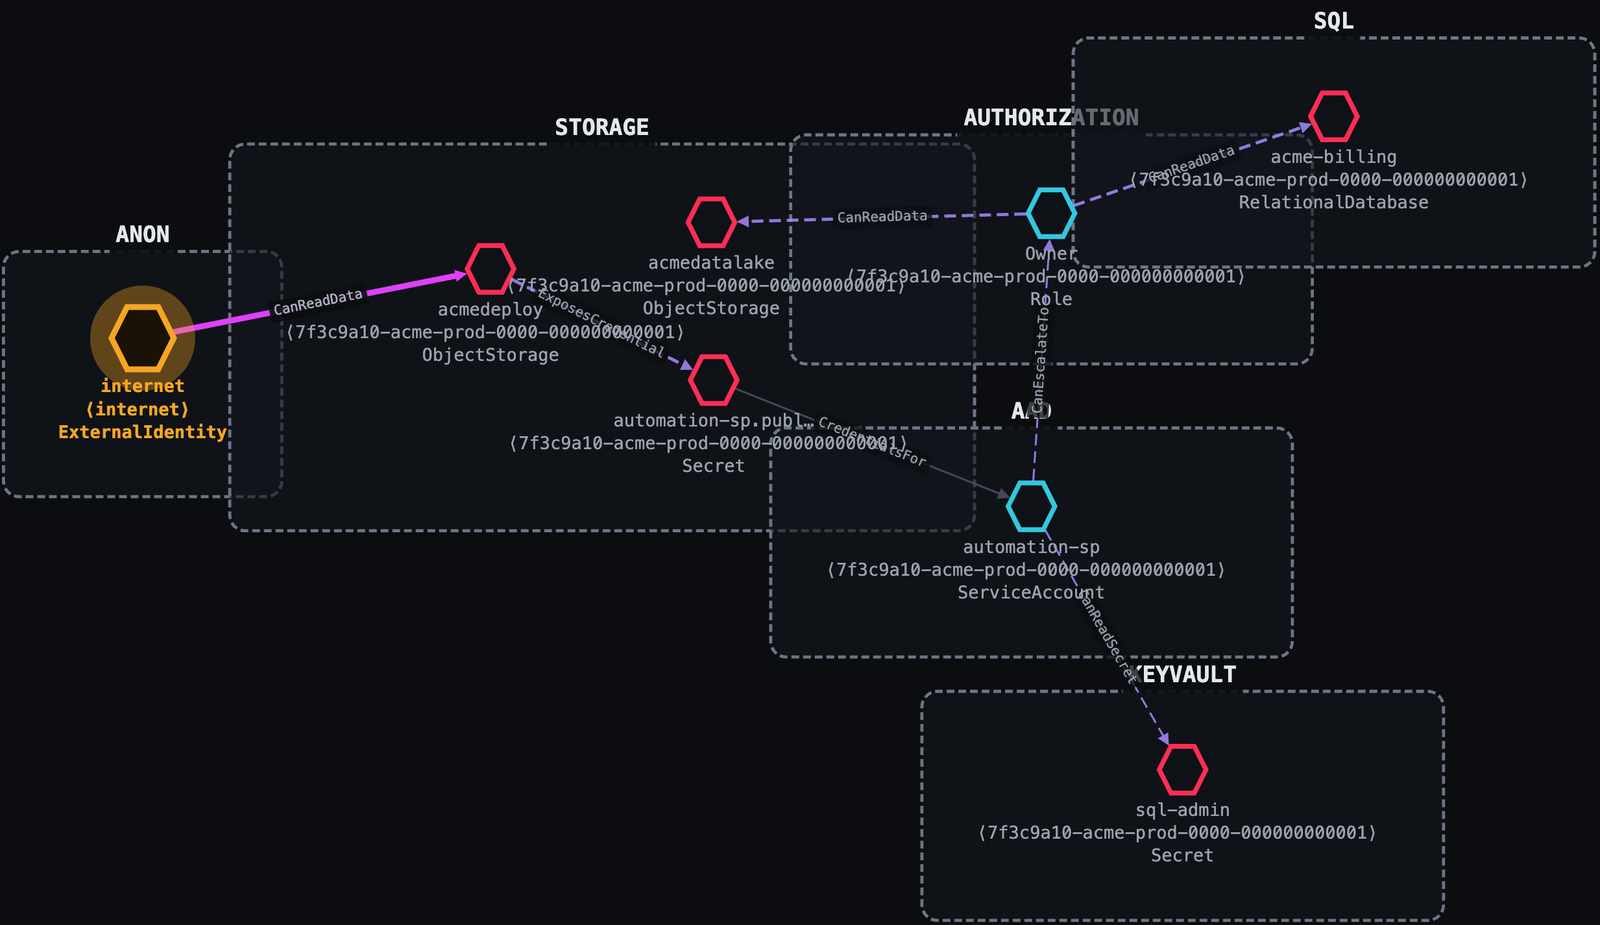 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…