
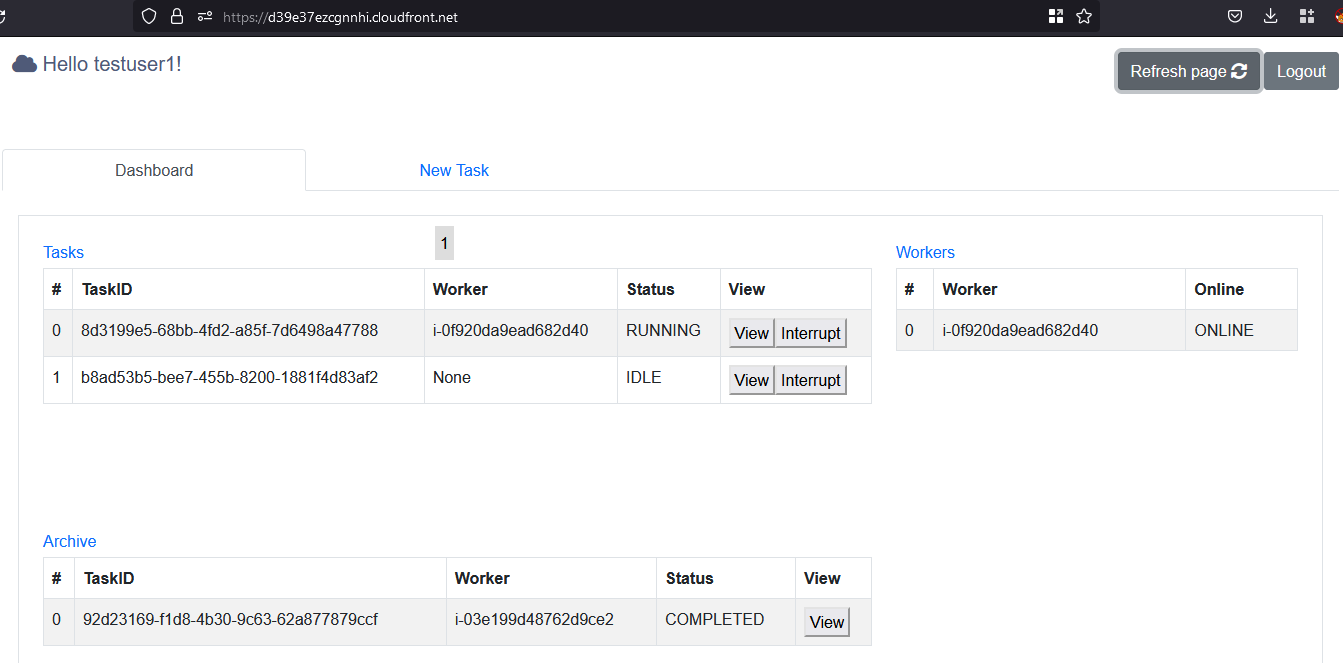
cowcloud
 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
cloud-infrastructure-securitycloud-securitydevsecops+5
60
nccgroup/cowcloudServerless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 tevora-threat/rt_redirectors
Ansible role to configure redirectors for red team C2
 aquasecurity/trivy-plugin-aqua
Plugin for integrating Trivy with Aqua Security platform to scan IaC, pipelines, and dependencies for vulnerabilities and misconfigurations.
 andresriancho/nimbostratus-target
This repository holds a target infrastructure you can use for running the nimbostratus tools.
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
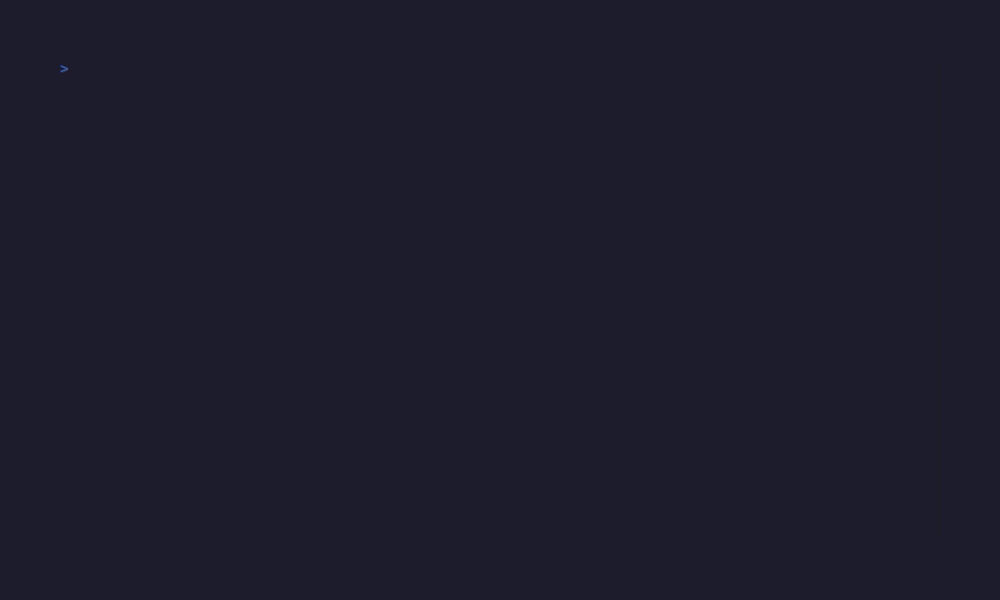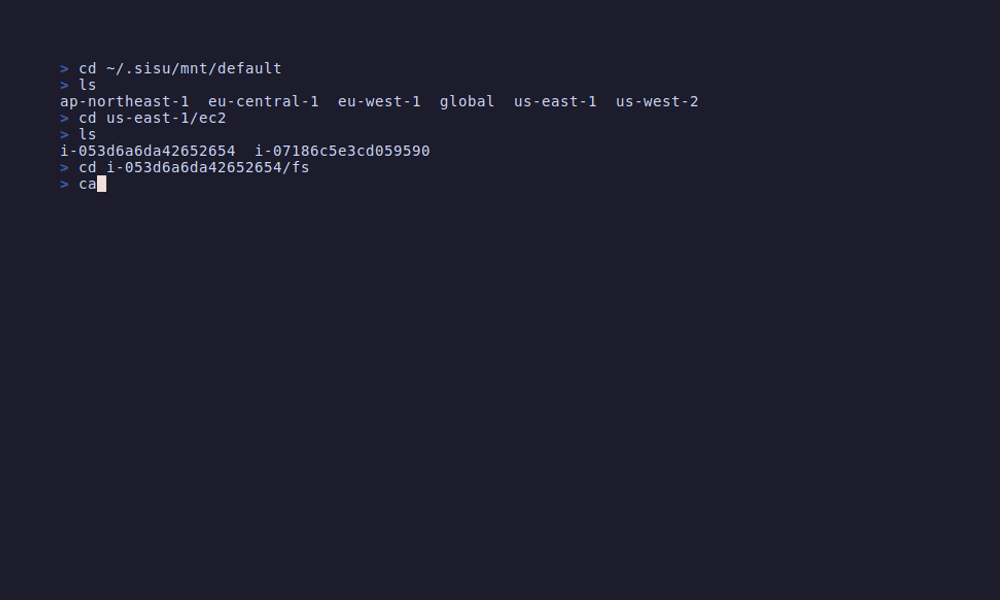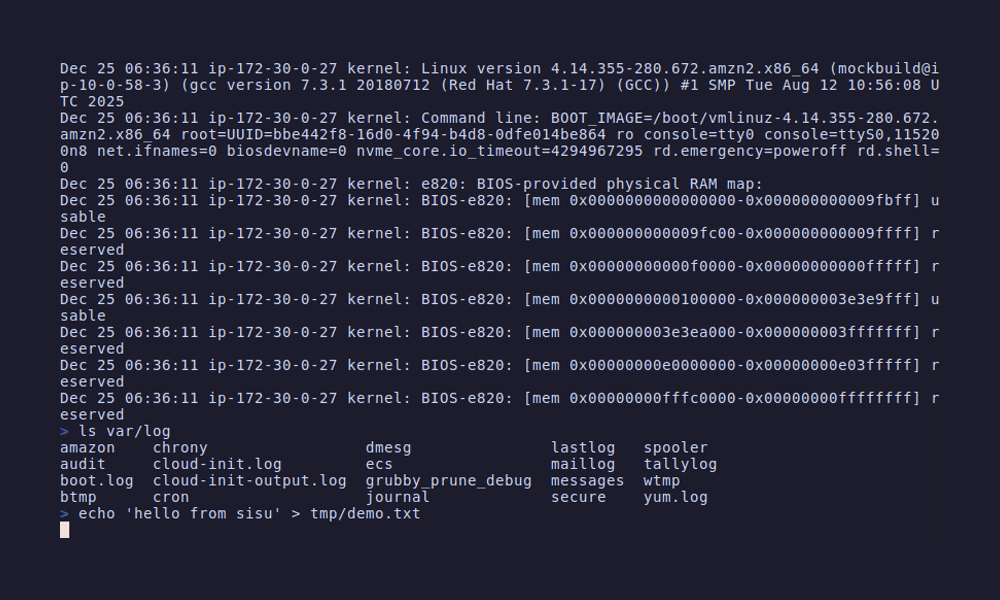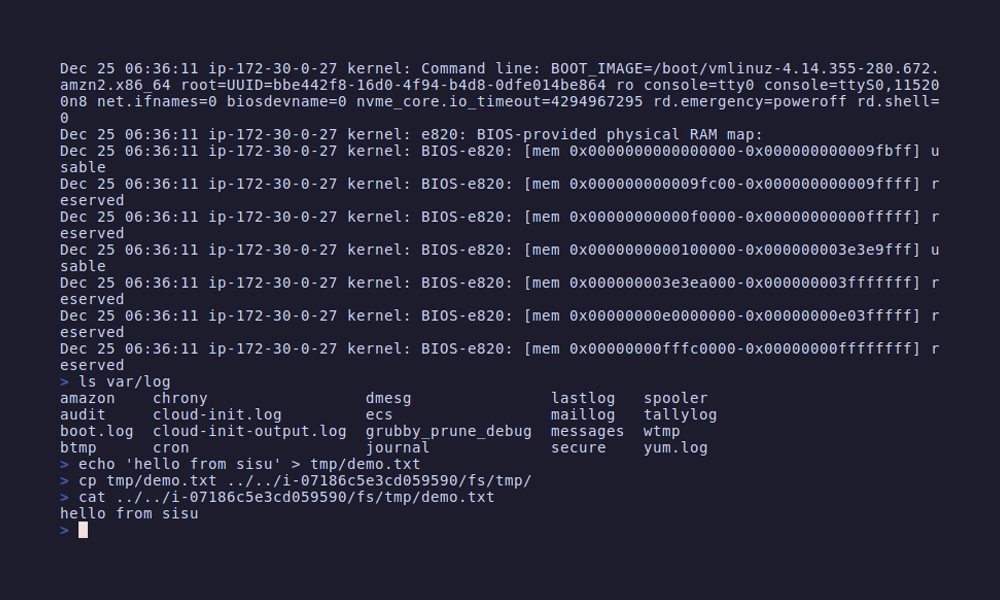 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.
 blake-fm/vcenter-log4j
Script to apply official workaround for VMware vCenter log4j vulnerability CVE-2021-44228
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 jq6l43d1/proxmox-lxc-docker-fix
Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
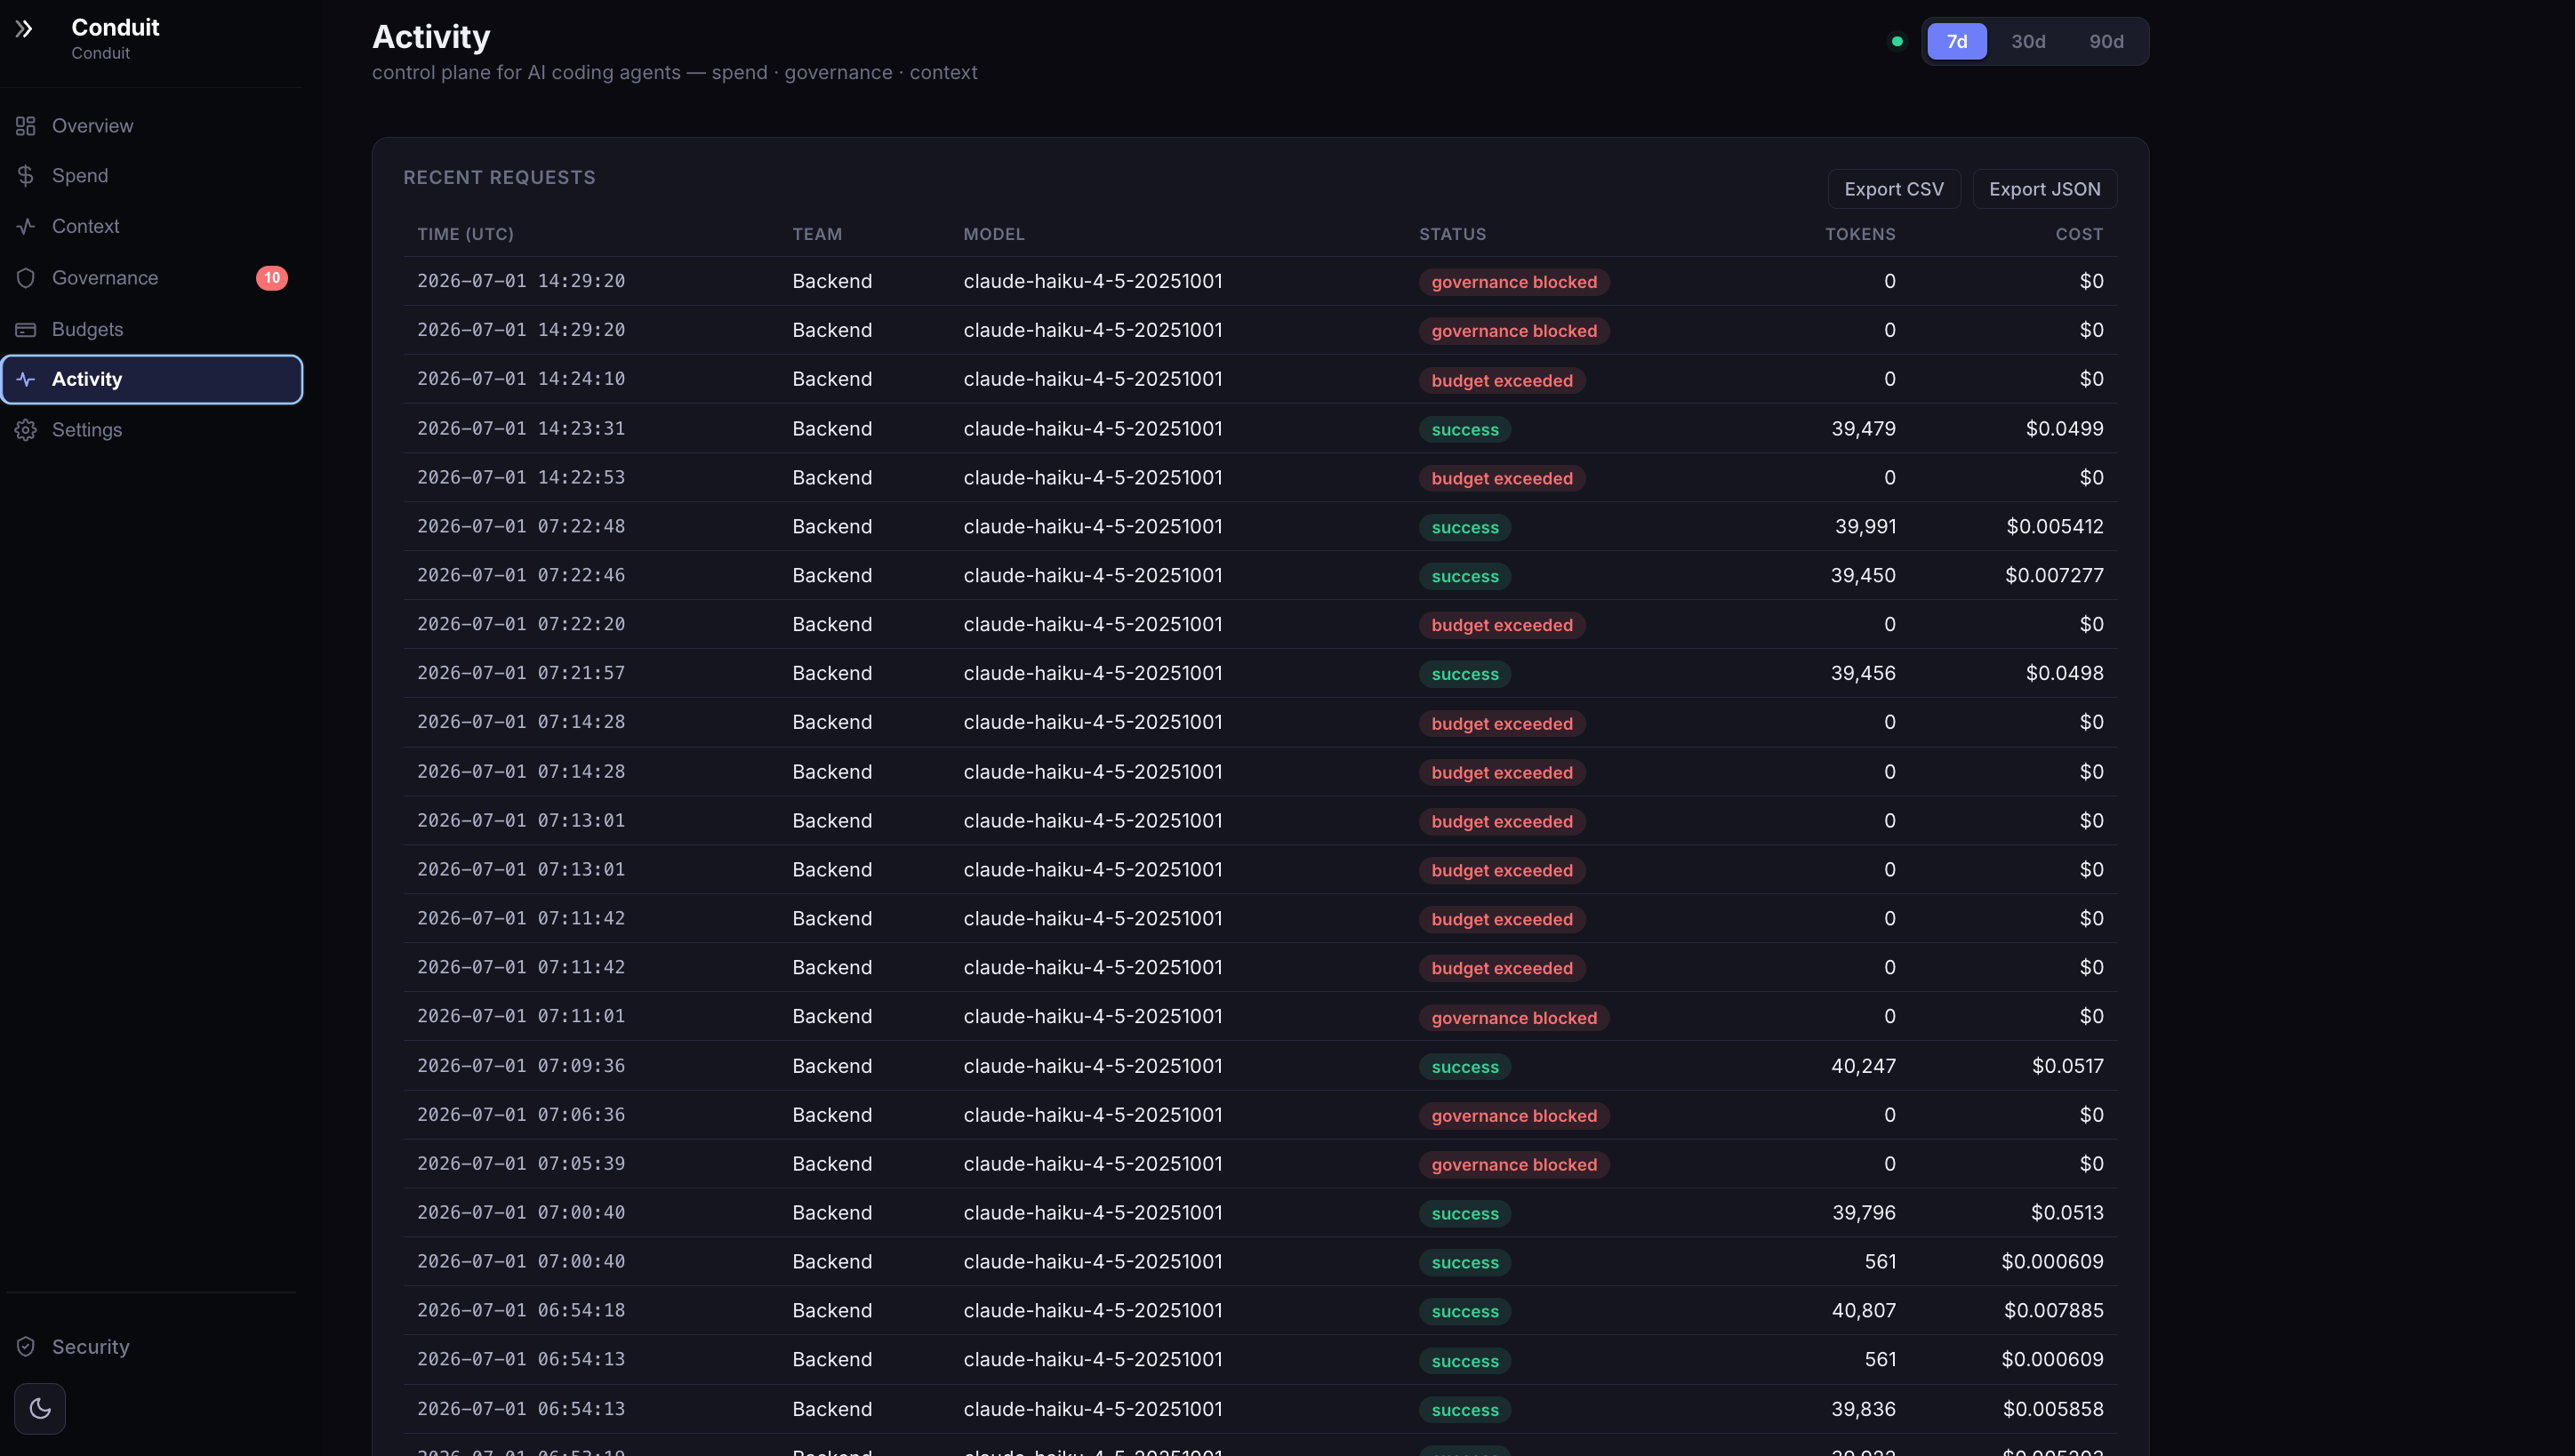 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 tapanmeena/azpim
A command-line interface tool for managing Azure Privileged Identity Management (PIM) role activations directly from your terminal.
 bishopfox/cirro-azcli-ext
Azure CLI extension for Cirro collection
 aoripus-ltd/januscape-hotfix
Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration