OWASP-Top-10-AI-Infrastructure-Security-Risks

A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…

A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…

Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…

Reference implementation of LR+ post-quantum authentication over WebPKI CA context, with corpus pipeline, reconstruction, evaluation, and provenance…

One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…

OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…

GhostLock - CVE-2026-43499 backport patch for openVZ 7

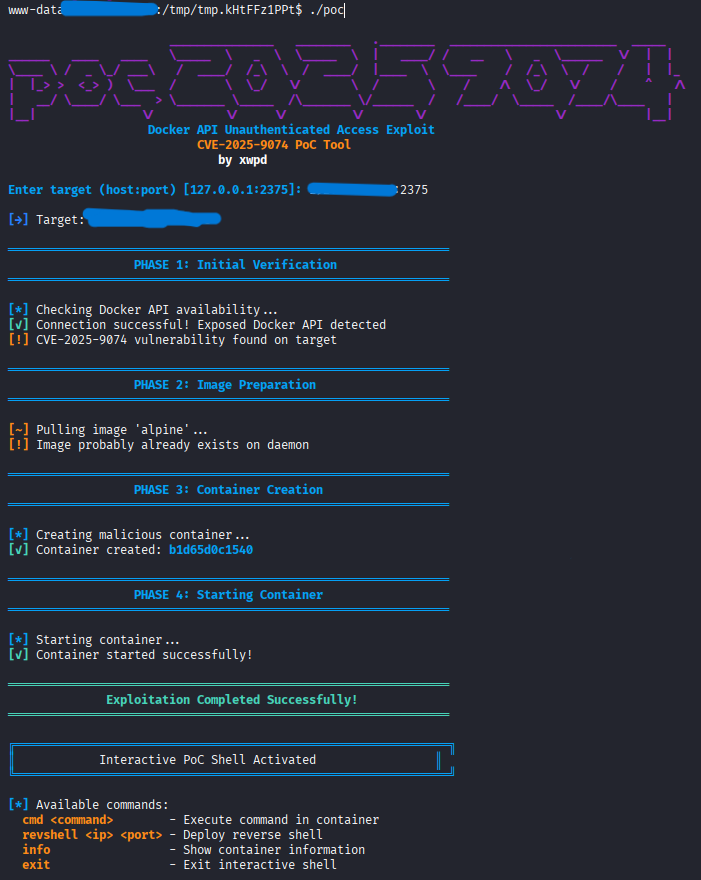
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…

Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…

Proof-of-concept for CVE-2026-22008 demonstrating AWS Lambda layer injection via untrusted ARNs, enabling arbitrary code execution and credential…

Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…

Exploit PoC and vulnerable admission webhook for CVE-2026-5556, demonstrating Kubernetes admission controller bypass via case-sensitive pod name…

Ansible playbook to detect and apply kernel cmdline mitigation for CVE-2026-31431 (Copy Fail) across Debian/Ubuntu/RHEL fleets, with read-only…

Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.

Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…

CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…

Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration

eBPF + nftables + DNS proxy egress enforcement for GitLab Runner CI/CD job containers — community edition data plane https://leitwacht.eu/

A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…