
cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources

Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources

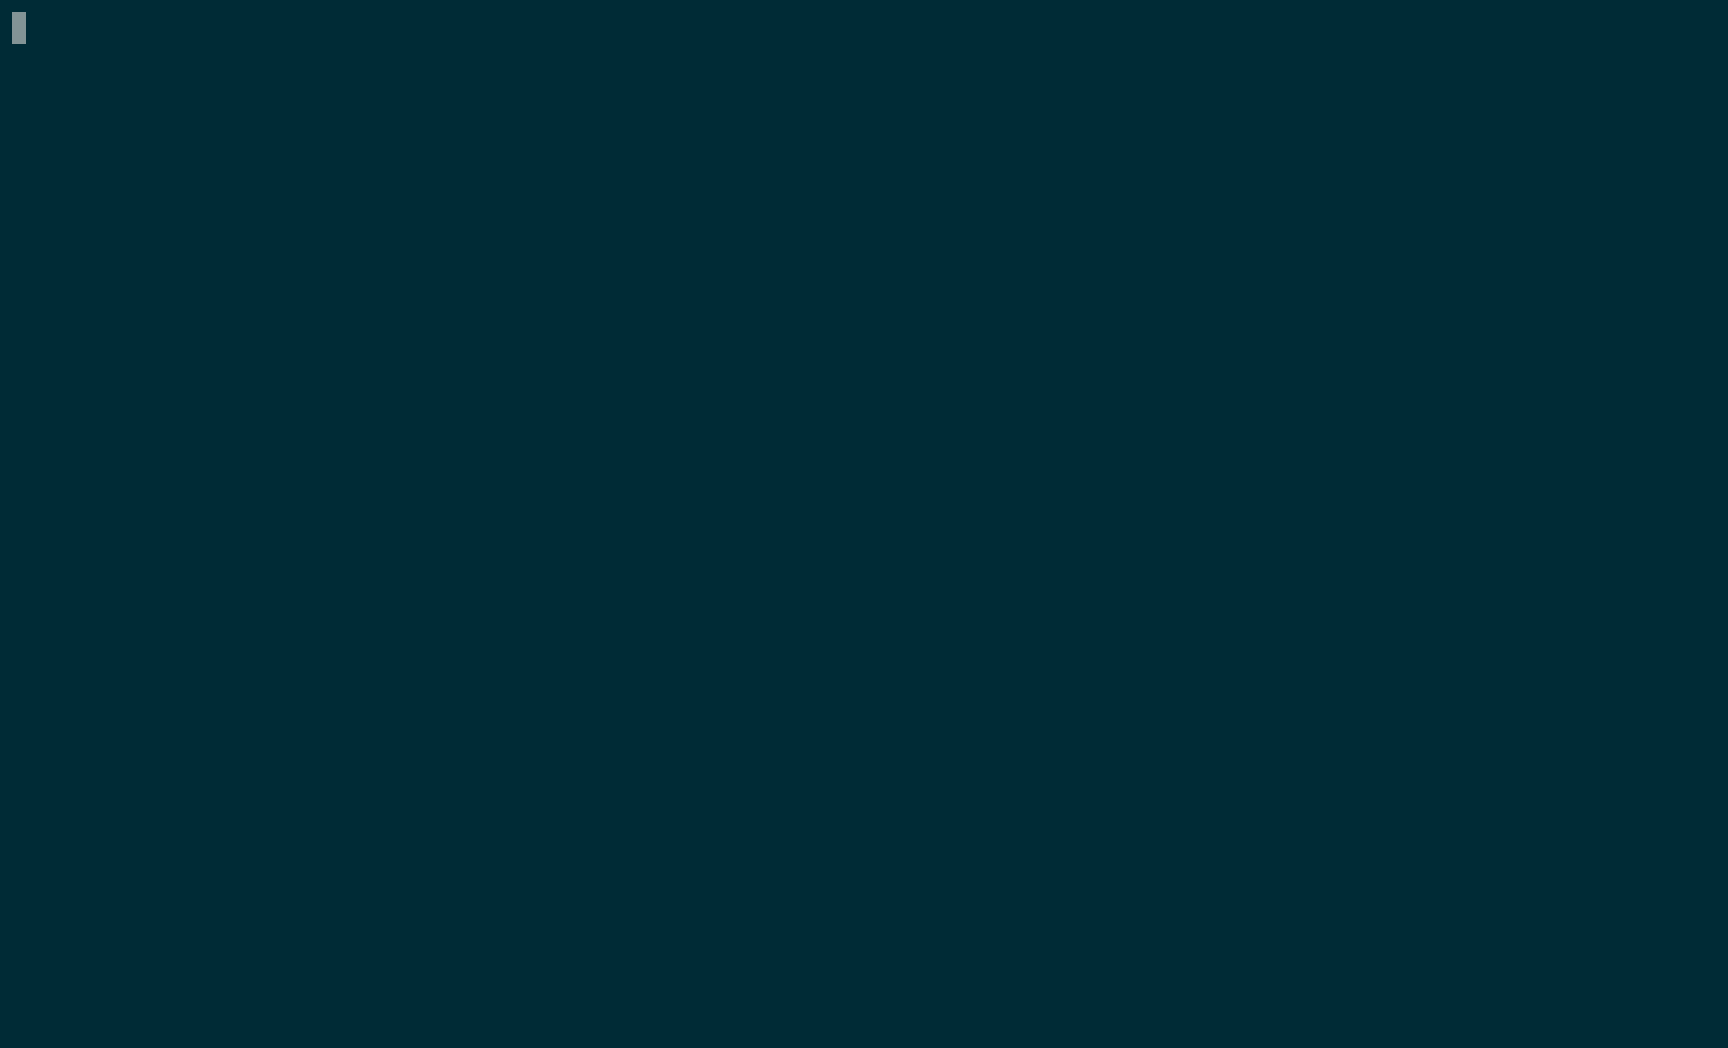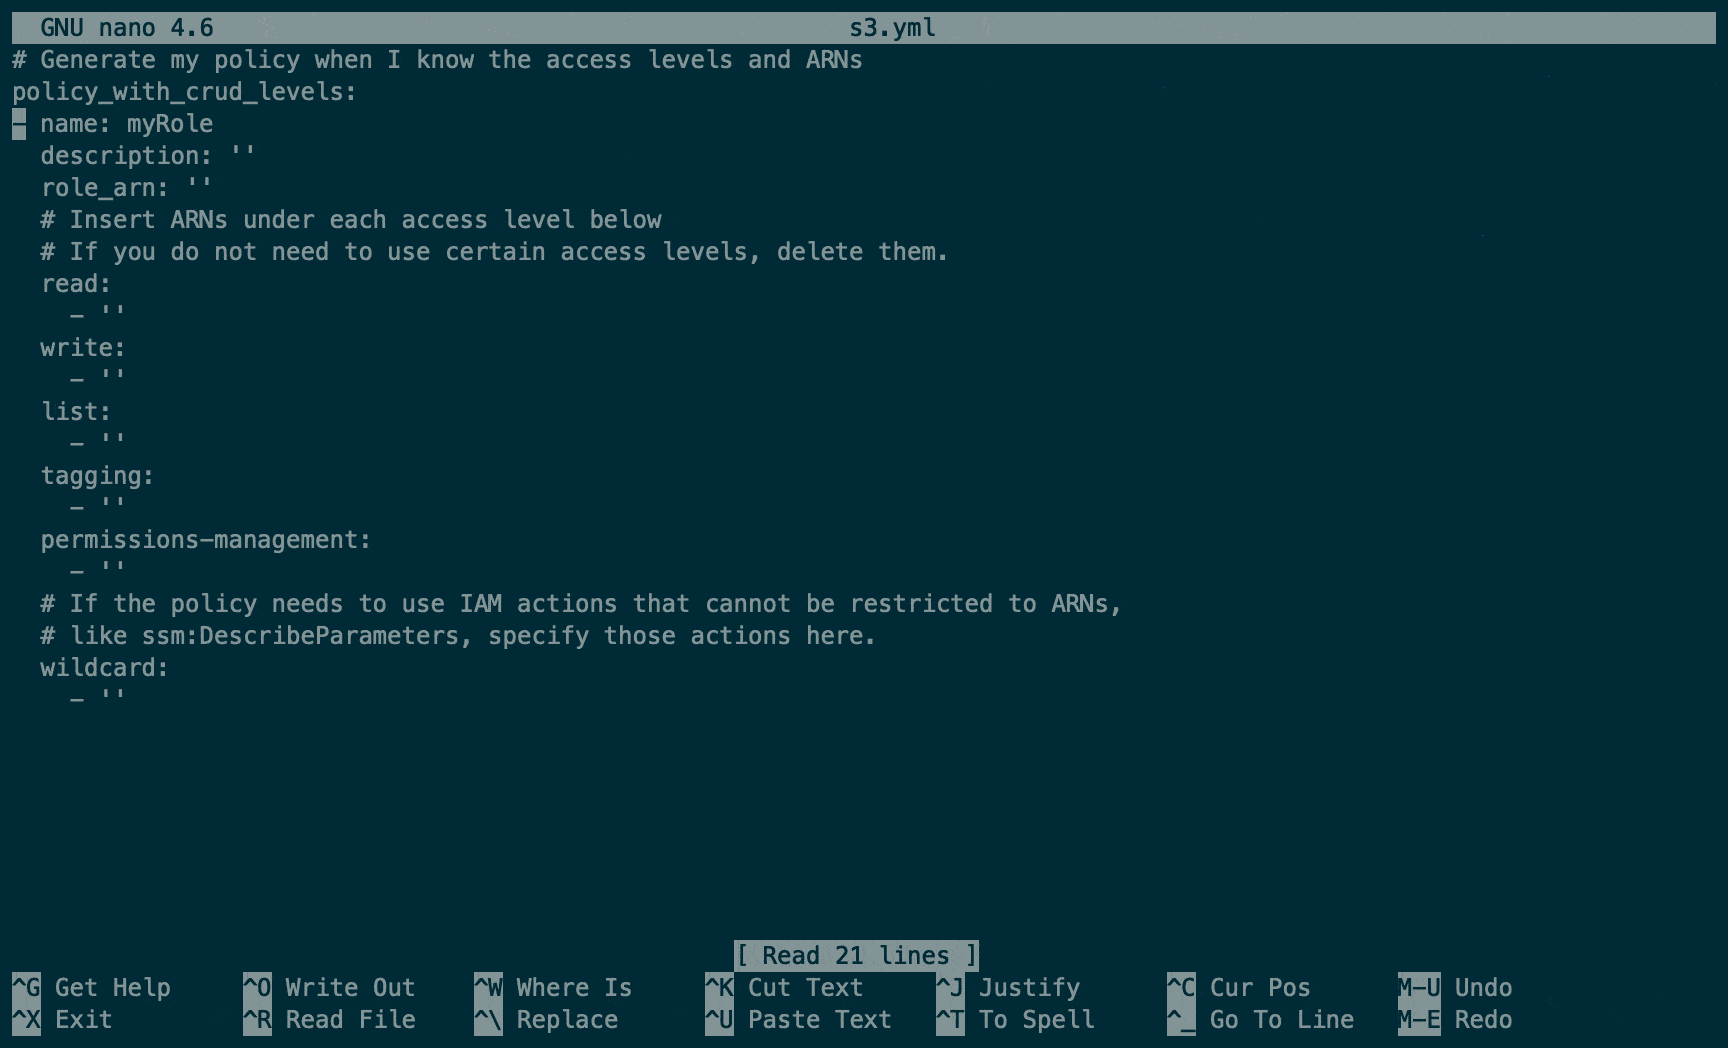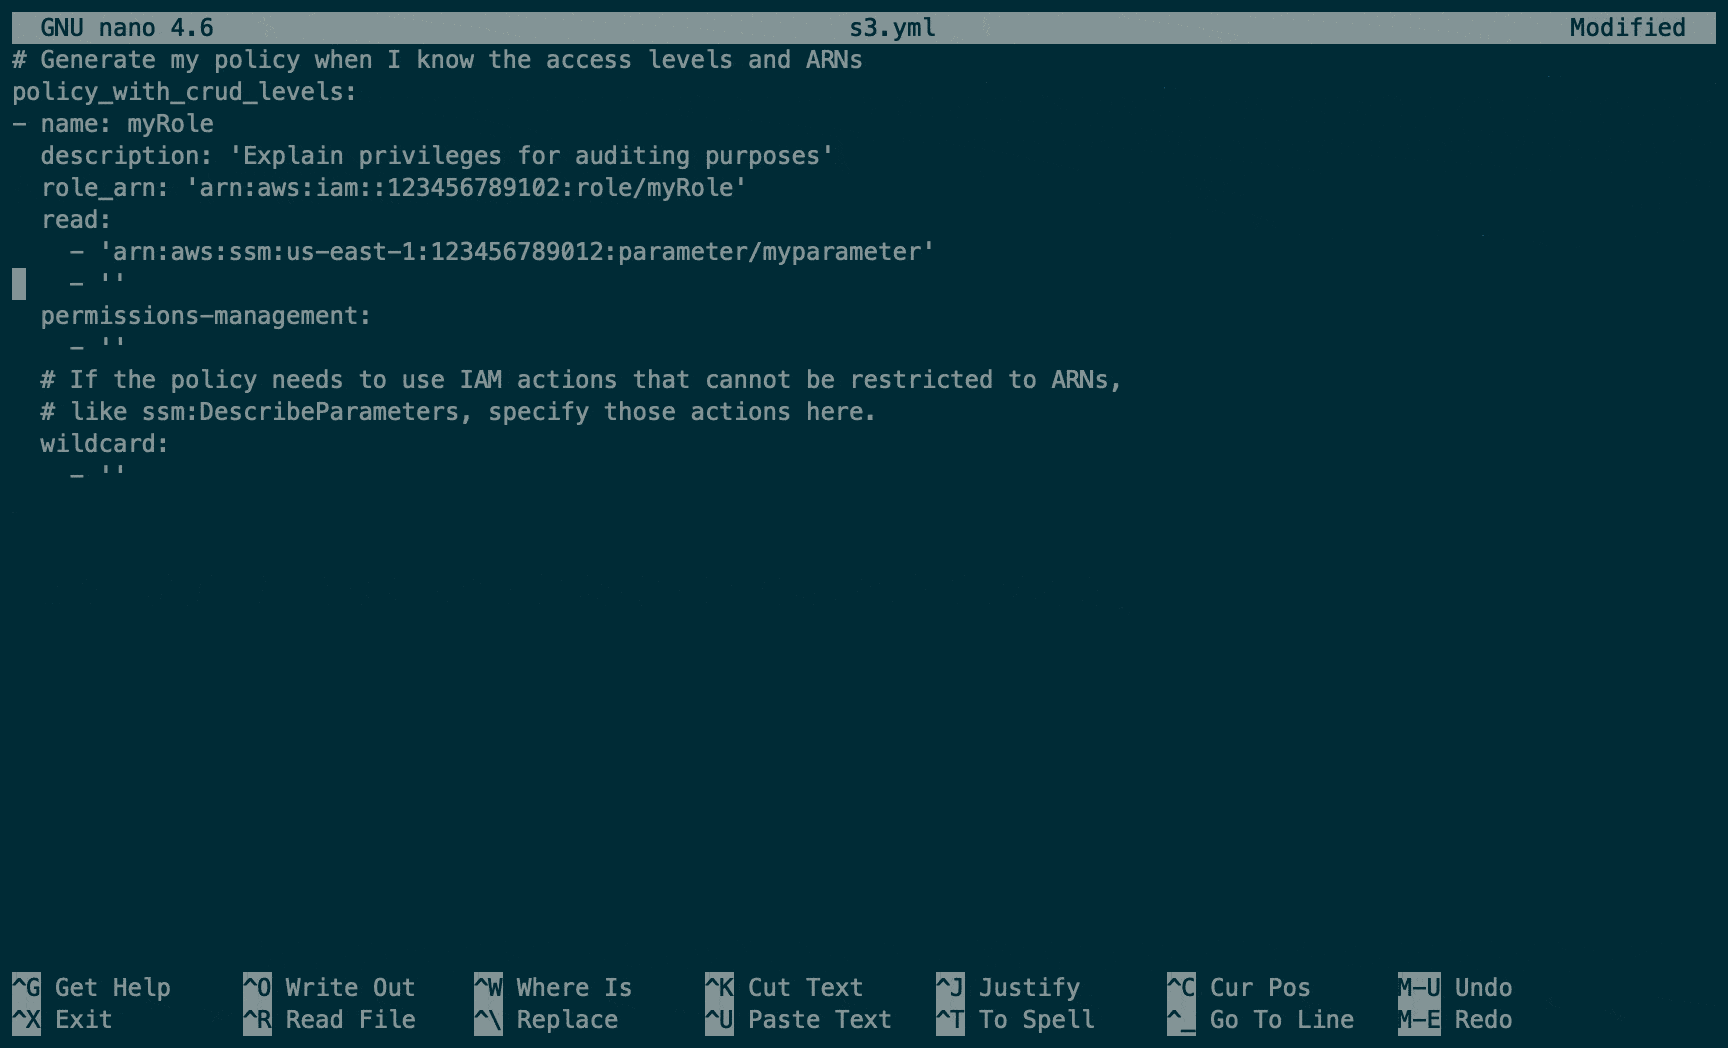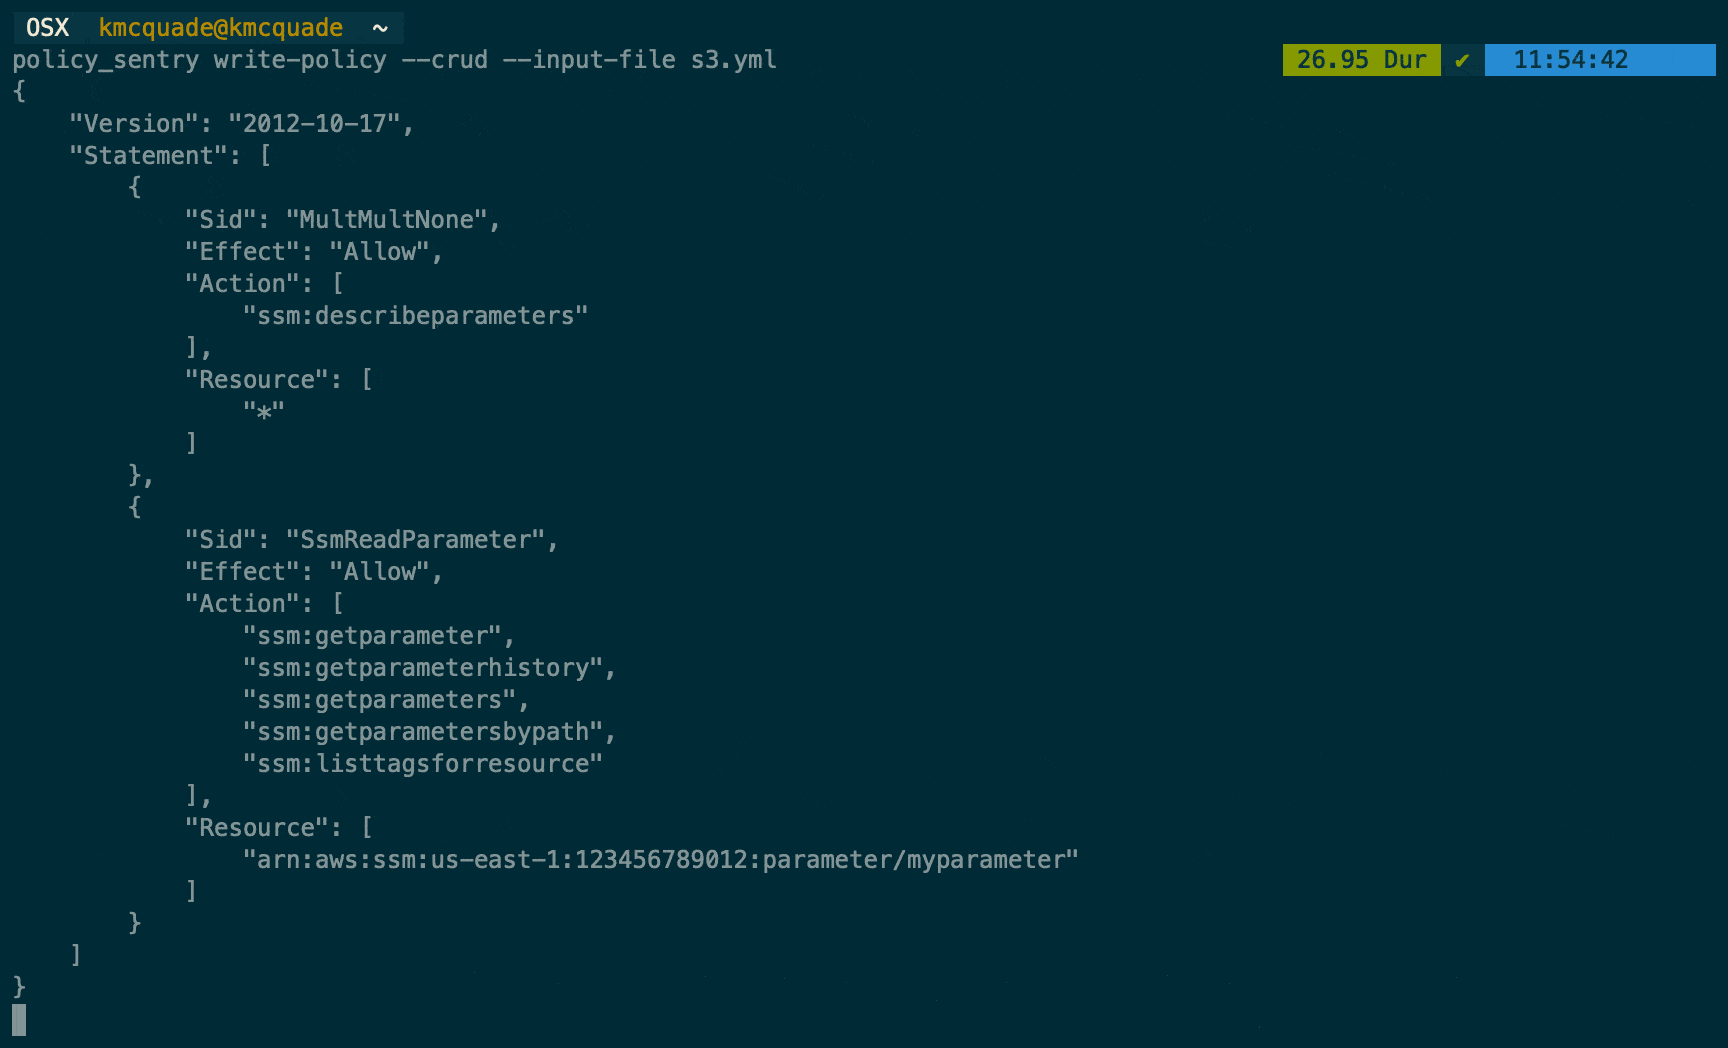
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.

Ansible playbooks to check and mitigate CVE-2026-31431 on Linux hosts, with scripts for local, remote, and containerized environments, including…

Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.

Powershell module for VMWare vSphere forensics

Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)

CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…

CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…

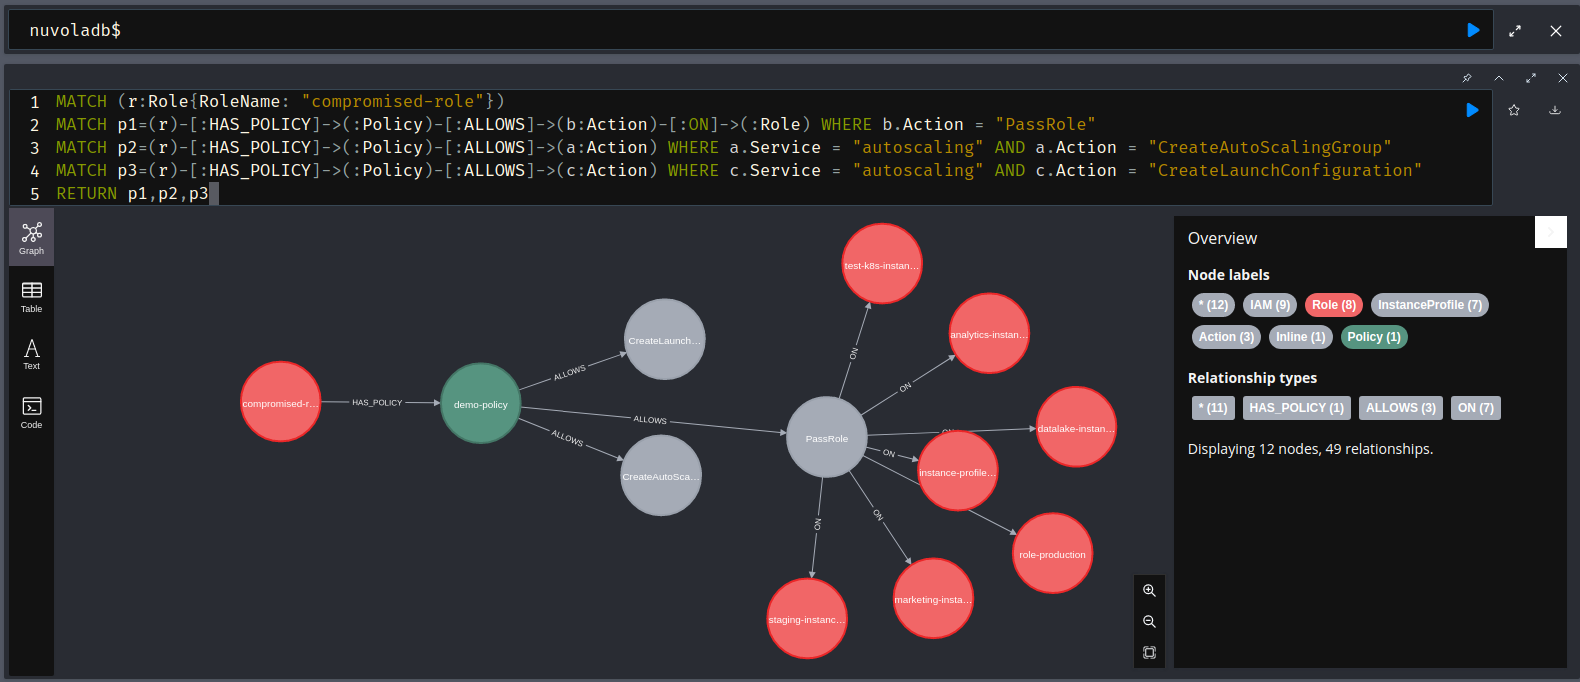
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…

Remediation task for CVE-2018-15686, CVE-2018-16866, and CVE-2018-16888 affecting SystemD in EL7

Like Envoy xDS, but for eBPF filters

Fleet-scale CVE-2026-31431 audit and remediation orchestrator for Linux hosts via SSH, with strict host-key verification and multi-format reporting.

Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…

Scans AWS IAM configurations for shadow admins by detecting misconfigured deny policies that fail to restrict user actions on groups, enabling…

Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…

Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…

Quick mitigation and patch script for CVE-2026-31431 (Copy Fail) on Ubuntu/Debian VPS

Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…