
vmsan
 angelorc/vmsan
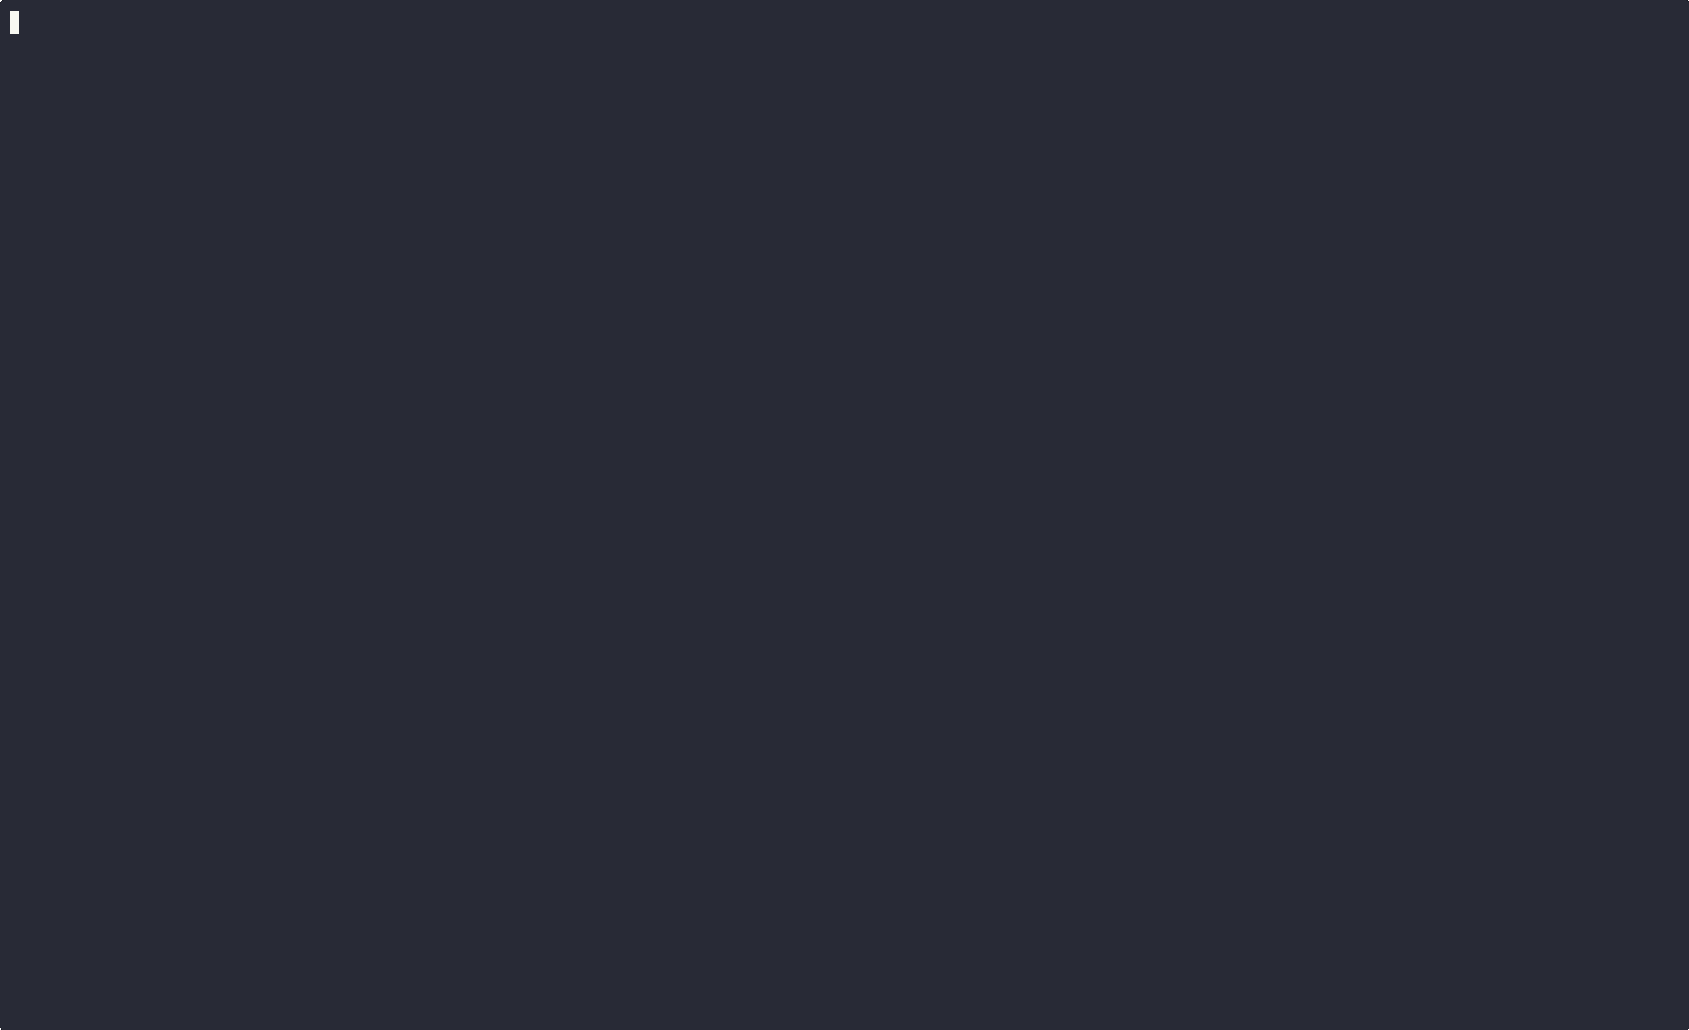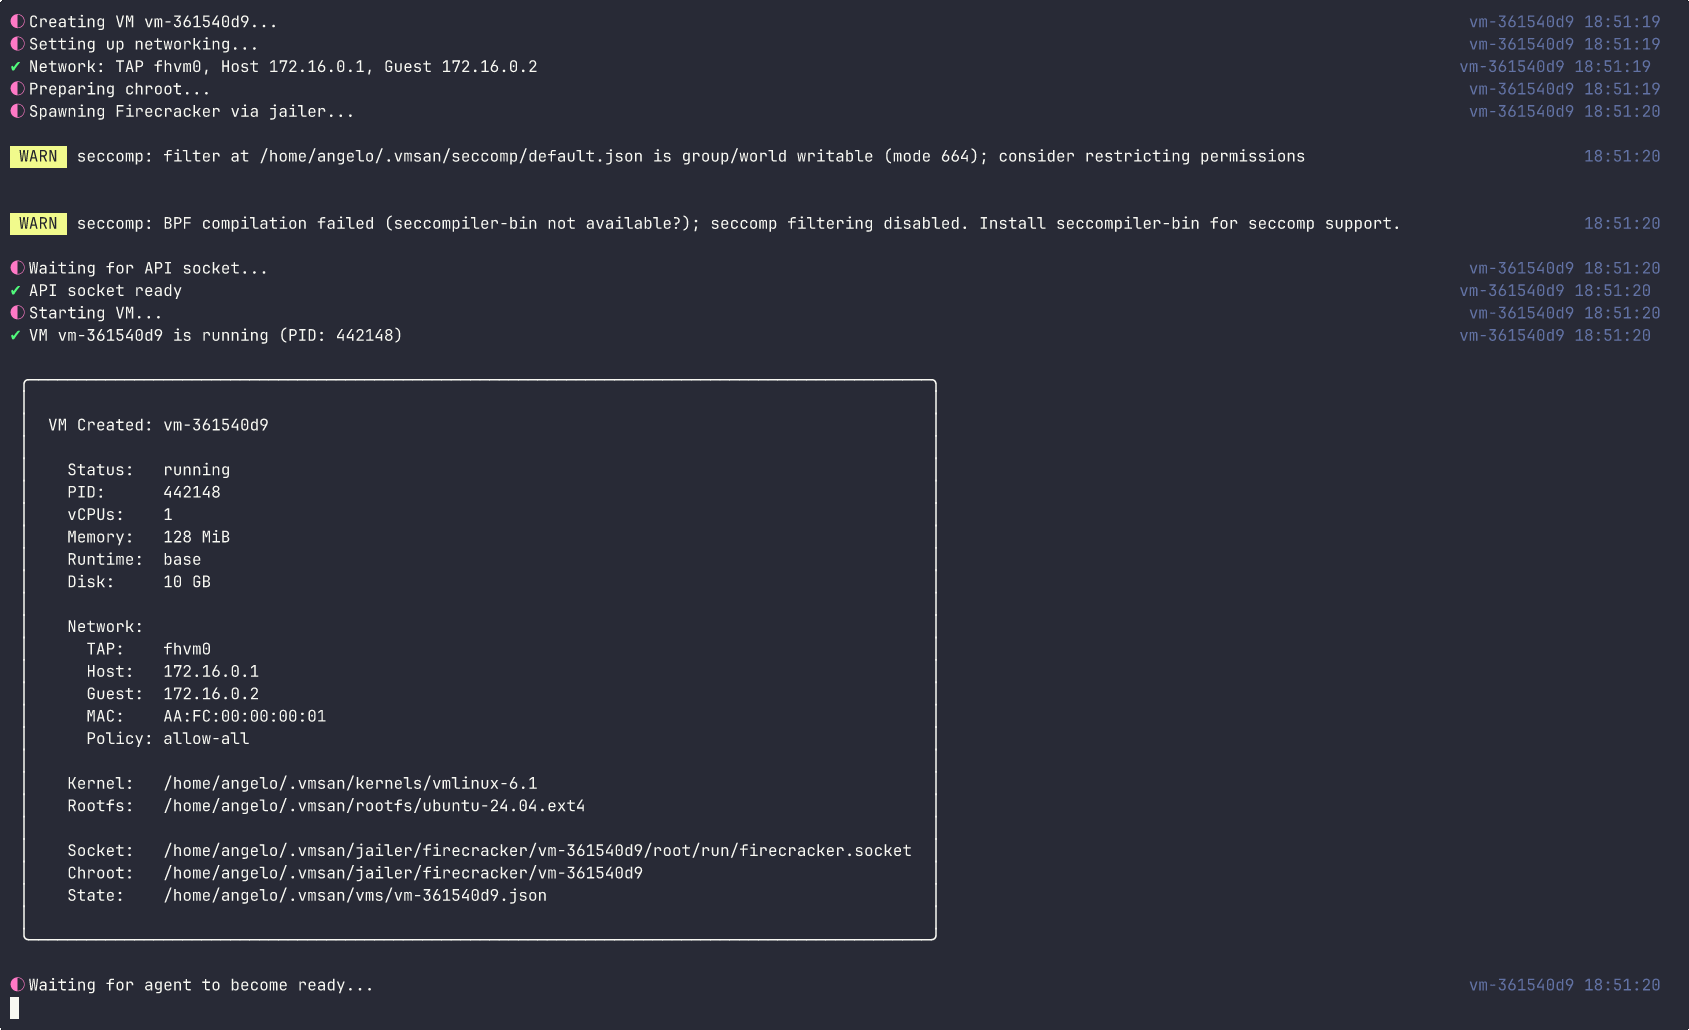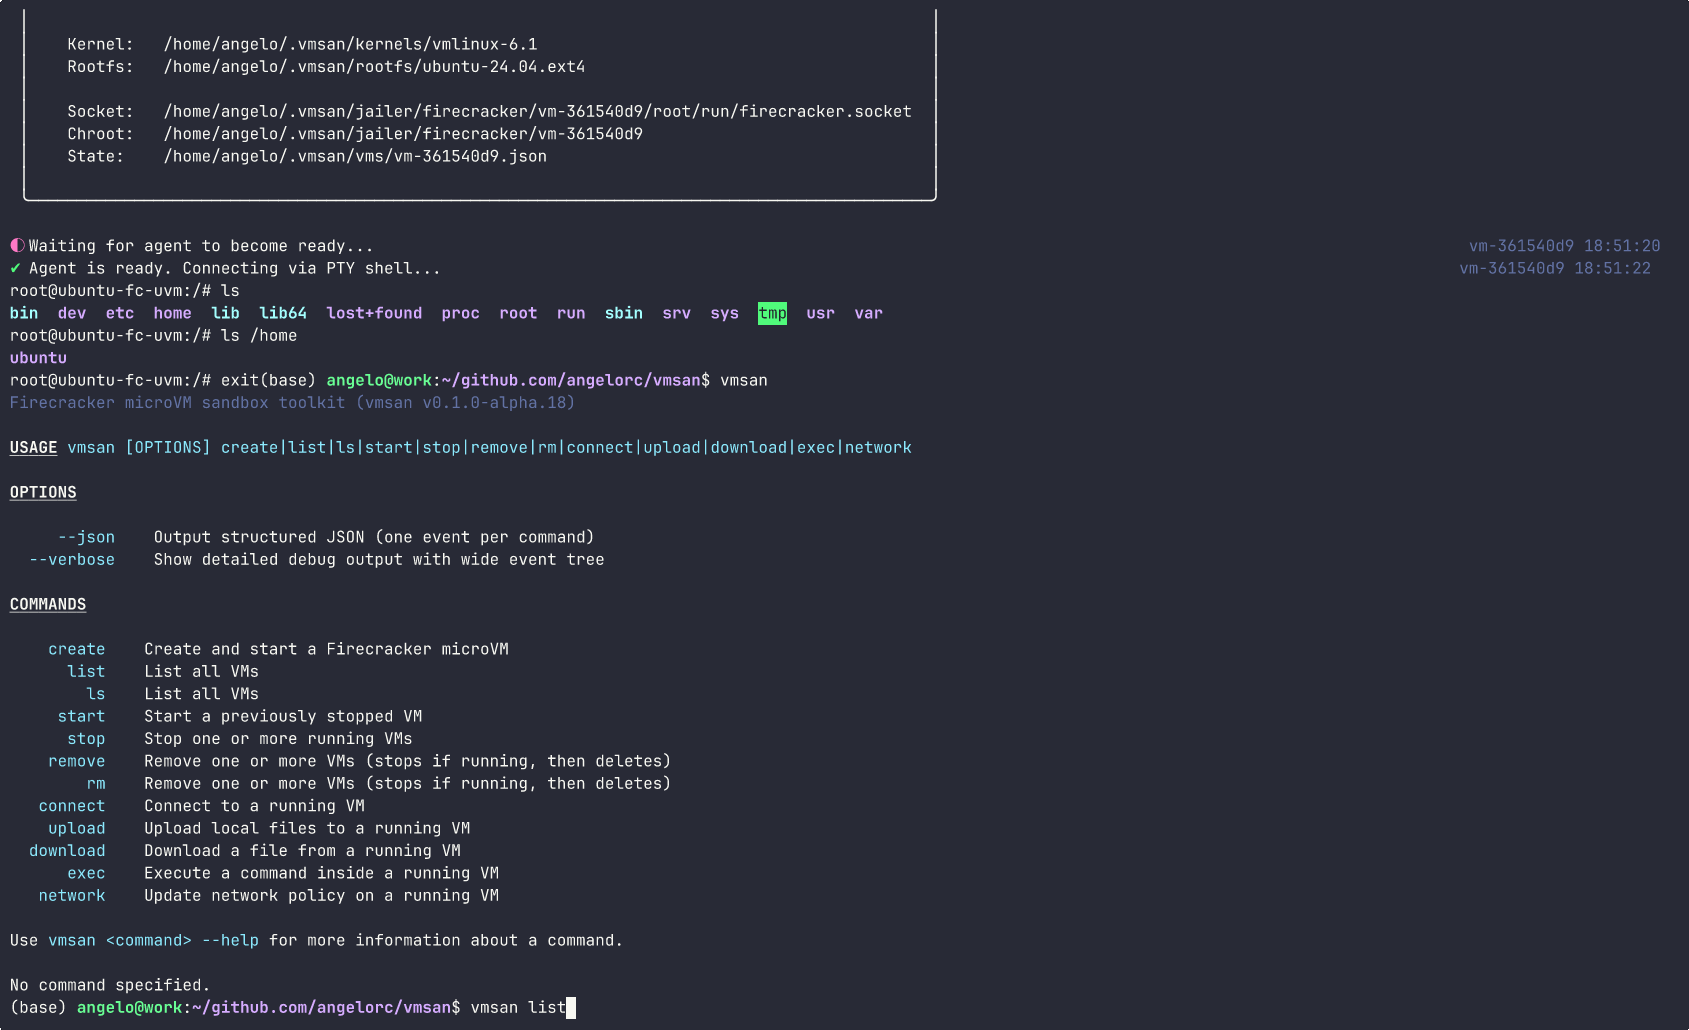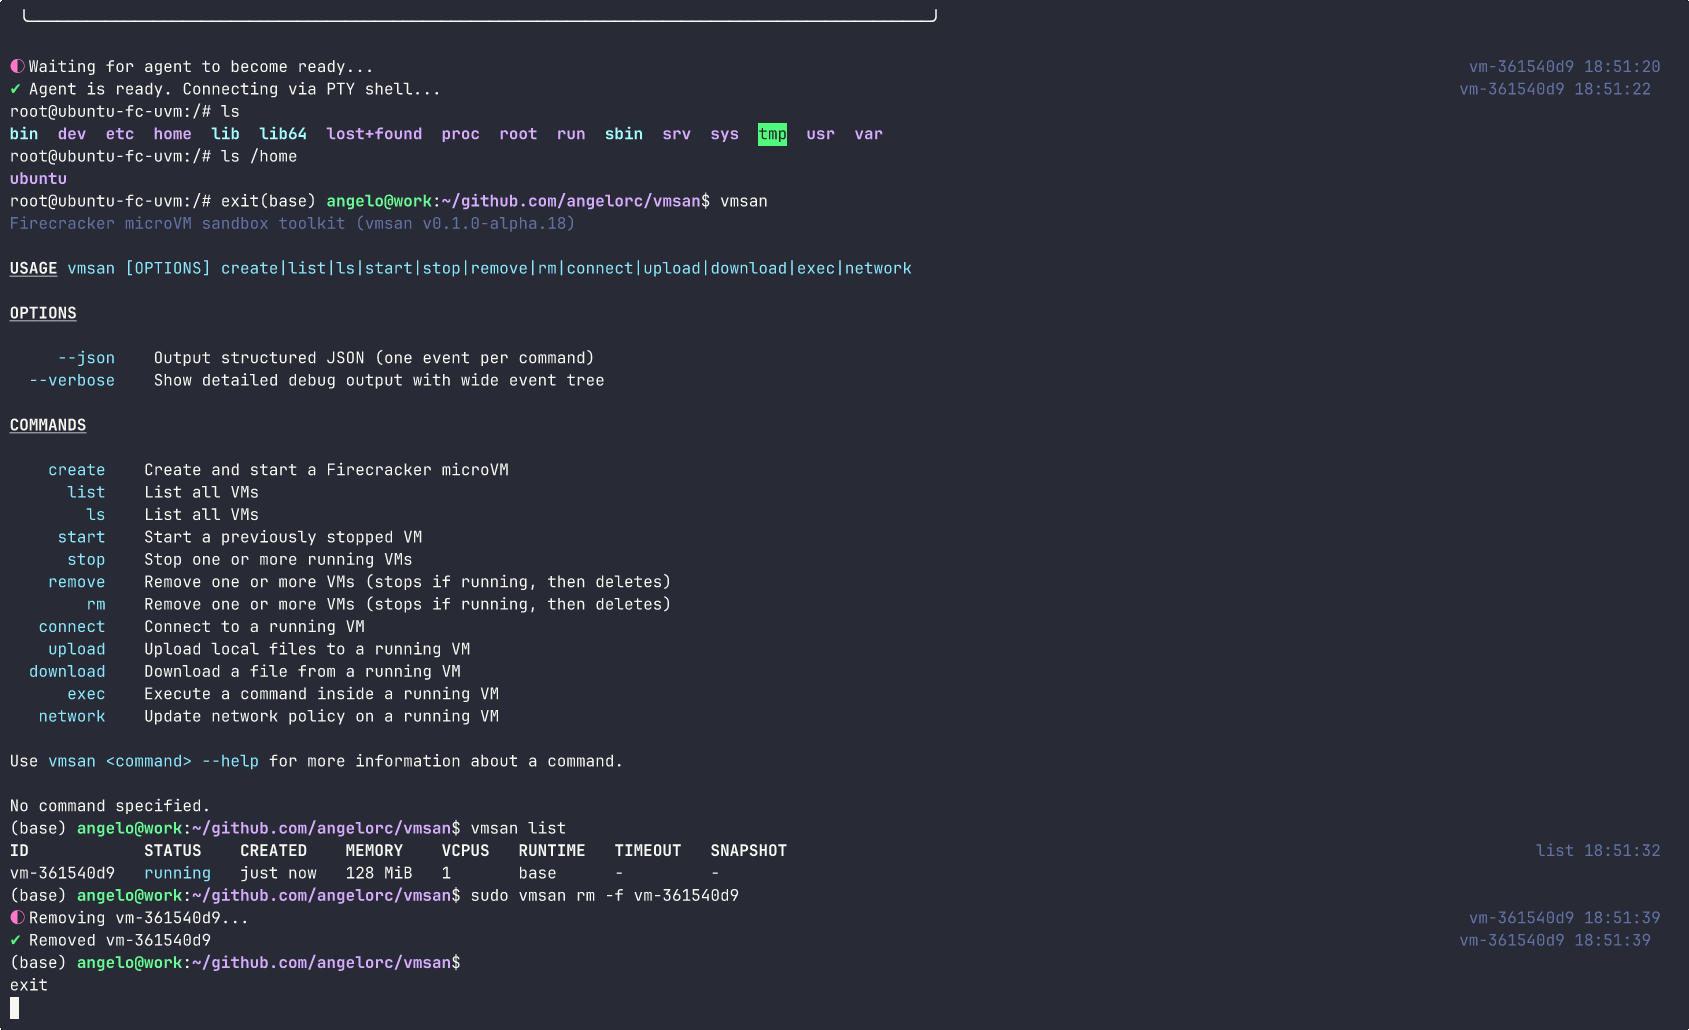
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
cloud-infrastructure-securitycontainer-securitydevsecops+3
angelorc/vmsanFirecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 wearecloudar/s3-account-search
S3 Account Search
 pyperanger/dockerevil
WorldFirst (Public) Docker API Exploit - My security researches involving Docker and Openshift
 qarait/ephemera
Zero-Trust SSH CA
 jdauphant/patch-openssl-cve-2014-0160
Patch openssl #heartbleed with ansible
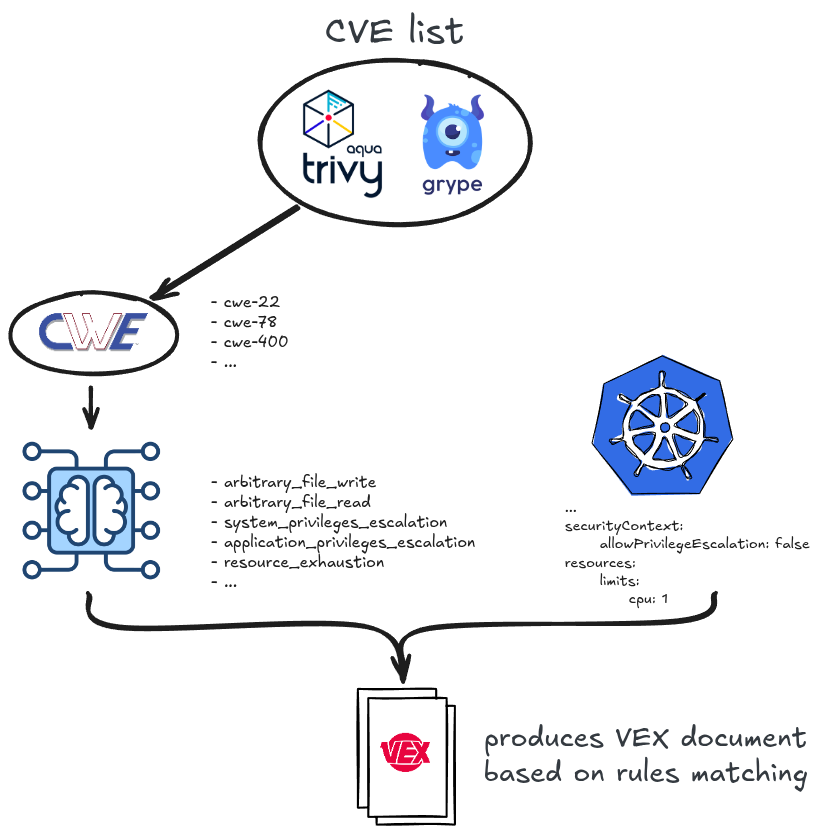 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 mitiga/log4shell-cloud-scanner
we are providing DevOps and security teams script to identify cloud workloads that may be vulnerable to the Log4j vulnerability(CVE-2021-44228) in…
 akhld/spark-exploit
Arbitary Code Execution in Unsecured Apache Spark Cluster
 atiilla/cve-2026-42897
CVE-2026-42897 - Exchange Health Checker blind spot: outbound IIS URL Rewrite rules silently ignored, making EOMT mitigations invisible in diagnostic…
 gduma-phdata/patch-cve-2026-15502
Patch: SSRF leading to RCE (Microsoft Exchange Server)
 schroeder-sys/pantheon-souverainete
Infrastructure cloud modulaire, redondante et 100% souveraine pour s'affranchir des GAFAM. Guides techniques, architecture Zero-Trust et chiffrement…
 oriolrius/kafka-keycloak-oauth
Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction
 xiaoqimikko/tomcat85-check
CVE-2025-55752:Tomcat 8.5 已 EOL,终版 8.5.100。Apache 逐条声明「8.5 也受影响」的 2025 CVE 有 14 条,其中 10 条在 NVD 按 8.5.100 查不到。离线单 jar,读 conf/ 判断你到底中了哪几条。
 imlzw/kubernetes-1.12.3-all-auto-install
个人整理的Centos7.x + Kubernetes-1.12.3 + Dashboard-1.8.3 无 CVE-2018-1002105 漏洞的master节点全自动快速一键安装部署文件,适用于测试环境,生产环境的快速安装部署
 infiniroot/ansible-mitigate-copyfail-dirtyfrag
Simple Ansible Playbook to mitigate against CopyFail (CVE-2026-31431) and DirtyFrag (CVE-2026-43284) vulnerabilities.