

kubeshark
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
ai-securitycloud-infrastructure-securitycloud-security+9
12.1k
kubeshark/kubesharkeBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 ooafa/bucketbuster
Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
 mailcow/mailcow-dockerized
Dockerized mail server suite with Postfix, Dovecot, Rspamd, and ClamAV. Provides secure email hosting with integrated spam filtering, antivirus, and…
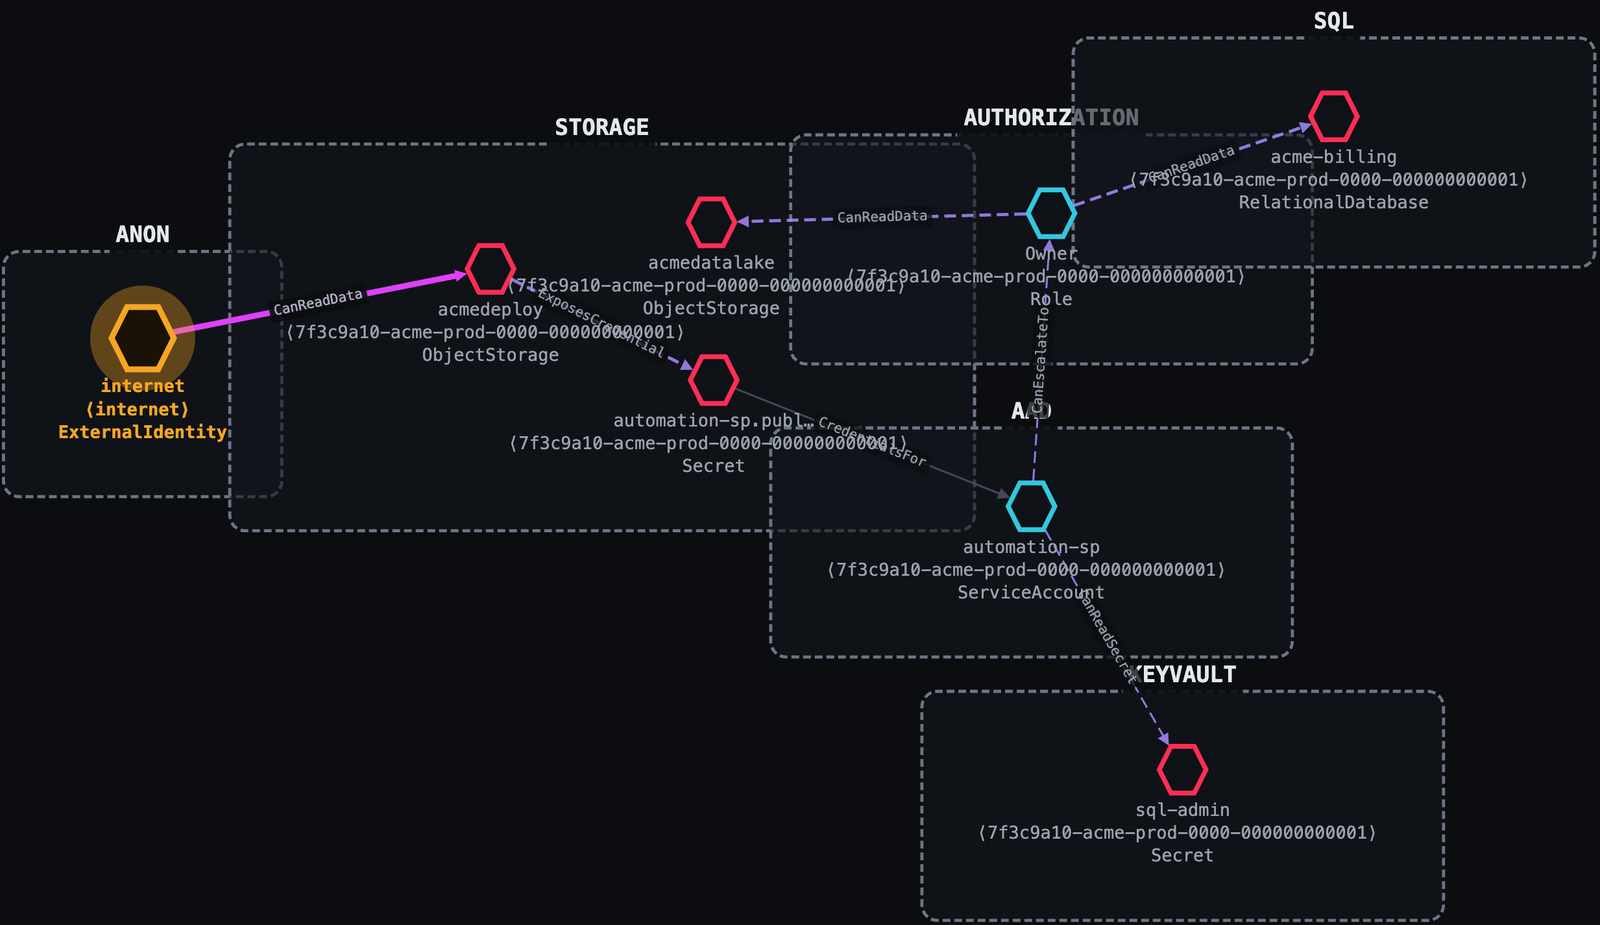 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
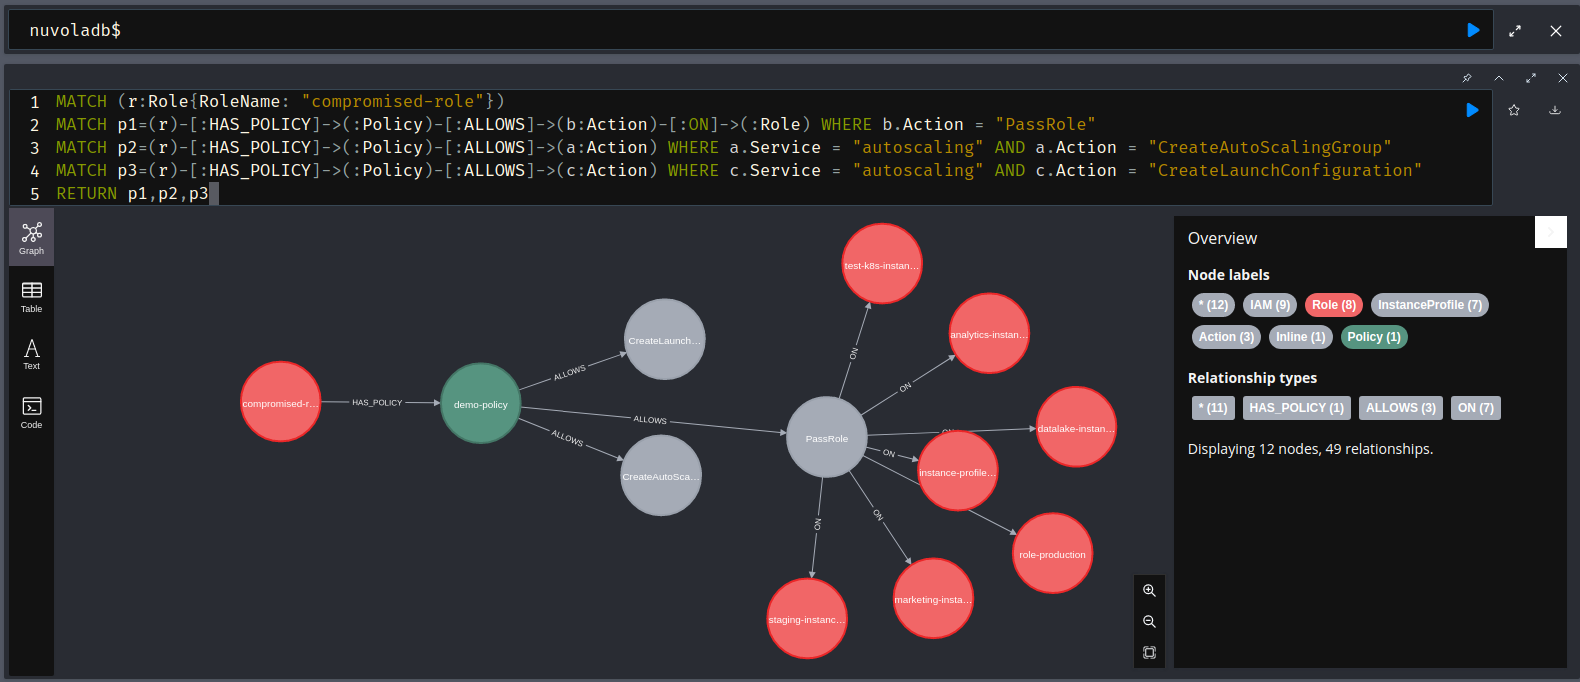 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
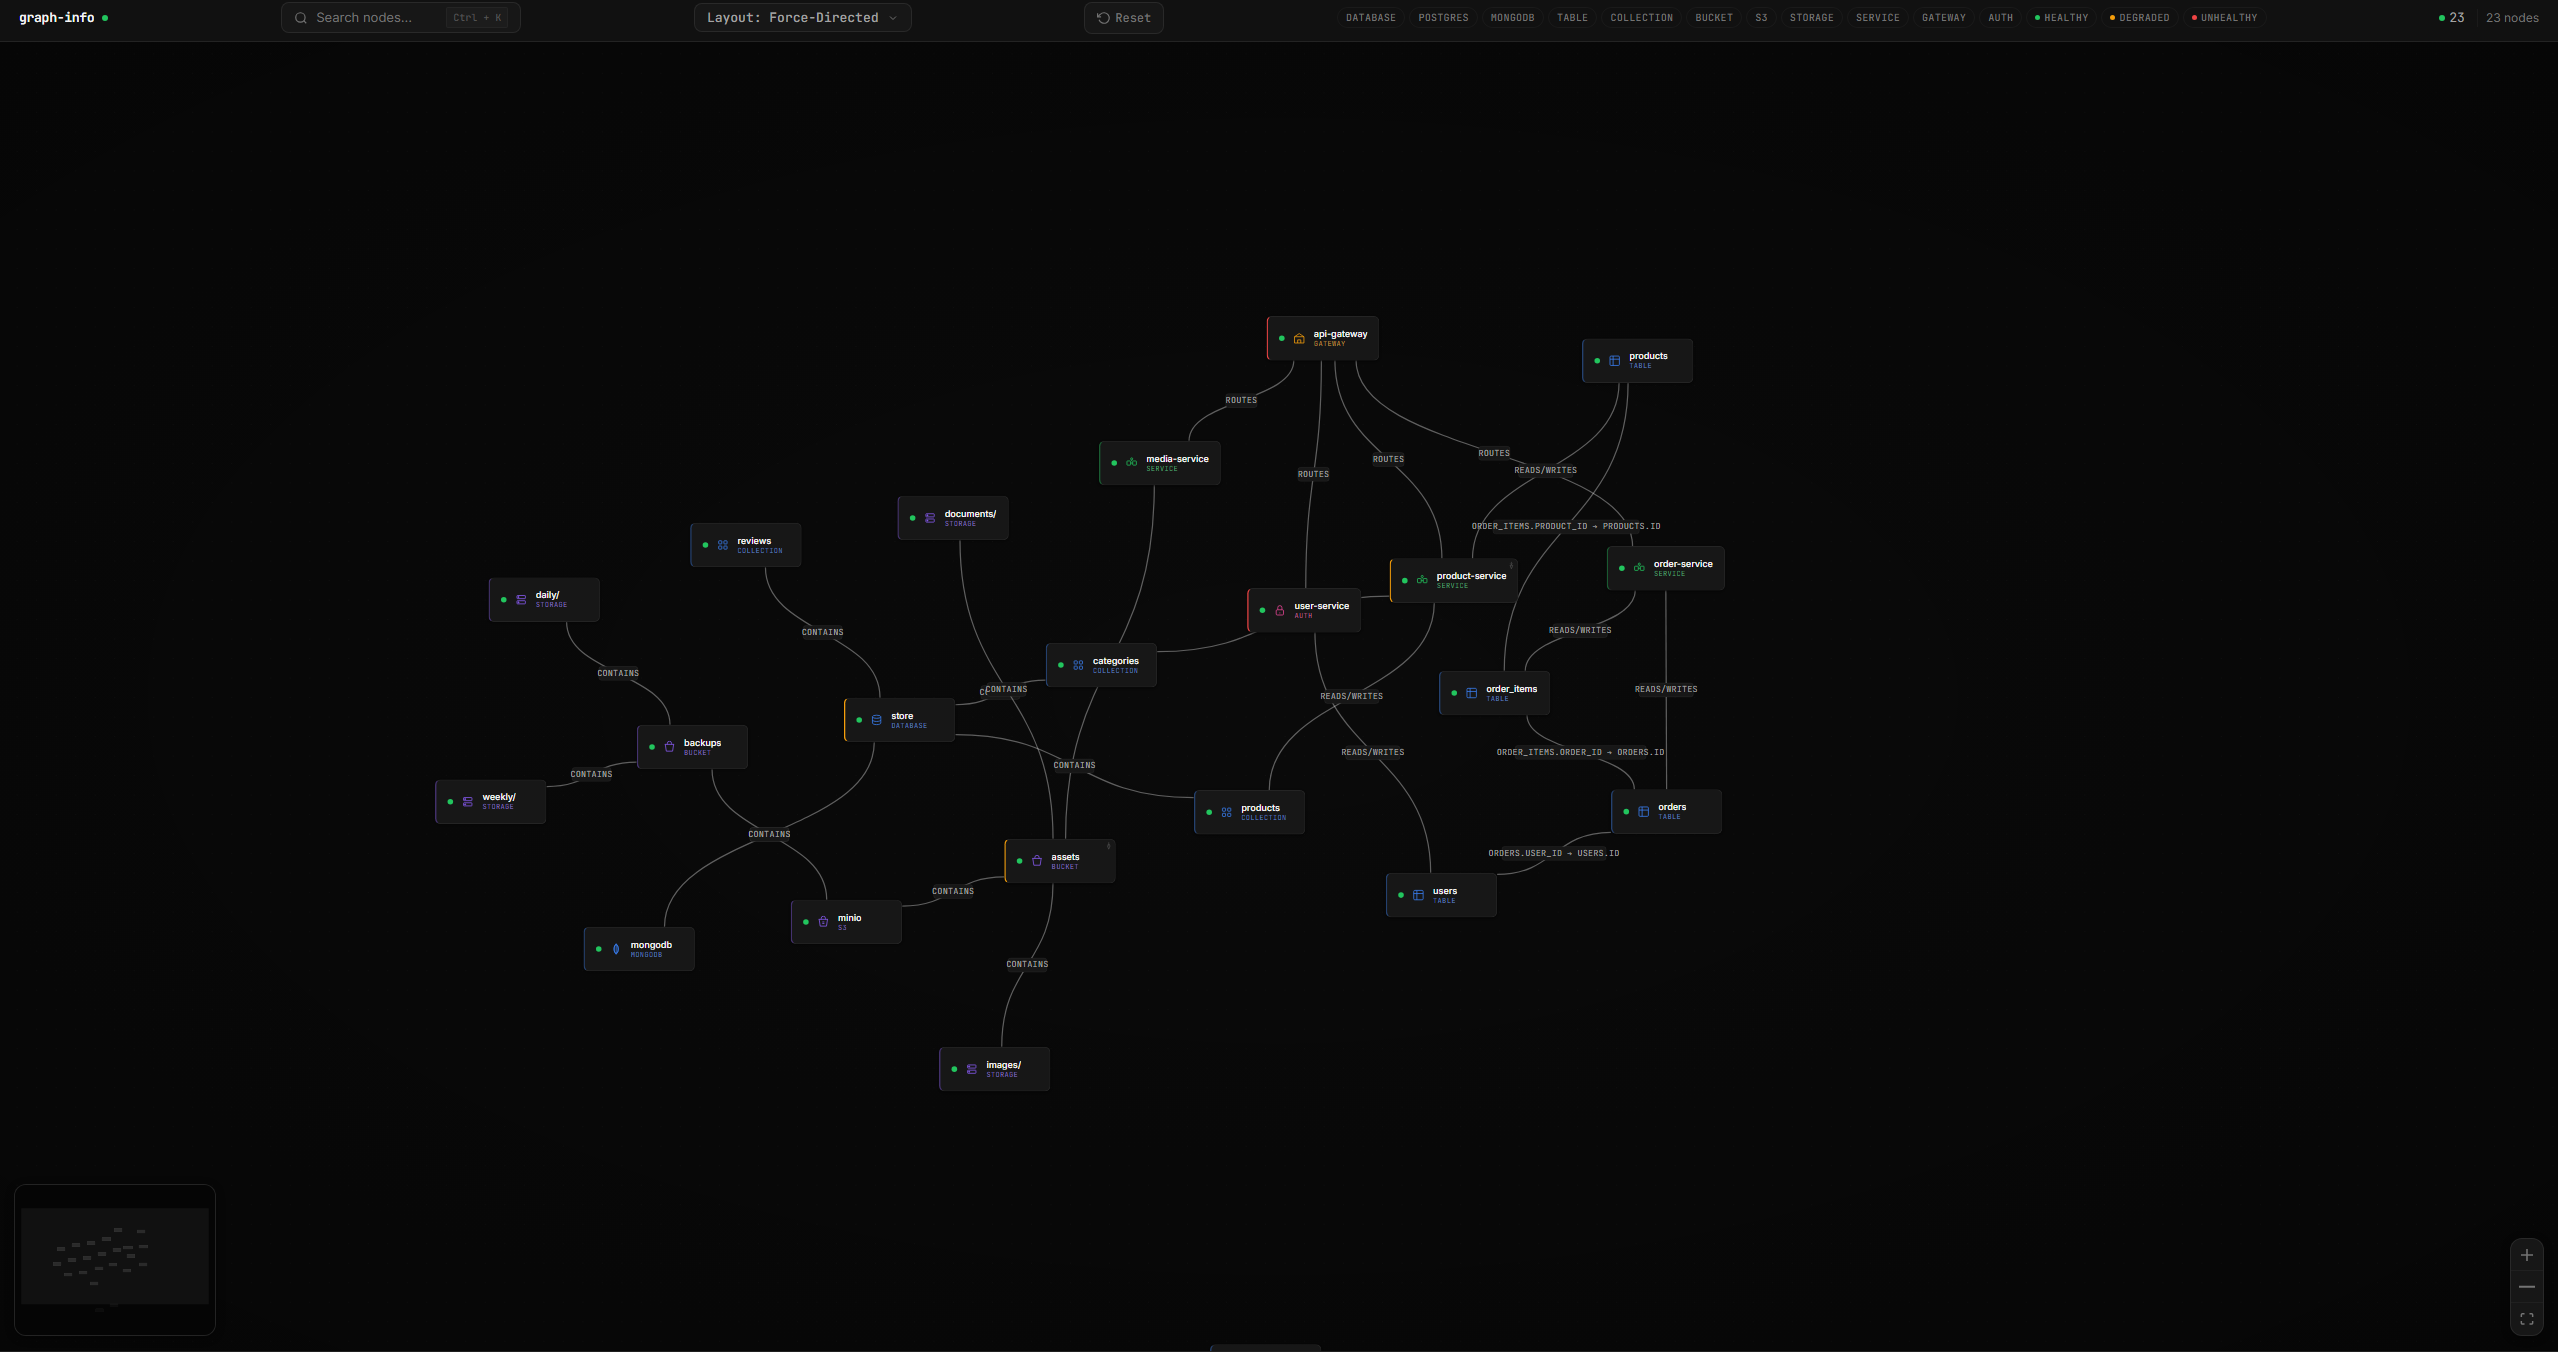 guilherme-grimm/graph-go
simply nodes and graphs
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
 netspi/microburst
A collection of scripts for assessing Microsoft Azure security
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 bishopfox/cirro-azcli-ext
Azure CLI extension for Cirro collection
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 abrahamsurf/sdwan-scanner-cve-2026-20127
Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026
 getanteon/anteon
eBPF-powered Kubernetes monitoring and performance testing platform that automatically generates service maps, tracks real-time metrics, and runs…
 natlas/natlas
Attack Surface Management since before Attack Surface Management was a thing