
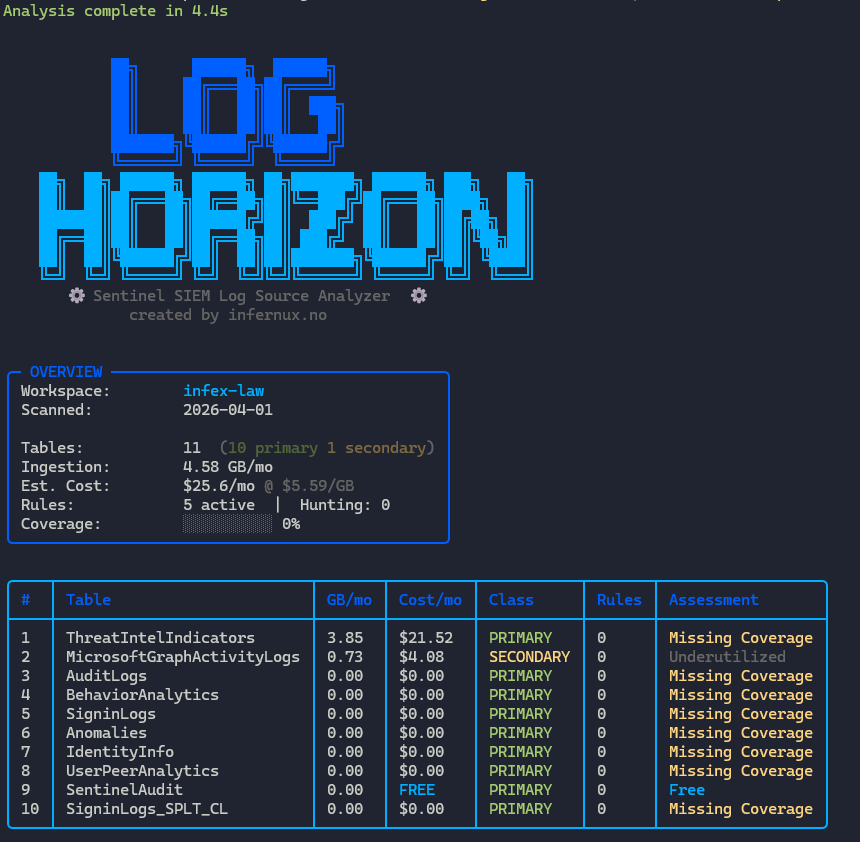
log-horizon
 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
cloud-infrastructure-securitycloud-securityconfiguration-auditing+4
312 days ago
lnfernux/log-horizonMicrosoft Sentinel SIEM Log Source Analyzer
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
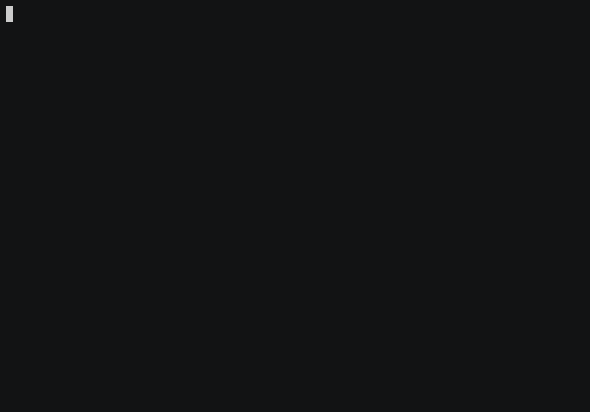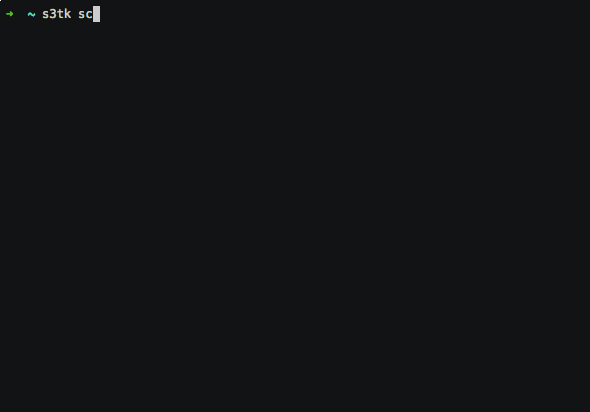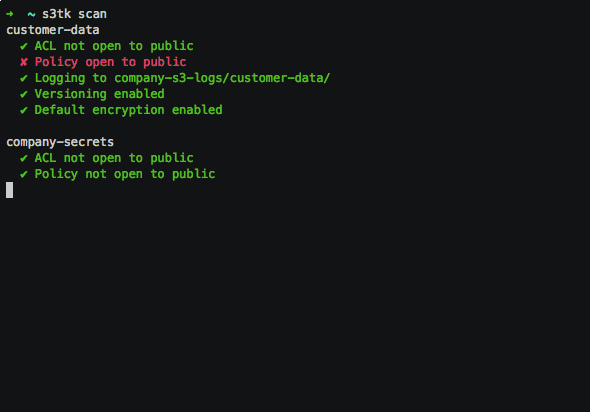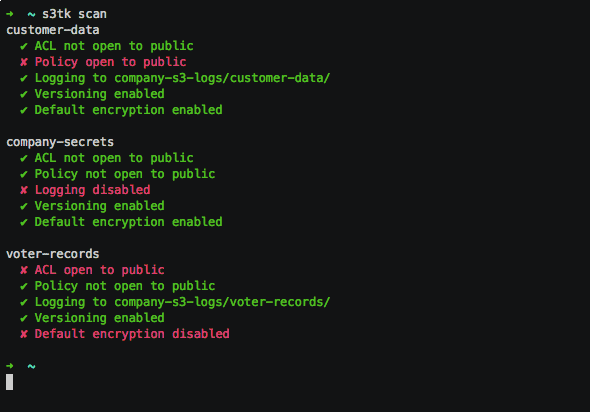 ankane/s3tk
A security toolkit for Amazon S3
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator