
boundary
 hashicorp/boundary
Boundary enables identity-based access management for dynamic infrastructure.
authentication-authorizationcloud-infrastructure-securityidentity-access-management+1
4.1k
hashicorp/boundaryBoundary enables identity-based access management for dynamic infrastructure.
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 chaosblade-io/chaosblade
An easy to use and powerful chaos engineering experiment toolkit.(阿里巴巴开源的一款简单易用、功能强大的混沌实验注入工具)
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 chaos-mesh/chaos-mesh
A Chaos Engineering Platform for Kubernetes.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
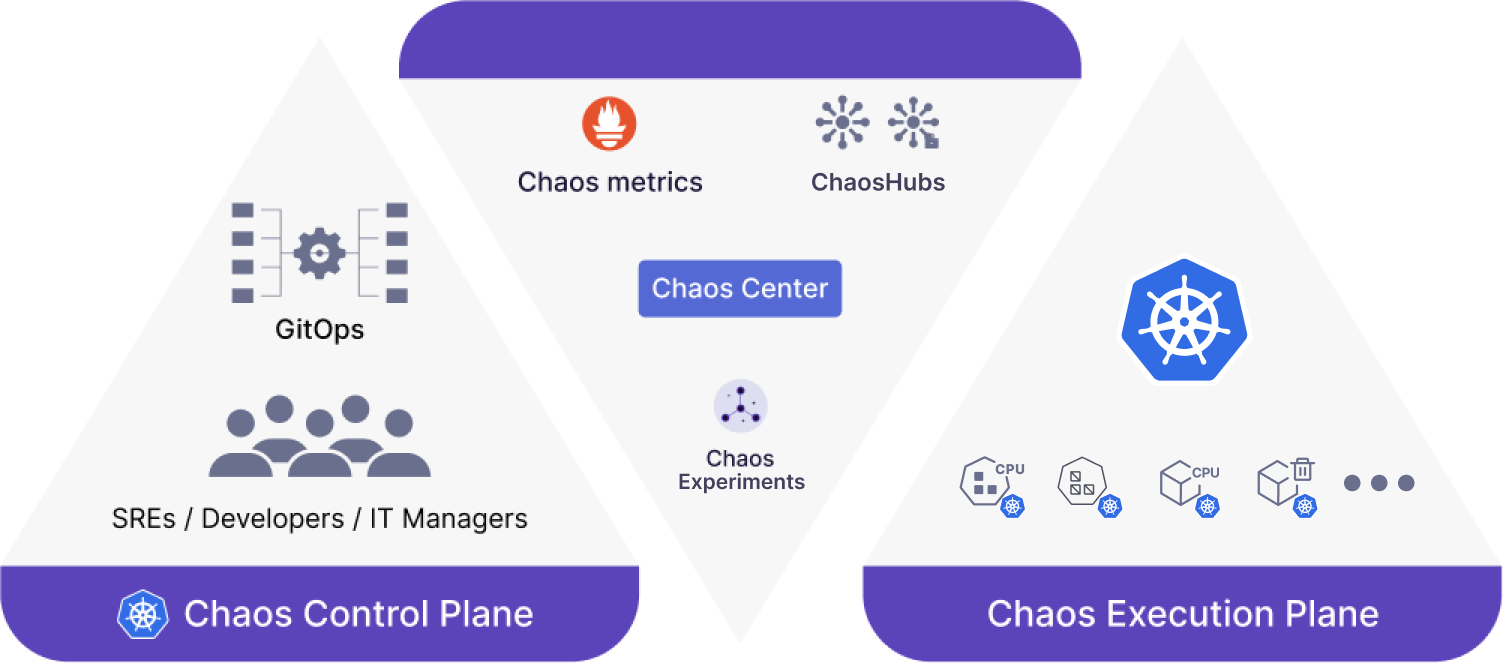 litmuschaos/litmus
Cloud-native chaos engineering platform for Kubernetes with fault injection, workflow orchestration, and steady-state validation to surface system…
 ooafa/bucketbuster
Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
 openbmc/bmcweb
A do everything Redfish, KVM, GUI, and DBus webserver for OpenBMC
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 elastic/agent-skills
Official Elastic Skills
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
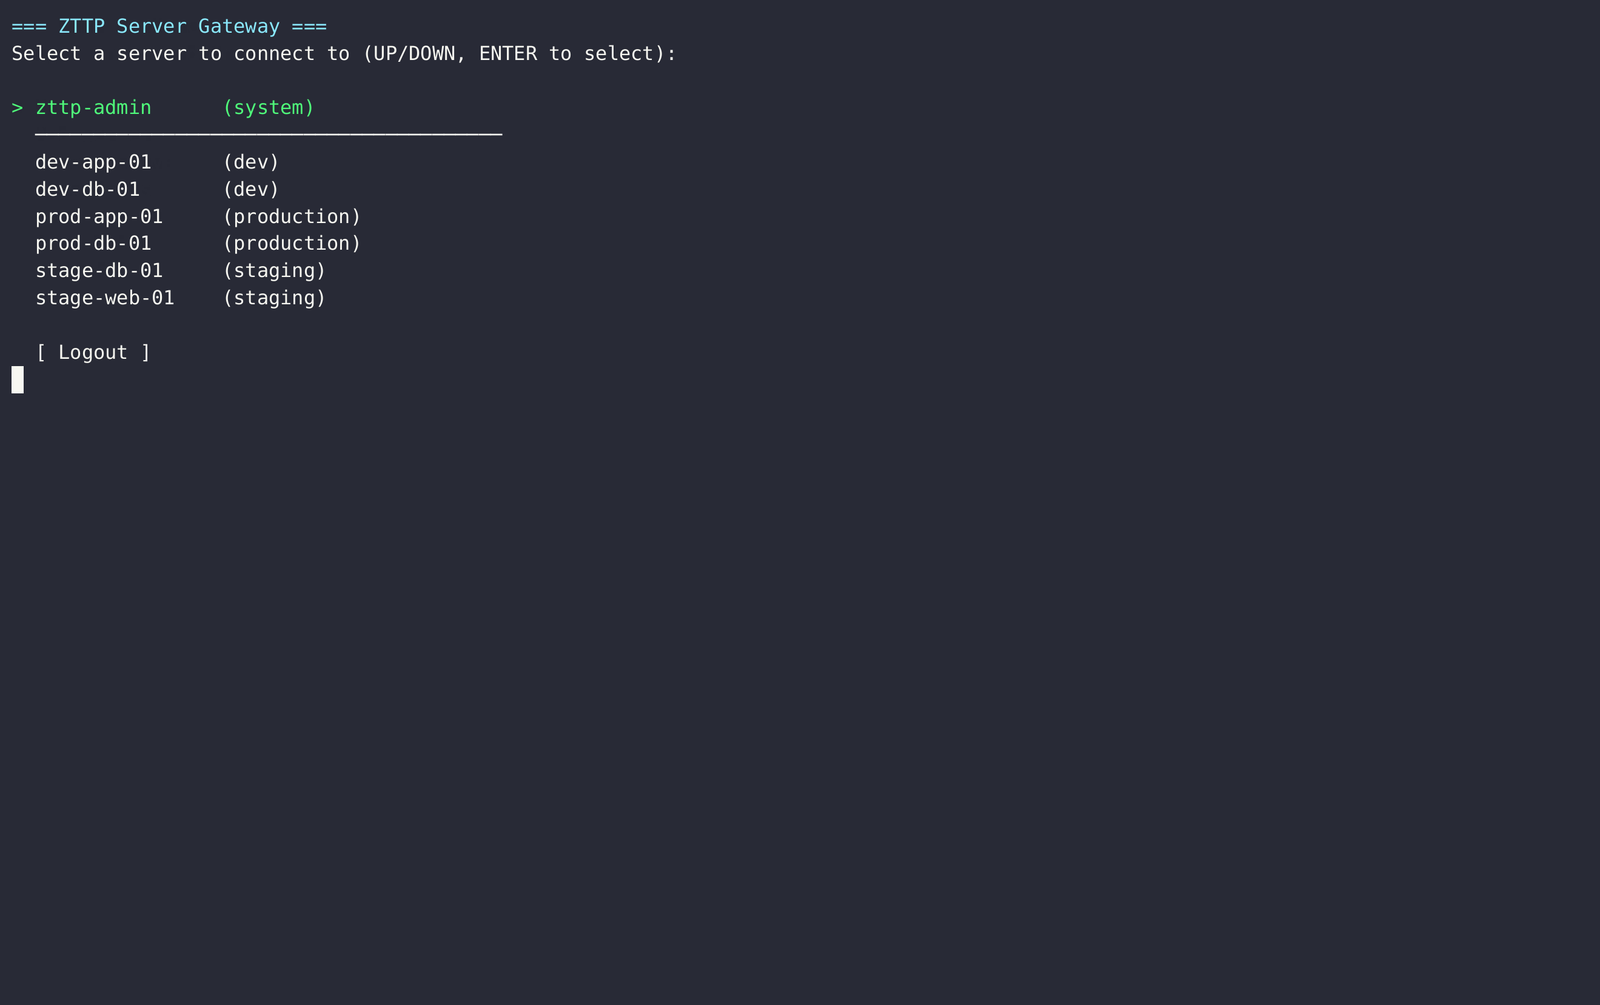
 nihal799/zttp
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…
 barun121/cve-2024-9264-in-grafana-11.x
Vulnerability Exploitation using tools Penetration Testing, Grafana, Docker, Kali Linux.
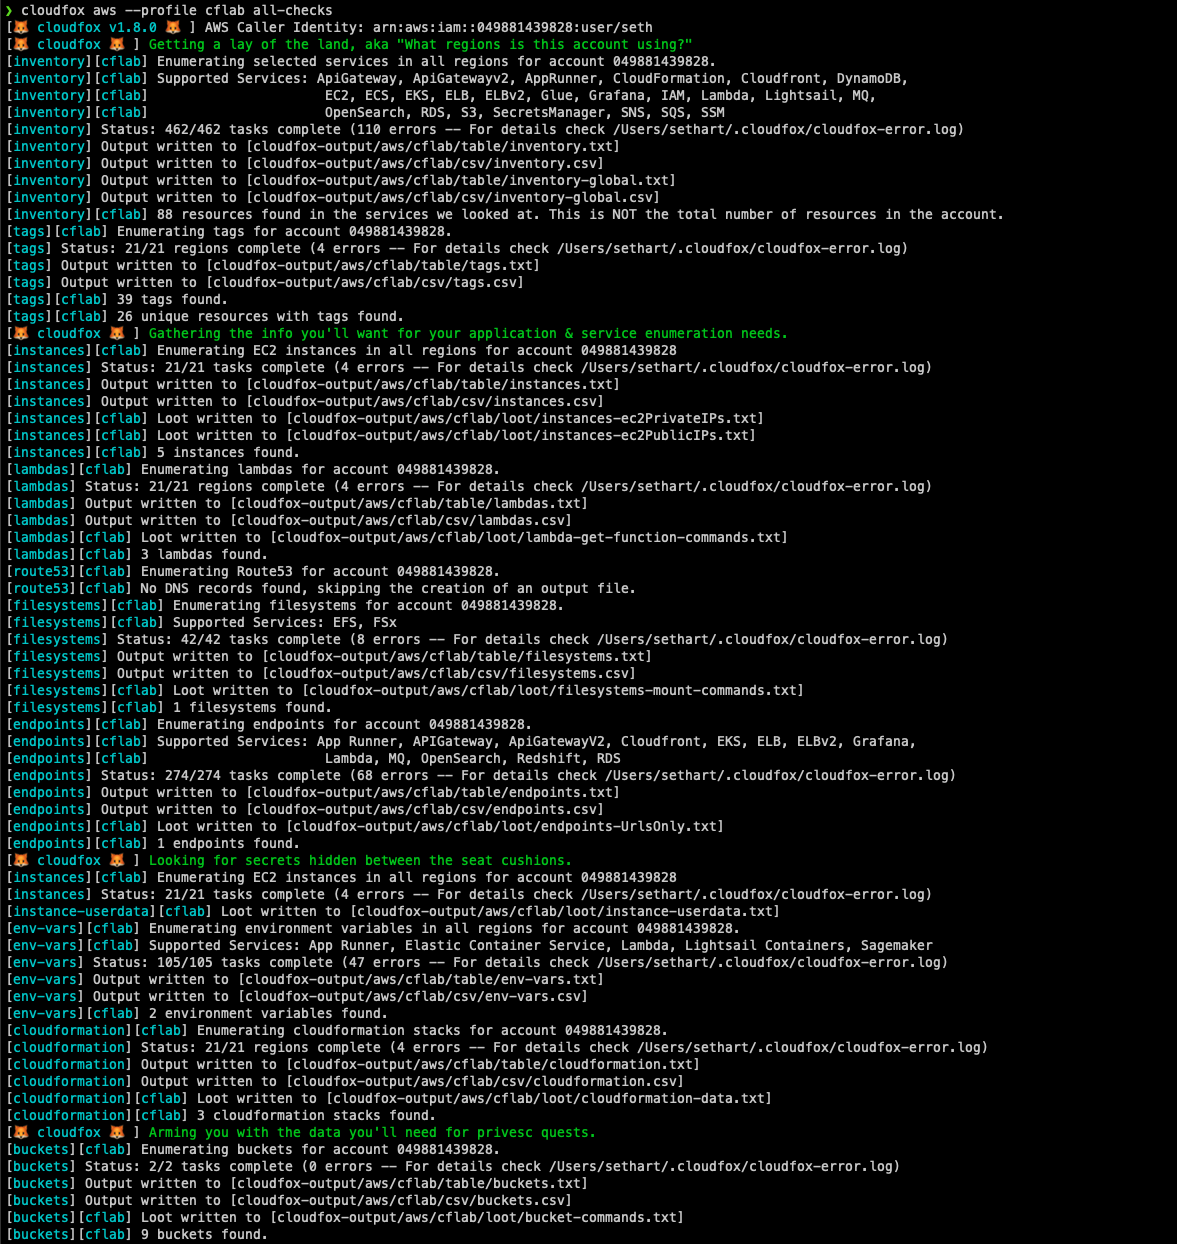 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…