

cnspec
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
cloud-infrastructure-securitycloud-securityconfiguration-auditing+6
442
mondoohq/cnspecAn open source, cloud-native security to protect everything from build to runtime
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
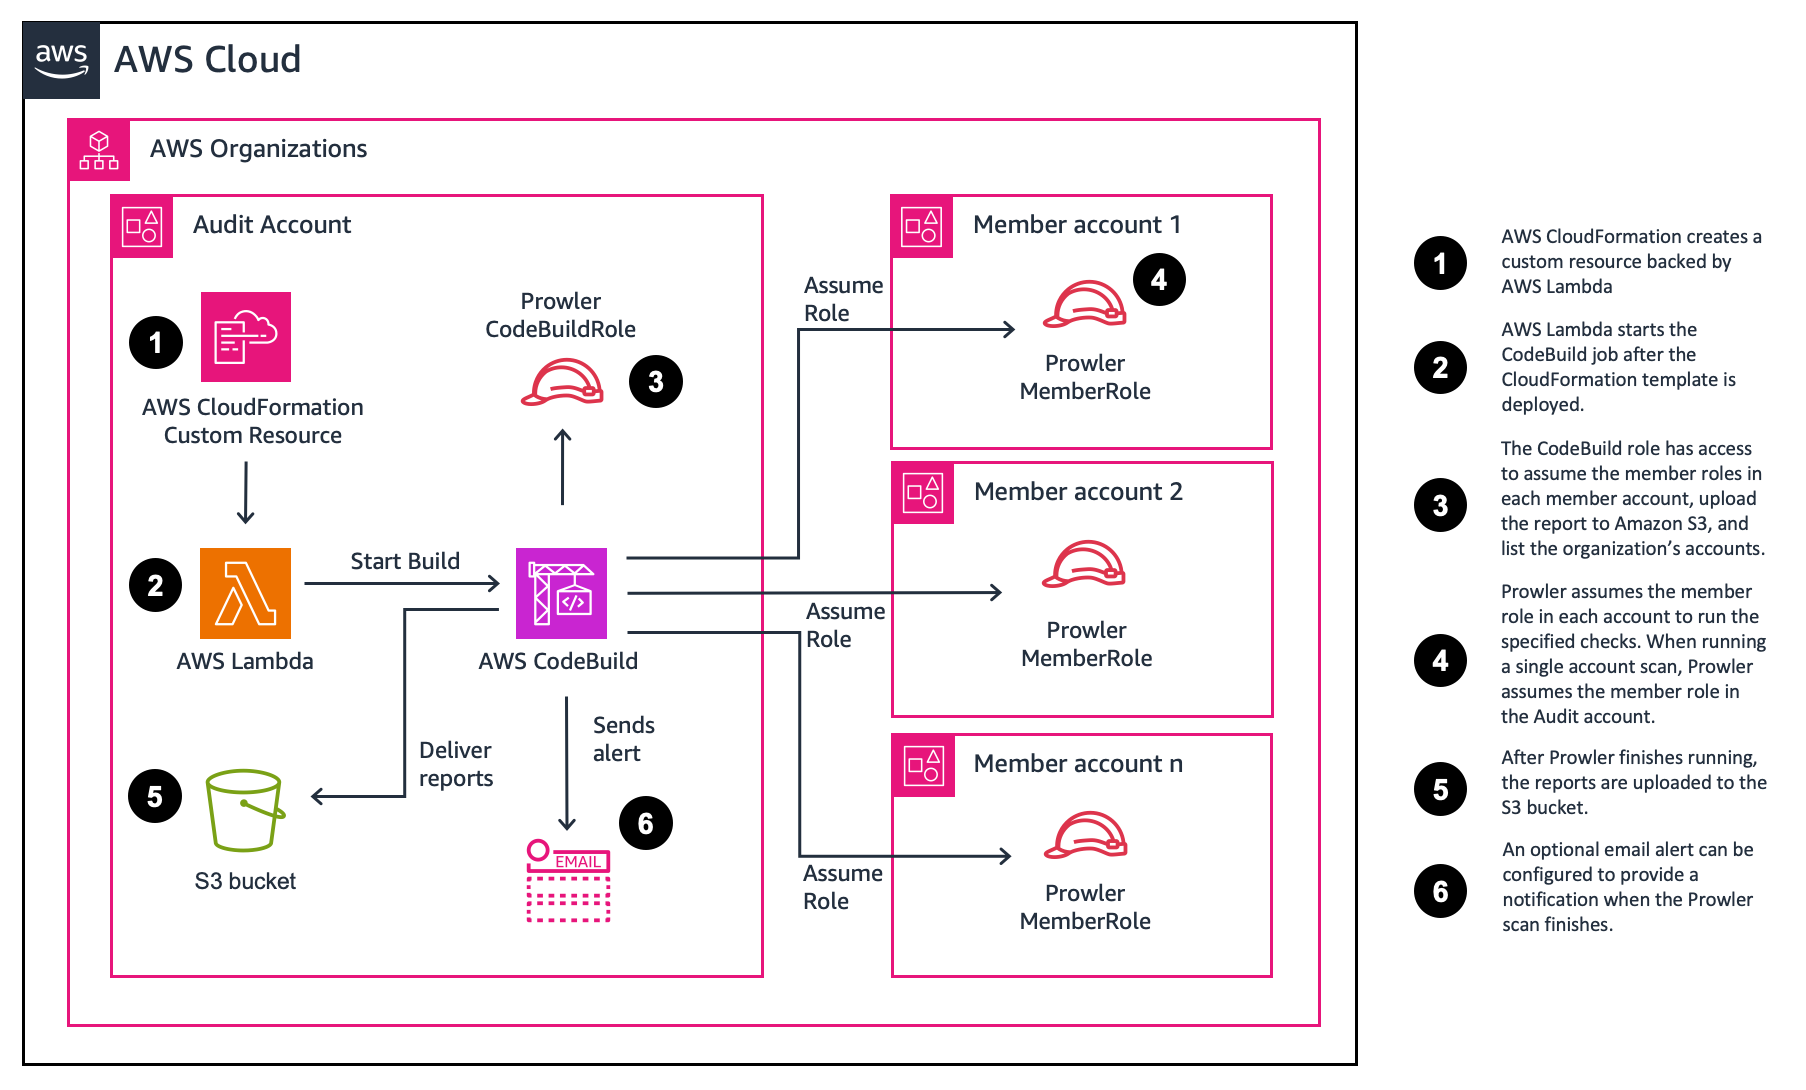 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
 rossengeorgiev/salt-security-backports
Salt security backports for CVE-2020-11651 & CVE-2020-11652
 shanika04/cloudfoundry_uaa
CVE-2016-4468
 natlas/natlas
Attack Surface Management since before Attack Surface Management was a thing
 wavestone-cdt/abaddon
Red team operations management platform automating infrastructure deployment, C2 setup, phishing campaigns, and reconnaissance with integrated tool…
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 shoucheng3/fabric8io__kubernetes-client_cve-2021-4178_5-0-2
Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…
 isagoakira/ghes-cve-scanner
Scans GitHub Enterprise Server instances for CVE-2026-3854 and CVE-2026-4821, providing version-based detection with batch scanning and multiple…
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
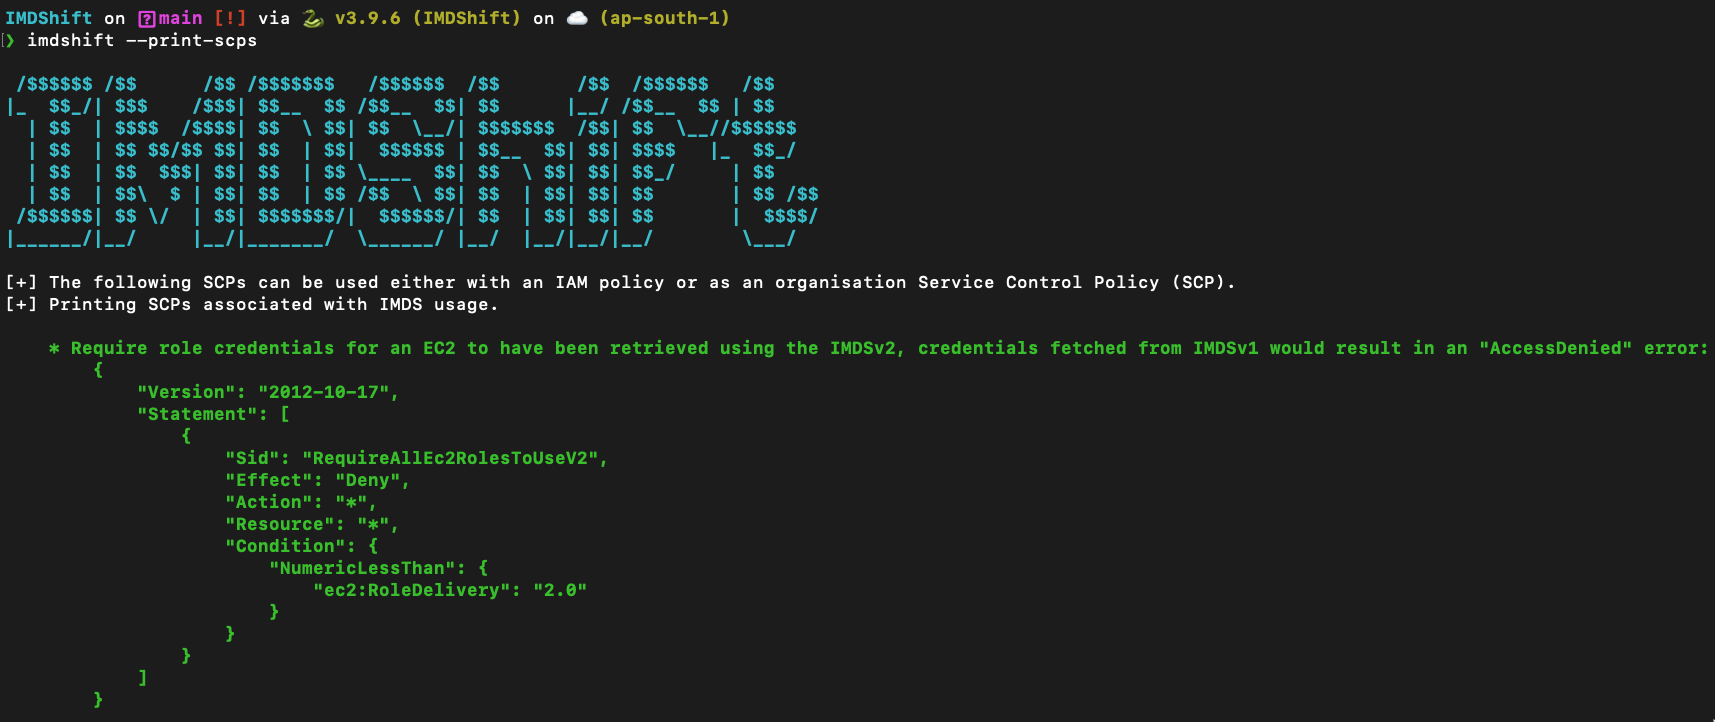 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 mitiga/log4shell-cloud-scanner
we are providing DevOps and security teams script to identify cloud workloads that may be vulnerable to the Log4j vulnerability(CVE-2021-44228) in…
 pop3ret/awsome-pentesting
My cheatsheet notes to pentest AWS infrastructure