
caeruleus
 praetorian-inc/caeruleus
Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…
bluetooth-securityfuzzinghardware-iot-security+8
60
praetorian-inc/caeruleusSingle Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 ymsniper/whisper_bully
Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
 hayzamjs/blueborne-cve-2017-1000251
Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 saruman9/ble_connect_rust
Norton Core Secure WiFi PoC (CVE-2018-5234) on Rust.
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…
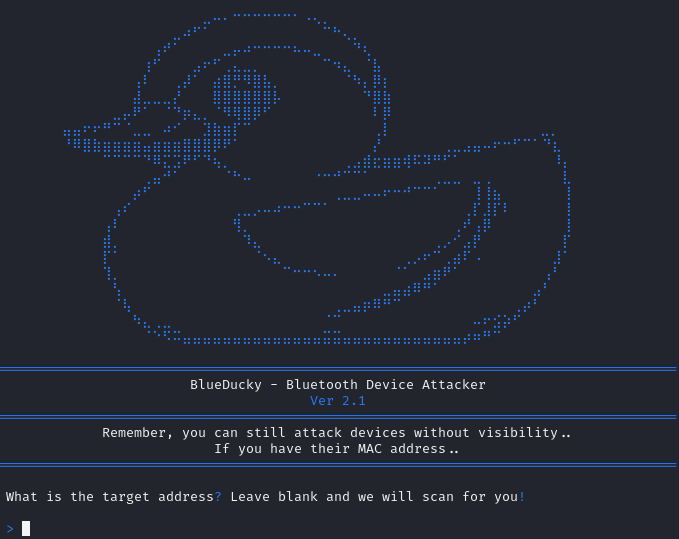 pentestfunctions/blueducky
🚨 CVE-2023-45866 - BlueDucky Implementation (Using DuckyScript) 🔓 Unauthenticated Peering Leading to Code Execution (Using HID Keyboard)
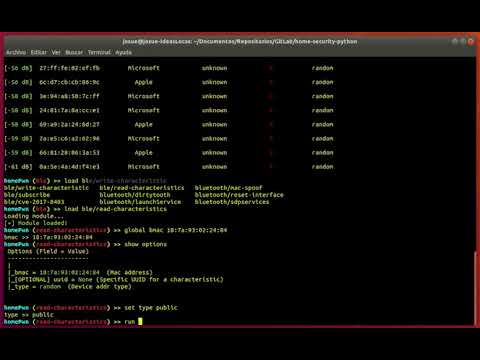 telefonica/homepwn
HomePwn - Swiss Army Knife for Pentesting of IoT Devices
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
 kevinmitchell-oswp-cissp/cve-2023-52709-poc
PoC for 2023-52709 - TI Bluetooth stack can fail to generate a resolvable Random Private Address (RPA) leading to DoS for already bonded peer devices.
 cedric-martz/cve-2025-36911_scan
This script can be used to check if a Bluetooth device is vulnerable to CVE-2025-36911.
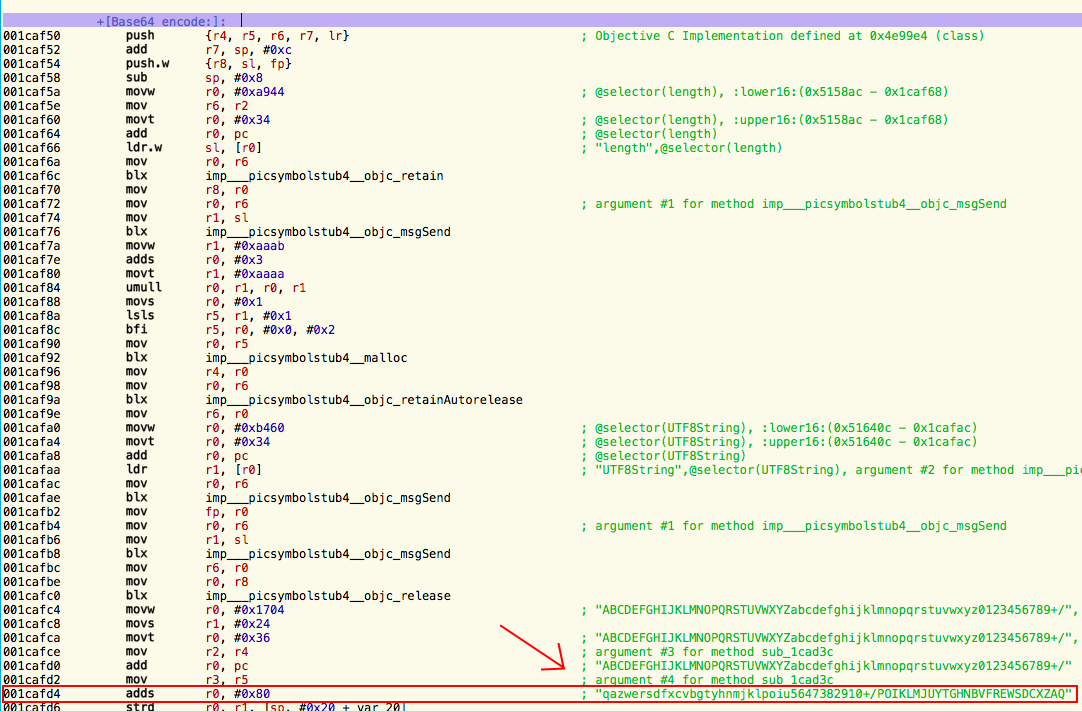 jasondoyle/komfy-switch-wifi-password-disclosure
Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…