
jackit
 insecurityofthings/jackit
Exploit tool for MouseJack vulnerability enabling keystroke injection and mouse hijacking over nRF24L01 wireless dongles. Supports multiple Microsoft…
bluetooth-securityexploitationhardware-iot-security+3
899
insecurityofthings/jackitExploit tool for MouseJack vulnerability enabling keystroke injection and mouse hijacking over nRF24L01 wireless dongles. Supports multiple Microsoft…
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 niranjangaire1995/cve-2025-46018-csc-pay-mobile-app-payment-authentication-bypass
Disclosure of CVE-2025-46018: A Bluetooth-based payment bypass vulnerability in CSC Pay Mobile App v2.19.4"
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 seemoo-lab/fitness-app
BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
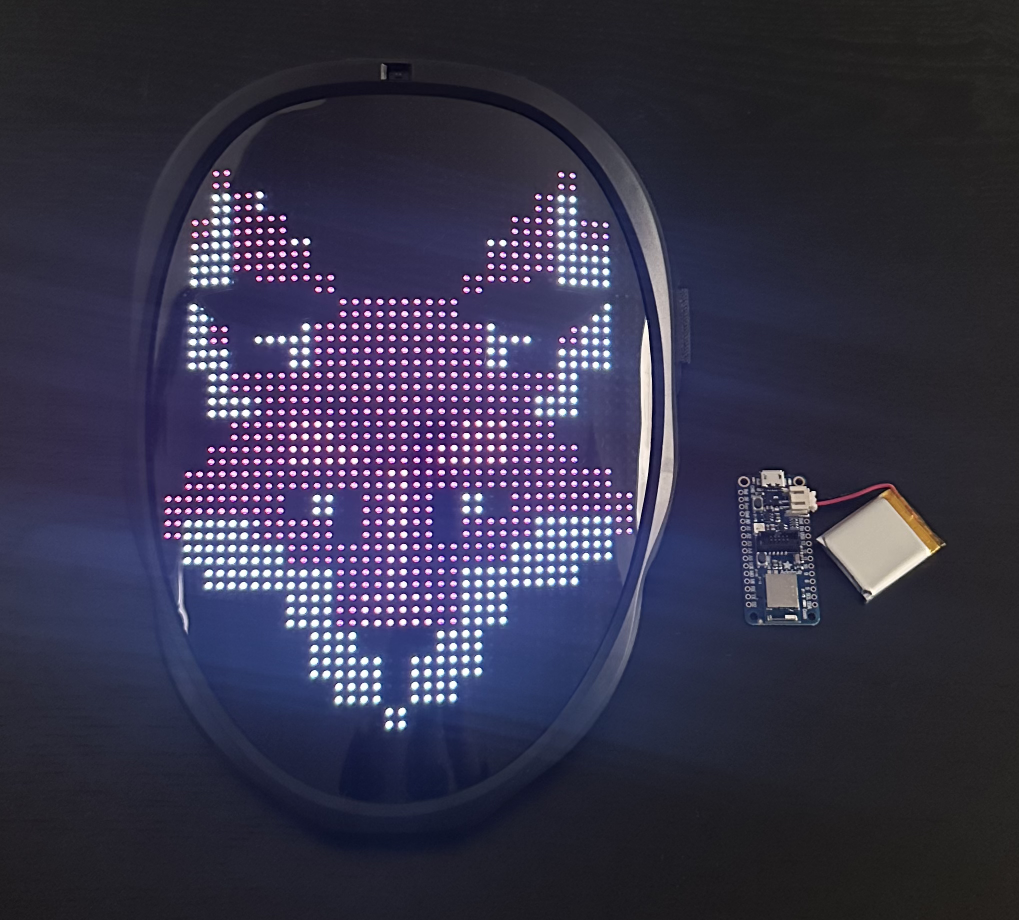 bishopfox/shining-mask
BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…
 aalex954/whisperpair-poc-tool
A security research tool that identifies and demonstrates the CVE-2025-36911: Fast Pair Pairing Mode Bypass vulnerability
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…
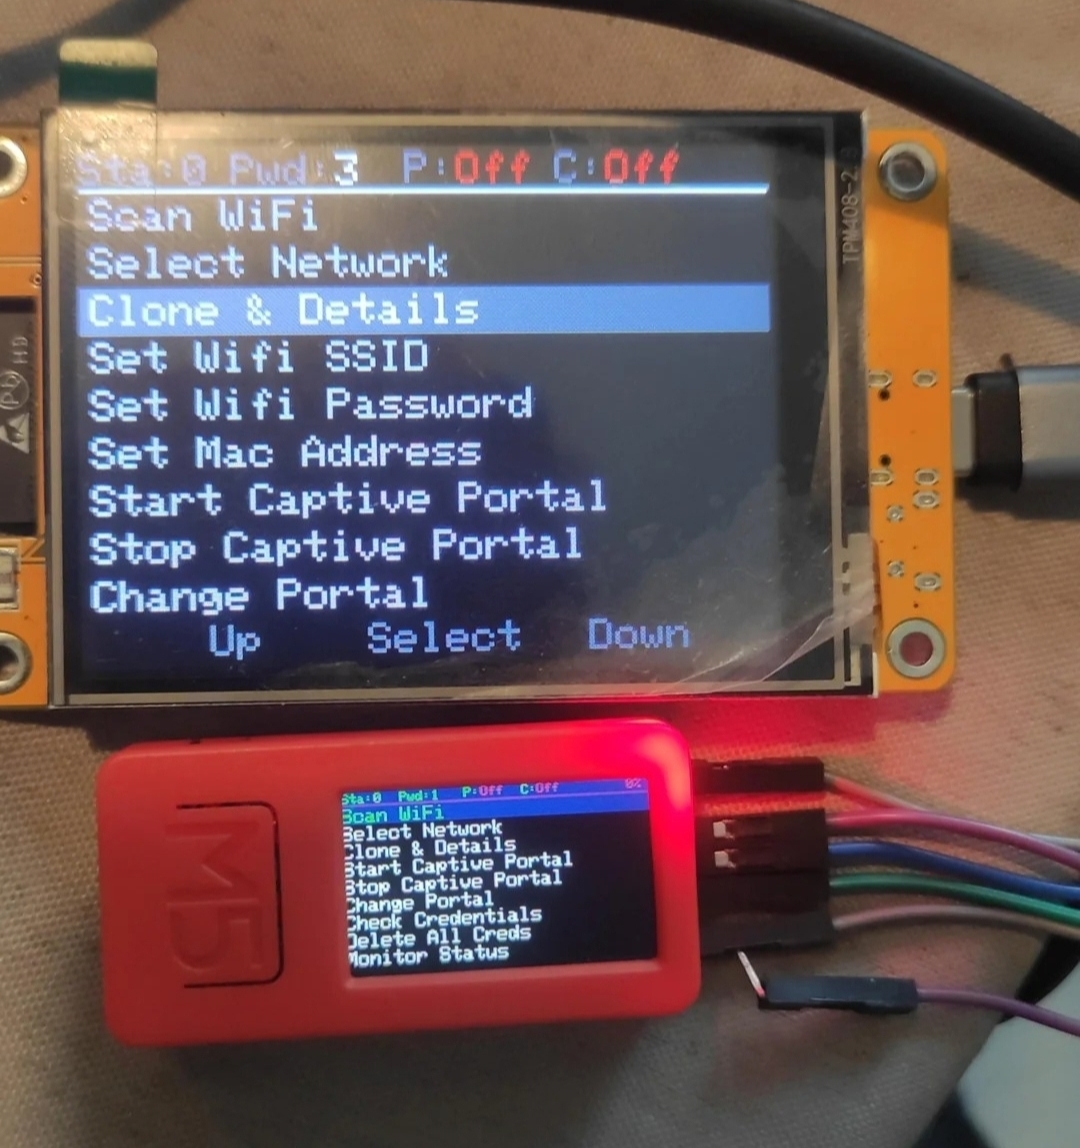 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 ymsniper/whisper_bully
Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)