Bluetooth-Attacks-CVE-2025-27840

Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth

Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth

DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306

Proof-of-concept exploit for BlueBorne vulnerability CVE-2017-1000251 targeting Bluetooth stack. Demonstrates remote code execution possibility. For…

Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.

BLE-based HTTP proxy system routing browser traffic through an iOS device. Supports HTTP/HTTPS, data compression, and mock mode for testing without…

Details of CVE-2020-14292

BLE Man-in-the-Middle framework that intercepts, replays, and modifies GATT traffic between Bluetooth Smart devices and mobile apps via a web-based…

A Node.js package for BLE (Bluetooth Low Energy) security assessment using Man-in-the-Middle and other attacks

HomePwn - Swiss Army Knife for Pentesting of IoT Devices

BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…

Hakku Framework penetration testing

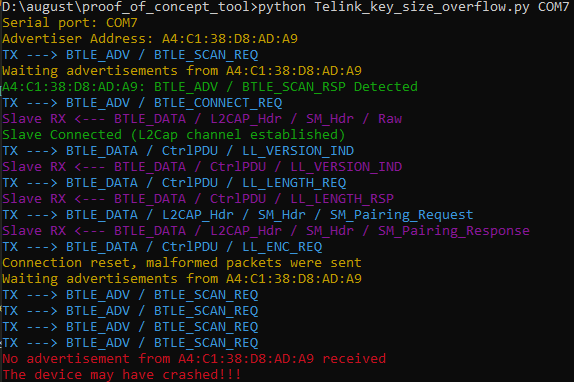
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.

Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…

CVE-2017-0785 BlueBorne PoC

Scan/Exploit Blueborne CVE-2017-0785

Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)

Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.

Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.