

internalblue
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
bluetooth-securityembedded-systems-securityfirmware-analysis+6
791
seemoo-lab/internalblueBluetooth experimentation framework for Broadcom and Cypress chips.
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 insecurityofthings/uc_mousejack
Mousejack for ATmega32u4
 whad-team/whad-client
Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…
 souravbaghz/radareeye
Tool for especially scanning nearby devices and execute a given command on its own system while the target device comes in range.
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
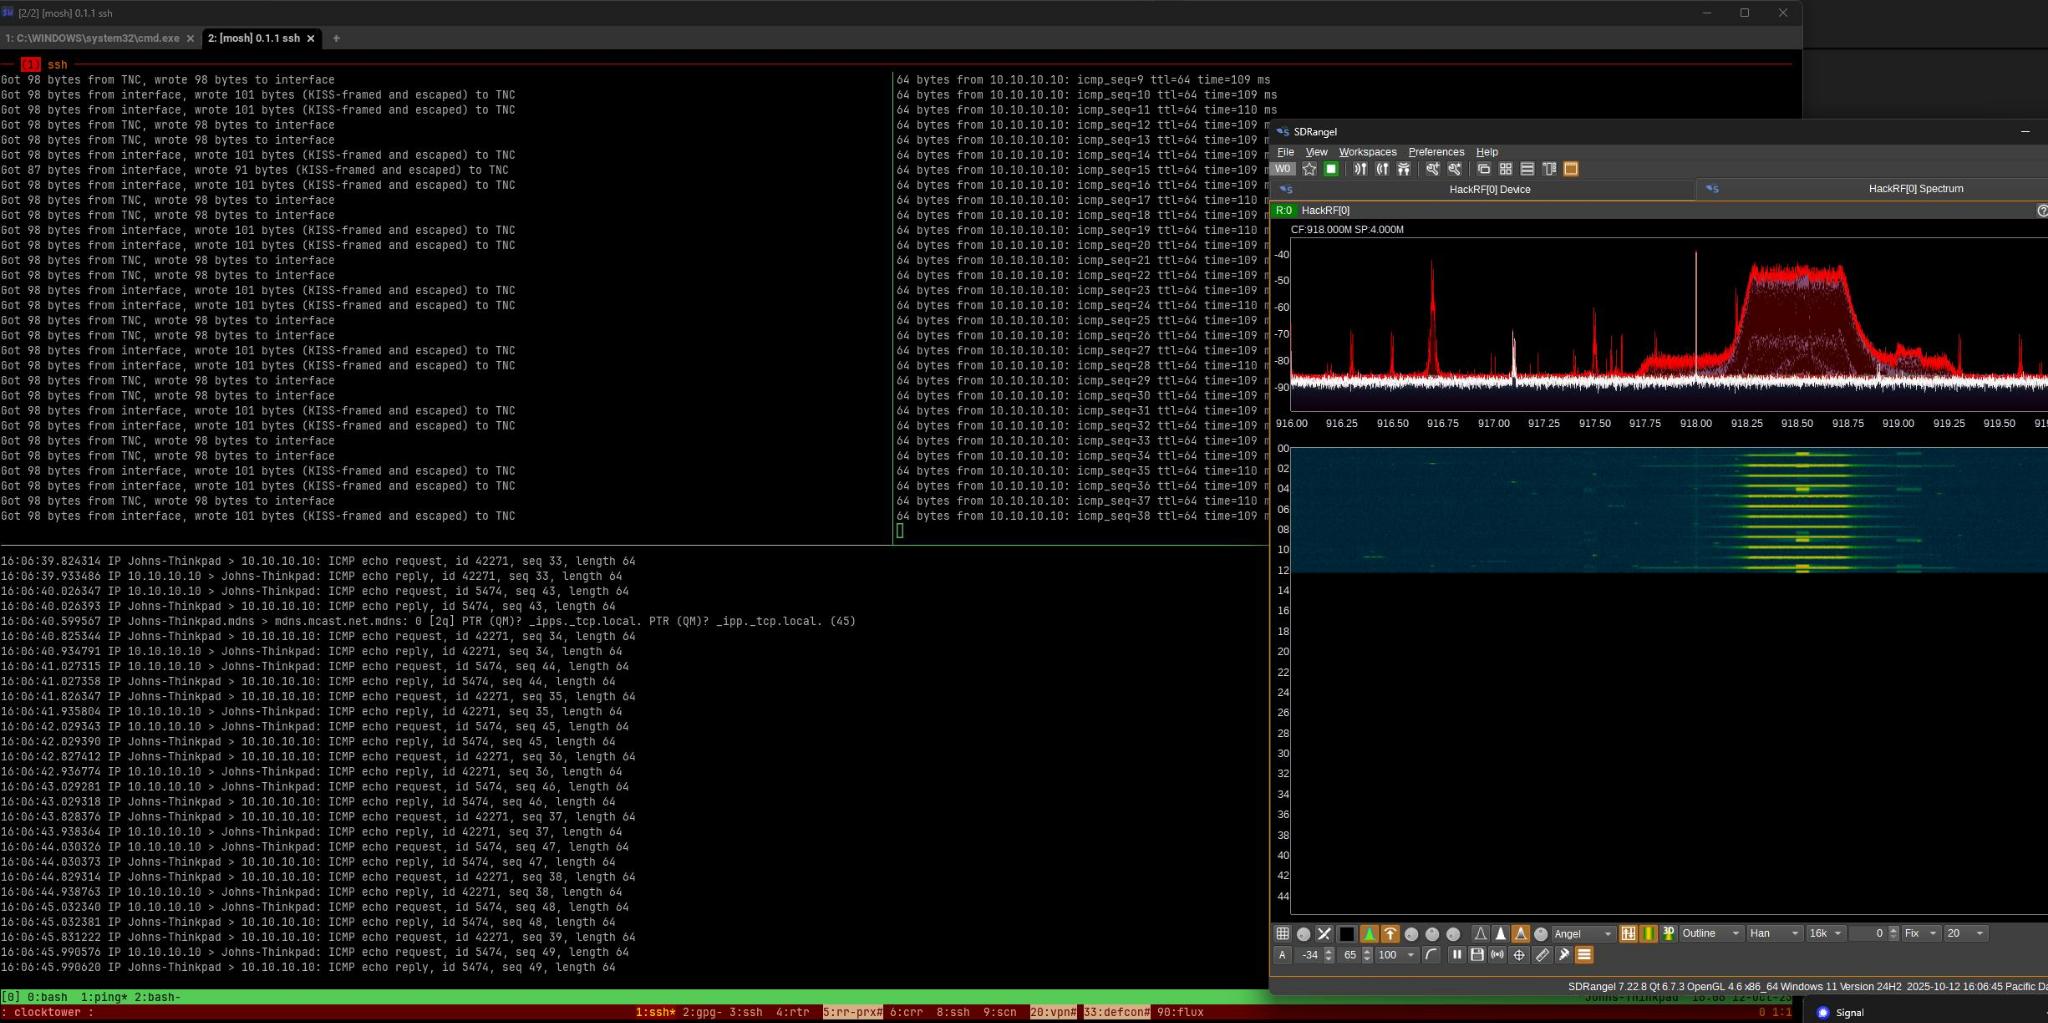 datapartyjs/meshtnc
Firmware for converting consumer LoRa radios into KISS TNC modems with serial CLI, BLE packet sniffing, and APRS/AX.25 compatibility for packet radio…
 elevenpaths/dirtytooth-raspberrypi
Exploit the hack for IOS 11.1.2 and earlier to collect leaked information.
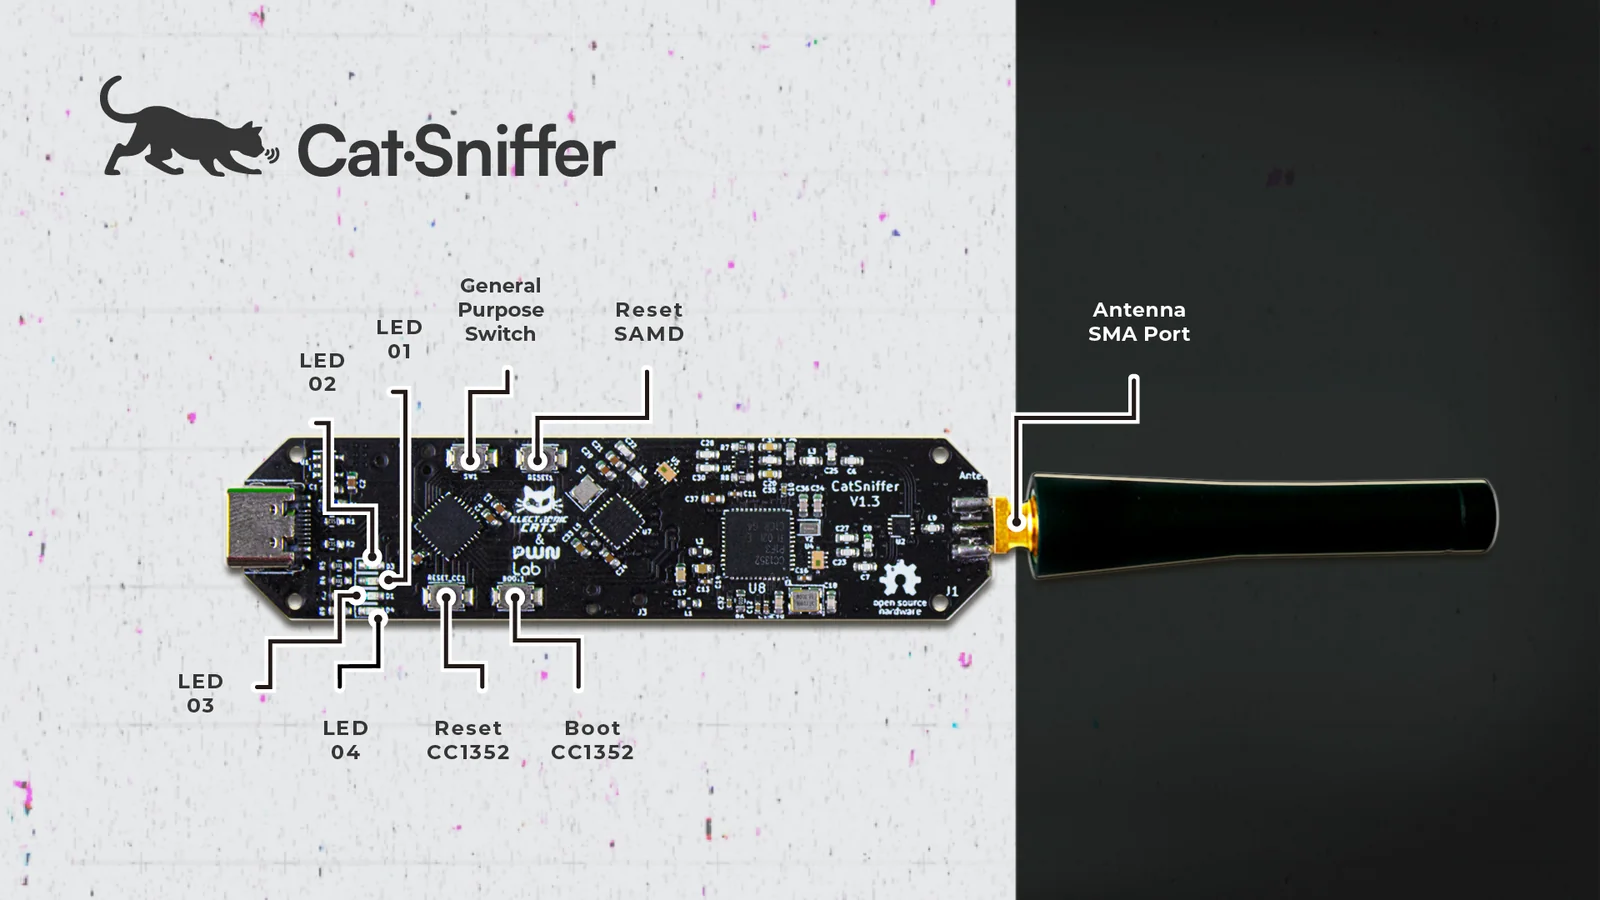 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
 redgridtactical/redgridlink
Retired September 27, 2026. Final v1.7.0 source retained for reference; no new store downloads or purchases. Development continues in Red Grid MGRS,…
 iotsrg/iot-pentest-devices-and-purpose
Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…
 seemoo-lab/fitness-app
BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…
 omerporze/brokentooth
POC for CVE-2018-4327
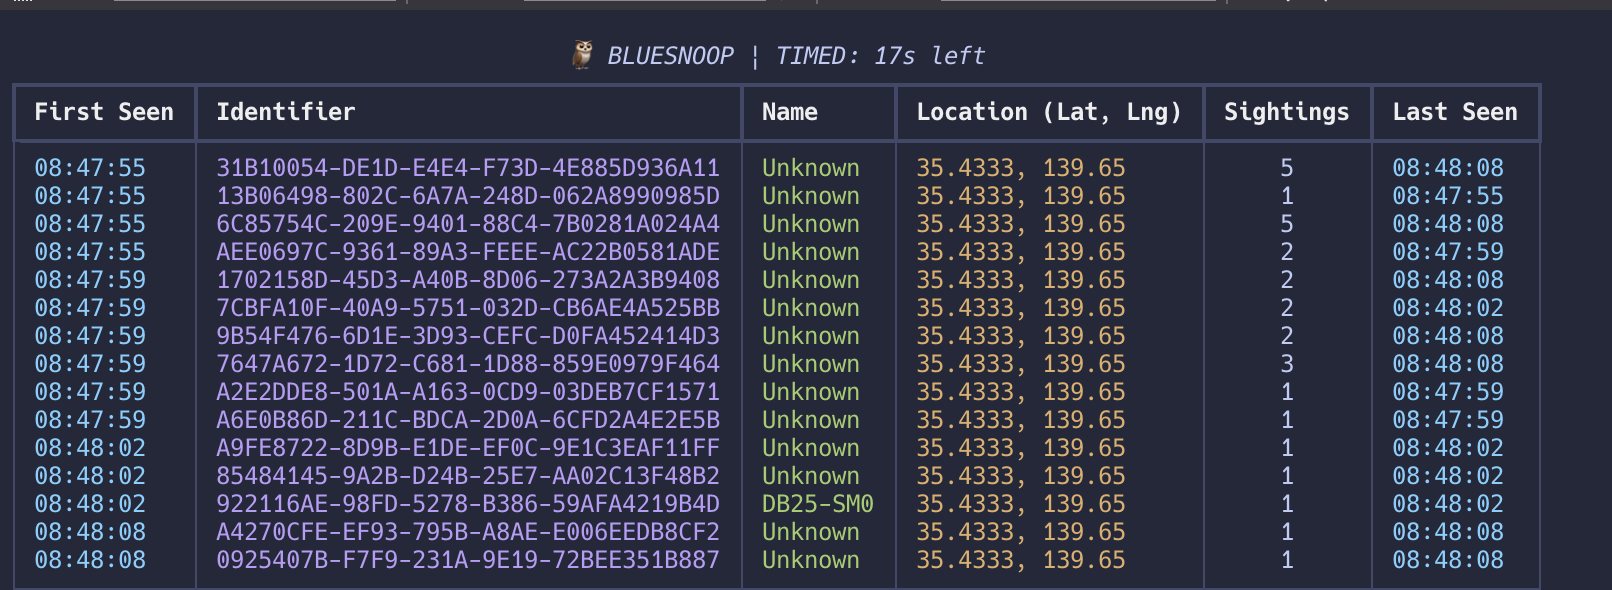 ang13t/bluesnoop
A TUI bluetooth utility for radar analysis and war driving 🦉
 jasondoyle/google-nest-cam-bug-disclosures
PoC vulnerability disclosures for consumer IoT cameras, detailing BLE buffer overflow and WiFi disassociation attacks that can take devices offline.
 butterflyhack/cve-2019-10207
PoC for CVE-2019-10207