
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
 pieterbork/blueborne
Scan/Exploit Blueborne CVE-2017-0785
 ymsniper/whisper_bully
Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
 hayzamjs/blueborne-cve-2017-1000251
Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 securelayer7/pwnfb50
:unlock: transfer ownership of any FB50 smart lock to yourself (CVE-2019-13143)
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 pivotchip/frostedfastpair
WhisperPair (CVE-2025-36911) POC for ESP32 device
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 phuchaudeveloper/badblue
CVE-2024-21306 BadBlue implementation (Using DuckyScript)
 aalex954/whisperpair-poc-tool
A security research tool that identifies and demonstrates the CVE-2025-36911: Fast Pair Pairing Mode Bypass vulnerability
 kevinmitchell-oswp-cissp/cve-2023-52709-poc
PoC for 2023-52709 - TI Bluetooth stack can fail to generate a resolvable Random Private Address (RPA) leading to DoS for already bonded peer devices.
 keldnorman/cve-2024-0230-blue
Helper script to POC of CVE-2024-0230 Bluetooth
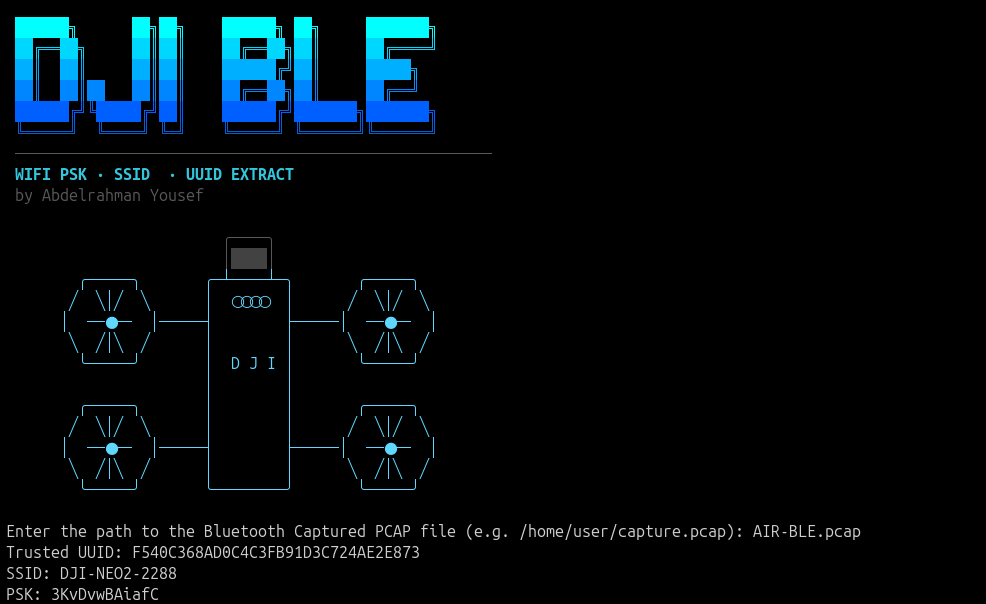 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 coleshelly/bandexploit
M1 Band Smart Watch Bluetooth Low Energy Exploit python script (CVE-2018-11631)
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.