

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.8k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
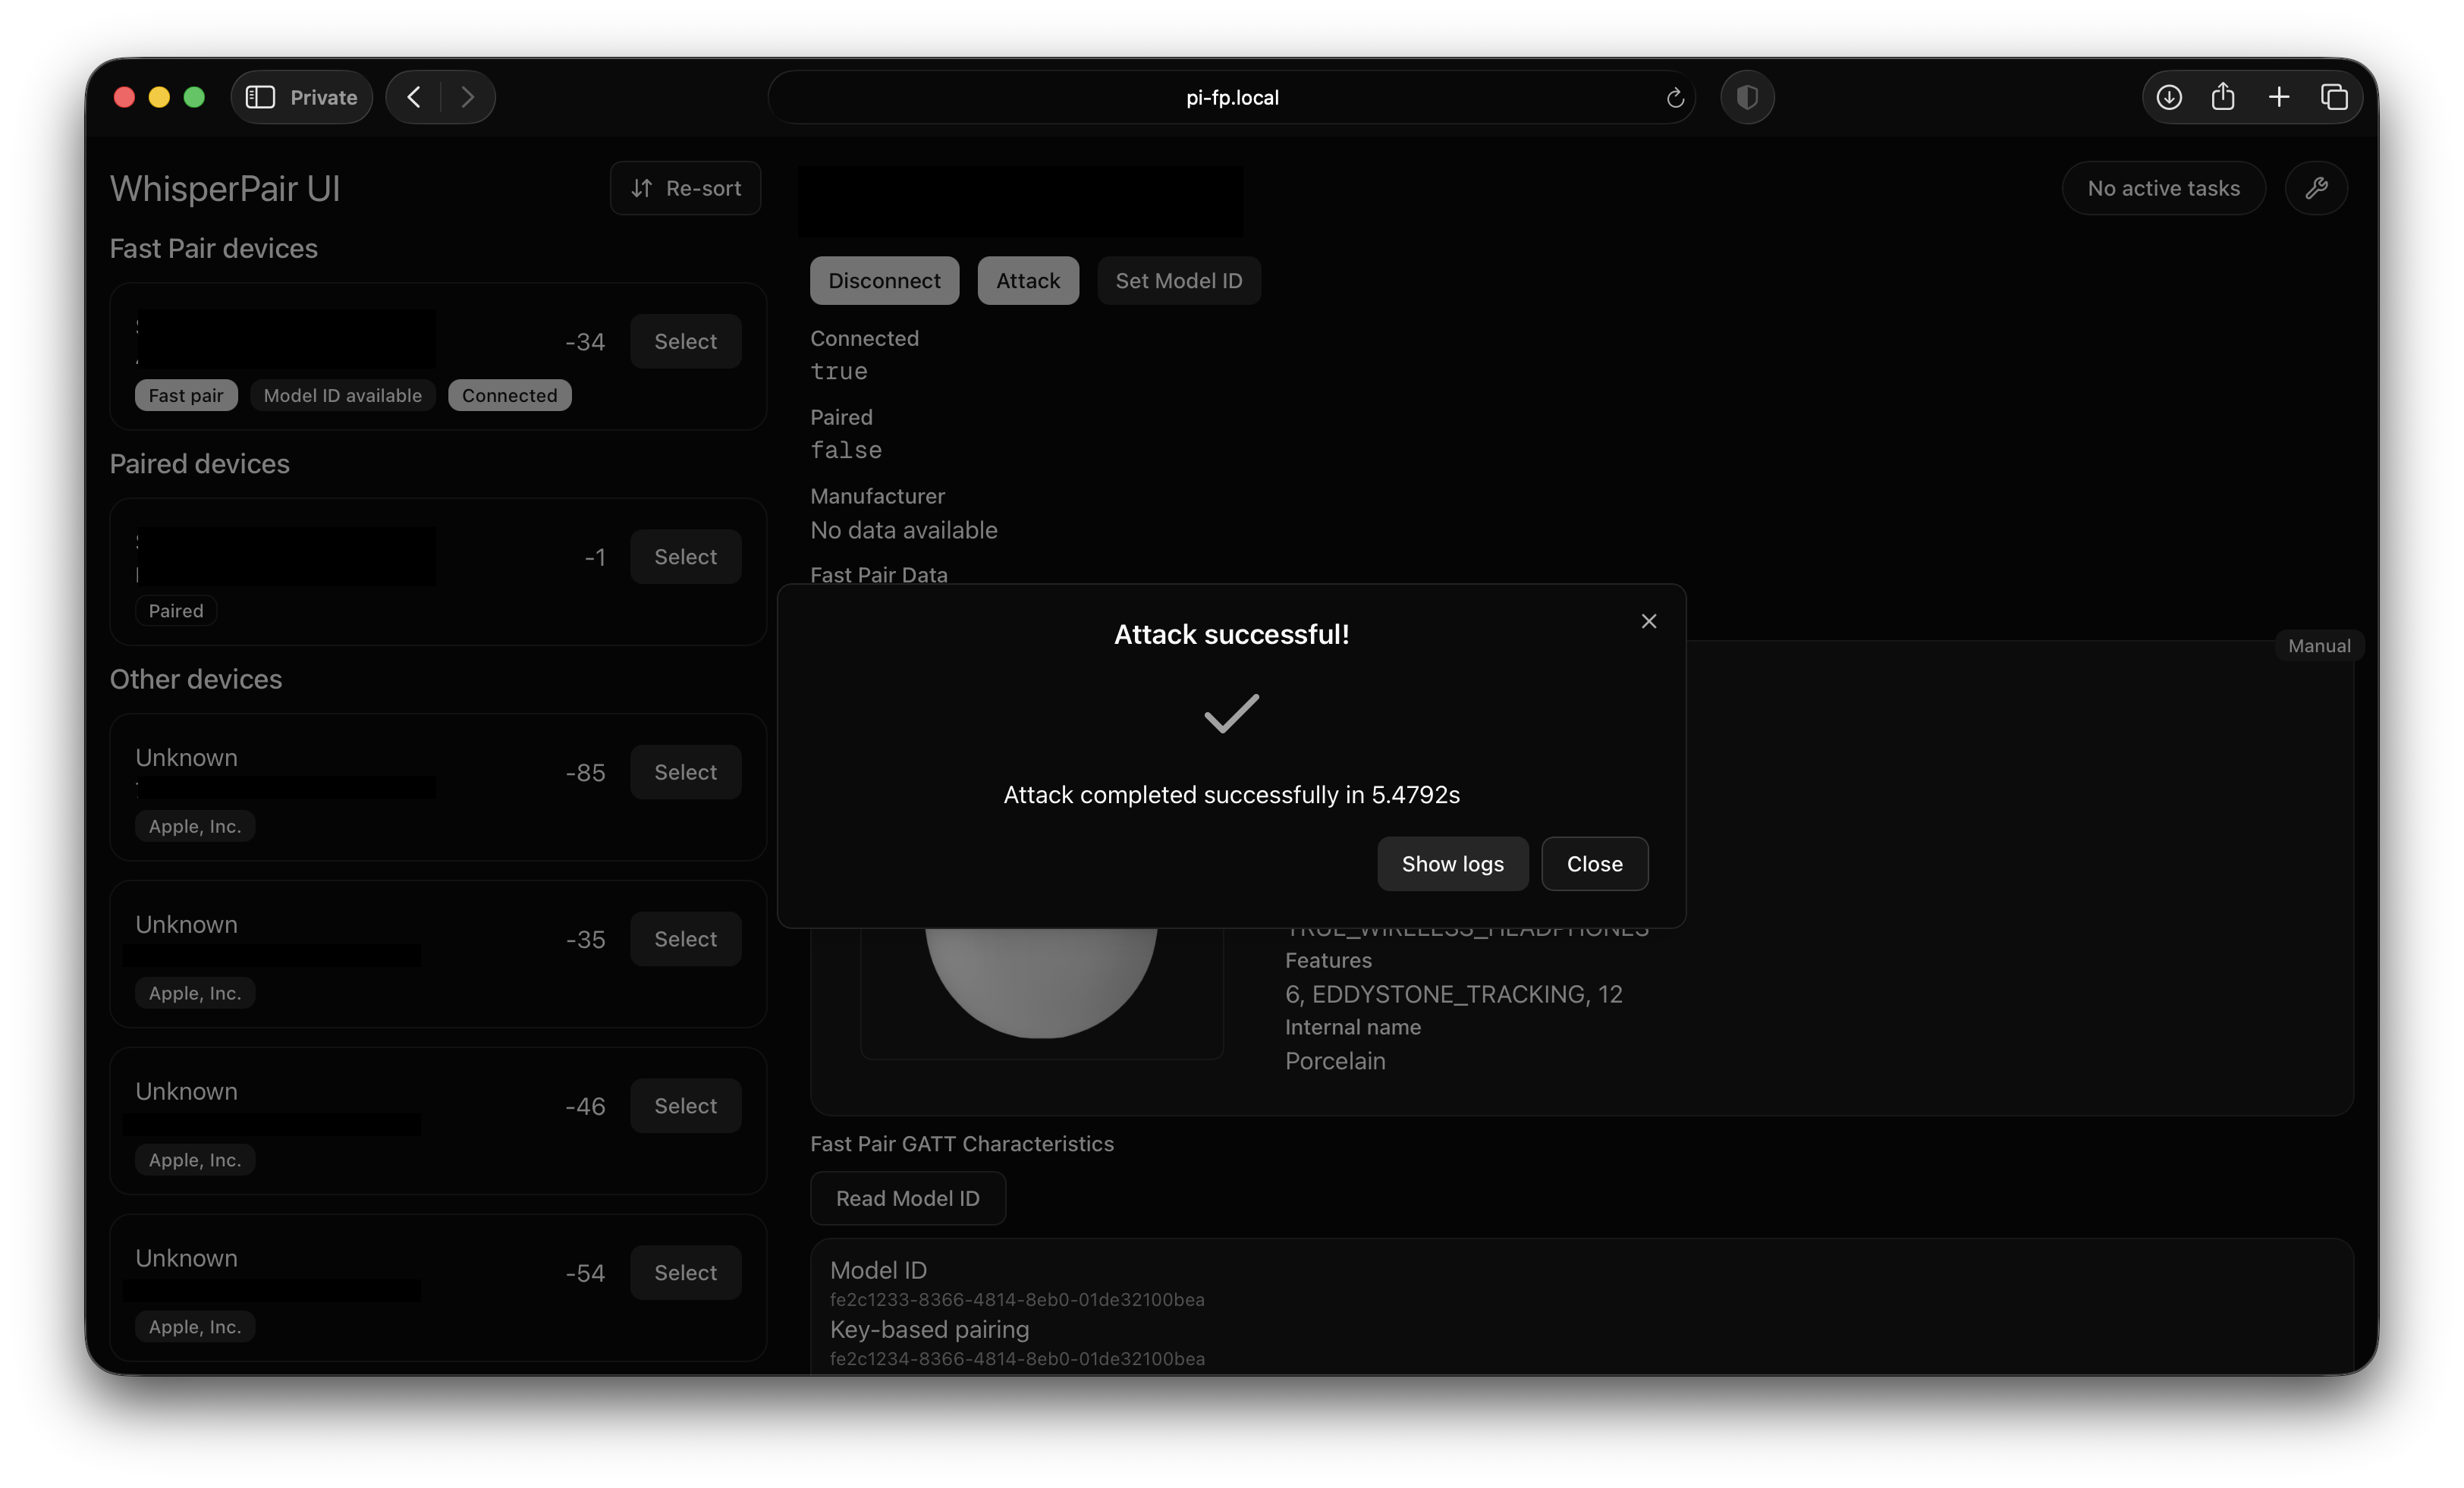 kuleuven-cosic/whisperpair
The official reference implementation & vulnerability verification of our attack WhisperPair (CVE-2025-36911) which affects Google's Fast Pair…
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
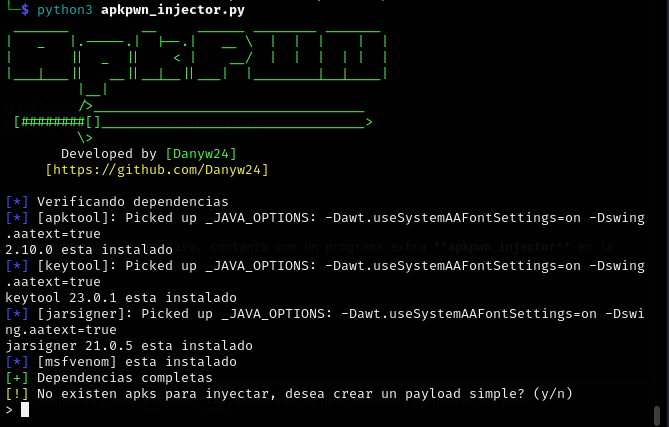 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
 nicholas-howland/cve-2026-6992-poc
Vulnerability proof of concept reworked from https://github.com/utmost3/cve/issues/2 I take no credit for discovering the vulnerability. This is for…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 spectrixdev/diy_whisperpair
Hijacking Bluetooth Accessories Using Google Fast Pair: WhisperPair CVE-2025-36911 Reference Implementation & Vulnerability Verification Toolkit
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 pivotchip/frostedfastpair
WhisperPair (CVE-2025-36911) POC for ESP32 device
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 aalex954/whisperpair-poc-tool
A security research tool that identifies and demonstrates the CVE-2025-36911: Fast Pair Pairing Mode Bypass vulnerability
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 nsm-barii/cve-2025-15474
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 yashodhanvivek/agatsa-easytouch-plus---cve-2025-56019
This report is for CVE-2025-56019 reserved for Easytouch+product for BLE authentication vulnerability assigned to Discoverer Yashodhan Vivek Mandke.…