
flipper-mcp
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
ai-securitybluetooth-securitycommand-and-control+9
22
roostercoopllc/flipper-mcpAI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
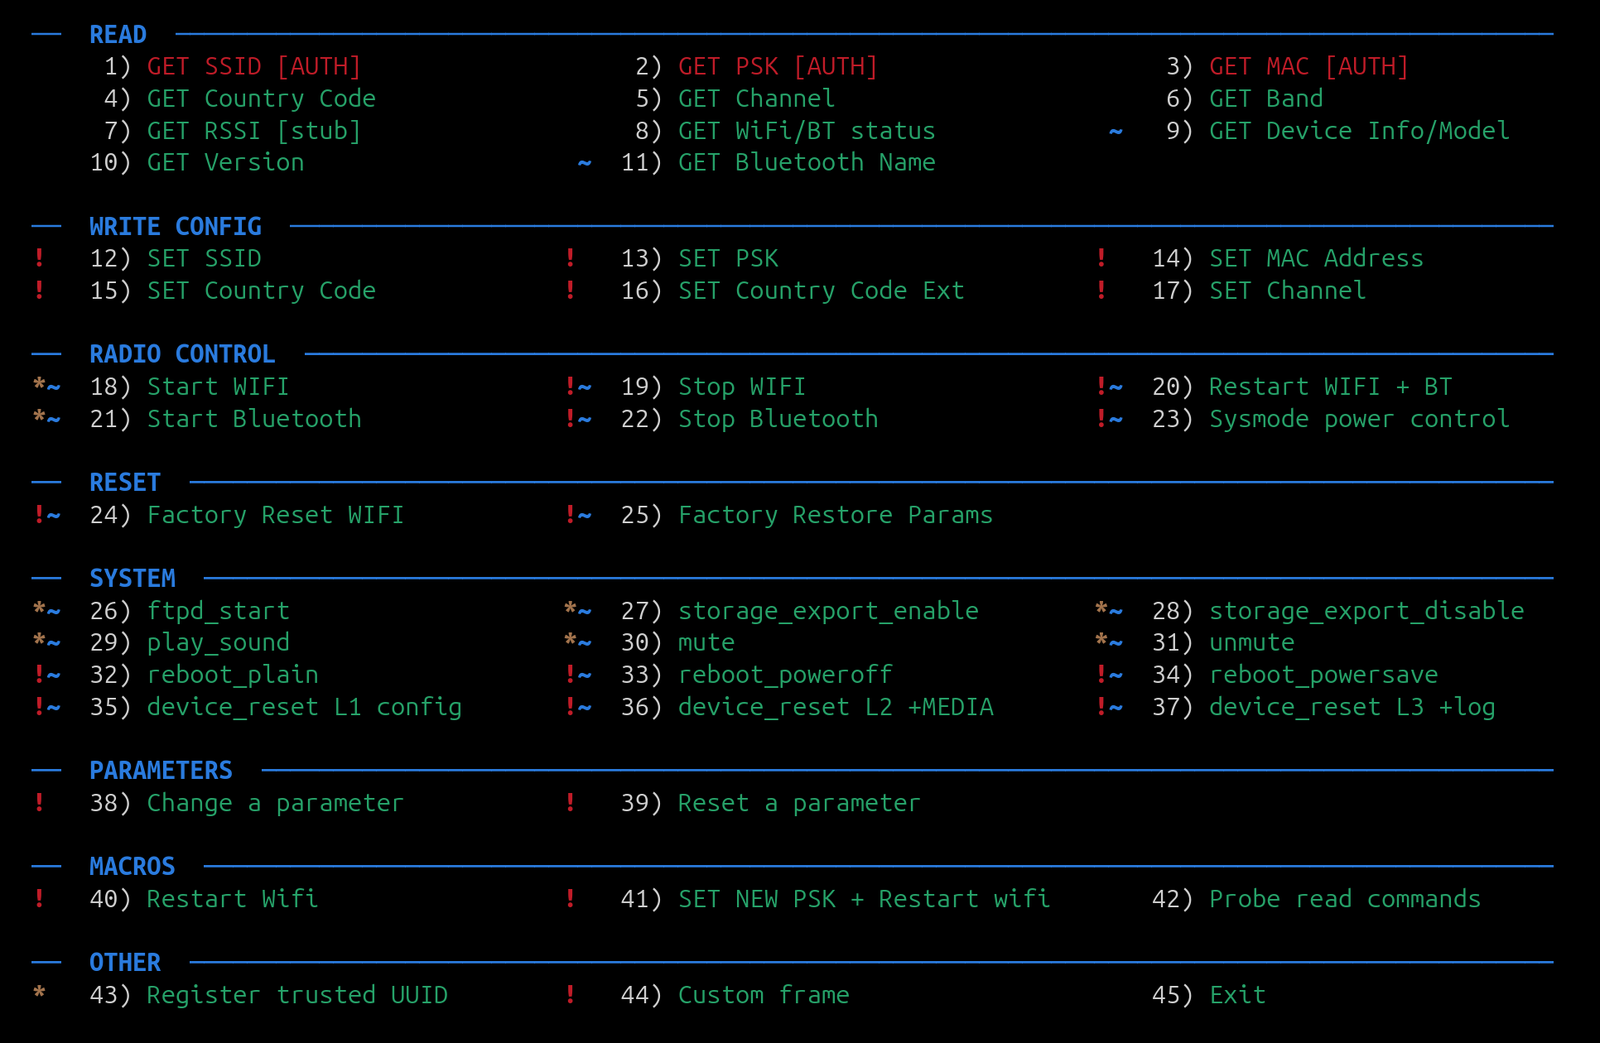 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 barghest-ngo/cve-2026-51376
Proof-of-concept exploit for BLE cache poisoning in Bitchat 1.15.0, demonstrating a man-in-the-middle attack that poisons the Bluetooth Low Energy…
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 v3ilsm1th/cve-2025-27840-wip
Work-in-progress PoC for CVE-2025-27840, an ESP32 Bluetooth vulnerability involving undocumented HCI commands enabling memory access and device…
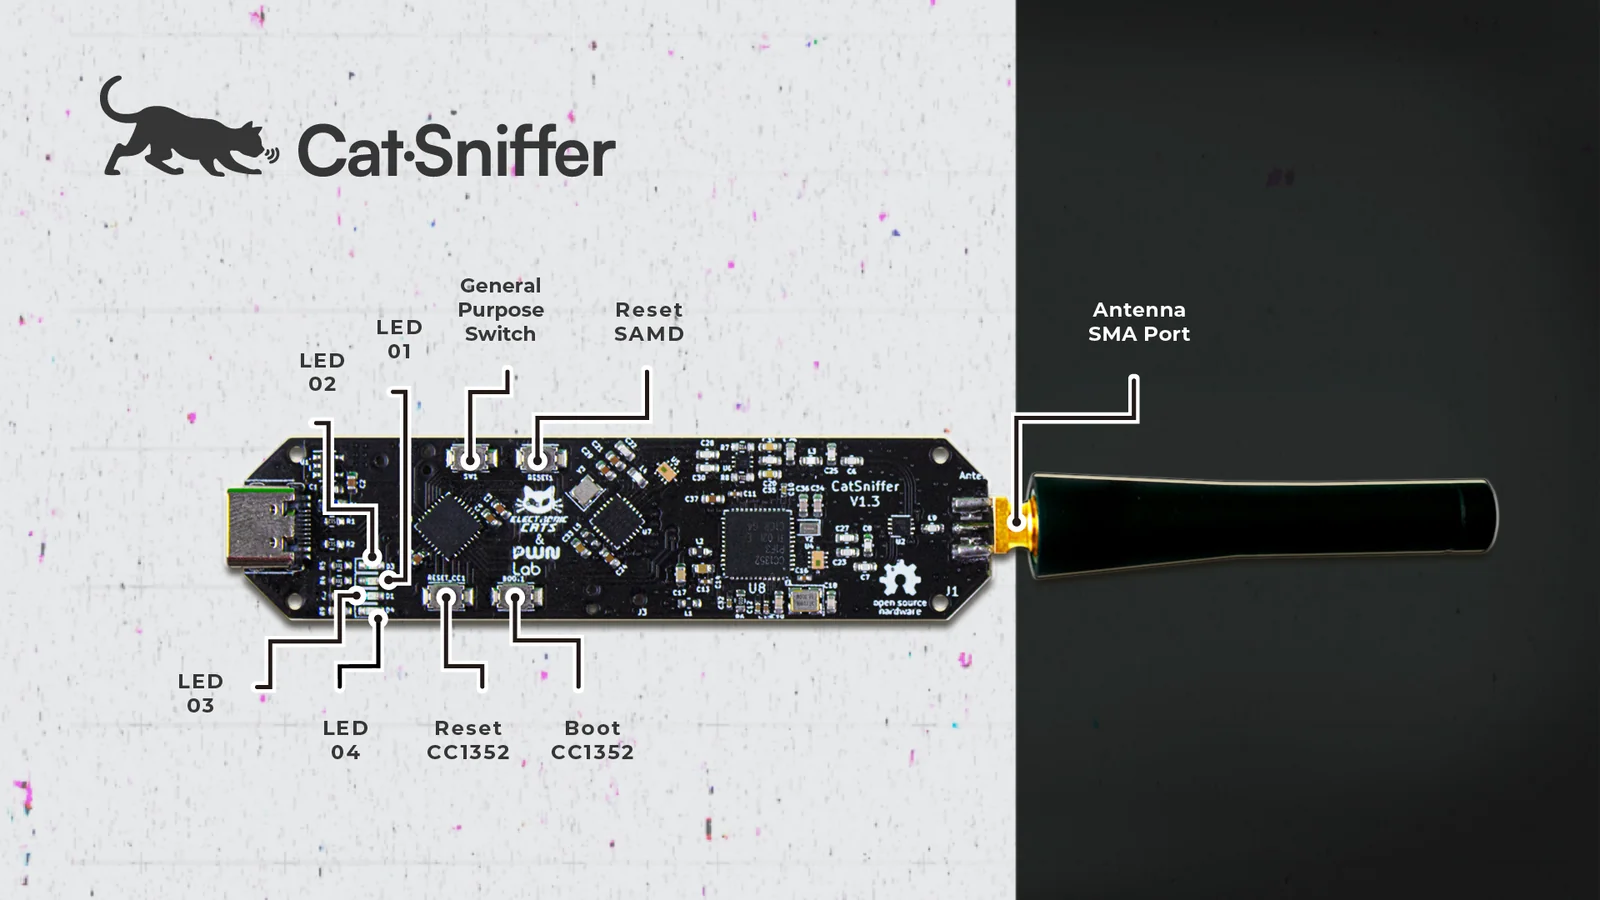 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
 pazhanivel07/system_bt_a10_r33_cve-2021-0474
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…
 pazhanivel07/system_bt_a10-r33_cve-2021-0474
Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0475
Android Bluetooth stack (Fluoride) with build instructions for AOSP and Linux, including dependency setup and GN/Ninja build steps.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0435
AOSP Bluetooth stack repository modified for CVE-2021-0435, providing a patched or vulnerable version for analysis and testing of Bluetooth…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 cipherx1802/cve-2026-31280-insecure-bluetooth-rfcomm-leading-to-device-crash-in-parani-m10-intercom
Proof-of-concept demonstrating an unauthenticated Bluetooth RFCOMM service in Parani M10 Intercom that allows arbitrary payload delivery, leading to…
 jjjjjjjj987/cve-2023-45866-py
Python-based proof-of-concept for CVE-2023-45866, a Bluetooth vulnerability, demonstrating exploitation techniques for security research and testing.
 shaikusaf/packages_apps_bluetooth_aosp10_r33_cve-2021-0329
Android Bluetooth package with modifications addressing CVE-2021-0329, a critical remote code execution vulnerability in Bluetooth. Provides patched…