
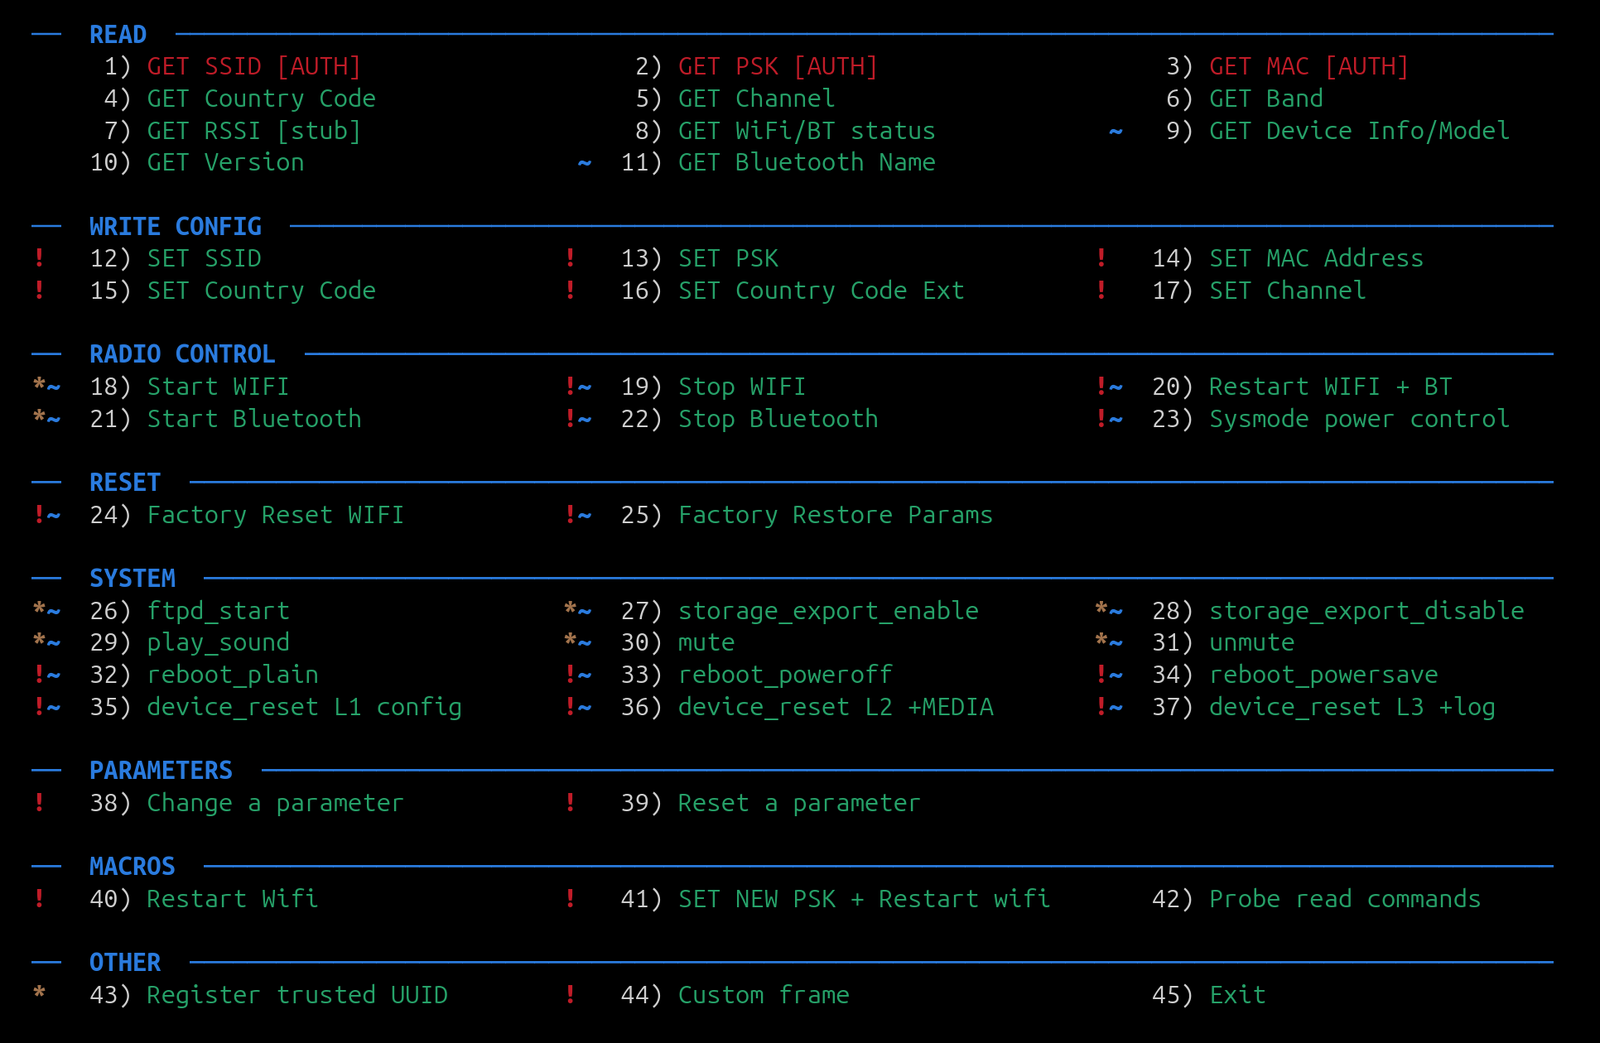
Dji_ble_vuln
 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
bluetooth-securitycommand-and-controlembedded-systems-security+6
feedbeef/dji_ble_vulnDJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
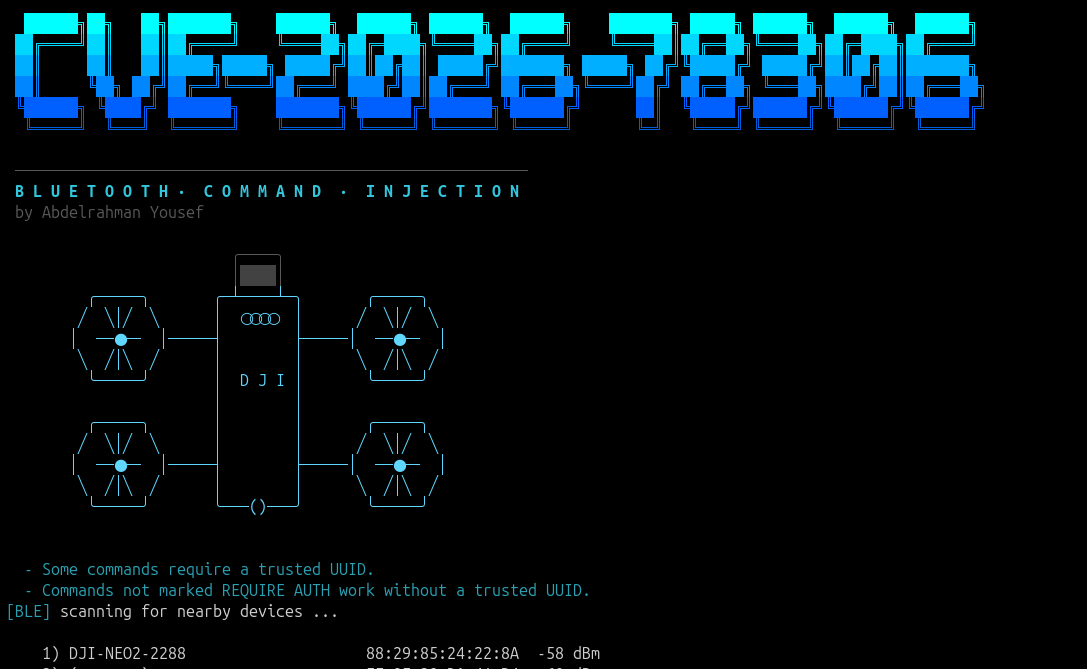 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
 barghest-ngo/cve-2026-51376
Proof-of-concept exploit for BLE cache poisoning in Bitchat 1.15.0, demonstrating a man-in-the-middle attack that poisons the Bluetooth Low Energy…
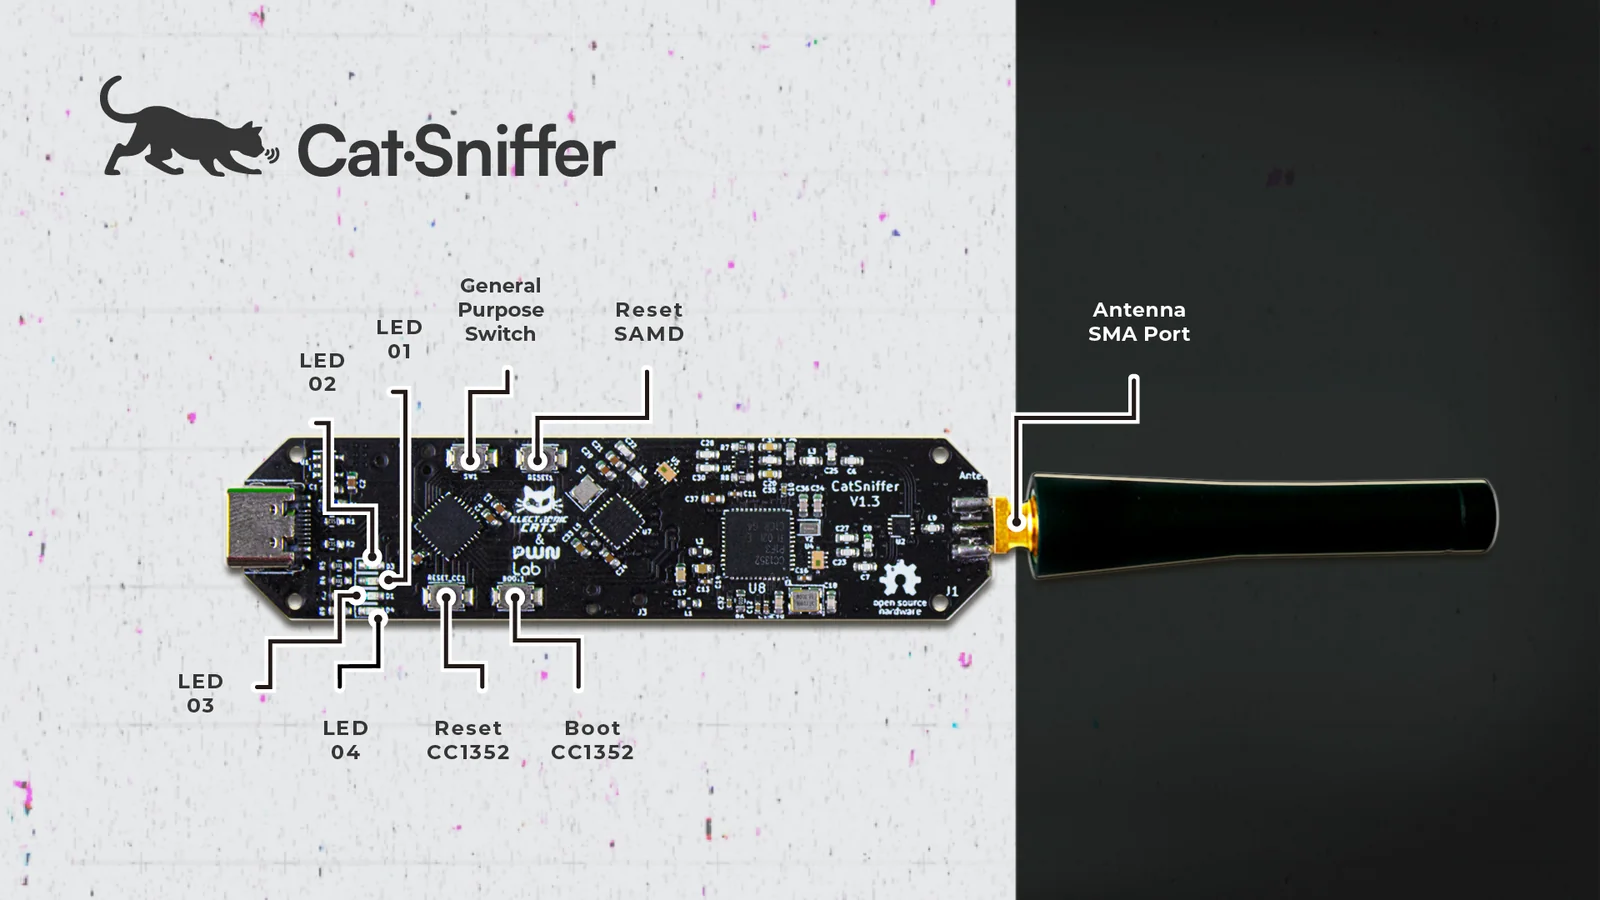 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
 whad-team/whad-client
Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…
 jiaoxianjun/btle
Bluetooth Low Energy (BLE) packet sniffer and transmitter for both standard and non standard (raw bit) based on Software Defined Radio (SDR).
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 quarkslab/conf-presentations
Quarkslab conference talks
 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
 anssi-fr/ultrablue
User-friendly Lightweight TPM Remote Attestation over Bluetooth
 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…