

CVE-2020-0022
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
android-securitybinary-exploitationbluetooth-security+4
idkwim/cve-2020-0022Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 pazhanivel07/system_bt_a10_r33_cve-2021-0474
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…
 pazhanivel07/system_bt_a10-r33_cve-2021-0474
Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0475
Android Bluetooth stack (Fluoride) with build instructions for AOSP and Linux, including dependency setup and GN/Ninja build steps.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0435
AOSP Bluetooth stack repository modified for CVE-2021-0435, providing a patched or vulnerable version for analysis and testing of Bluetooth…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 shaikusaf/packages_apps_bluetooth_aosp10_r33_cve-2021-0329
Android Bluetooth package with modifications addressing CVE-2021-0329, a critical remote code execution vulnerability in Bluetooth. Provides patched…
 jiaoxianjun/btle
Bluetooth Low Energy (BLE) packet sniffer and transmitter for both standard and non standard (raw bit) based on Software Defined Radio (SDR).
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 jasonw88/esp32-cve-2025-27840-power-trace-experiment
Firmware for getting a power trace of the behavior of the bluetooth module on the ESP32 when the ESP32 is sent the undocumented hci bluetooth…
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
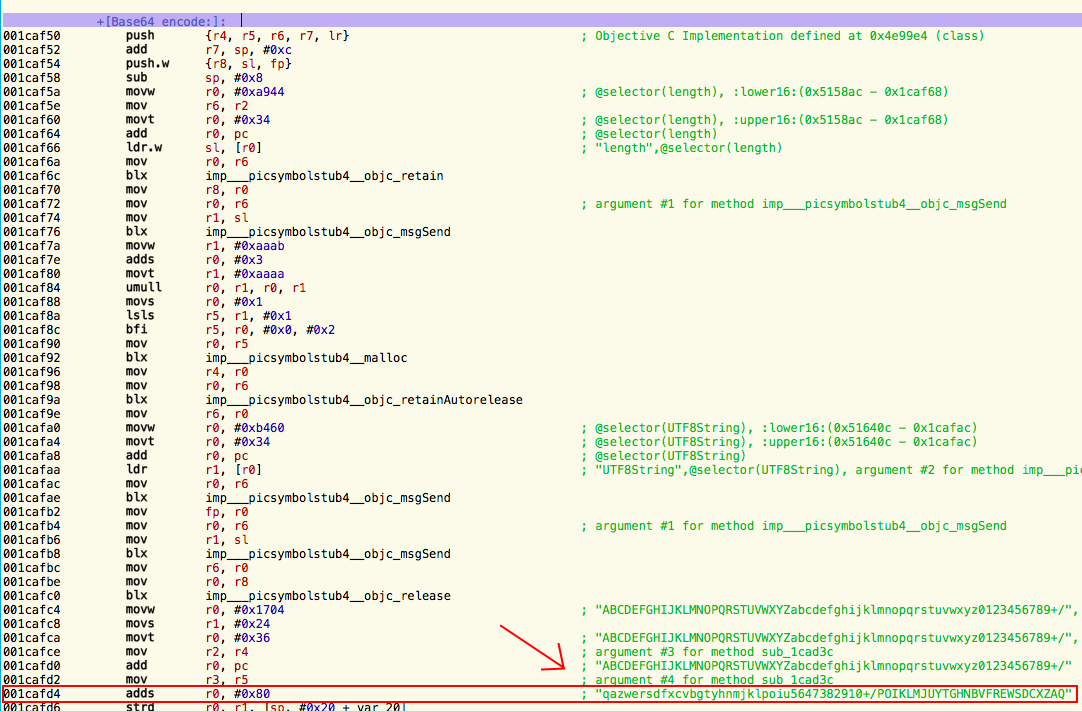 jasondoyle/komfy-switch-wifi-password-disclosure
Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…
 satheesh575555/system_bt_aosp_10_r33_cve-2021-0316
Patched Bluetooth stack for Android 10 (AOSP r33) fixing buffer overflow vulnerability CVE-2021-0316.
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.