

CVE-2020-0022
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
android-securitybinary-exploitationbluetooth-security+4
idkwim/cve-2020-0022Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 pazhanivel07/system_bt_a10_r33_cve-2021-0474
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…
 pazhanivel07/system_bt_a10-r33_cve-2021-0474
Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0475
Android Bluetooth stack (Fluoride) with build instructions for AOSP and Linux, including dependency setup and GN/Ninja build steps.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0435
AOSP Bluetooth stack repository modified for CVE-2021-0435, providing a patched or vulnerable version for analysis and testing of Bluetooth…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 shaikusaf/packages_apps_bluetooth_aosp10_r33_cve-2021-0329
Android Bluetooth package with modifications addressing CVE-2021-0329, a critical remote code execution vulnerability in Bluetooth. Provides patched…
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
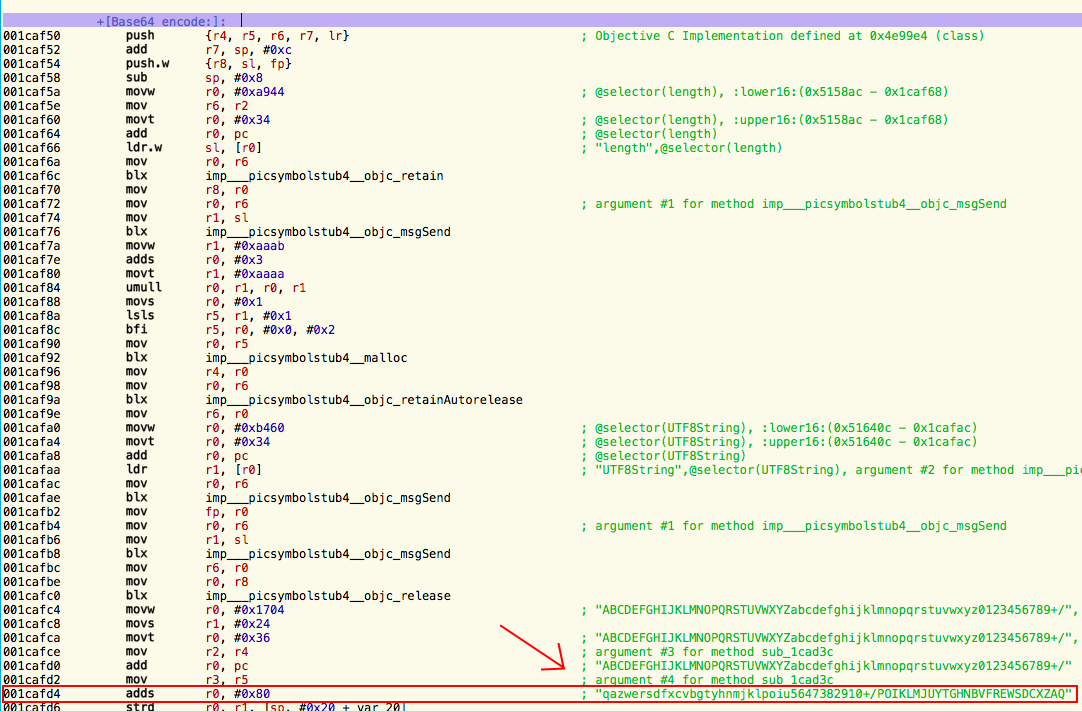 jasondoyle/komfy-switch-wifi-password-disclosure
Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 satheesh575555/system_bt_aosp_10_r33_cve-2021-0316
Patched Bluetooth stack for Android 10 (AOSP r33) fixing buffer overflow vulnerability CVE-2021-0316.
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
 nanopathi/system_bt_aosp10_r33_cve-2021-0522
Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.
 hackingdave/btrpa-scan
Bluetooth Low Energy (BLE) scanner with Resolvable Private Address (RPA) resolution using Identity Resolving Keys (IRKs)
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 m4rm0k/cve-2020-10135-bias
CVE 2020-10135 a.k.a BIAS (Bluetooth Impersonation Attack)
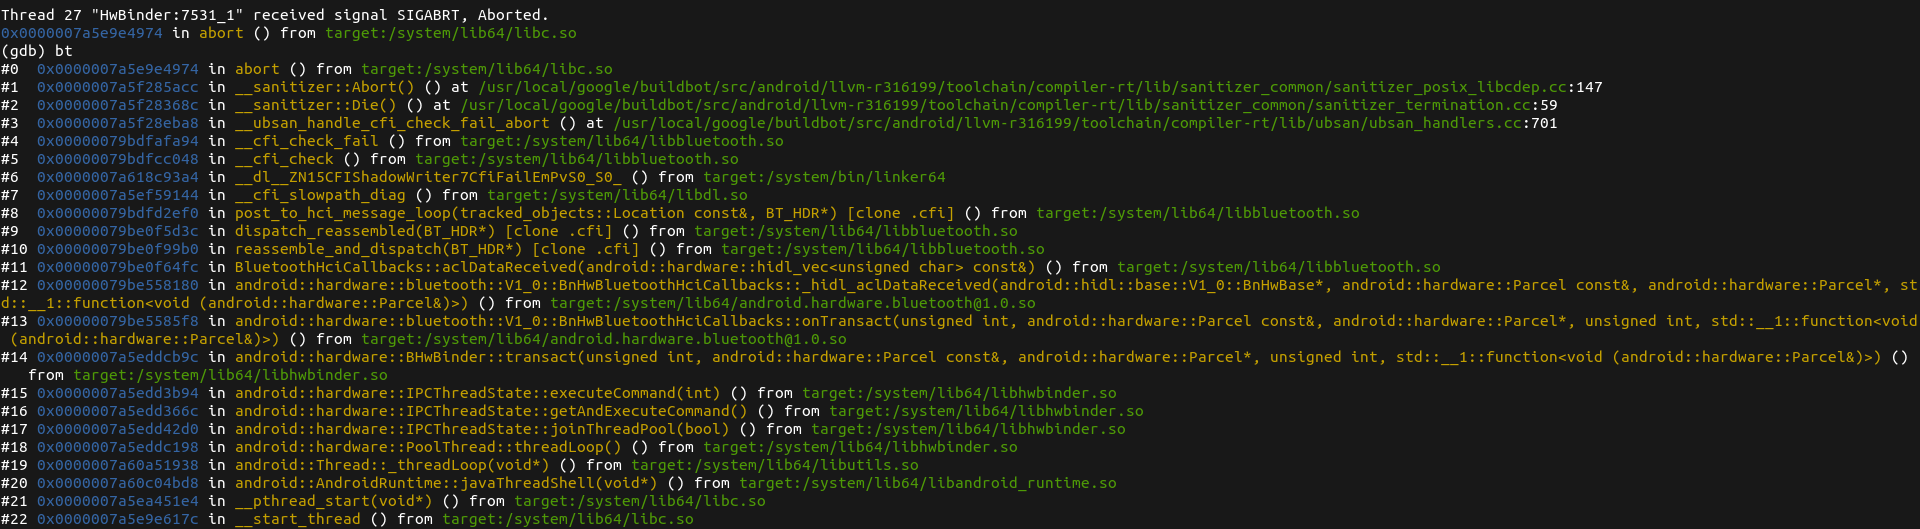 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)