

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.3k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
 aalex954/whisperpair-poc-tool
A security research tool that identifies and demonstrates the CVE-2025-36911: Fast Pair Pairing Mode Bypass vulnerability
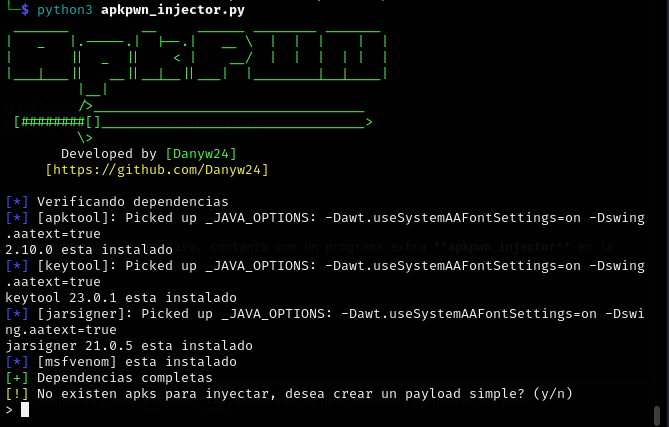 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
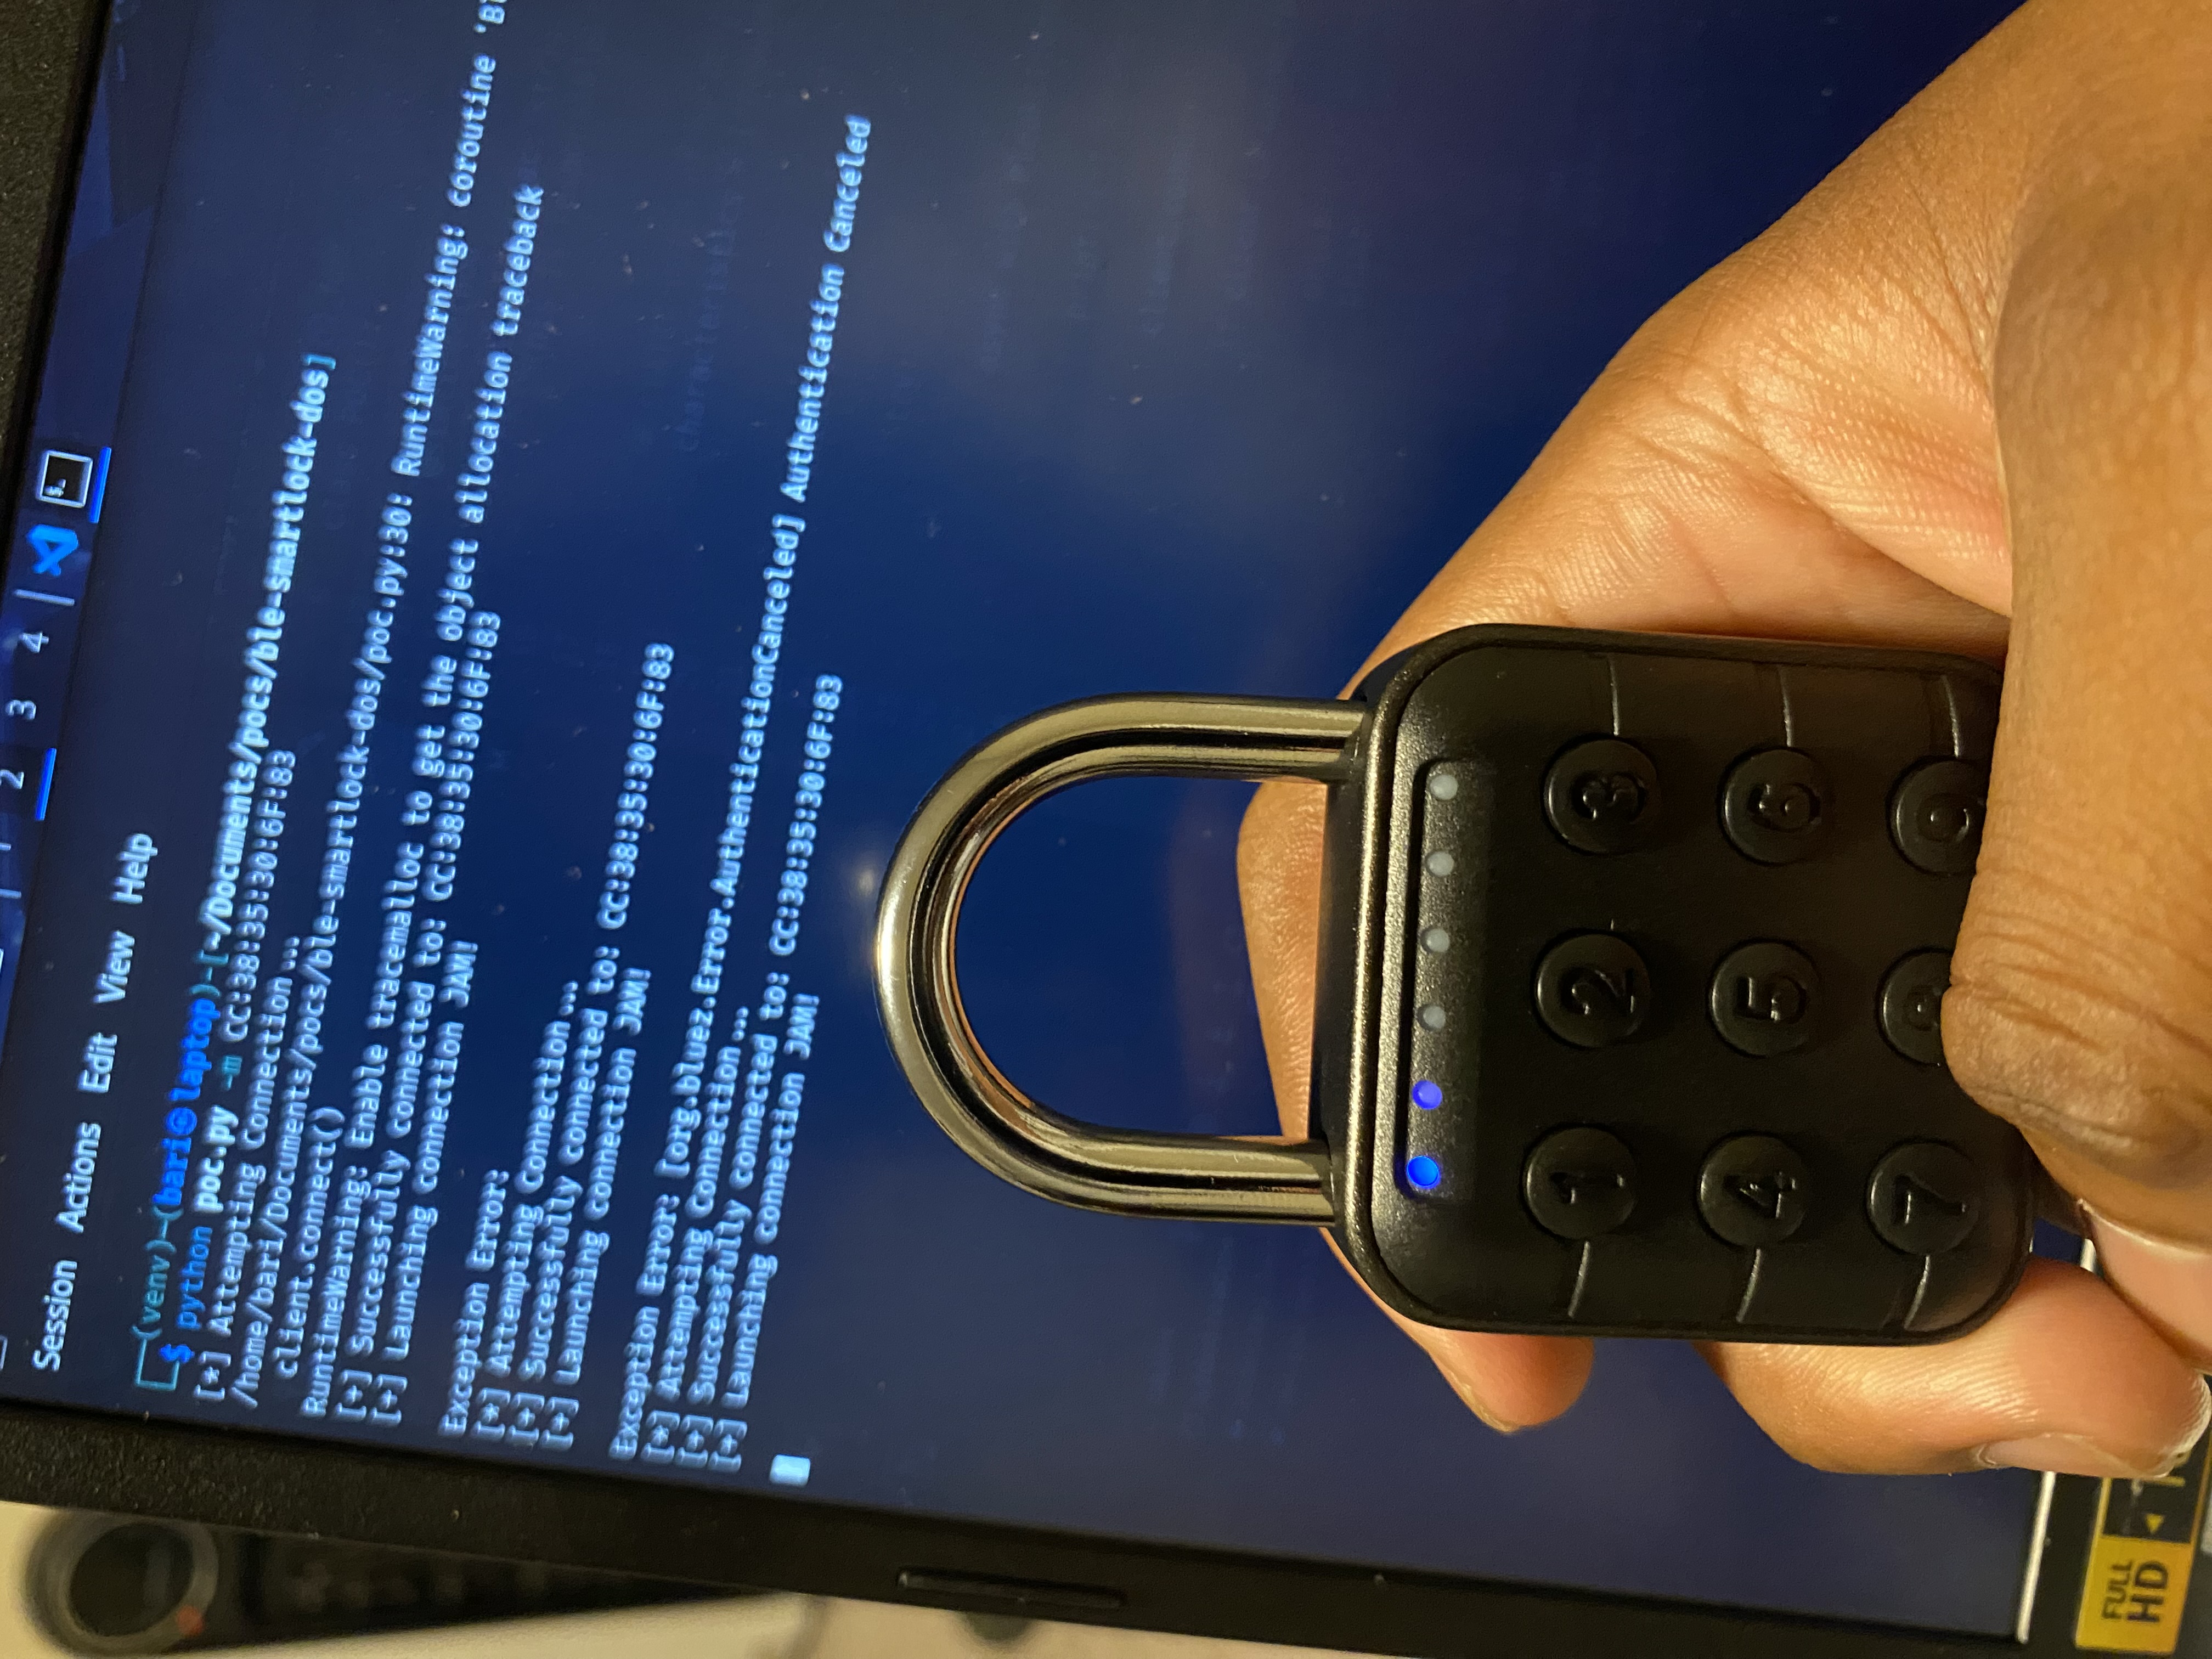 nsm-barii/cve-2025-15474
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 aymankhalfatni/cve-2017-0785
CVE-2017-0785: BlueBorne PoC
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 ojasookert/cve-2017-0785
Blueborne CVE-2017-0785 Android information leak vulnerability
 demining/bluetooth-attacks-cve-2025-27840
Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth
 yashodhanvivek/agatsa-easytouch-plus---cve-2025-56019
This report is for CVE-2025-56019 reserved for Easytouch+product for BLE authentication vulnerability assigned to Discoverer Yashodhan Vivek Mandke.…
 nanopathi/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…