
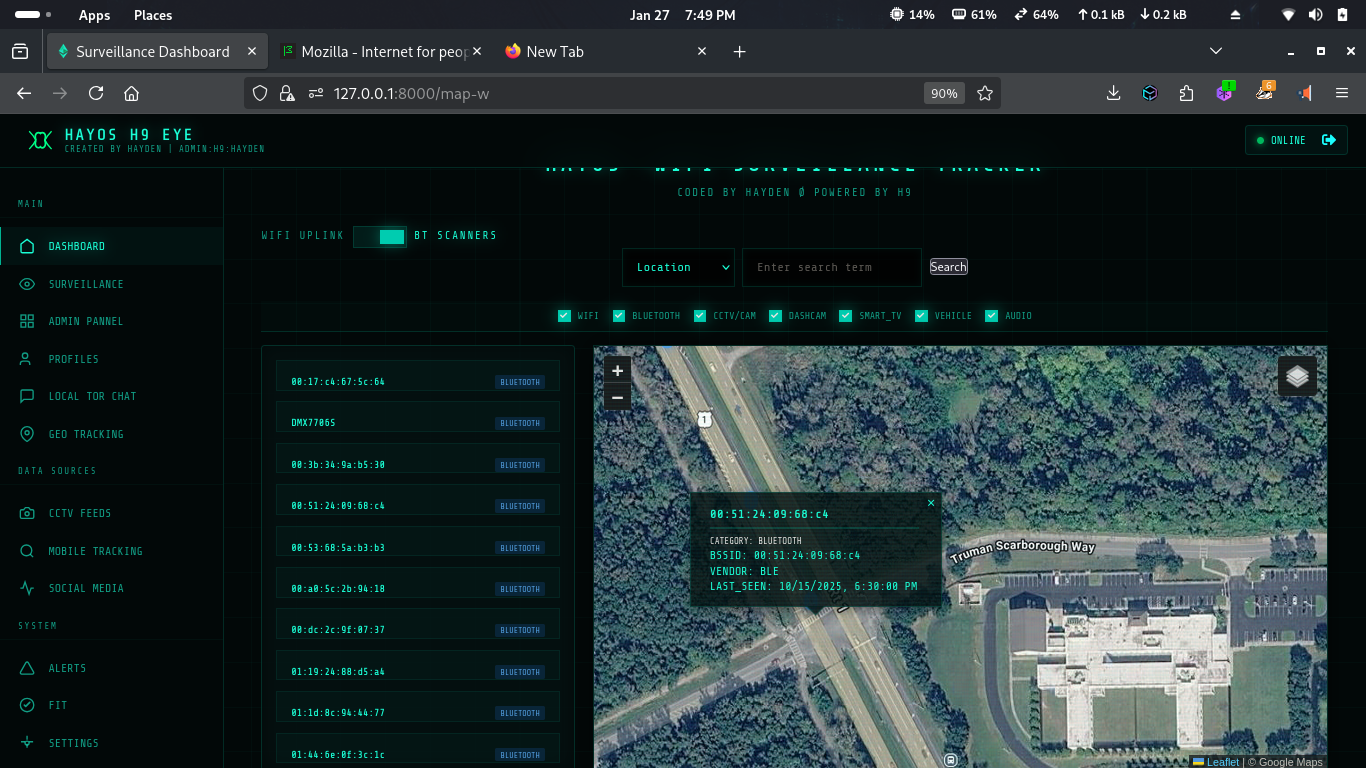
WireTapper
 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
bluetooth-securitydns-subdomain-enumerationembedded-systems-security+9
2.5k
h9zdev/wiretapperPassive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 aalex954/whisperpair-poc-tool
A security research tool that identifies and demonstrates the CVE-2025-36911: Fast Pair Pairing Mode Bypass vulnerability
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 insecurityofthings/jackit
Exploit tool for MouseJack vulnerability enabling keystroke injection and mouse hijacking over nRF24L01 wireless dongles. Supports multiple Microsoft…
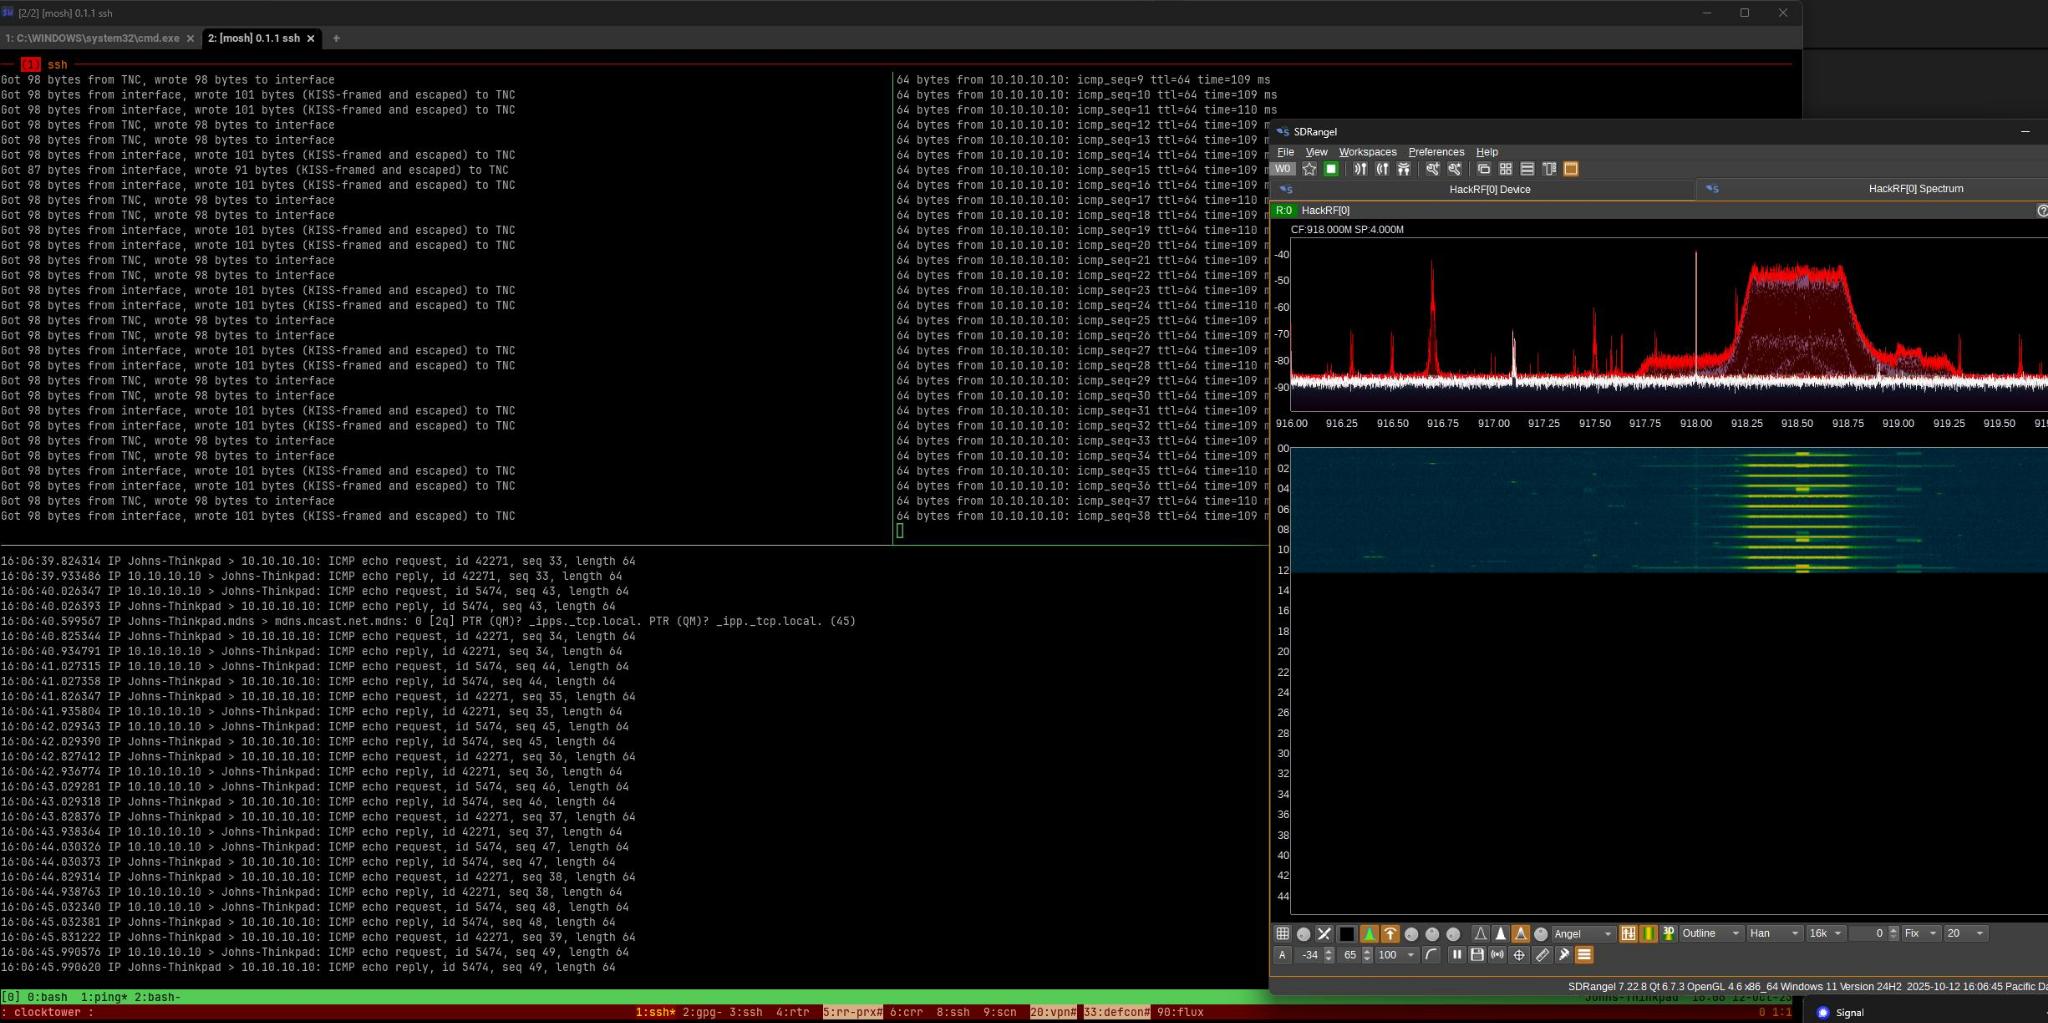 datapartyjs/meshtnc
Firmware for converting consumer LoRa radios into KISS TNC modems with serial CLI, BLE packet sniffing, and APRS/AX.25 compatibility for packet radio…
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 nccgroup/bleboy
BLEBoy is a training tool to teach users about BLE security by providing a single BLE peripheral that can be used to experiment with each BLE pairing…
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…
 evilsocket/bleah
This repository is DEPRECATED, please use bettercap as this tool has been ported to its BLE modules.
 ymsniper/whisper_bully
Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
 nccgroup/blesuite-cli
BLESuite_CLI is a command line tool to enable an easier way to test Bluetooth Low Energy (BLE) devices
 ap425q/whisper-pair
Scans Bluetooth Low Energy devices for Fast Pair vulnerabilities (CVE-2025-36911), testing if accessories accept unencrypted Key-Based Pairing…
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment