

CVE-2024-1086
 xzx482/cve-2024-1086
Universal local privilege escalation exploit for CVE-2024-1086 targeting Linux kernels v5.14 to v6.6. Provides root shell with 99.4% success rate on…
binary-exploitationeducationexploitation+3
xzx482/cve-2024-1086Universal local privilege escalation exploit for CVE-2024-1086 targeting Linux kernels v5.14 to v6.6. Provides root shell with 99.4% success rate on…
 chrisl0tus/cve-2023-34924
Proof-of-concept exploit for a buffer overflow vulnerability in H3C Magic B1STW router's SetAPInfoById function, causing web service crash and…
 wh04m1001/cve-2023-21752
Proof-of-concept exploit for CVE-2023-21752, an arbitrary file delete vulnerability in Windows Backup service, with two variants including privilege…
 jas502n/cve-2018-17182
Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
 whotwagner/logrotten
Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…
 nhh9905/cve-2026-62735
Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…
 synacktiv/samsung-q60t-exploit
Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…
 0xshe/cve-2026-31431
Kernel privilege escalation exploit for CVE-2026-31431, abusing AF_ALG interface to overwrite /bin/su and spawn a root shell. Includes C…
 imbas007/cve-2026-42533
Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…
 convisolabs/cve-2022-24834
Generic heap overflow exploit for CVE-2022-24834 in Redis Lua cjson library, with auto gadget finder, symbol resolution, and reverse shell handler…
 petergottesman/pwnkit-exploit
Local privilege escalation exploit for CVE-2021-4034 in pkexec, providing a proof-of-concept that drops a root shell on vulnerable systems.
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 peterpan0927/tfc-chrome-v8-bug-cve-2021-38001-poc
Proof-of-concept exploit for CVE-2021-38001, a Chrome V8 JavaScript engine vulnerability. Demonstrates exploitation via d8 shell with a malicious…
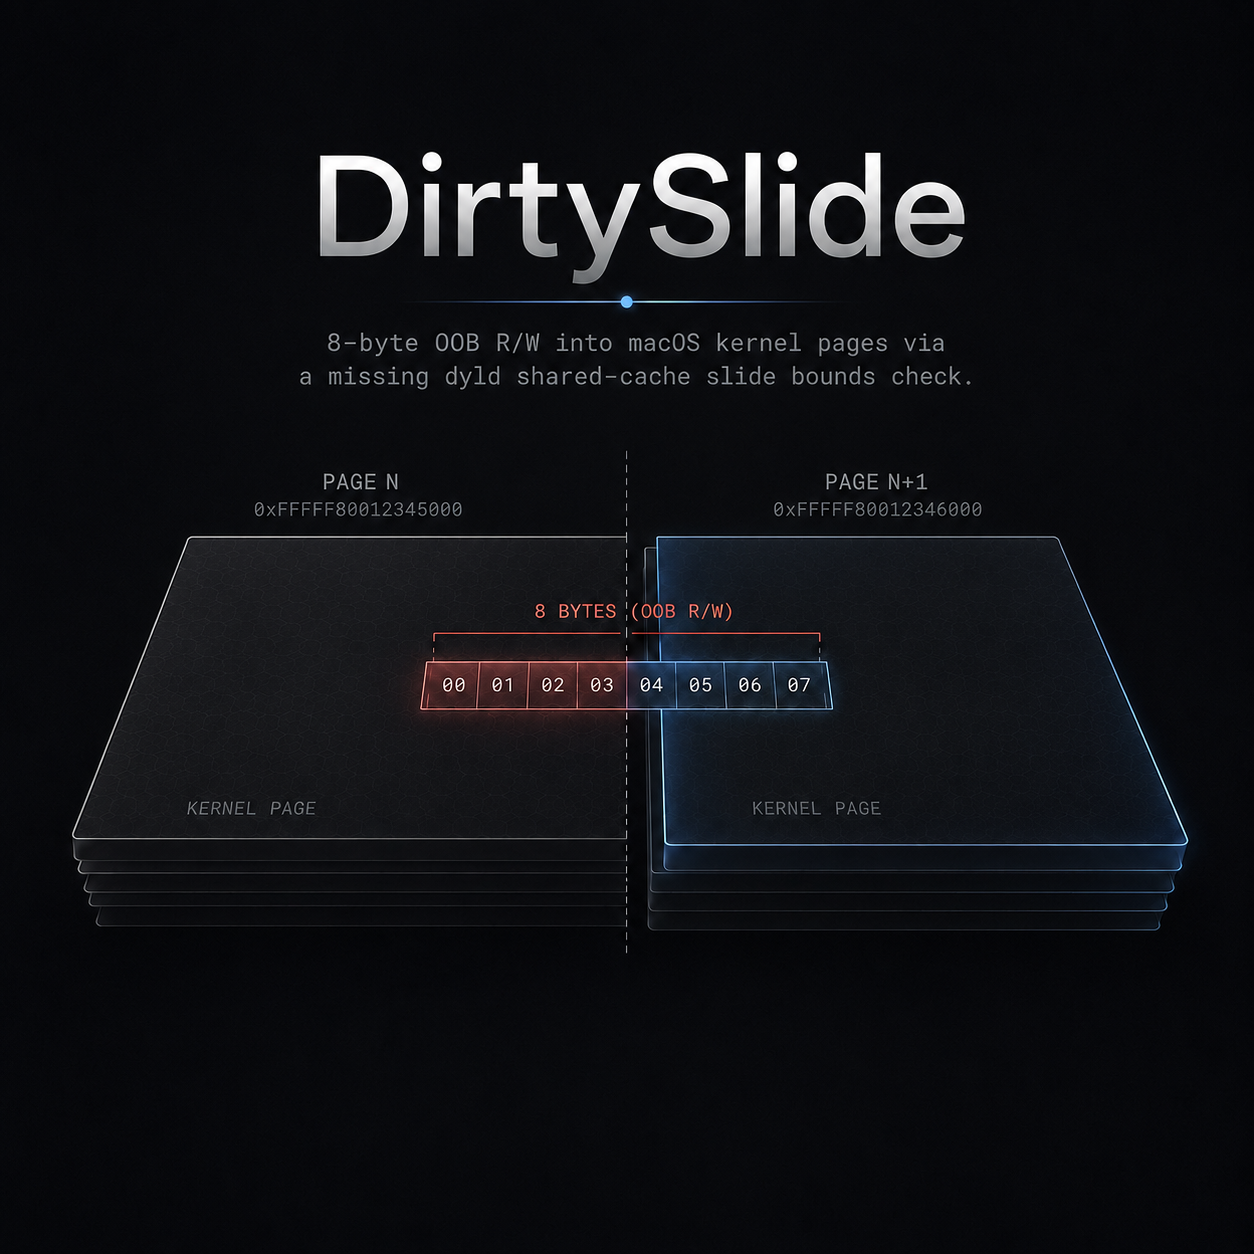 gracecondition/dirtyslide
Local privilege escalation exploit for macOS XNU kernel (CVE-2026-43724) that uses an out-of-bounds write in dyld shared-cache slide walk to gain a…
 otsmane-ahmed/cve-2025-2620-poc
Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 hackspeak/cve-2026-53365
Local privilege escalation exploit targeting a Linux kernel io_uring AF_VSOCK reference-count bug, using page-cache manipulation to overwrite…