

cve-2019-1663
 kylvgoi/cve-2019-1663
Educational exploit for CVE-2019-1663 targeting a stack-based buffer overflow in Cisco RV routers. Includes a Python exploit script, reverse shell…
binary-exploitationeducationembedded-systems-security+5
kylvgoi/cve-2019-1663Educational exploit for CVE-2019-1663 targeting a stack-based buffer overflow in Cisco RV routers. Includes a Python exploit script, reverse shell…
 petergottesman/pwnkit-exploit
Local privilege escalation exploit for CVE-2021-4034 in pkexec, providing a proof-of-concept that drops a root shell on vulnerable systems.
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 peterpan0927/tfc-chrome-v8-bug-cve-2021-38001-poc
Proof-of-concept exploit for CVE-2021-38001, a Chrome V8 JavaScript engine vulnerability. Demonstrates exploitation via d8 shell with a malicious…
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 whotwagner/logrotten
Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
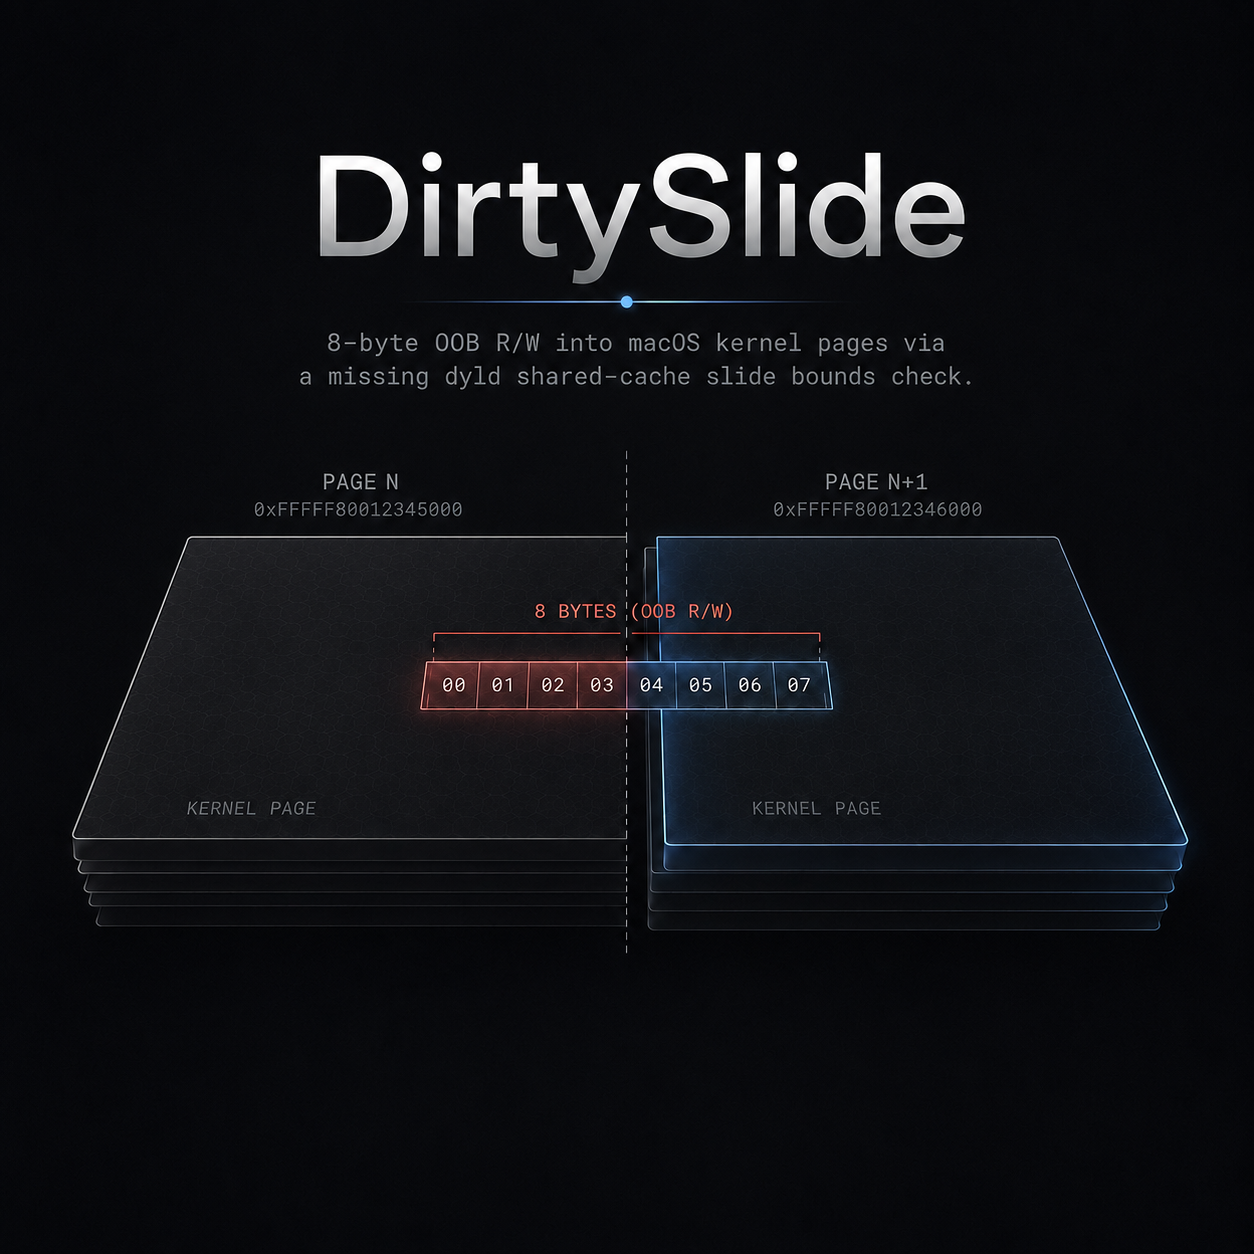 gracecondition/dirtyslide
Local privilege escalation exploit for macOS XNU kernel (CVE-2026-43724) that uses an out-of-bounds write in dyld shared-cache slide walk to gain a…
 itmarcin2211/cve-2022-0847-dirtypipe-exploit
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) that overwrites root's password field in /etc/passwd to pop a root shell, with automatic…
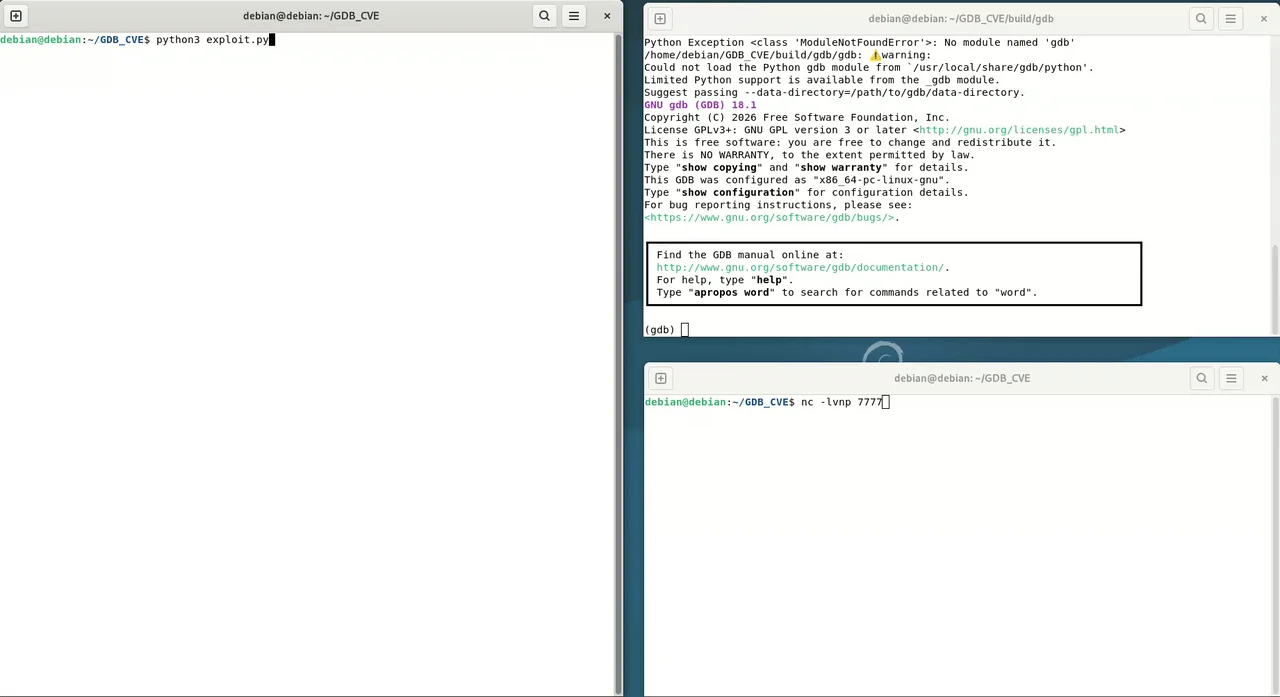 deebumg/cve-2026-121994-poc
Weaponized proof-of-concept for CVE-2026-121994: a fake GDB remote debug stub that sends a malicious p-packet to trigger memory corruption and a…
 synacktiv/samsung-q60t-exploit
Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…
 dungsocool/cve-2017-18349
Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
 chrisl0tus/cve-2023-34924
Proof-of-concept exploit for a buffer overflow vulnerability in H3C Magic B1STW router's SetAPInfoById function, causing web service crash and…
 wh04m1001/cve-2023-21752
Proof-of-concept exploit for CVE-2023-21752, an arbitrary file delete vulnerability in Windows Backup service, with two variants including privilege…
 jas502n/cve-2018-17182
Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
 nhh9905/cve-2026-62735
Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…