
cve-2026-31431
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
binary-exploitationcloud-securitycontainer-security+7
2
nisec-eric/cve-2026-31431Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 zhanghangorg/cve-2026-31431
Detector and proof-of-concept for a Linux kernel page-cache write vulnerability (CVE-2026-31431) in algif_aead, including a non-destructive scanner…
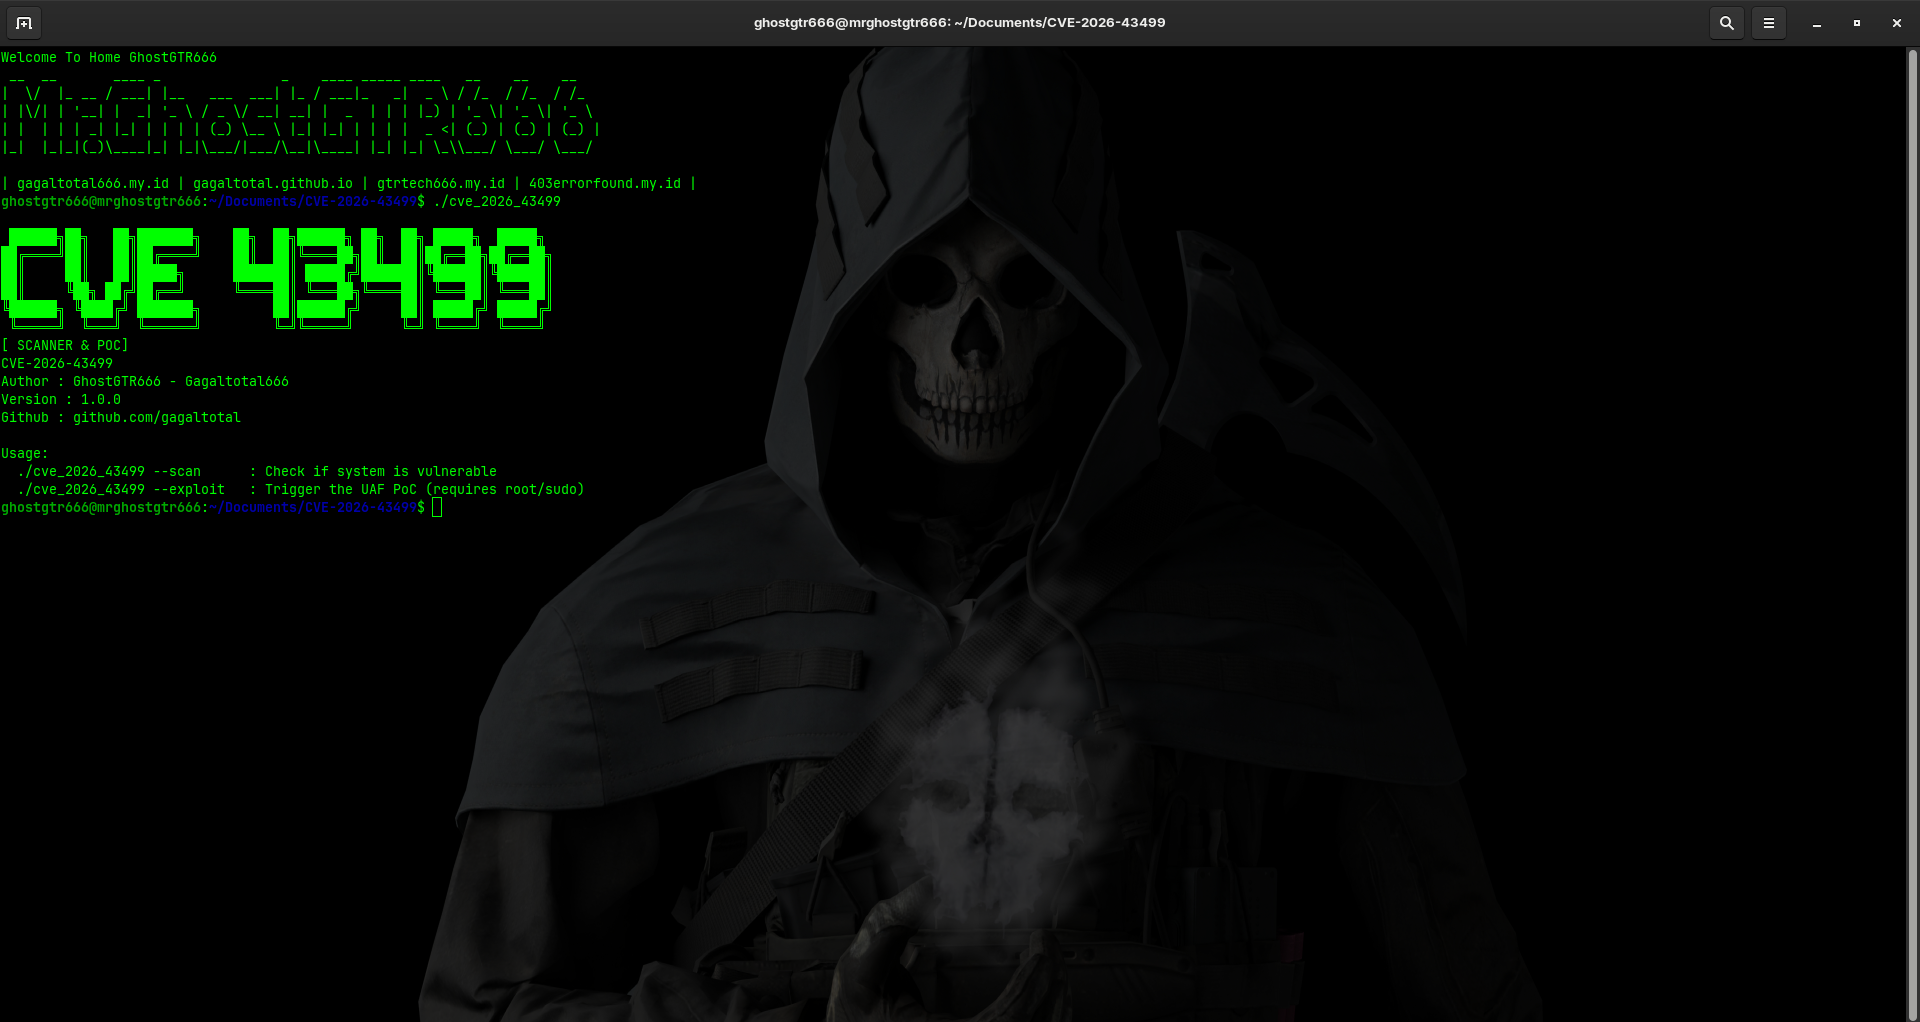 gagaltotal/cve-2026-43499-poc-scanner
CVE-2026-43499 PoC Scanner
 alexisahmed/cve-2022-0847-dirtypipe-exploits
A collection of exploits and documentation that can be used to exploit the Linux Dirty Pipe vulnerability.
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 elttam/publications
Offensive security research hub aggregating original vulnerability advisories, CVE proof-of-concept exploits, conference talks, and internal tooling…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
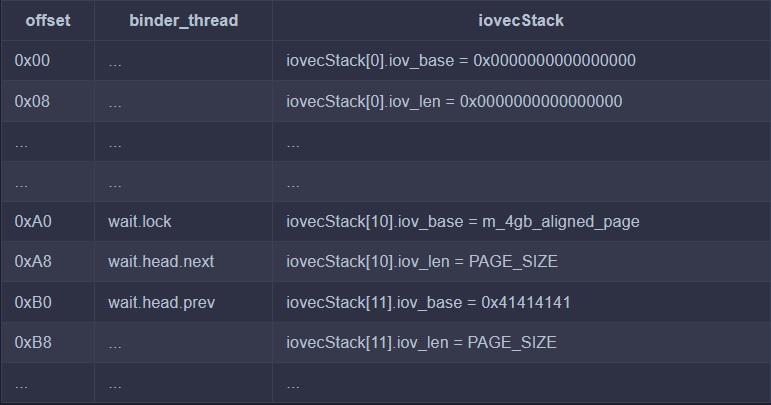 sharif-dev/androidkernelvulnerability
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
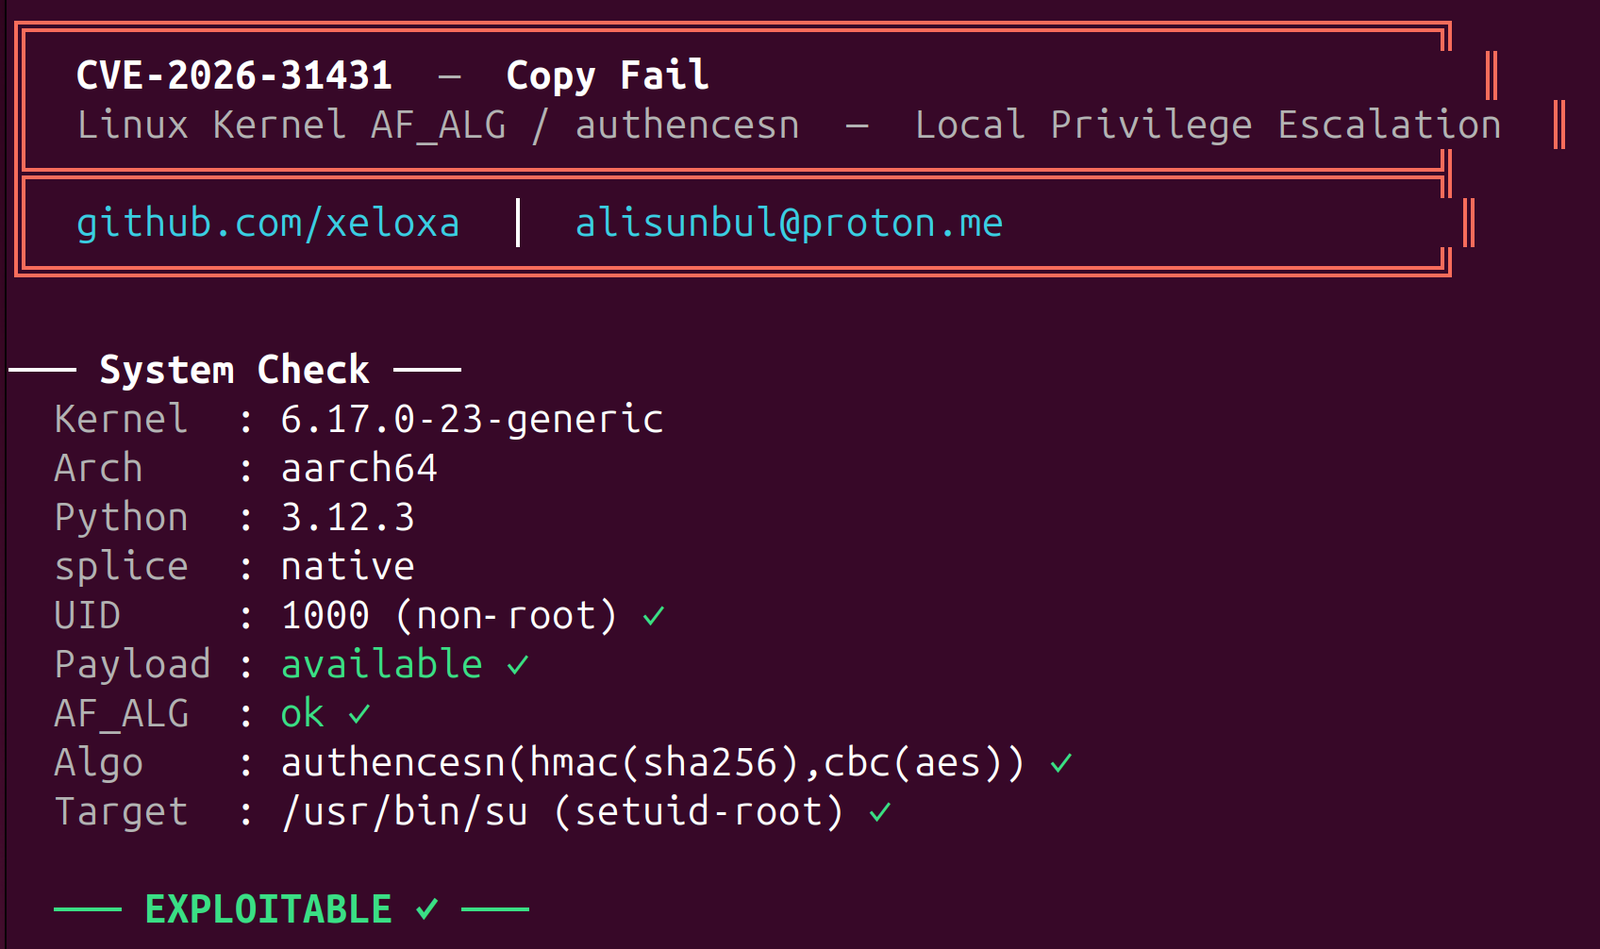 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 hrtowii/cve-2024-23208-test
Proof-of-concept exploit for CVE-2024-23208, targeting a specific vulnerability in Apple platforms. Provides a test case for security researchers and…
 mrk336/cve-2025-26686-the-tcp-ip-flaw-that-opens-the-gates
A critical RCE vulnerability in Windows TCP/IP stack (CVE-2025-26686) leaves sensitive memory unlocked, allowing remote attackers to hijack systems.…
 freeide/cve-2021-31955-poc
Proof-of-concept exploit for CVE-2021-31955, a Windows kernel information disclosure vulnerability. Demonstrates exploitation on 64-bit systems to…
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 0xkol/ripple20-digi-connect-exploit
RCE exploit for CVE-2020-11896 (Ripple20 IP-in-IP Heap Overflow Vulnerability) targeting Digi Connect ME 9210