
CVE-2024-29943
 seadragnol/cve-2024-29943
Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
binary-exploitationeducationexploitation+2
2
seadragnol/cve-2024-29943Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 7bitsteam/exch_cve-2021-42321
Modified .NET deserialization payload for CVE-2021-42321, based on ysoserial.net, that writes files and bypasses Windows Defender to target Microsoft…
 vp777/windows-kernel-exploitation
Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
 adenkiewicz/cve-2009-1330
Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.
 lsw29475/cve-2020-17057
Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
 adenkiewicz/cve-2003-0264
Exploit for CVE-2003-0264 based on pwntools and metasploit's windows/reverse_tcp
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
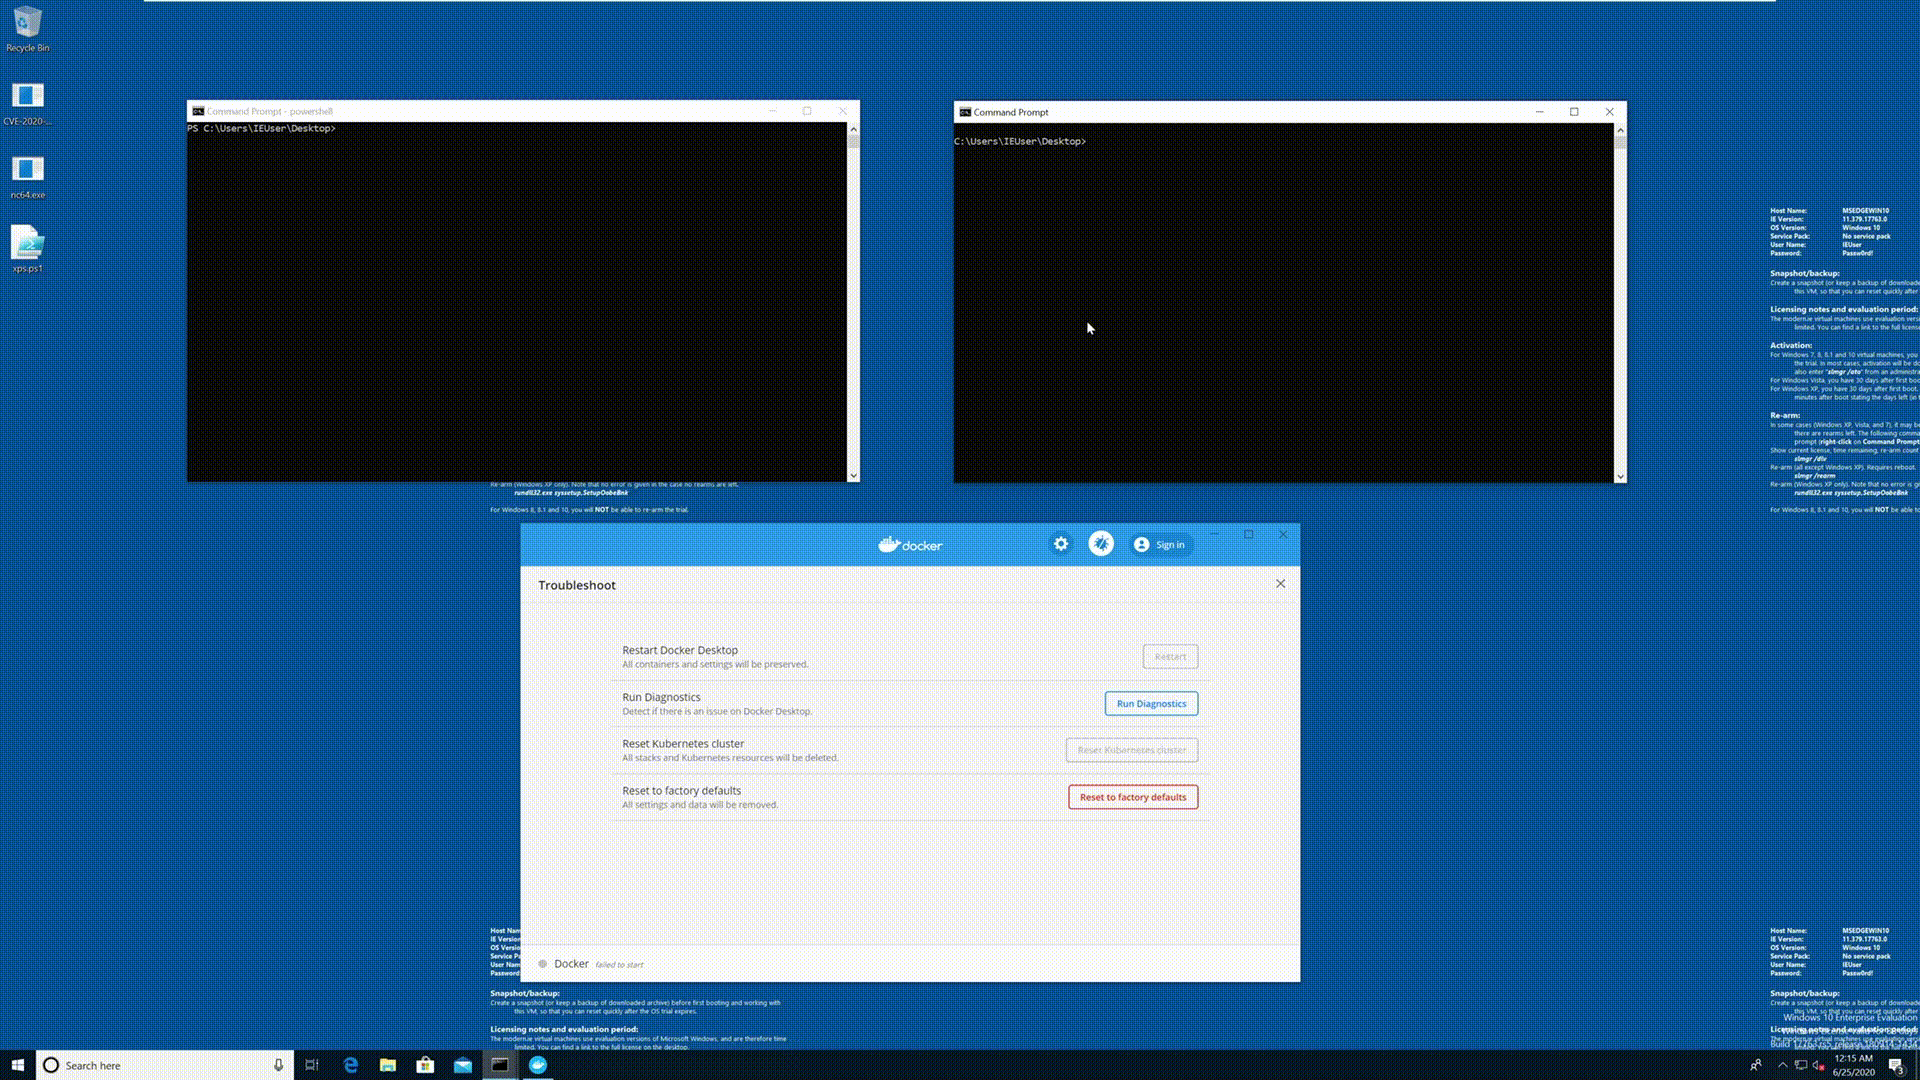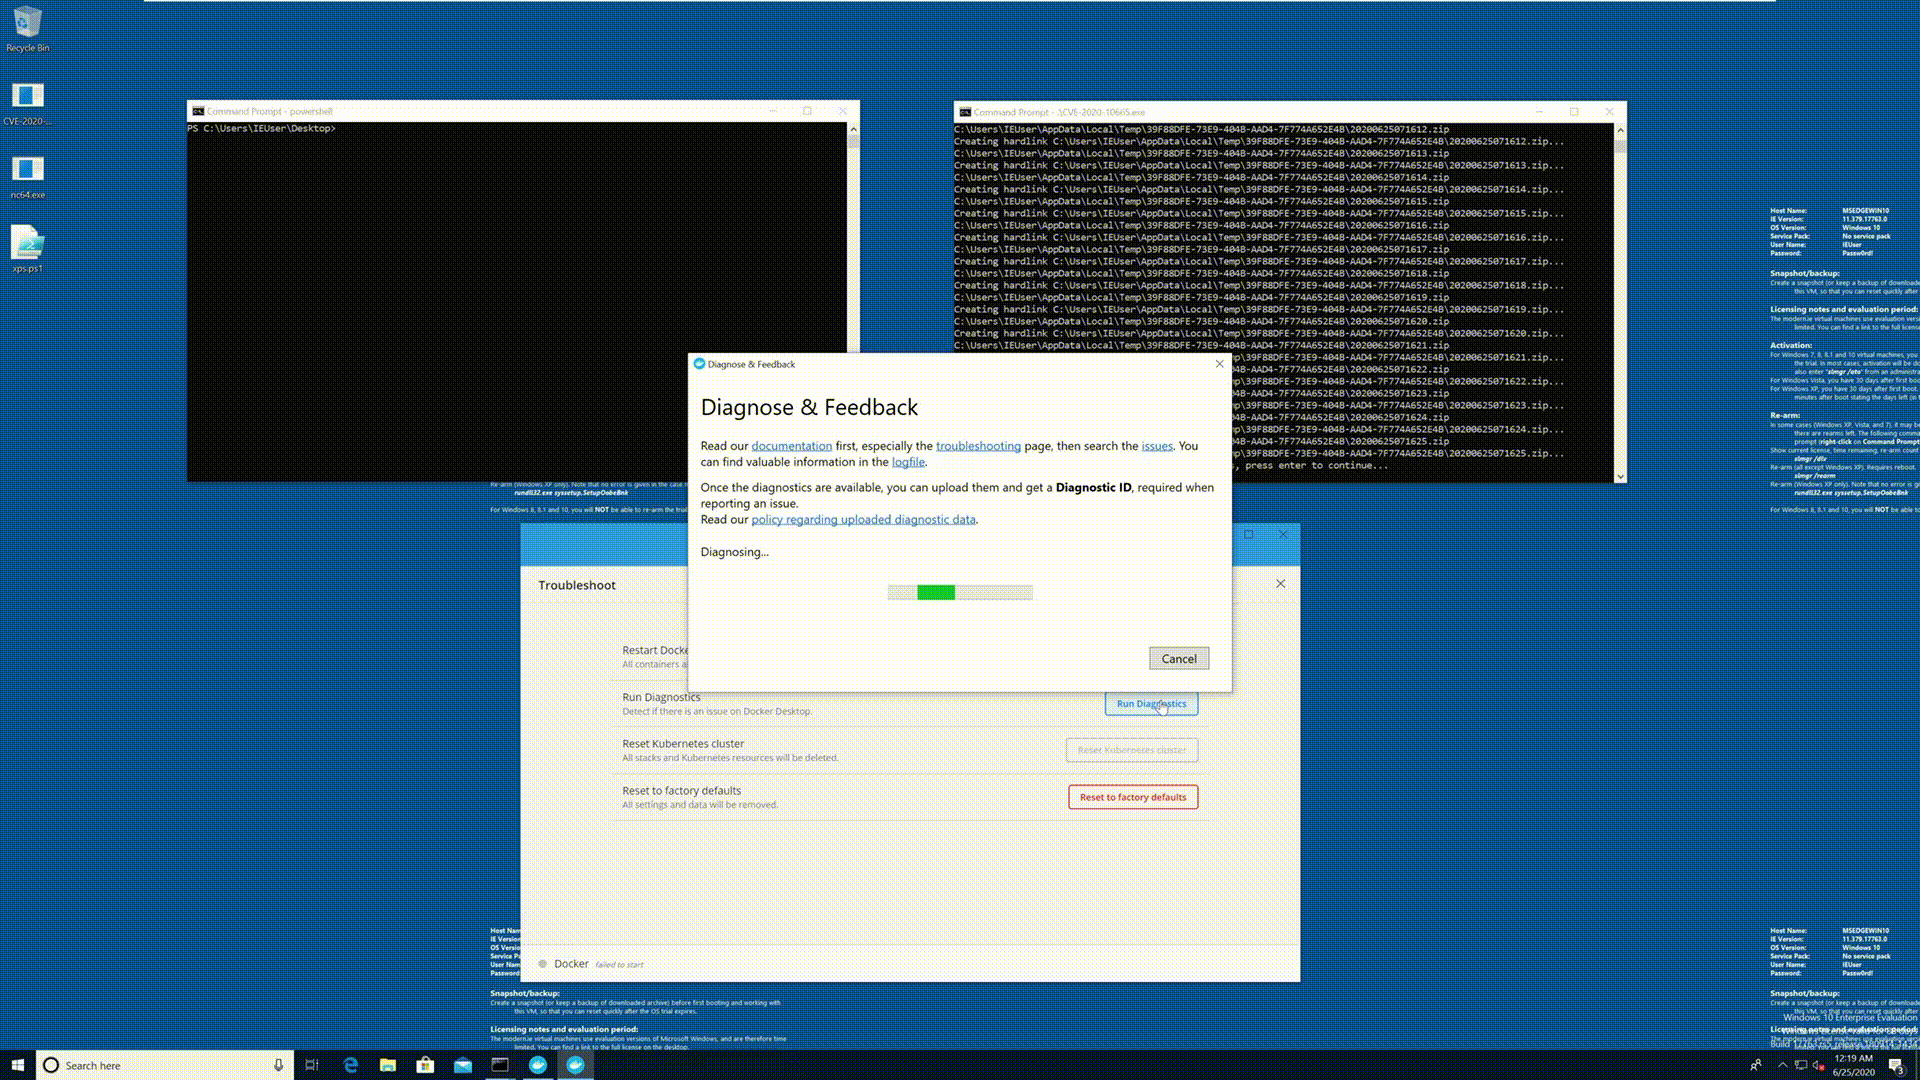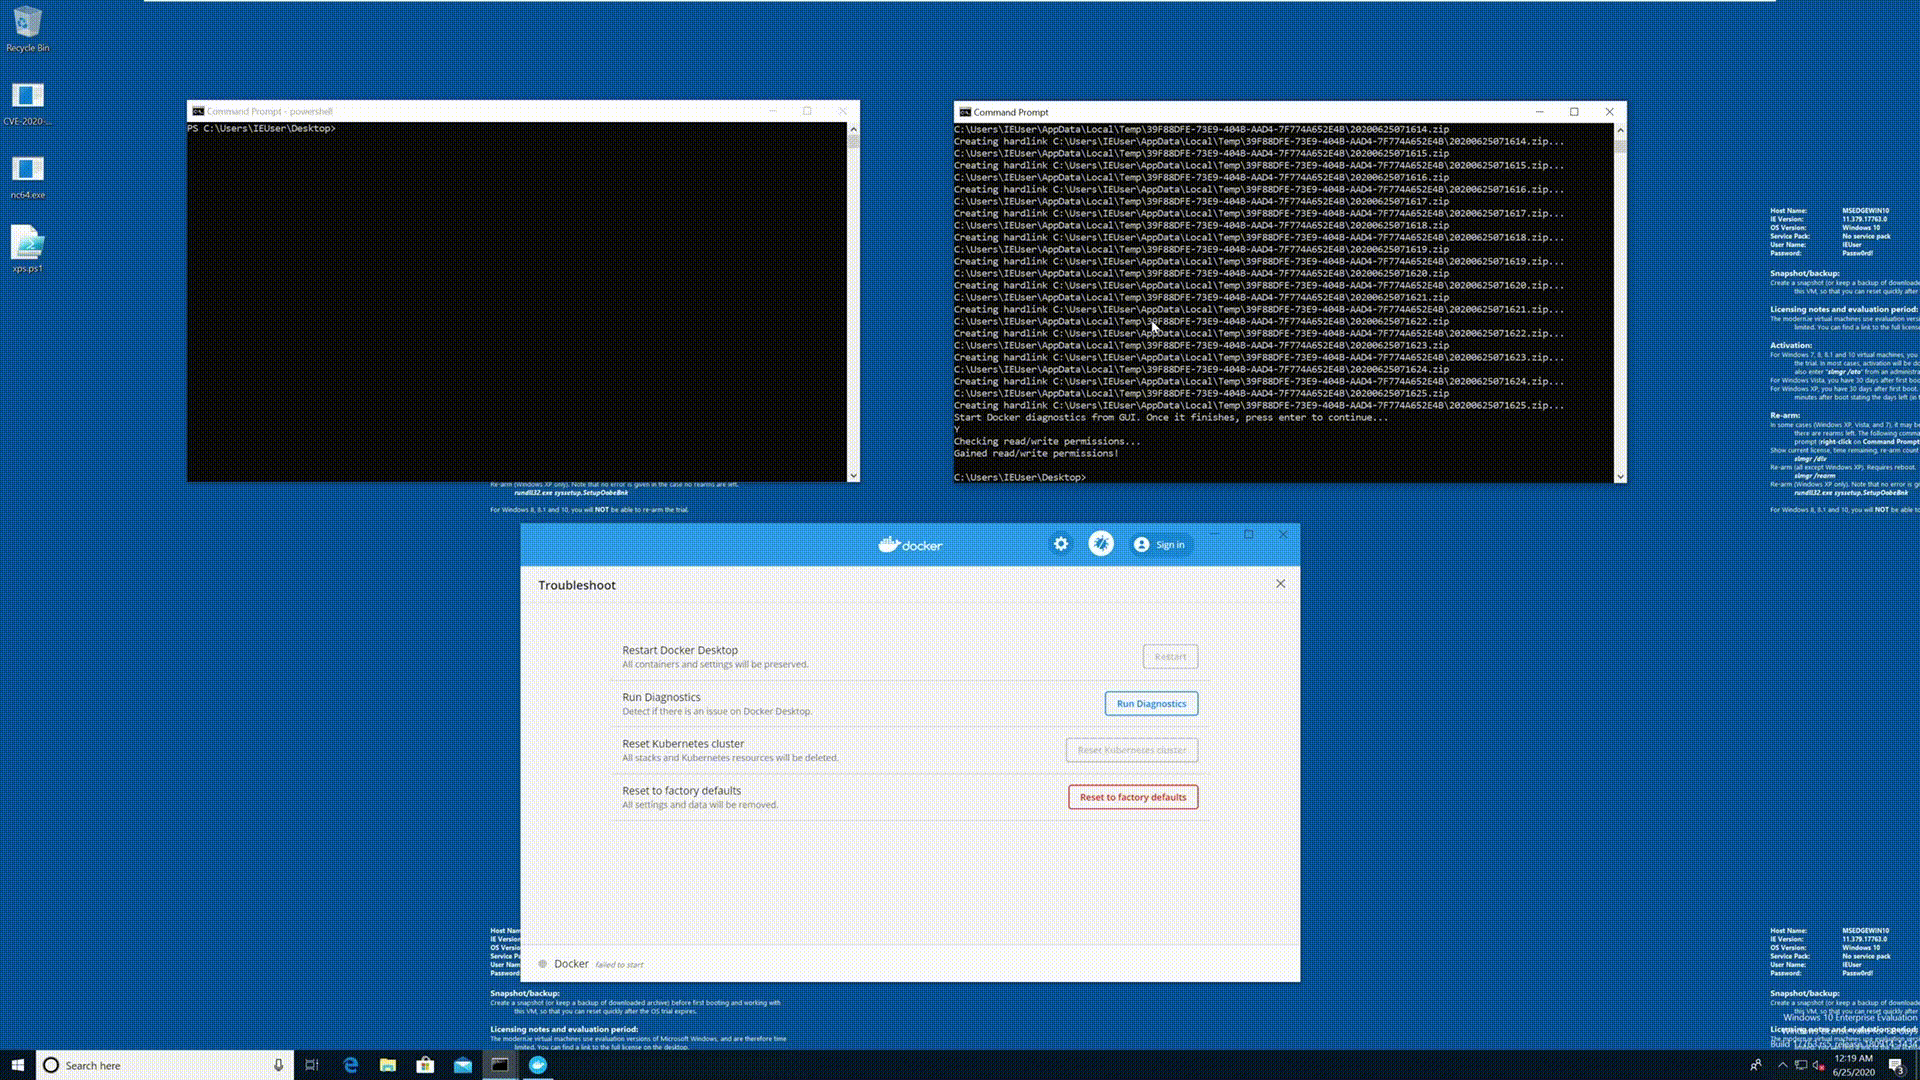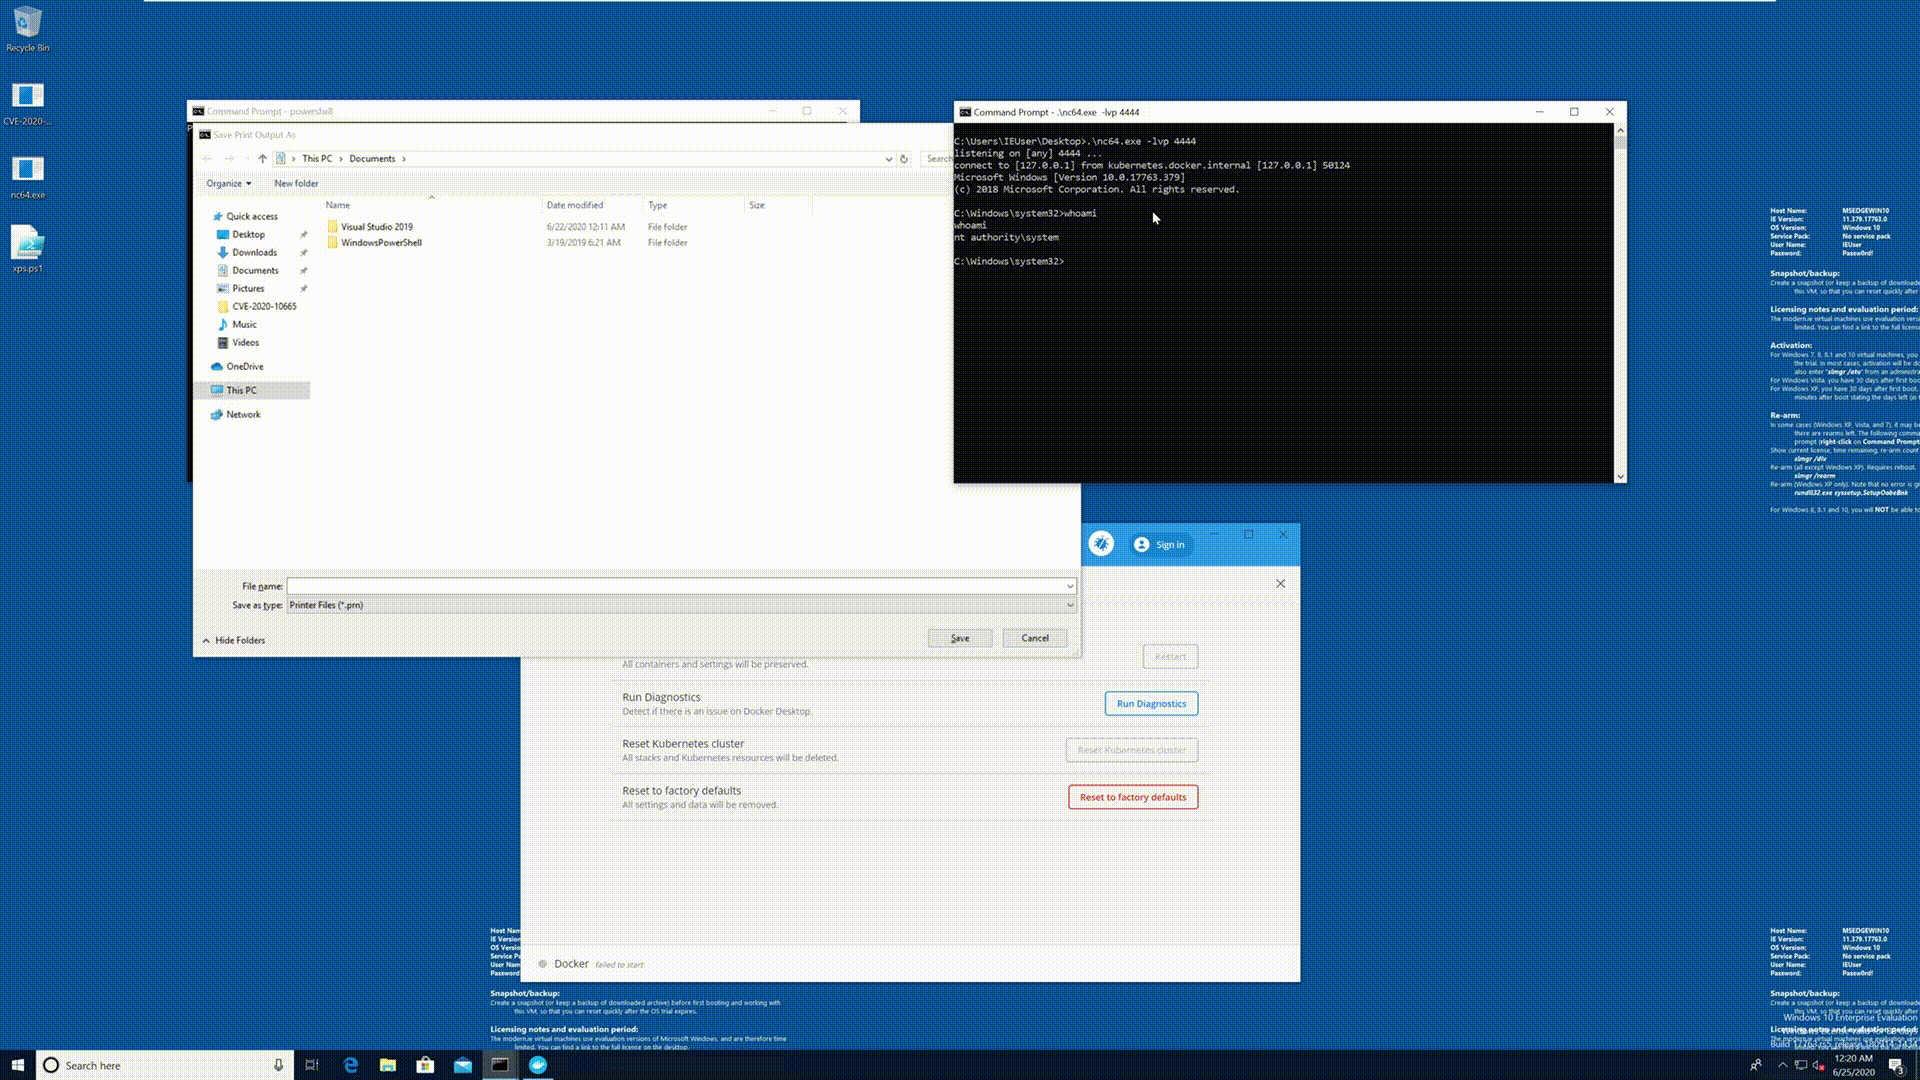 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 h4xl0r/winrar_ace_exploit_cve-2018-20250
This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
 spiralbl0ck/kernel-arbitrary-read-vulnerability-superfetch-eop
Kernel Arbitrary Read Vulnerability + Superfetch EOP based on reacher from https://starlabs.sg/blog/2022/06-trying-to-exploit-a-windows-kernel-arbitra…
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 mathisvickie/cve-2021-27965
stack based buffer overflow in MsIo64.sys, Proof of Concept Local Privilege Escalation to nt authority/system