
ps-ppl-bypass
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
binary-exploitationdefensive-toolsexploitation+5
258 days ago
r41n3rzuf477/ps-ppl-bypassProcess Explorer vulnerable driver PPL Bypass
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
 orinimron123/cve-2026-40369-exploit
Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 yardenshafir/ioringreadwriteprimitive
Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
 secmob/badkernel
Full exploit of CVE-2016-6754(BadKernel) and slide of SyScan360 2016
 secmob/pwnfest2016
full exploit of pwnfest2016, slide and full text of syscan2017
 bjrjk/cve-2022-4262
Full Chain Analysis of CVE-2022-4262, a non-trivial feedback slot type confusion in V8.
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 tacnetsol/cve-2019-10999
Full exploit for D-Link DCS-5020L, POC crash for others that are vulnerable as well.
 spiralbl0ck/cve-2025-0087-
CVE-2025-0087 EoP full PoC
 mrk336/cve-2025-26686-the-tcp-ip-flaw-that-opens-the-gates
A critical RCE vulnerability in Windows TCP/IP stack (CVE-2025-26686) leaves sensitive memory unlocked, allowing remote attackers to hijack systems.…
 keto0422/cve-2023-33107
Full exploit code for CVE-2023-33107 with a detailed writeup and demonstration video, providing a practical resource for understanding and testing…
 dangokyo/cve-2017-3000
A full exploit of CVE-2017-3000 on Flash Player Constant Blinding PRNG
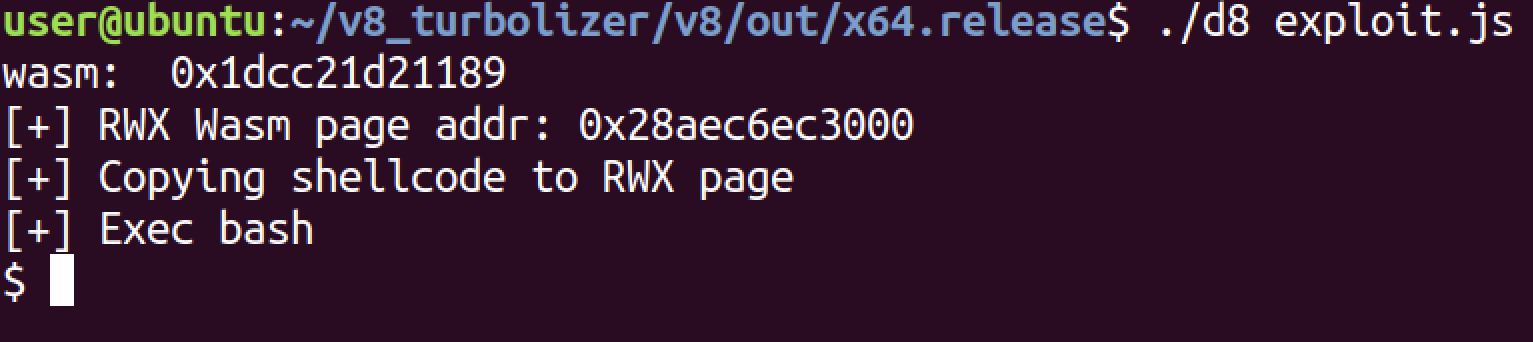 habooblab/cve-2019-13764
Full exploit for CVE-2019-13764 targeting V8 JavaScript engine on Linux, with root cause analysis and proof-of-concept code from Haboob Research Team.
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 diegslva/cve-2010-4221-lab
From patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…