
CVE-2026-59346-POC
 0xcyberstan/cve-2026-59346-poc
PoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
binary-exploitationexploitationhardware-iot-security+3
13
0xcyberstan/cve-2026-59346-pocPoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
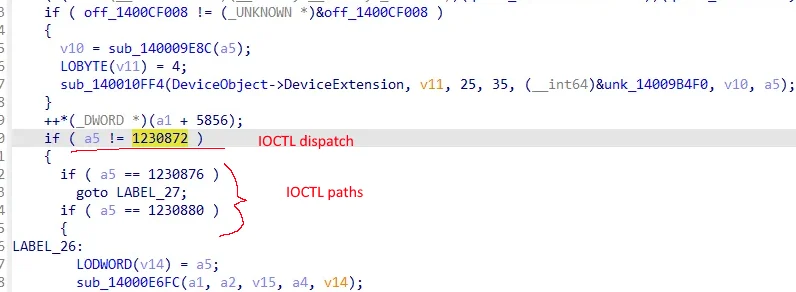 catforgor/cve-2026-51585
rt26cx21x64.sys exploit (Realtek PCIe GbE/2.5GbE/5GbE family)
 george0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser
Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…
 dylvie/cve-2024-9570_d-link-dir-619l-bof
Remote buffer overflow exploit for D-Link DIR-619L router (CVE-2024-9570) targeting the formEasySetTimezone function for penetration testing and…
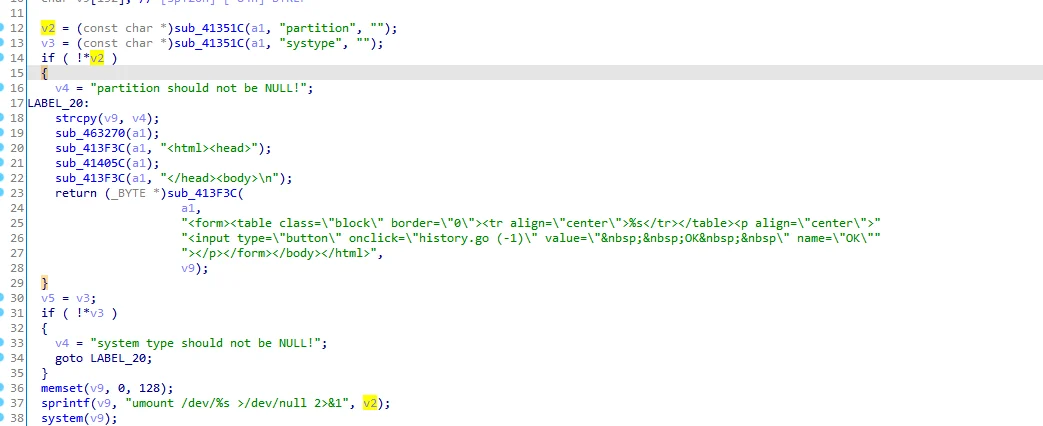 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 st3v3nss/cve-2017-7651
This is the repository used for CVE-2017-7651 for exploiting mosquitto 1.4.14
 str0ng4le/cve-2022-30114
Proof-of-concept exploit for CVE-2022-30114, a heap-based buffer overflow in Fastweb FastGate routers. Sends a crafted HTTP Authorization header to…
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 openl2d/moc3ingbird
MOC3ingbird Exploit for Live2D (CVE-2023-27566)
 mbanyamer/cve-2025-5688-freertos-plus-tcp-out-of-bounds-write
PoC exploit for CVE-2025-5688: remote out-of-bounds write in FreeRTOS-Plus-TCP via crafted LLMNR/mDNS queries, causing crash or potential RCE on…
 hacefresko/cve-2025-40634
Exploit for stack-based buffer overflow found in the conn-indicator binary in the TP-Link Archer AX50 router
 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38427
CVE-2026-38427 — Integer Wraparound → Heap Buffer Overflow in Tasmota fetch_jpg() uint16_t (Tasmota <= 15.3.0.3)
 spiralbl0ck/iot_hacking_camera_0day
Iot Camera 0day