
CVE-2023-2002
 lrh2000/cve-2023-2002
Linux Bluetooth - Run arbitrary management commands as an unprivileged user
binary-exploitationbluetooth-securityeducation+3
853 years ago
lrh2000/cve-2023-2002Linux Bluetooth - Run arbitrary management commands as an unprivileged user
 canyie/transitionplayer
CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
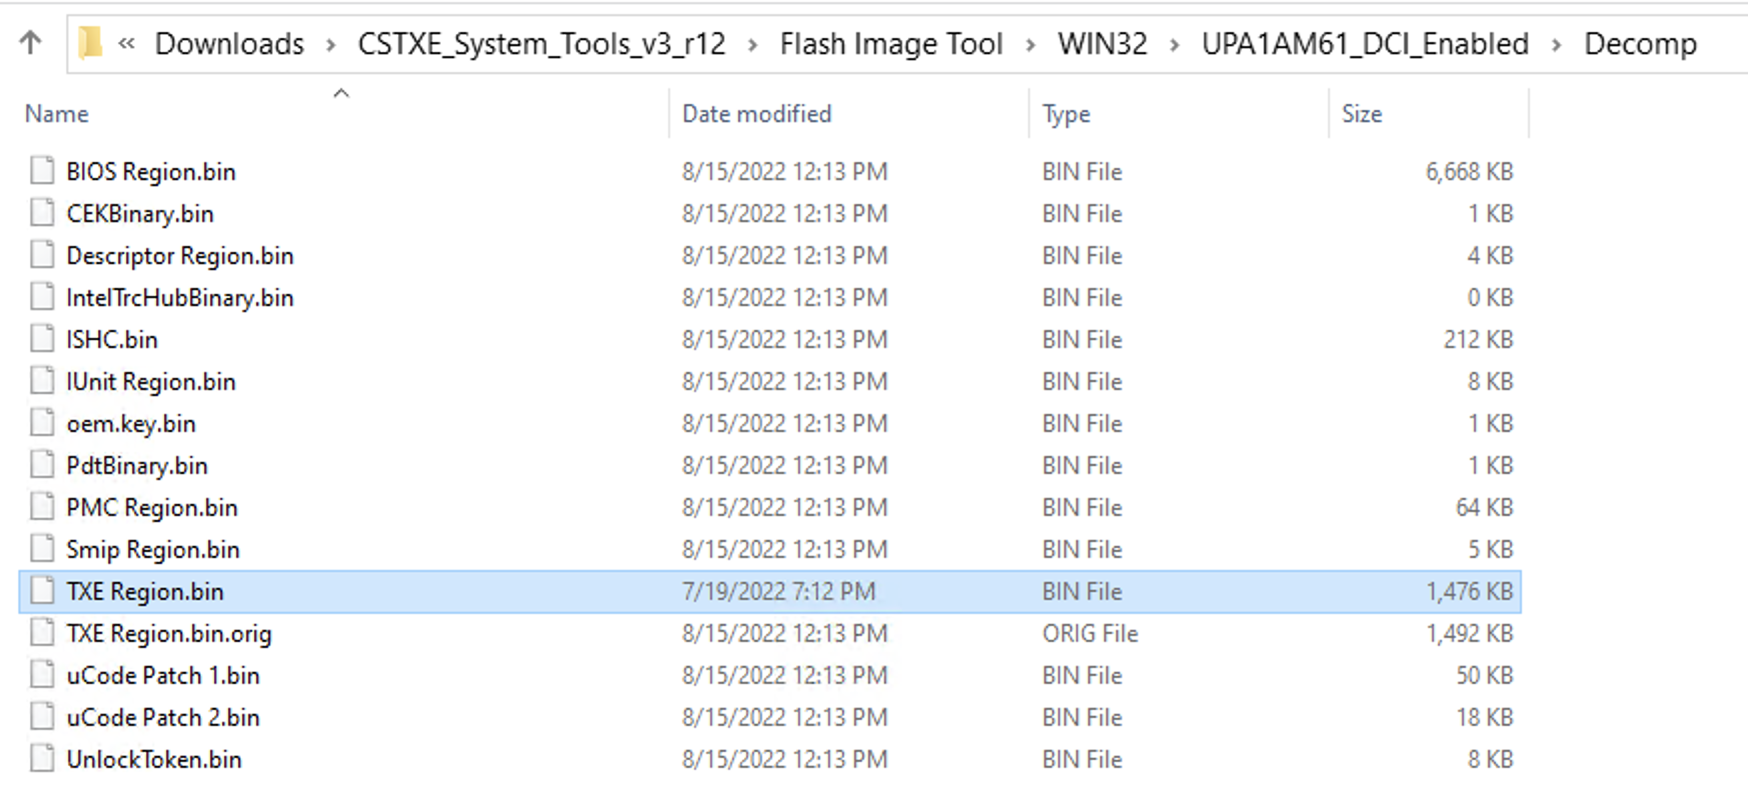 xenokovah/inteltxe-poc
Intel Management Engine JTAG Proof of Concept - 2022 Instructions
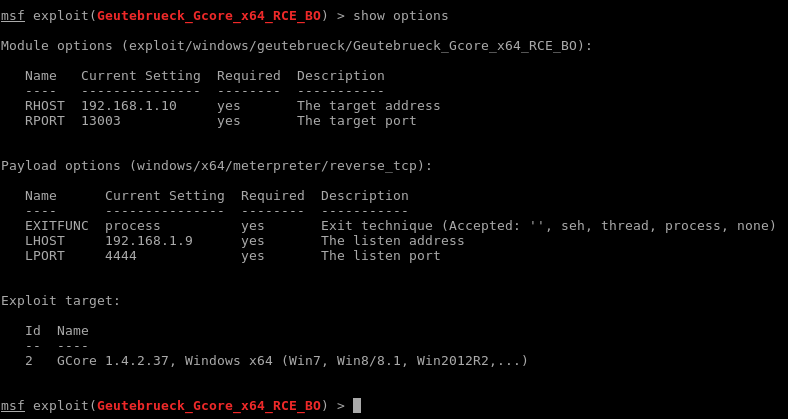 m4p0/geutebrueck_gcore_x64_rce_bo
Metasploit module for Geutebrueck GCore "video management" system. Tested with version 1.3.8.42 and 1.4.2.37
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 miapatsune/cve-2026-43499
Kernel exploit for Redmi Pad Pro (dizi) / POCO Pad 5G with browser-based upload and execution interface, admin panel for log management, and…
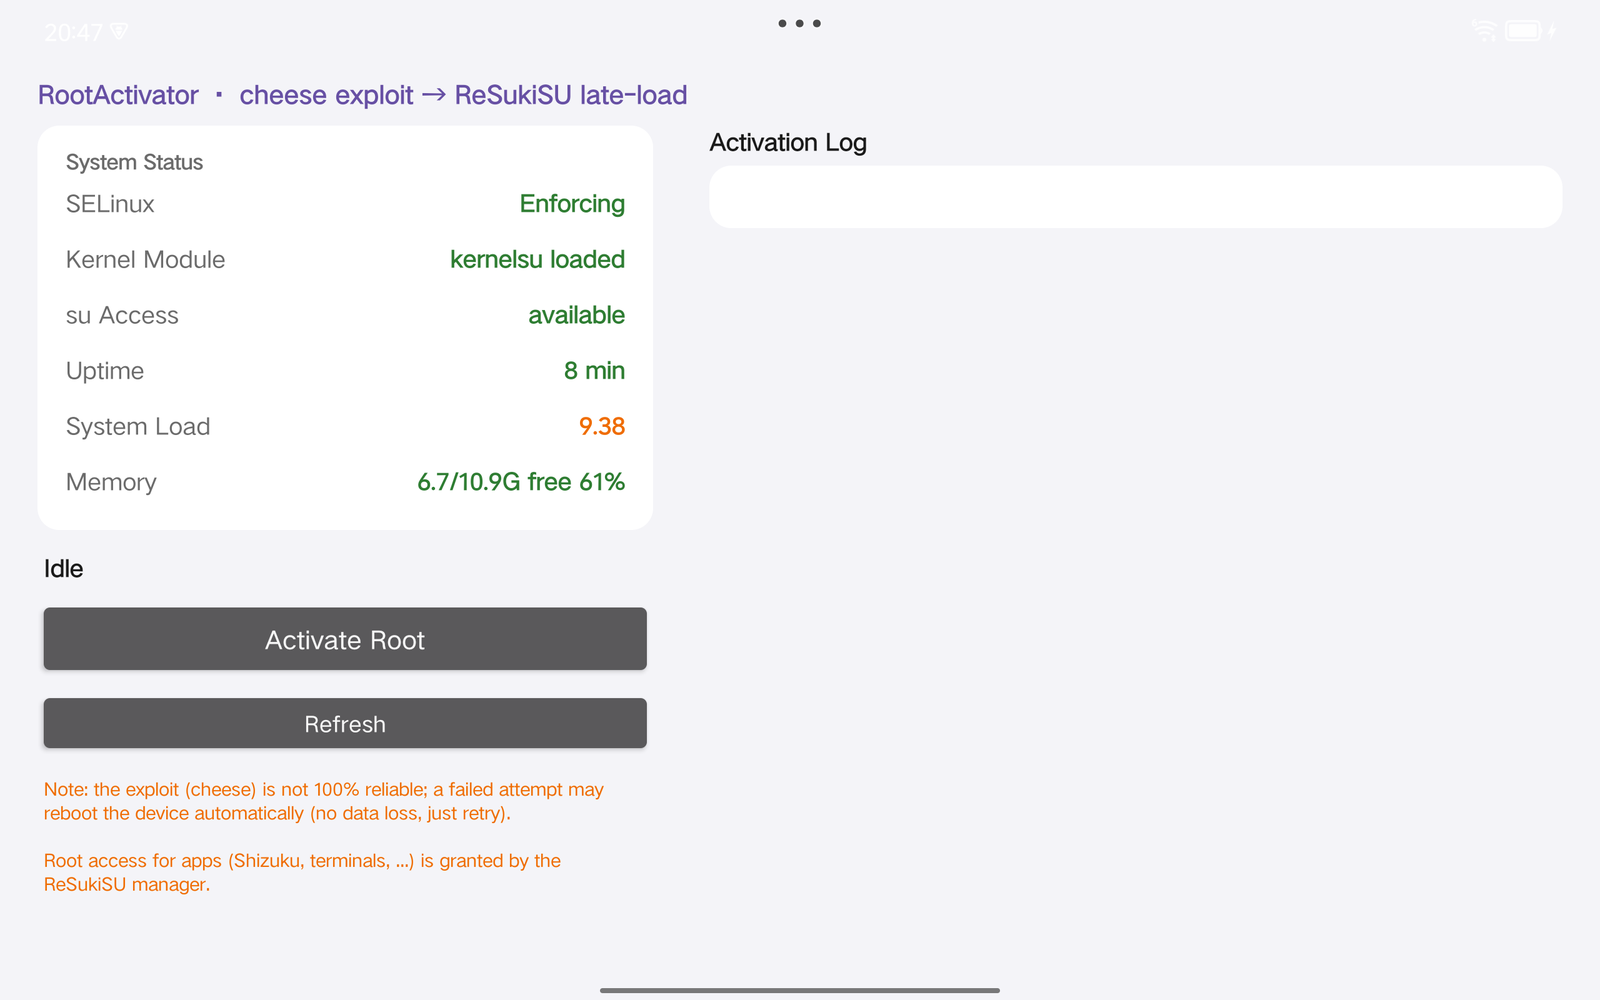 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
 lzty/cve-2025-7771
Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
 simoesctt/cve-2024-0070-nvidia-gpu-driver--resonance-vulnerability
NVIDIA's GPU drivers have a temporal coherence flaw in their memory management. At 587 kHz resonance, the driver's memory pages experience α-decay…
 encrypter15/cve-2025-30400
Educational Python model demonstrating a Use-After-Free (UAF) privilege escalation vulnerability inspired by CVE-2025-30400 in Windows DWM. Simulates…
 kernoelpanic/cve-2015-8299
Proof-of-concept exploit for a remote buffer overflow vulnerability in KNX ETS4 management software, demonstrating ROP-based code execution via…
 wolffcorentin/cve-2019-1663-binary-analysis
Binary analysis and exploitation of CVE-2019-1663, a buffer overflow in Cisco router web management, including root cause, exploit steps, and ROP…
 h1n4mx0z/research-cve-2016-5195
Detailed technical analysis and proof-of-concept exploit for CVE-2016-5195 (Dirty COW), a Linux kernel privilege-escalation vulnerability using a…
 ggkendall/securecodingdemo
fall2022 secure coding CVE-2019-13272 : Linux Kernel Improper Privilege Management Vulnerability
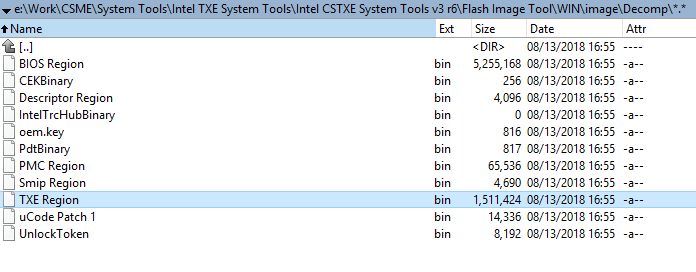 ptresearch/inteltxe-poc
Intel Management Engine JTAG Proof of Concept
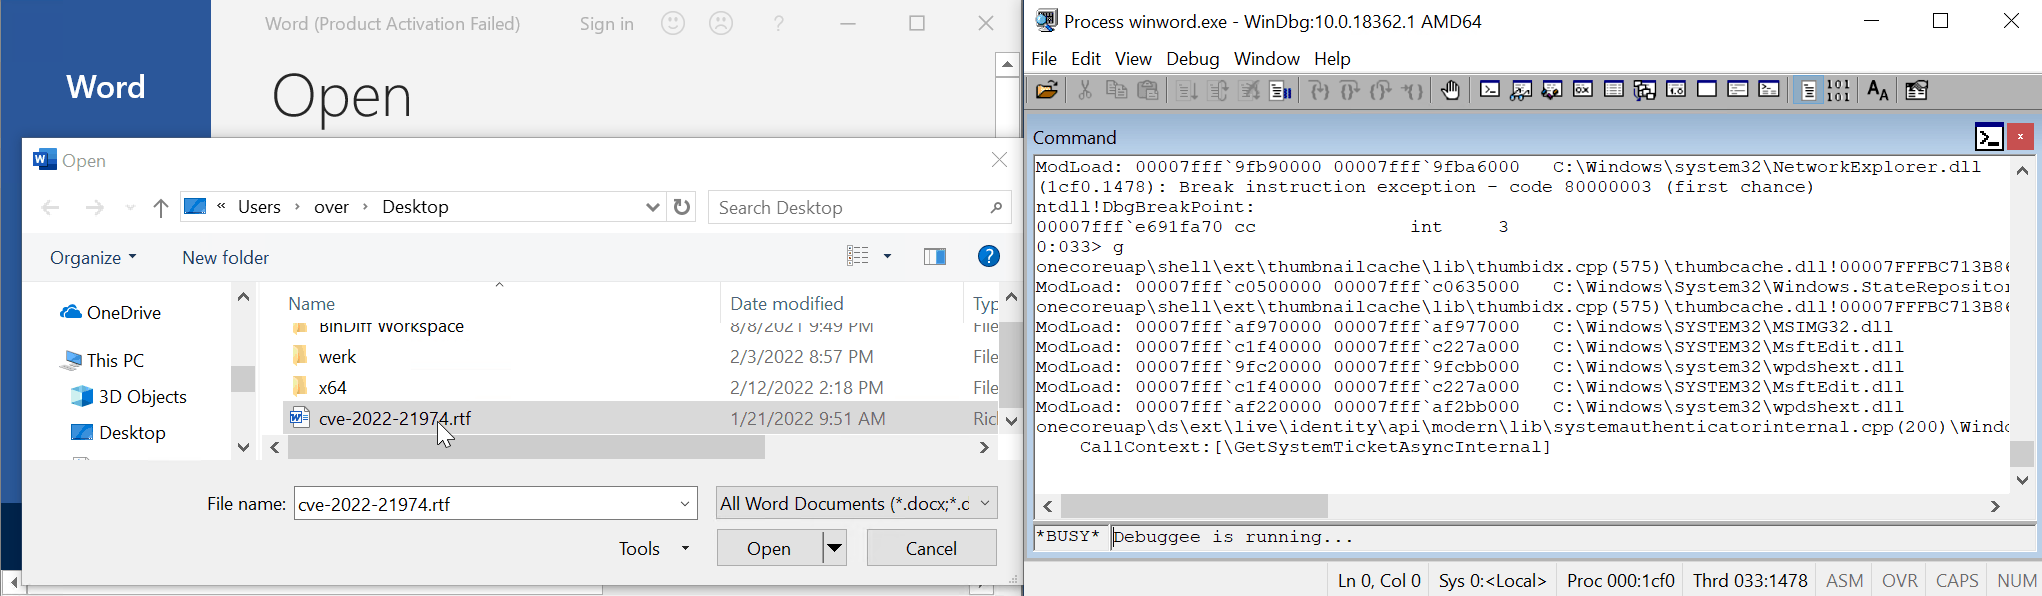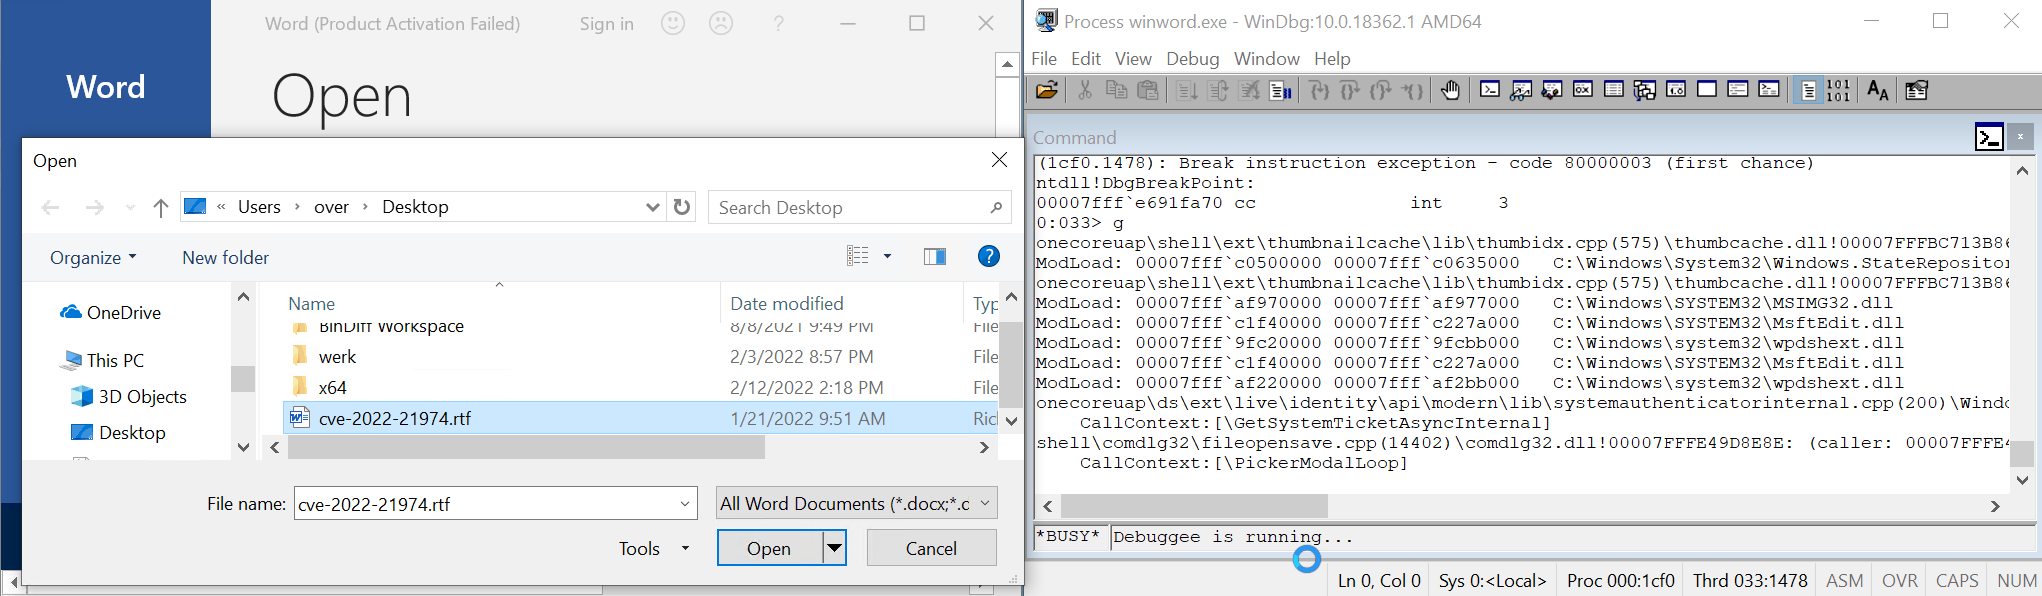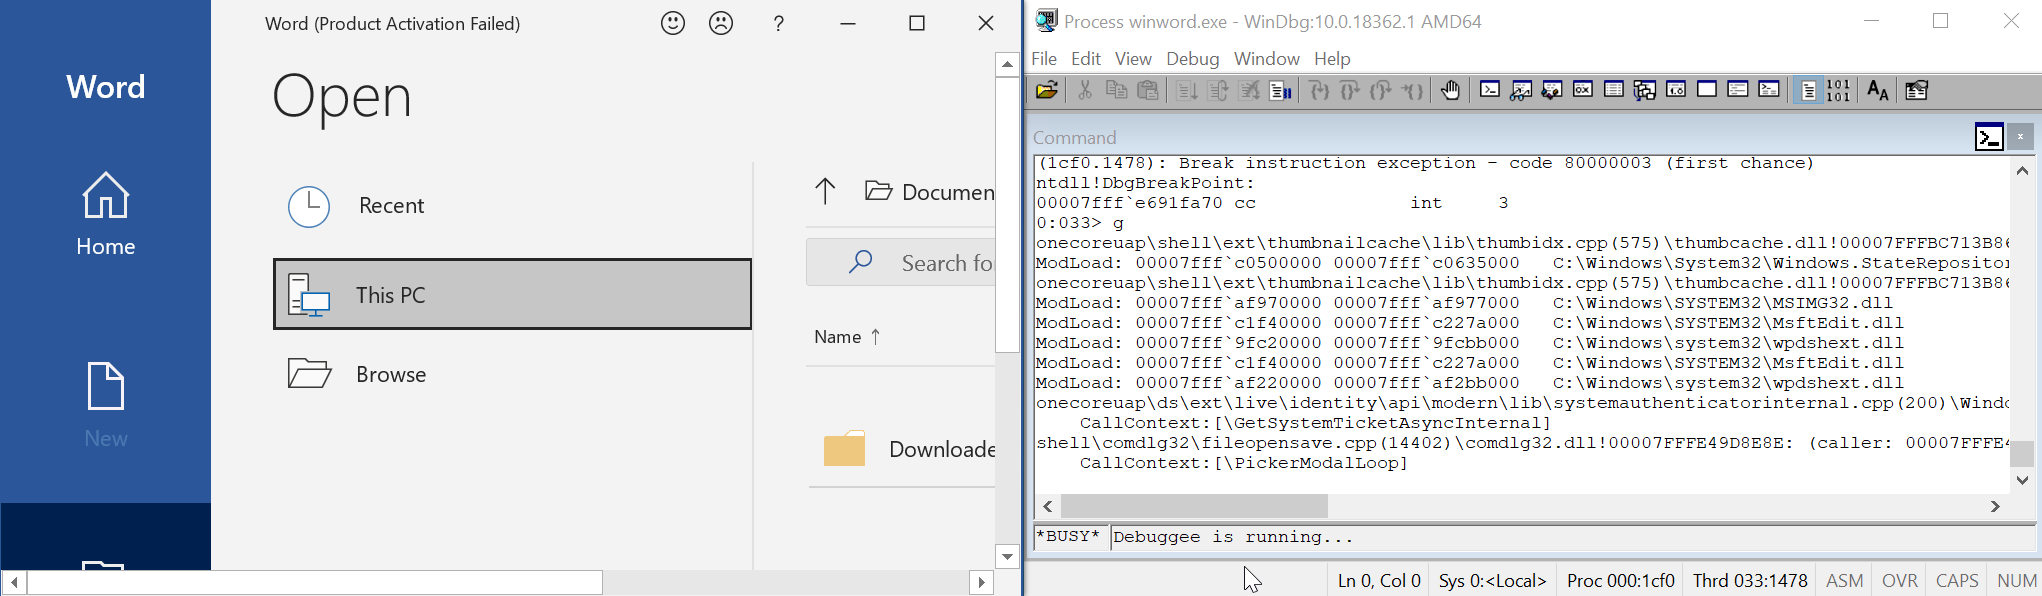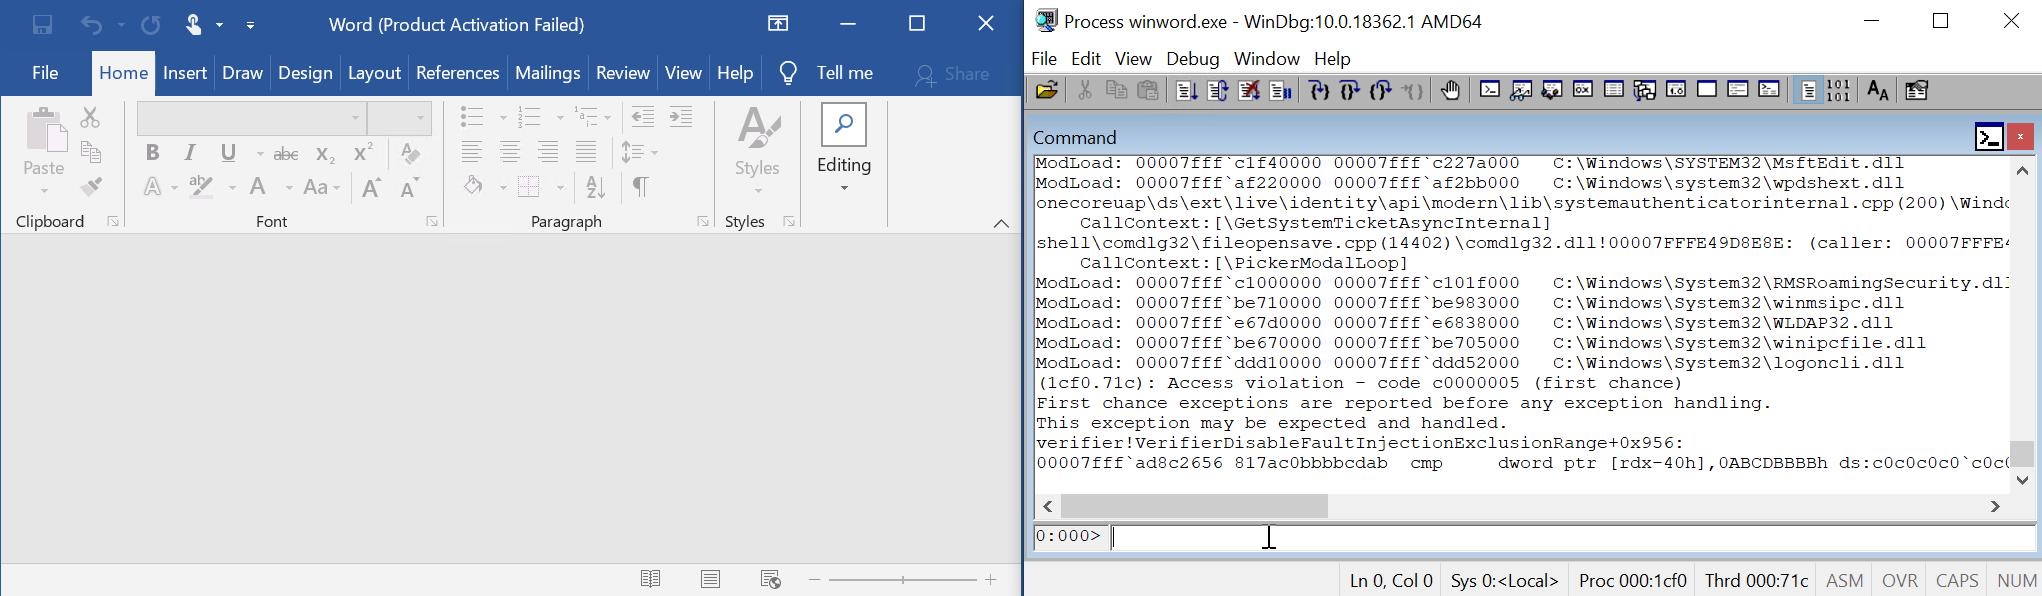 0vercl0k/cve-2022-21974
PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 bazad/launchd-portrep
CVE-2018-4280: Mach port replacement vulnerability in launchd on macOS 10.13.5 leading to local privilege escalation and SIP bypass.