
CacheMeIfYouCan
 lsinus/cachemeifyoucan
SLUBStick exploitation of CVE-2022-2588. Converting a DF into a cross-cache arbitrary memory R/W primitive through PTE manipulation.
binary-exploitationexploitationmemory-forensics+1
2
lsinus/cachemeifyoucanSLUBStick exploitation of CVE-2022-2588. Converting a DF into a cross-cache arbitrary memory R/W primitive through PTE manipulation.
 sneakynachos/cve-2026-84118-who-labeled-the-crit-as-a-high
Proof-of-concept for CVE-2026-84118, a SpiderMonkey GC use-after-free leading to out-of-bounds read/write and potential code execution. Includes…
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
 tamagaft/cve-2019-17662
Golang implementation of CVE-2019-17662 TinyVNC Arbitrary File Read leading to Authentication Bypass Exploit
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 sandi-go/cve-2018-8389
Technical analysis and proof-of-concept for CVE-2018-8389, a use-after-free vulnerability in Internet Explorer's jscript.dll allowing remote code…
 sandi-go/cve-2018-12798
Proof-of-concept exploit for CVE-2018-12798, a heap overflow in Adobe Acrobat Reader that enables remote code execution via malicious PDF files.
 bananoname/cve-2024-49138-poc
Proof-of-concept exploit for CVE-2024-49138 in Windows CLFS.sys, achieving local privilege escalation to system shell via token manipulation.
 xmzyshypnc/cve-2021-30551
my exp for chrome V8 CVE-2021-30551
 neo-neo6/cve-2025-65018-heap-buffer-overflow-in-libpng-ps4-ps5-
Proof-of-concept exploit for a heap buffer overflow in libpng on PS4/PS5. Generates a malicious PNG that triggers the vulnerability when opened in…
 xlucas/dirtycow.cr
CVE-2016-5195 exploit written in Crystal
 ps5dev/ps5-umtx-jailbreak
A webkit-based kernel exploit and jailbreak for PS5
 jm33-m0/cve-2021-3156
Go-based exploit for CVE-2021-3156, a sudo heap overflow vulnerability enabling local privilege escalation on Linux systems.
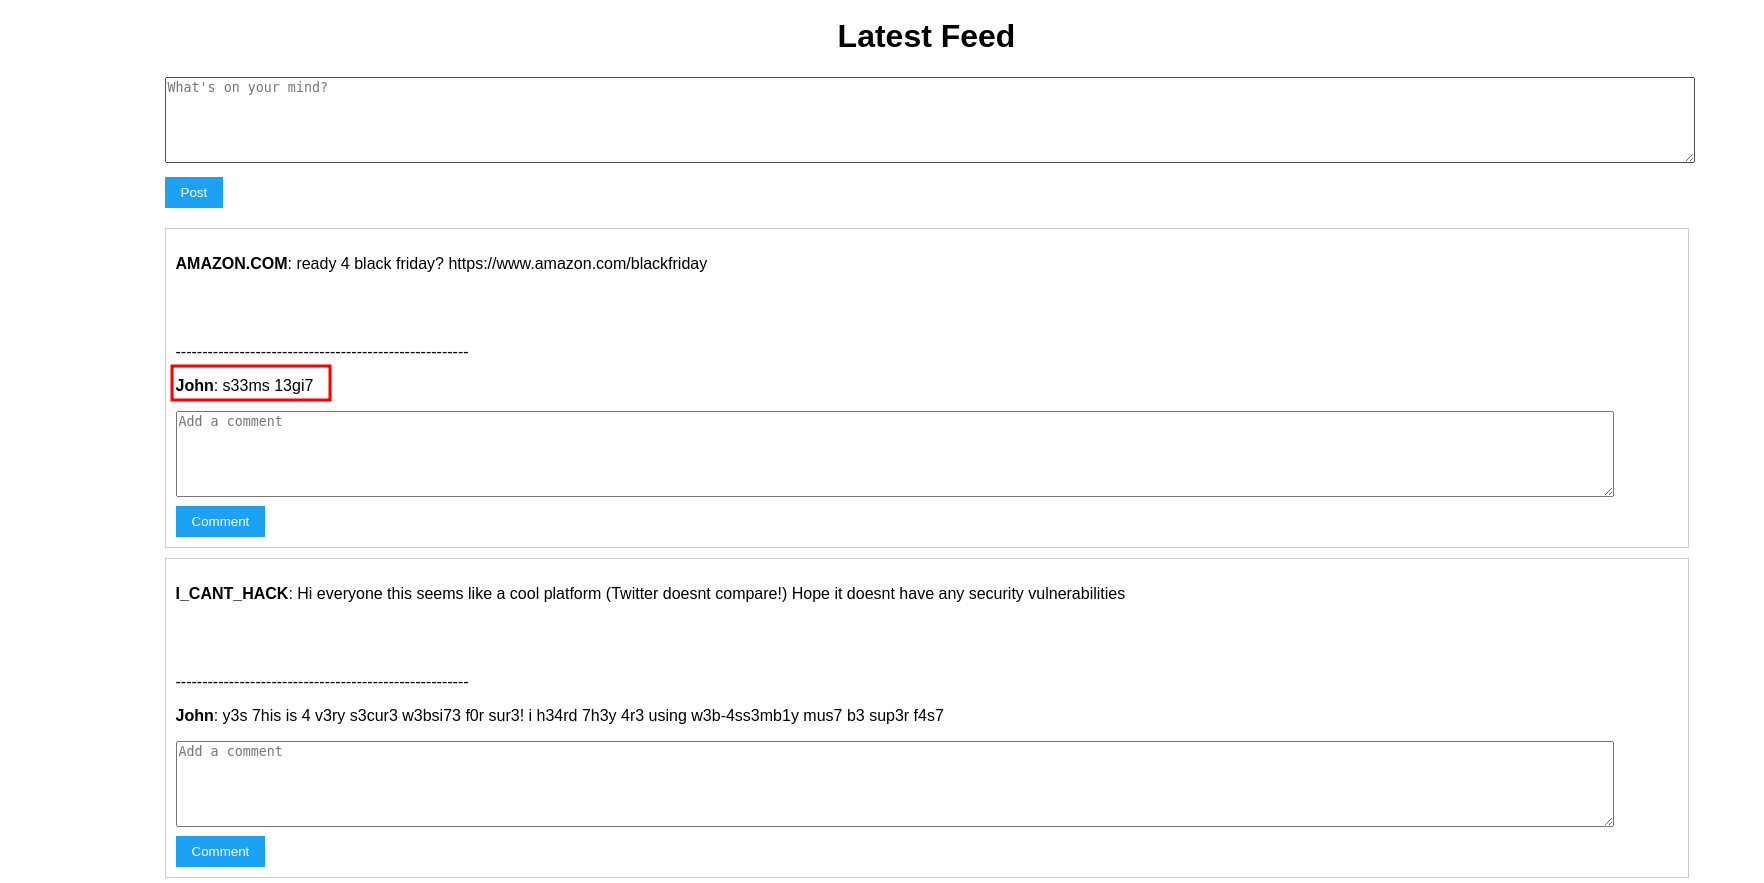 paras98/cve-2021-38297-go-wasm-replication
Educational proof-of-concept replicating CVE-2021-38297, a Go WASM buffer overflow leading to stored XSS. Includes vulnerable app setup, exploit…
 adrivillab/cve-2018-6574
Proof-of-concept exploit demonstrating remote command execution in Go's `go get` via crafted cflags in a malicious third-party package.
 seoqqq/cve-2018-6574
Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.
 alialucas7/cve-2025-27591_poc
Proof-of-concept exploit for CVE-2025-27591, demonstrating a binary vulnerability and providing a buildable Go exploit for security testing.
 percivalll/copy-fail-cve-2026-31431-statically-poc
Static Go proof-of-concept for CVE-2026-31431, leveraging Linux AF_ALG and splice(2) to trigger the vulnerability. Provides prebuilt binaries for…