

CVE-2020-8597
 lakwsh/cve-2020-8597
Exploit for CVE-2020-8597 targeting RM2100 routers, providing proof-of-concept code for remote code execution via buffer overflow in the router's web…
binary-exploitationembedded-systems-securityexploitation+3
5
lakwsh/cve-2020-8597Exploit for CVE-2020-8597 targeting RM2100 routers, providing proof-of-concept code for remote code execution via buffer overflow in the router's web…
 kkaanozturk/hyperos-directory-traversal-analysis
Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…
 chrisl0tus/cve-2023-34924
Proof-of-concept exploit for a buffer overflow vulnerability in H3C Magic B1STW router's SetAPInfoById function, causing web service crash and…
 mouftan/cve-2022-44268
Python-based exploit for CVE-2022-44268, an arbitrary file read vulnerability in ImageMagick. Poisons PNG images to read sensitive files from…
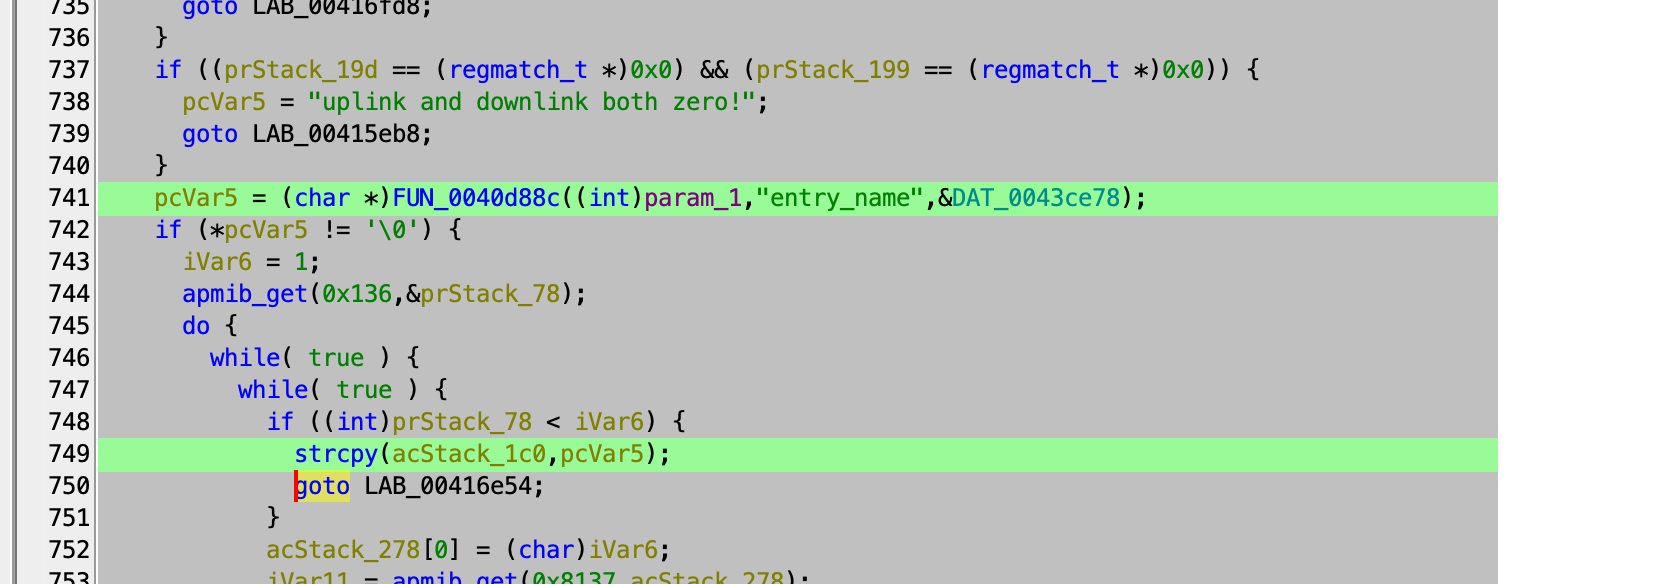 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
 niklasb/libc-database
Build a database of libc offsets to simplify exploitation
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 seregonwar/uaf-2023-28205
PoC CVE-2023-28205: Apple WebKit Use-After-Free Vulnerability
 abdullahmaqbool22/explosive-as-hell-mcs-qualifer-web-500
[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 mcw0/poc
Issues has been disabled for these PoC's, as they are simply PoC, Public Domain and unsupported.
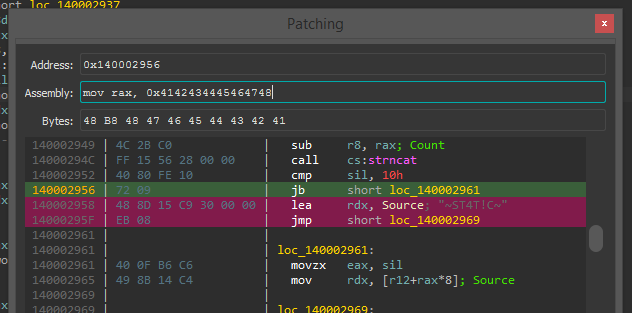 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 alexisahmed/cve-2022-0847-dirtypipe-exploits
A collection of exploits and documentation that can be used to exploit the Linux Dirty Pipe vulnerability.
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 elttam/publications
Offensive security research hub aggregating original vulnerability advisories, CVE proof-of-concept exploits, conference talks, and internal tooling…